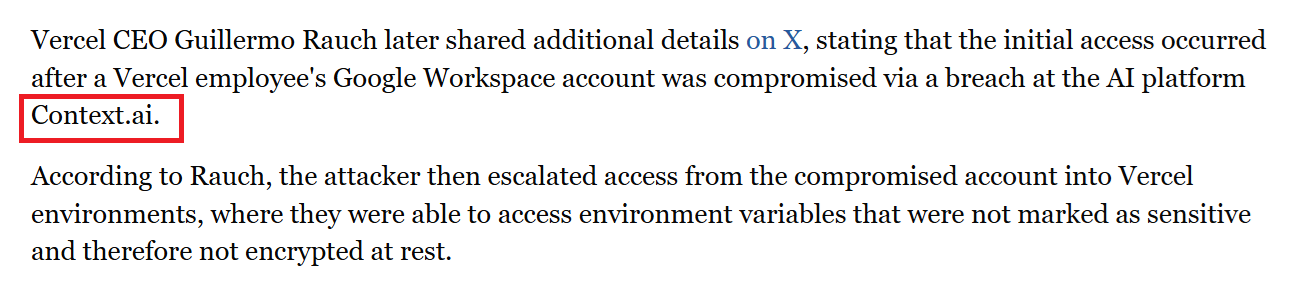
Hudson Rock found that a recent Lumma stealer infection on a Context.ai third‑party employee—triggered by downloading Roblox “auto‑farm” scripts—likely provided the initial access that enabled the Vercel breach. Compromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealer‑exposed credentials could have prevented the supply‑chain escalation. #Lumma #ShinyHunters
Category: Cyber Security News

Cybersecurity Threat Research ‘Weekly’ Recap: A roundup of social engineering, phishing, and remote-access abuse highlights Cross-tenant helpdesk impersonation, a Black Basta affiliate executive-targeting campaign, and the ClickFix phishing operation. The report also covers ransomware, extortion, data leaks, malware post-exploitation, cloud and identity abuse, and mobile-endpoint threats across multiple sectors. #CrossTenantHelpdesk #BlackBasta #ClickFix #UNC1069 #AgenziaDelleEntrate #YouTubeCopyrightNotices #InteractiveBrokers #MacSyncStealer #NightSpire #PayoutsKing #Qilin #TheGentlemen #INC_Ransom #MOIS #HomelandJustice #Karma #Handala #ForceHound #Keenadu #RecruitRat #SaferRat #Astrinox #Massiv #RedSun #TP-Link #JoomlaSEOSpam
Threat actors are abusing Apple account-change notifications by embedding phishing text into Apple ID profile fields so fraudulent iPhone purchase alerts are sent from Apple’s own mail infrastructure and pass SPF, DKIM, and DMARC checks. Recipients are urged to call scammer phone numbers to cancel purchases, a callback tactic that can lead to remote-access installs, stolen funds, or data exfiltration. #Apple #iCloud
Vercel disclosed unauthorized access to certain internal systems after a threat actor claimed to have breached its environment and offered stolen data for sale. The company says a limited subset of customers were affected, services remain operational, and it has engaged incident responders while advising customers to review and rotate secrets. #ShinyHunters #Vercel
NIST will stop assigning severity scores and enriching lower-priority CVEs in the NVD starting April 15, focusing analysis only on issues that meet specific risk-based criteria such as inclusion in CISA’s KEV, impact on U.S. federal software, or designation as critical under Executive Order 14028. All submitted CVEs will remain listed but non-prioritized entries will be marked “Not Scheduled” for enrichment, with NIST accepting enrichment requests via [email protected]. #NIST #NVD

This week’s roundup highlights advances in AI and agent identity governance, new frameworks and tools for fraud detection and attribution, and a range of incidents revealing gaps in software and operational security. Notable stories include agentic memory attacks spreading across sessions and users and a zero-day in Adobe Acrobat Reader (CVE-2026-34621) exploited in the wild. #CVE-2026-34621 #MemoryTrap
Microsoft patched CVE-2026-26144, a cross-site scripting flaw in Excel that chains to Copilot Agent and enables silent, clickless exfiltration of spreadsheet data to attacker-controlled endpoints. This incident signals a new class of AI‑amplified exploits that demand stricter egress controls, distinct monitoring for AI-initiated activity, and updated vulnerability prioritization. #CVE-2026-26144 #CopilotAgent

Daily Recap, Tycoon 2FA pressure pushed attackers to spread out across Mamba 2FA, EvilProxy, and Sneaky 2FA while increasingly using device code phishing to bypass modern authentication. Google Gemini helped block 602 million scam ads and contributed to removing or blocking over 8.3 billion ads in 2025 amid a major malvertising crackdown. #Tycoon2FA #Gemini #Qilin #Synnovis #PayoutsKing #Nexcorium
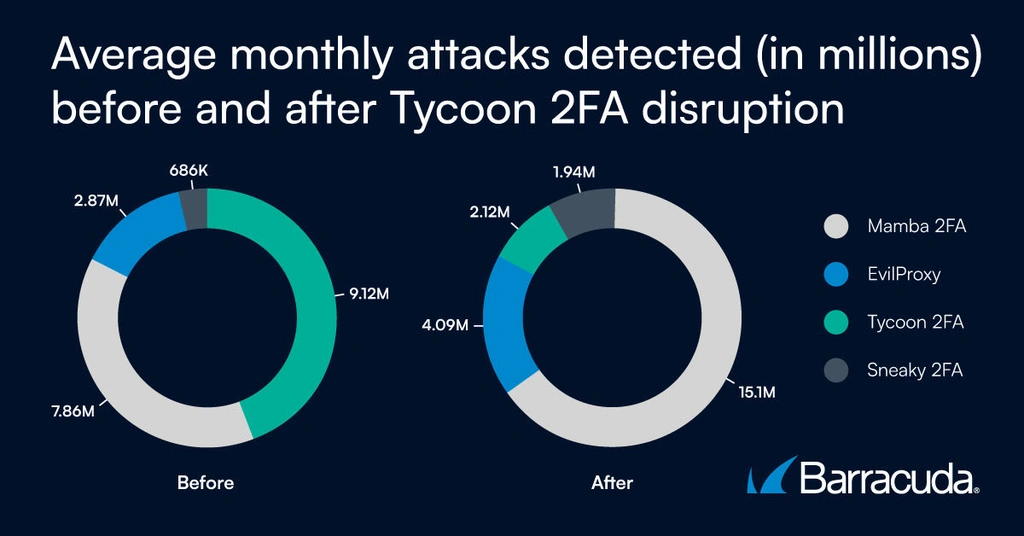
After law enforcement disrupted Tycoon 2FA by seizing 330 domains, threat actors migrated to other phishing-as-a-service platforms and began reusing Tycoon’s tools, Barracuda Networks reports. Although Tycoon lost its market-leading position to Mamba 2FA and EvilProxy, attacks leveraging the major phishing kits rose from roughly 20 million to over 23 million,…
NIST’s National Vulnerability Database is scaling back enrichment work and will prioritize which CVEs receive detailed metadata, acknowledging it can no longer manually enrich the growing backlog. Cyber teams and vendors are urged to adapt by improving CNA reporting, speeding patch deployment, and using automated or private-sector tools (such as Anthropic’s Mythos) to fill gaps as NVD coverage shrinks. #NIST #NVD
Microsoft warns a recent Microsoft Edge update introduced a code regression that breaks right-click paste in the Microsoft Teams desktop client, greying out the Paste option in chat context menus. Users can bypass the issue using keyboard shortcuts (Ctrl/Cmd + C and Ctrl/Cmd + V) and Microsoft is rolling out a staged fix while monitoring telemetry. #MicrosoftEdge #MicrosoftTeams
Proof-of-concept exploit code has been published for a critical remote code execution flaw in protobuf.js that stems from unsafe dynamic function generation from schemas. Users should upgrade to protobuf.js 8.0.1 or 7.5.5, audit schema sources, and avoid loading untrusted schemas to mitigate the risk. #protobufjs #EndorLabs

GitLab 18.11 expands agentic AI across the software lifecycle, adding platform-native agents for security remediation, pipeline configuration, and delivery analytics via the GitLab Duo Agent Platform. New capabilities include Agentic SAST Vulnerability Resolution, CI Expert and Data Analyst agents, and GitLab Credits spending controls to manage AI costs. #GitLab #AgenticSAST
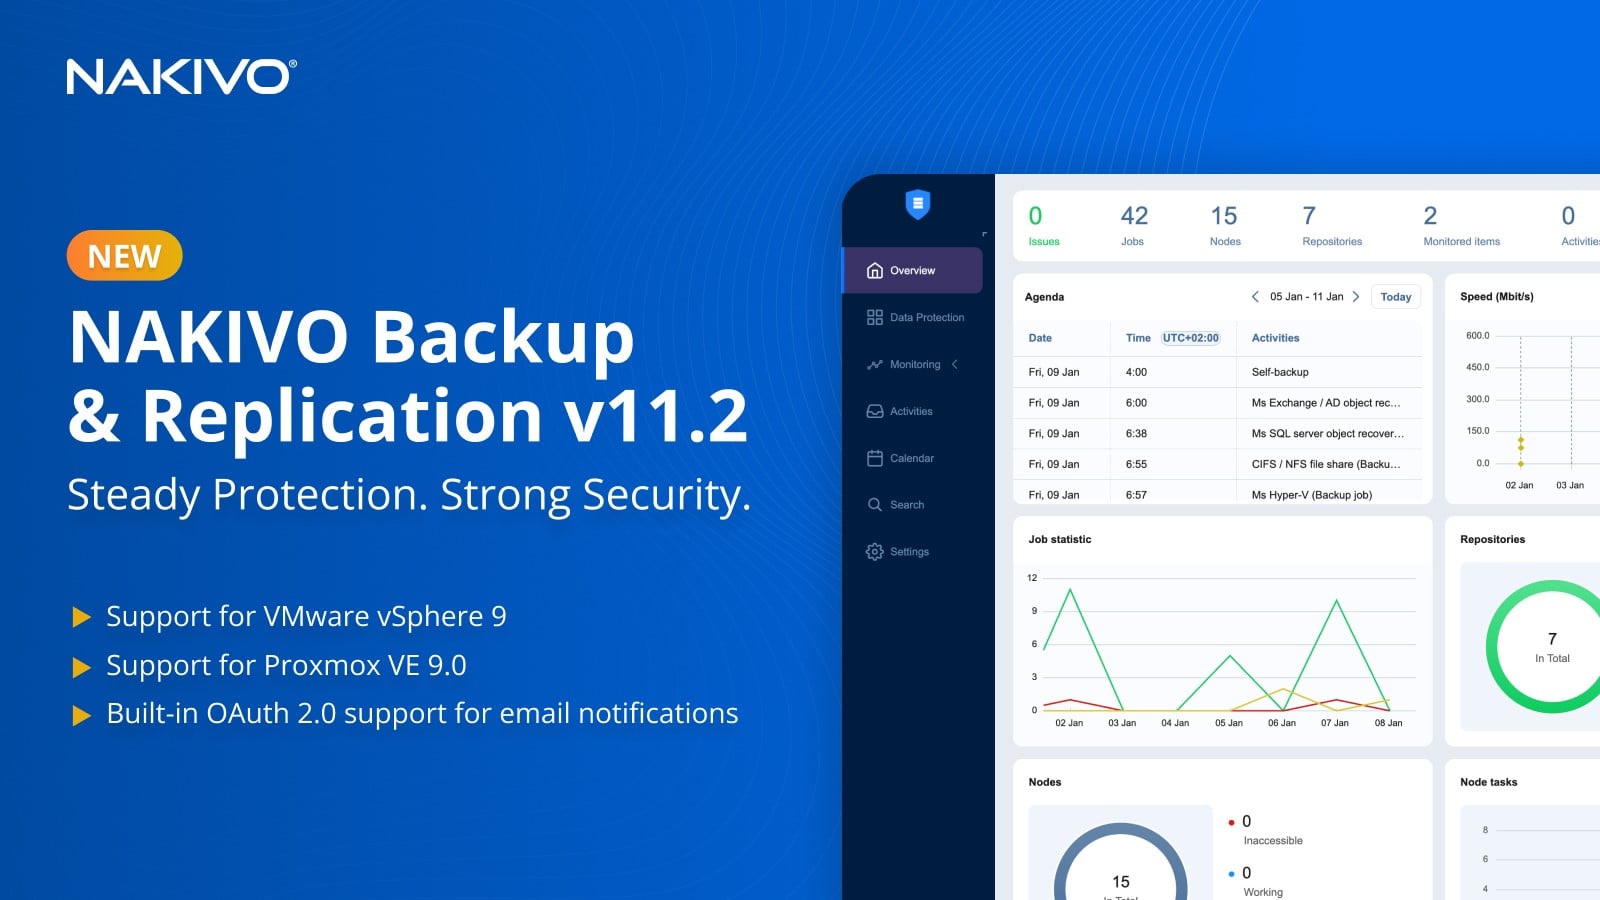
NAKIVO Backup & Replication v11.2 delivers automated real-time replication, OAuth 2.0 email authentication, and expanded support for VMware vSphere 9 and Proxmox VE 9 to speed recovery and simplify upgrades. The release also strengthens ransomware resilience with immutable backups, pre-recovery malware scanning, and broad object storage and air-gapped options. #vSphere9 #ProxmoxVE9

Tycoon 2FA’s coordinated takedown knocked out 330 domains and sharply reduced its monthly attack volume, but the phishing ecosystem quickly adapted and dispersed. Competitors like Mamba 2FA, EvilProxy, and Sneaky 2FA have absorbed activity and attackers are increasingly adopting device code phishing techniques. #Tycoon2FA #Mamba2FA #EvilProxy #Sneaky2FA #DeviceCodePhishing