
CISA added four actively exploited vulnerabilities affecting SimpleHelp, Samsung MagicINFO 9 Server, and D-Link DIR-823X routers to its Known Exploited Vulnerabilities catalog. The flaws include missing authorization and path traversal in SimpleHelp, a path traversal in Samsung MagicINFO, and a command injection in end-of-life D-Link routers tied to DragonForce ransomware activity…
Category: Cyber Security News

Daily Recap, Bitwarden and Checkmarx faced separate supply-chain compromises that exposed developer secrets through malicious npm, Docker, and extension loaders affecting CLI, KICS, VS Code, and Open VSX users. Vercel disclosed broader fallout from a Context.ai intrusion, with Lumma Stealer stealing API keys and tokens that could impact downstream systems. #Bitwarden #Checkmarx #ContextAI #LummaStealer #Vercel

China-linked threat actors have shifted from individually procured infrastructure to large-scale covert networks and botnets built from compromised SOHO routers, IoT, and other edge devices, the NCSC warns. The NCSC and partner agencies issued an advisory urging organizations to map and baseline edge-device traffic, monitor VPN and remote access connections, and adopt dynamic threat-feed filtering using known covert-network indicators. #FlaxTyphoon #IntegrityTechnologyGroup
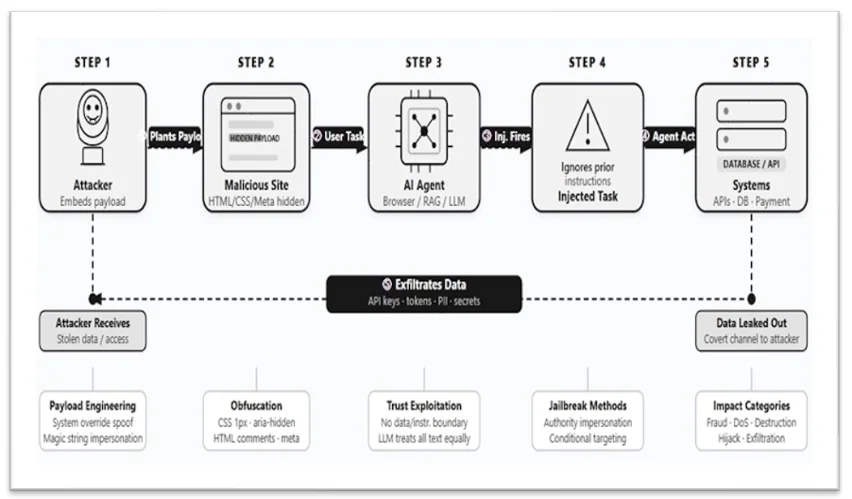
The open web is filling with hidden “traps” called indirect prompt injection (IPI) that embed covert instructions in ordinary pages to manipulate LLM-powered agents. Google and Forcepoint research documents real-world IPI examples—from benign prompts to payment fraud, data exfiltration, DoS and destructive commands—and shows attackers hide payloads in invisible text, comments and metadata. #IndirectPromptInjection #Forcepoint

The National Cyber Security Centre (NCSC) is urging consumers to abandon passwords in favour of passkeys, arguing they provide stronger protection against phishing and compromised credentials. The agency published technical guidance after engaging with vendors and the FIDO Alliance, and recommends password managers and two-step verification only where passkeys are not available. #NCSC #passkeys
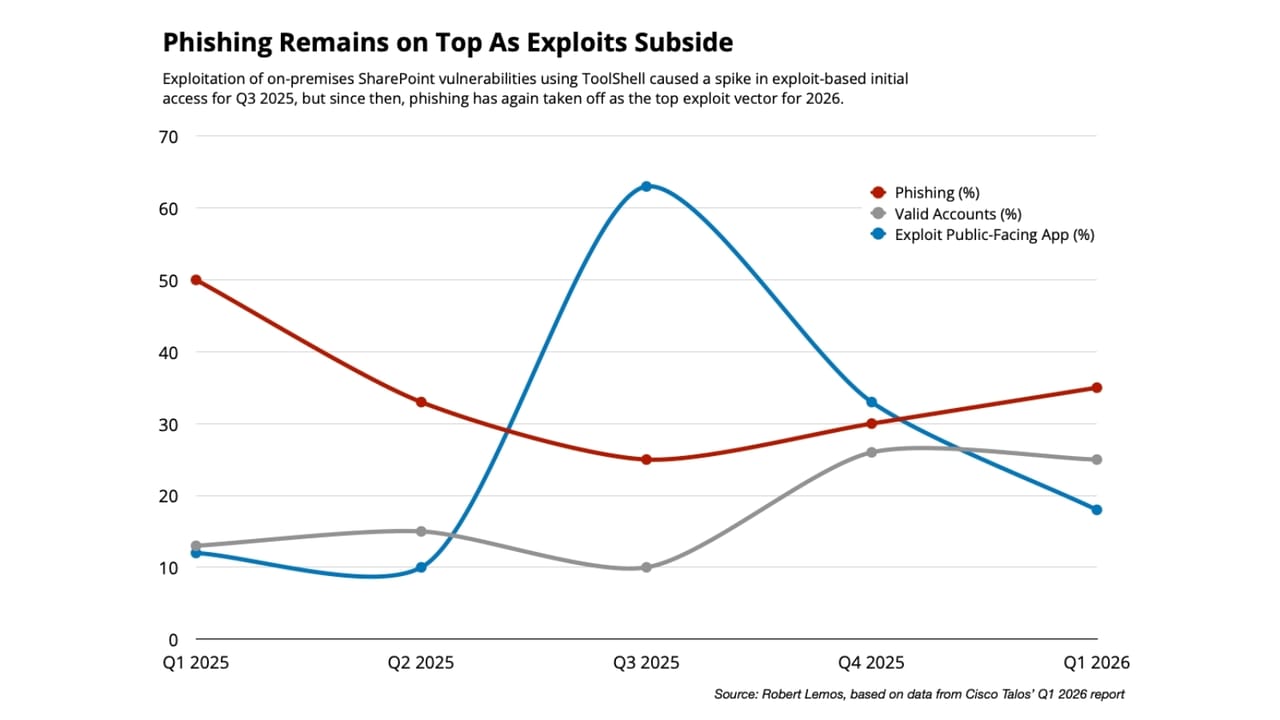
AI-generated phishing has surged to become the top initial-access vector in Q1 2026 incident-response engagements, accounting for 35% of investigated compromises and overtaking exploitation of external vulnerabilities. Attackers are using AI to craft highly personalized, polymorphic lures that abuse legitimate services and valid accounts, prompting calls for defenders to adopt AI-driven defenses and reinforce identity and MFA protections. #CiscoTalos #Gmail
The US government led coordinated actions — including sanctions, indictments, and seizures of a Telegram channel and more than 500 domains — against an organized Southeast Asian scam network tied to Cambodia powerbroker Kok An and compounds like Shunda. Operation Level Up and the Scam Center Strike Force say they disrupted nearly 9,000 crypto-fraud cases and recovered about $562 million, but experts warn trafficked, casino-backed scam compounds are resilient and likely to relocate. #OperationLevelUp #KokAn

ADT confirmed a data breach after the ShinyHunters extortion group threatened to leak stolen records unless paid, saying it detected unauthorized access on April 20 and terminated the intrusion. The company said stolen data was limited mainly to names, phone numbers, and addresses, with a small number of records including dates of birth and the last four digits of Social Security numbers or Tax IDs, and that no payment information or home security systems were affected. #ADT #ShinyHunters

Congress failed to pass an 18-month extension of Section 702 of the Foreign Intelligence Surveillance Act, instead approving only a 10-day reauthorization as lawmakers scramble for a longer solution. House Speaker Mike Johnson’s three-year extension proposal — including language barring the targeting of Americans — drew criticism from civil liberties groups who say it fails to require warrants for U.S. person searches and is largely cosmetic. #Section702 #FISA
Microsoft is rolling out Windows Update improvements that give users more control over how updates are installed while reducing disruption from frequent or poorly timed restarts. The initial Insider release adds OOBE update skipping, a 35‑day calendar pause, separate non‑update power options, clearer driver labels, and consolidated monthly restarts, and will later reach all users. #Microsoft #WindowsUpdate
U.S. and U.K. cybersecurity agencies warn that a custom backdoor called Firestarter has been found persisting on Cisco Firepower and Secure Firewall devices running ASA or FTD, allowing attackers continued access even after patches and reboots. Attributed to actor UAT-4356 and often preceded by Line Viper deployment, the implant exploits CVE-2025-20333 and/or CVE-2025-20362, hooks into the LINA process to inject shellcode via crafted WebVPN requests, and can be detected and mitigated using Cisco advisories, CISA YARA rules, or device reimaging. #Firestarter #LineViper #UAT-4356 #CVE-2025-20333 #CVE-2025-20362 #CiscoFirepower #ASA #FTD #CISA #NCSC #CiscoTalos
Senior military leaders warn that AI-driven autonomy will be integral to future warfare, creating urgent questions about how to secure and control the software and machine-learning models that may help make battlefield decisions. A public standoff with Anthropic over its Mythos Preview model — including government restrictions, intelligence access, and legal challenges — highlights supply-chain, procurement, and trust gaps the Pentagon must address. #Anthropic #MythosPreview
ADT said cybercriminals breached company systems and stole a limited set of customer and prospective customer information. An associated criminal group claiming to be ShinyHunters asserted it obtained 10 million records, threatened to leak them for ransom, and ADT has notified impacted individuals while law enforcement and third-party cyber experts investigate. #ShinyHunters #ADT
U.S. officials warn that Iranian-linked cyber actors are more likely to conduct opportunistic intrusions that exploit basic security gaps than to launch a single large-scale destructive attack. Recent incidents like the Stryker breach demonstrate attackers using social engineering and stolen credentials to log in and cause damage, often amplified by information operations. #IranianActors #Stryker
A new local privilege-escalation vulnerability dubbed Pack2TheRoot (CVE-2026-41651) in the PackageKit daemon can allow local Linux users to install or remove system packages and gain root privileges. The flaw, present since PackageKit 1.0.2 (Nov 2014) through 1.3.4, was reported by the Deutsche Telekom Red Team and fixed in PackageKit 1.3.5; users should patch immediately. #Pack2TheRoot #CVE-2026-41651