Microsoft will roll out Entra passkey support on Windows starting late April, with general availability expected by mid‑June 2026, extending phishing‑resistant passwordless sign‑ins to unmanaged, corporate, personal, and shared devices. Device‑bound FIDO2 passkeys will be stored in the Windows Hello container and managed via Conditional Access and Authentication Methods policies, closing a security gap exploited in recent Entra SSO credential‑theft attacks while preventing passkey exfiltration. #MicrosoftEntra #WindowsHello
Category: Cyber Security News
A financially motivated group tracked as BlackFile has used vishing campaigns since February 2026 to impersonate IT helpdesk staff, steal employee credentials, and demand seven-figure ransoms from retail and hospitality organizations. Using stolen credentials to register devices and abuse Salesforce and SharePoint APIs, the attackers exfiltrate confidential data to a dark web leak site and sometimes employ swatting; Unit 42 and RH-ISAC link the group to broader criminal networks. #BlackFile #Salesforce

AI agents create a delegation gap because their authority is granted by existing human and machine identities rather than arising independently. Closing this gap requires first reducing identity dark matter and then using continuous observability to drive a real-time Agent-AI delegation authority layer. #Orchid #AgentAI…

The NASA Office of Inspector General disclosed a multi-year spear-phishing campaign in which Chinese national Song Wu impersonated U.S. researchers to obtain aerospace modeling software and sensitive defense technology from NASA, government agencies, universities, and private companies. The Department of Justice indicted Song in 2024, linking him to the Aviation Industry…

CISA reported that a federal civilian agency’s Cisco Firepower device running ASA software was compromised in September 2025 by a Linux ELF backdoor named FIRESTARTER that can persist through firmware updates and normal reboots by altering the device boot sequence. The intrusion leveraged now-patched vulnerabilities (CVE-2025-20333 and CVE-2025-20362) to deliver FIRESTARTER…
Canadian police arrested three men in what authorities describe as the country’s first known criminal case involving a mobile “SMS blaster” that impersonated cellular towers to send mass phishing messages and disrupt networks. Tens of thousands of phones connected to the rogue system, police recorded over 13 million network disruptions, and the investigation remains ongoing. #SMSBlaster #TorontoPoliceService
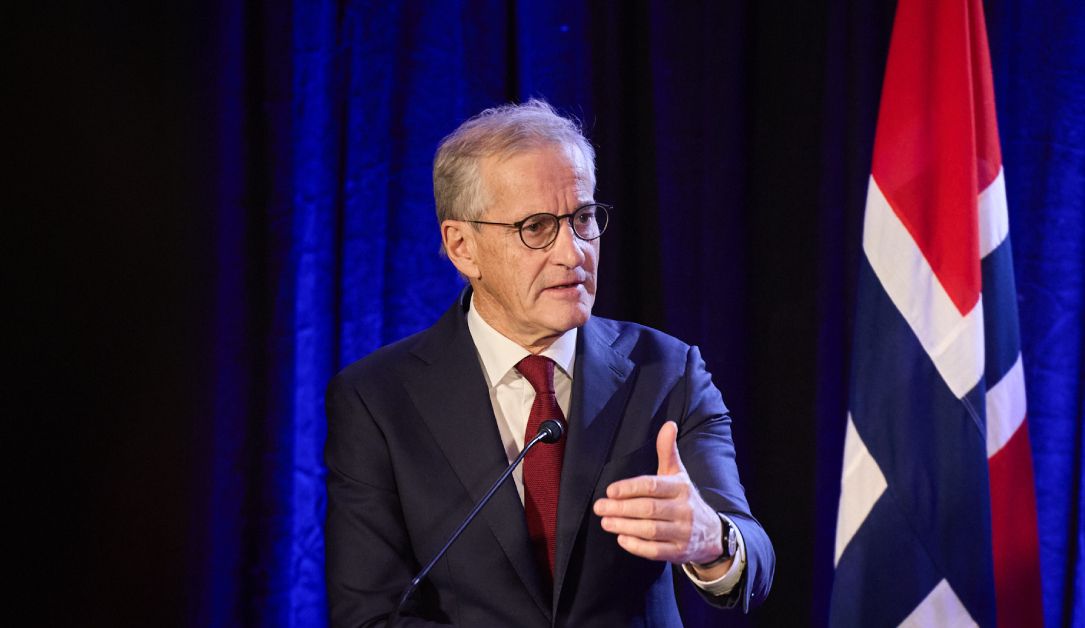
Norway’s prime minister announced a bill to ban children under 16 from using social media and to hold big tech accountable by requiring age verification tools to block young users. The proposal follows similar moves across Europe but may face uncertain passage in Norway because the Labour party does not hold a parliamentary majority. #JonasGahrStøre #EuropeanUnion
Microsoft has made the RemoveMicrosoftCopilotApp policy broadly available after the April 2026 Patch Tuesday, allowing IT administrators to uninstall the AI-powered Copilot assistant from managed enterprise devices. The policy is delivered as a Policy CSP and Group Policy for endpoints managed via Microsoft Intune or SCCM, applies to Windows 11 25H2 devices meeting specific conditions, and can be enabled under User Configuration > Administrative Templates > Windows AI > Remove Microsoft Copilot App; users may reinstall the app if they choose. #RemoveMicrosoftCopilotApp #Microsoft365Copilot
Over 10,000 Zimbra Collaboration Suite instances remain exposed and vulnerable to active exploitation of a cross-site scripting flaw tracked as CVE-2025-48700, Shadowserver warns. CISA has added the vulnerability to its KEV catalog and ordered federal agencies to patch while past XSS exploits by APT28 and APT29 show the issue is being abused in targeted phishing and mass intrusions. #Zimbra #CVE-2025-48700 #Shadowserver #CISA #APT28 #APT29
DORA Article 9 makes credential security a binding operational resilience obligation for EU financial entities, mandating phishing-resistant MFA, least-privilege access, and cryptographic key protection while treating credential compromise as an operational resilience failure that can trigger rapid reporting and supervisory action. Passwork offers a self-hosted, ISO/IEC 27001‑certified credential vault that enforces FIDO2/WebAuthn MFA, role-based access, encrypted credential storage, and tamper-evident audit logs to help institutions demonstrate compliance and manage third‑party risk. #DORA #Ficoba
In March 2026 at RSA Conference, industry leaders warned that agentic AI—systems that autonomously generate code and take actions—creates dual-use risks that empower both defenders and attackers. Experts recommended treating AI as an identity and applying identity threat detection and risk mitigation to control rogue agents and avoid fragmented point-solution sprawl….

In Other News: Unauthorized Mythos Access, Plankey CISA Nomination Ends, New Display Security Device
This week’s roundup covers a range of notable incidents, from a Tennessee hacker’s probation and a major French state agency breach to warnings about state-linked botnet infrastructure and misconfigurations at prominent tech firms. Key developments include Volt Typhoon’s router botnet, unauthorized access to Anthropic’s Claude Mythos, Lovable’s BOLA exposure, the UK’s…
SentinelOne has uncovered Fast16, a Lua-based sabotage framework predating Stuxnet that used a carrier service (svcmgmt.exe) and a kernel driver (fast16.sys) to intercept filesystem I/O and patch executables on pre-Windows 7 systems. SentinelLabs links Fast16 to a 2005 campaign referenced by the ShadowBrokers, highlights wormable propagation via weak Windows 2000/XP share…
The Bitwarden CLI NPM package was compromised in a supply chain attack that installed a loader to fetch and execute a JavaScript payload which systematically harvested credentials and secrets across local systems, CI pipelines, GitHub, and multiple cloud providers. Analysts link the incident to a broader OSS supply chain campaign related…

Daily Recap, Microsoft Edge updates disrupted Teams meetings on Windows as engineers review diagnostics while Sean Plankey withdrew from consideration to lead CISA amid workforce losses and budget strain. The recap also highlights AI security advances and a surge in threat activity, including GopherWhisper using Outlook/Slack/Discord for C2, Contagious Interview and related BeaverTail, OtterCookie, and InvisibleFerret campaigns, proxy networks by Chinese actors, and patches such as Defender CVE-2026-33825 and iOS CVE-2026-28950, plus Mirai in D-Link routers, KICS/Docker Hub supply-chain issues, CanisterSprawl, Harvester’s GoGra backdoor, and Lotus Wiper hits in Venezuela.
#GopherWhisper #ContagiousInterview #BeaverTail #OtterCookie #InvisibleFerret #GoGra #LotusWiper #TuMangaOnline #CISA #Edge #Teams