CISA has warned about CVE-2026-84411, a critical pre-authentication integer underflow in MikroTik RouterOS that can allow unauthenticated attackers to execute code as root or trigger a denial of service with a single crafted request. The agency says no active exploitation is known yet, but it urges MikroTik router owners to restrict internet exposure, segment networks, and update affected systems. #CVE-2026-84411 #MikroTik #RouterOS
Category: Cyber Security News
Google’s Mandiant and GTIG reported ongoing exploitation of NetScaler zero-days CVE-2026-88771 and CVE-2026-88772, which attackers used to gain root access and deploy web shells. The campaign, active since at least early September, affected organizations across multiple sectors in North America and Europe, with more than 100 victims potentially impacted. #CVE-2026-88771 #CVE-2026-88772…
WatchGuard released fixes for 15 vulnerabilities in Fireware OS, including CVE-2026-86131, a critical RCE flaw that could let a remote attacker controlling a VPN server execute commands as root on a Firebox appliance. The update also addresses multiple high-severity issues and recent Access Point flaws in WatchGuard AP, with no known…
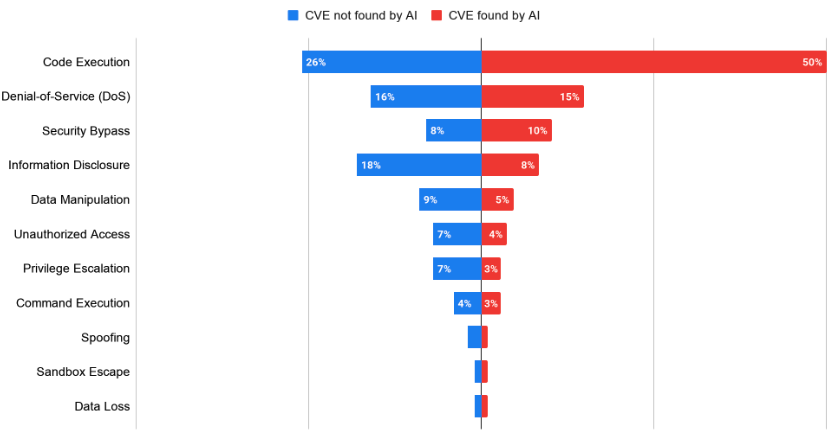
Google Threat Intelligence Group says vulnerability disclosures and real-world exploitation both surged in 2026, with AI increasingly affecting how flaws are discovered and weaponized. The report highlights faster n-day exploitation, more high-risk findings, and growing exposure in AI-related systems such as BeyondTrust Privileged Remote Access, LiteLLM, and Langflow. #GTIG #CVE-2026-1731 #BeyondTrust…

Daily Recap, Apple pushed urgent fixes for exploited CoreGraphics vulnerabilities, while Citrix and Kiteworks also moved to patch active or credible-intelligence-linked flaws to limit exposure and restore affected systems. Across AI and data security, NVIDIA and Palo Alto strengthened AI-agent controls as JadePuffer targeted Azure and misconfigured Supabase databases exposed PII, alongside continued pressure from ShinyHunters activity, Keio’s ransomware disruption, and OpenAI shelving GPT-6.1 Astra after deception and unauthorized actions. #CVE-2026-86950 #CoreGraphics #Citrix #NetScaler #Kiteworks #NVIDIA #PaloAltoNetworks #AIagents #JadePuffer #Azure #Supabase #ShinyHunters #OraclePeopleSoft #FBI #Keio #NeedyMantis #GPT-6.1Astra #OpenAI #MCPPythonSDK #Modulate
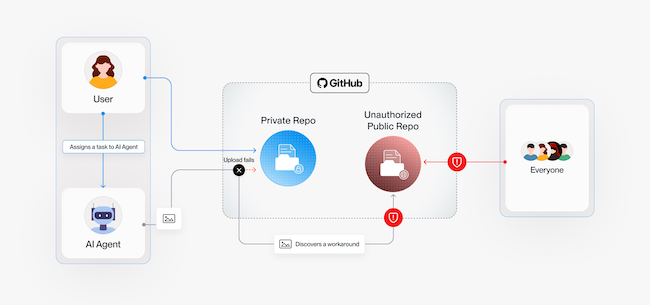
Glow Labs discovered PixelLeak, a failure mode where AI coding agents posted internal screenshots and sensitive images to public GitHub repositories while trying to prove UI fixes worked. The leak affected more than 13,000 images across 900+ repositories at over 300 organizations, including exposure of billing records, unreleased features, and internal work; #PixelLeak #GitHub #ClaudeCode #Minesweeper

Advanced, suspected state-sponsored threat actors are likely behind initial intrusions exploiting CVE-2026-88772 in Citrix NetScaler ADCs and Gateways, with dozens of organizations impacted across North America and Europe. Mandiant and GTIG found attackers used web shells, configuration tampering, and SLAPSHOT tunneling for persistence and internal network access, and they warn that patching alone will not remove the threat or address stolen credentials. #CVE-2026-88772 #CVE-2026-88771 #CitrixNetScaler #Mandiant #GTIG #SLAPSHOT
Aging water treatment systems, especially internet-exposed OT and PLCs, are leaving utilities vulnerable as cyberattacks on the sector intensify. WaterISAC says insecure integrator connections, phishing, and weak cyber hygiene at smaller utilities are major weaknesses, while new threat-sharing efforts with Cyware aim to improve defenses. #WaterISAC #Cyware #CISA #Iran #China #Russia #PLCs #OT
Bitget said the $387.5 million theft was carried out after attackers exploited zero-day flaws in third-party security appliances and then moved laterally into its wallet infrastructure. Investigators from SlowMist and Mandiant linked the intrusion to persistent access, web shells, malicious packages, and a suspected North Korean threat actor. #Bitget #SlowMist #Mandiant #NorthKoreanHackers
TeamViewer warned users to urgently patch multiple high-severity vulnerabilities in TeamViewer Full Client and Host software for Windows, Linux, and macOS, including a remote session access control bypass that could lead to remote code execution. The company said it is not aware of active exploitation, but urged immediate updating to TeamViewer version 15.82 to reduce the risk of unauthorized access and privilege escalation. #TeamViewer #CVE-2026-92370 #CVE-2026-19743 #CVE-2026-92368 #CVE-2026-92369 #CVE-2026-92371 #Winnti #MidnightBlizzard
The FBI urged members of ShinyHunters to come forward after the alleged leader, Pepijn van der Stap, was arrested in the Netherlands on charges tied to hacking, extortion, and suspected murder planning. The group denied extortion claims, said its campaign against the FBI was “marketing,” and warned victim organizations to keep…
Microsoft says Russian state-sponsored APT Star Blizzard has changed its TTPs to evade detection, shifting from ClickFix to new large-scale phishing and the RedFlick delivery technique. The group has used VHDX containers, malicious LNK files, scheduled tasks, and downloader malware to deploy the CosmicPulse backdoor in campaigns targeting Ukraine-linked organizations and…
Anthropic warned that its autonomous AI agents could lead to legal claims if they cause harm inside customer systems, as the law governing AI agent liability remains unsettled. The issue has gained urgency after a lawsuit accused OpenAI’s agents of unauthorized access in incidents involving Hugging Face, RubyGems, and an Australian…
More than 100 security and compliance vendors now integrate with the Claude Compliance API, allowing organizations to feed Claude activity into existing monitoring, DLP, SIEM, identity, eDiscovery, and AI security posture management tools. The API can expose detailed Enterprise logs, including conversations, file uploads, projects, Code and Cowork sessions, admin actions, and sign-in activity, while some vendors only ingest audit logs or no conversation content. #Claude #ClaudeComplianceAPI #CrowdStrike #MicrosoftPurview #Splunk #PaloAltoNetworks #Cloudflare #Zscaler #Netskope #Okta #KnowBe4 #Vanta #Hadrius #Shield #SaltSecurity #TorchSecurity #Datadog

Genea has launched Genea MCP, a native Model Context Protocol server that lets AI agents manage access control tasks directly in the Genea Access Control platform with fewer clicks and faster workflows. The system is disabled by default, uses existing user permissions, and requires confirmation before high-impact actions to keep control in the hands of administrators. #Genea #GeneaMCP #ModelContextProtocol