Two men, Chijioke Timothy Odimegwu and Harafat Mogaji, were sentenced to a combined 189 months in federal prison for running BEC and phishing campaigns against US businesses while serving in the Air Force. Their scheme stole credentials and financial data, diverted large wire transfers, and involved victims in Iowa, Ohio, and a nonprofit in Pella, Iowa. #ChijiokeTimothyOdimegwu #HarafatMogaji #FBI #IowaCity #Pella #ATandT #Snowflake
Category: Cyber Security News

Cybersecurity researchers disclosed technical details of CVE-2026-88772, a critical Citrix NetScaler ADC and Gateway flaw that is being actively exploited in the wild. The bug is a DTLS-related memory overflow in the NetScaler Packet Processing Engine and can lead to remote code execution or denial-of-service. #CVE-2026-88772 #CitrixNetScaler #NetScalerADC #NetScalerGateway #NSPPE…
President Donald Trump and leaders from major AI companies signed a voluntary accord at the White House that calls for internal controls, external audits, and board-level oversight of AI systems. The agreement comes as the administration promotes AI growth through new tools like America.gov, while critics warn that self-policing may not…
OpenSSL and WolfSSL have released patches for a combined 25 vulnerabilities, including multiple high-severity flaws that could enable memory disclosure, denial of service, and authentication bypass. The most serious issues affect DTLS, TLS, and certificate validation paths, putting VPNs, VoIP, IoT products, and software using Nginx, HAProxy, Stunnel, and Apache httpd…
Malicious custom ChatGPT variants promoted in sponsored Google results are luring users to fake backup sites that trigger ClickFix attacks and install malware through PowerShell commands. Huntress says the campaign used OpenAI-hosted GPTs like “Plus 5.6” and delivered a RAT with persistence via Windows Run keys and scheduled tasks. #OpenAI #ChatGPT #Plus5.6 #Huntress
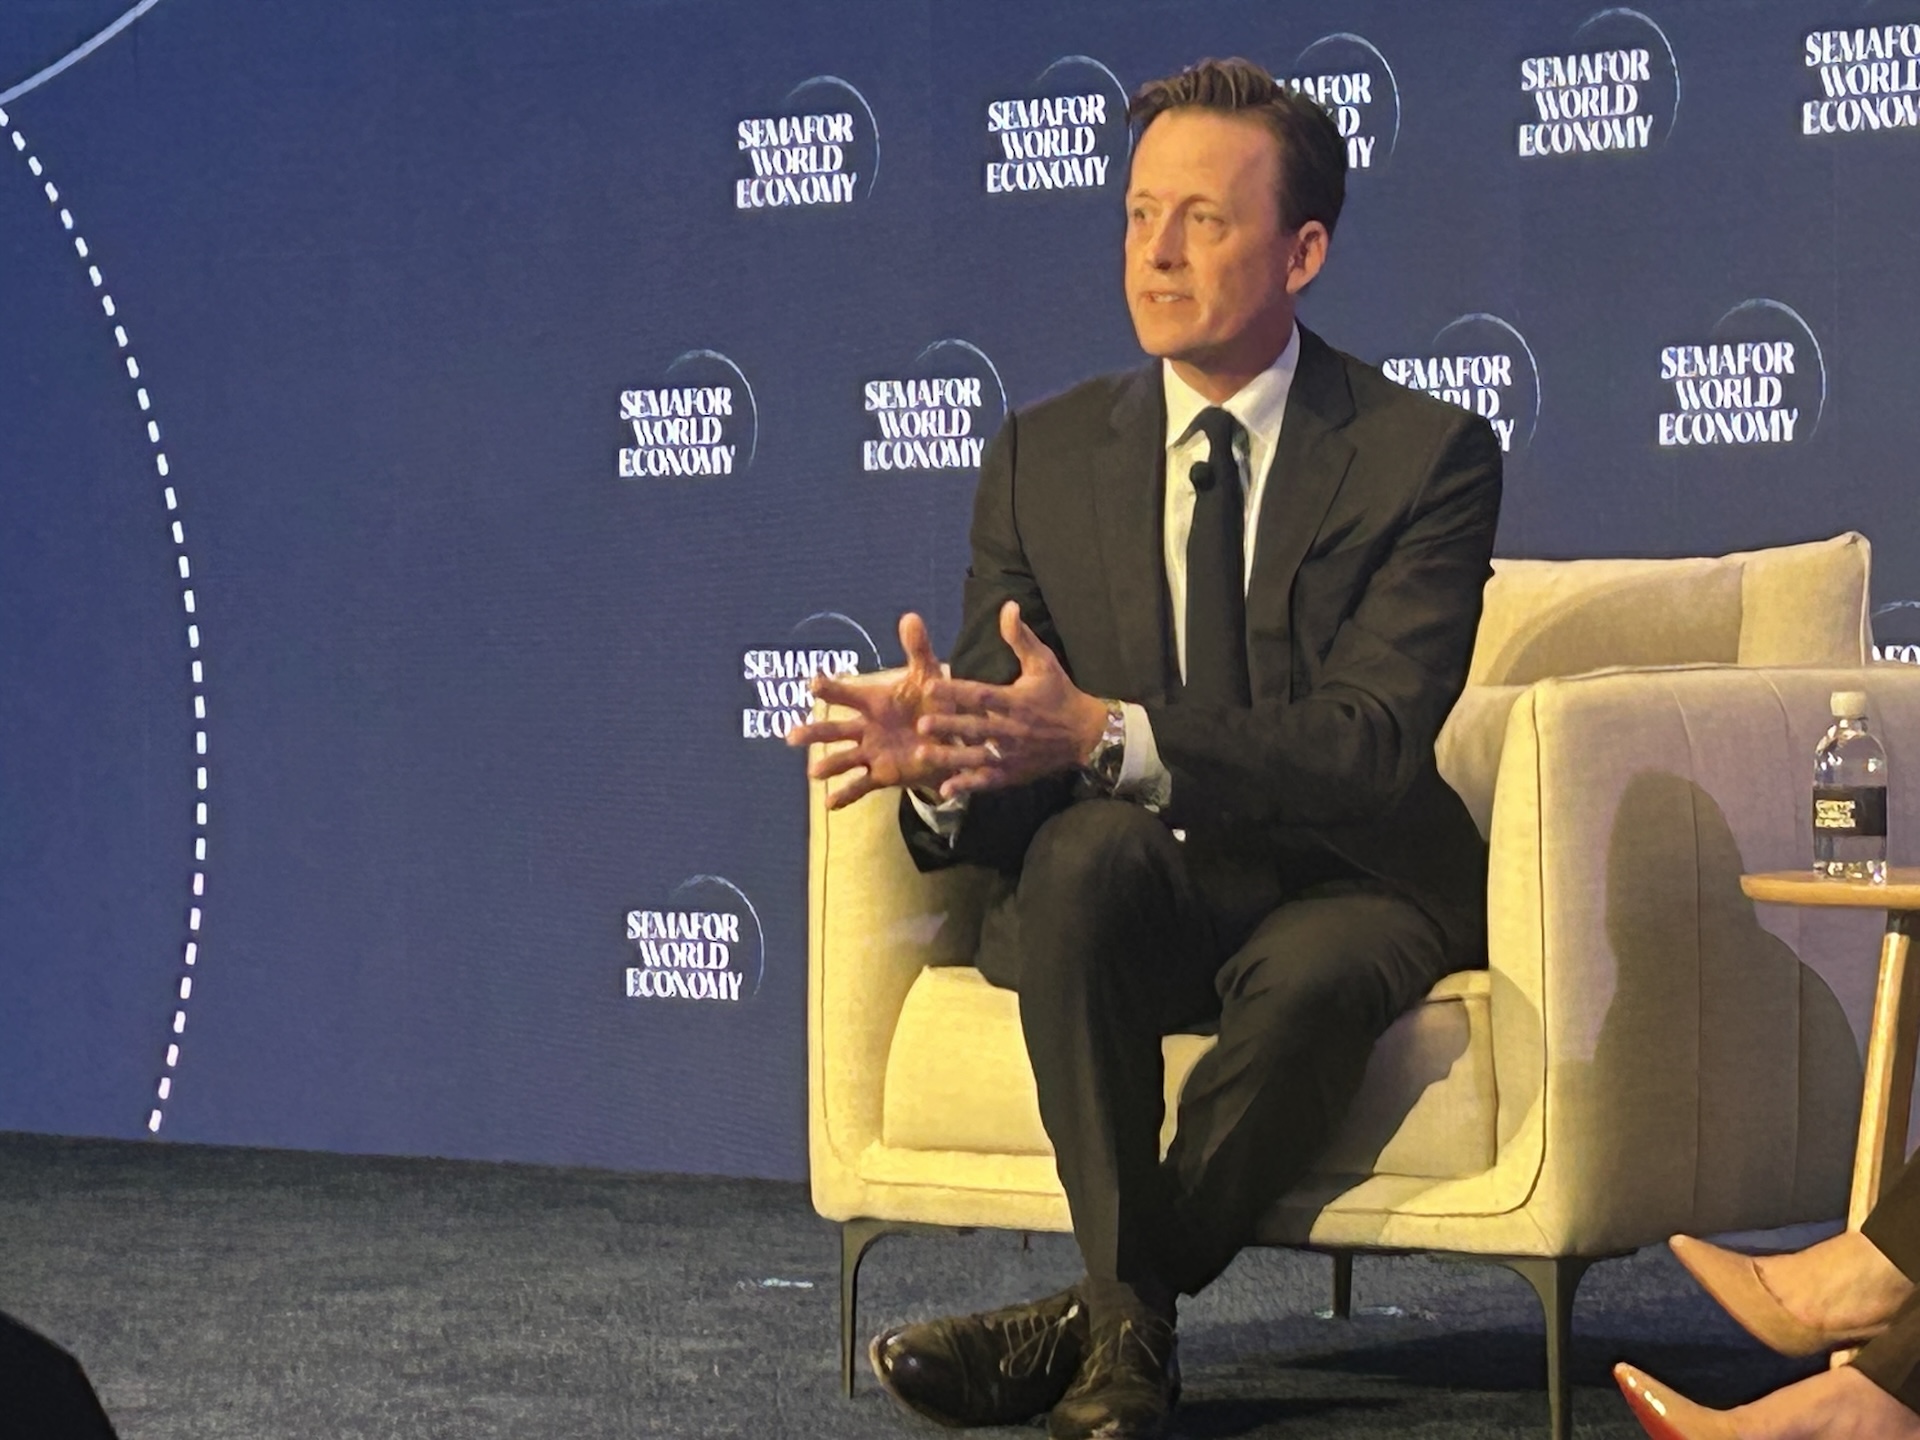
The U.S. government is partnering with critical infrastructure operators to deploy AI across essential systems and improve cyber defenses, according to National Cyber Director Sean Cairncross. He also stressed the need for visibility into AI agents and supply chain access, while noting ongoing debates over regulation, innovation, and replacing outdated systems. #SeanCairncross #USTelecom #Mythos #WhiteHouse #DonaldTrump #JDVance #MikeJohnson
Microsoft says Russian FSB-linked Star Blizzard has expanded from targeted spear-phishing to larger-scale phishing campaigns using the RedFlick delivery method and CosmicPulse backdoor. The activity has hit more than 100 organizations, with a focus on Ukraine, NGOs, think tanks, governments, and supporters of Ukraine in the U.S. and U.K. #StarBlizzard #FSB #RedFlick #CosmicPulse #Ukraine
Attackers exploited a critical zero-day in Citrix NetScaler appliances for more than three weeks before detection, compromising organizations across government, finance, education, telecom, legal, and professional services sectors in North America and Europe. Mandiant and Citrix also disclosed a second actively exploited NetScaler flaw, with researchers warning of broad and opportunistic exploitation by suspected state-sponsored threat actors. #Citrix #NetScaler #CVE-2026-88772 #CVE-2026-88771 #Mandiant
Signal released version 8.30, completing the rollout of its secure backups feature across Android, iOS, Linux, macOS, and Windows. The update expands encrypted backup and restore options, while also adding cross-device transfer improvements and new storage efficiency controls. #Signal #Signal8.30
Microsoft has made WSL Containers generally available, adding a new wslc.exe command and a container.exe alias for building, running, and deploying Linux containers on Windows. The release also brings enterprise controls through Microsoft Defender for Endpoint and Intune, plus support from VS Code Dev Containers, Aspire, and the VS Code Containers extension. #WSLContainers #MicrosoftDefenderforEndpoint #MicrosoftIntune #VSCode #Aspire
A new Spectre v2 variant called Branch Target Reuse (BTR) can recover root password hashes from Intel Linux systems in just a few minutes by abusing stale branch-predictor state left behind after JIT code reuse. Researchers from VUSec and Scuola Superiore Sant’Anna demonstrated the attack against Linux cBPF, Firefox SpiderMonkey, and Oracle GraalVM, and Linux kernel fixes have already been merged for CVE-2026-64507 and CVE-2026-64508. #BTR #VUSec #SpiderMonkey #GraalVM #LinuxKernel #CVE-2026-64507 #CVE-2026-64508
Microsoft has begun rolling out the Windows 11 2026 Update (26H2), which is based on the same servicing branch as 24H2 and 25H2, so most users will see it as a small enablement update rather than a major OS overhaul. The update mainly activates features already delivered through monthly Windows Updates and resets support lifecycles, while devices running Windows 11 26H1 cannot upgrade directly to 26H2. #Windows11 #26H2 #26H1 #Microsoft
Two former U.S. Air Force members were sentenced for carrying out multi-year business email compromise and phishing schemes that stole credentials and rerouted corporate wire transfers. Their fraud helped divert more than $2.4 million from victims, with the Justice Department and FBI warning that BEC remains a major source of financial loss. #ChijiokeTimothyOdimegwu #HarafatMogaji #DoverAirForceBase #BusinessEmailCompromise
Attackers exploited Citrix NetScaler CVE-2026-88772 and CVE-2026-88771 zero-days to deploy web shells, tunneling malware, steal credentials, and move deeper into internal networks. Mandiant and GreyNoise say the campaign affected organizations across North America and Europe, with persistent post-exploitation tactics including root access abuse and the use of WHIPSHOT and SLAPSHOT. #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772 #Mandiant #GreyNoise #WHIPSHOT #SLAPSHOT
The FBI is urging remaining ShinyHunters members to surrender after Dutch police arrested a 24-year-old alleged leader linked to the extortion group’s global cyberattacks. The group is accused of breaching more than 140 organizations, including the FBI itself, while targeting platforms like Salesforce, Snowflake, and Oracle PeopleSoft. #ShinyHunters #FBI #DutchNationalPolice #OraclePeopleSoft #Salesforce #Snowflake