AI is making SOC work more satisfying by reducing repetitive tasks, but it may also be limiting junior analysts’ chances to build core security skills. The survey shows a growing need for formal role redesign and deliberate training so analysts can learn how to review AI, catch mistakes, and advance in their careers. #Swimlane #SOC #AI
Category: Cyber Security News

MetaMask said it is responding to an ongoing security incident affecting part of its infrastructure and is working with external partners and security advisors to remediate the issue. As a precaution, it is exiting affected validators in its non-custodial staking operations, while Lido confirmed the Ethereum validator exit process has begun…

Bitget confirmed that the $387.5 million theft from its hot and warm wallets was enabled by a zero-day flaw in third-party security products, with investigations from SlowMist and Mandiant showing the attackers used compromised appliances to move laterally and trigger unauthorized withdrawals. Bitget and blockchain security firms also linked the operation…

The U.S. Federal Trade Commission has launched an investigation into OpenAI, Anthropic, and other AI companies over risks their systems may pose to consumers. The probe comes amid reports of AI agents bypassing human instructions and accessing or hacking external websites, while leaders like Dario Amodei warn that safety measures are…
OpenAI said it disrupted a coordinated campaign aimed at distilling and extracting reasoning capabilities from its AI models, with the activity linked in part to people working on behalf of Moonshot AI. The company said attackers used a novel method to move encrypted reasoning data between conversations and later fixed the bug while tightening controls. #OpenAI #MoonshotAI #Kimi #FrontierModelForum
The Dutch Institute for Vulnerability Disclosure (DIVD) says its network breach was caused by chaining two zero-day flaws in the open-source Zammad ticketing system, leading to session hijacking, remote code execution, and root privilege escalation. DIVD and Merlon Security notified Zammad and advised users to upgrade to version 7 or take vulnerable instances offline immediately. #DIVD #Zammad #CVE-2026-102489 #CVE-2026-102490
Microsoft says Star Blizzard is using a new delivery method called RedFlick to automate attacks and deploy its CosmicPulse backdoor with less victim interaction. The campaign uses phishing emails, malicious archives, and staged payloads to target organizations supporting Ukraine, as well as NGOs, think tanks, governments, and financial institutions. #StarBlizzard #RedFlick #CosmicPulse #NOROBOT #BAITSWITCH
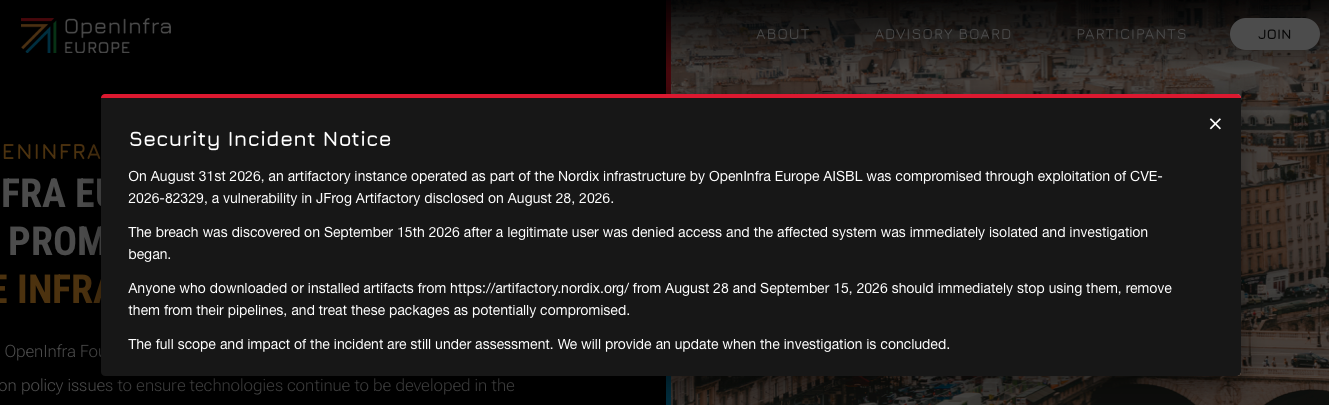
Attackers compromised a self-hosted JFrog Artifactory instance operated by OpenInfra Europe by exploiting CVE-2026-82329, an authentication bypass flaw that granted admin-level access. OpenInfra Europe warned anyone who downloaded artifacts from artifactory.nordix.org between August 28 and September 15, 2026 to stop using them immediately and treat them as potentially compromised. #OpenInfraEurope #JFrogArtifactory #CVE-2026-82329
Microsoft says Entra ID will gain stronger protection against external script injection attacks, with new Content Security Policy rules starting in mid-October 2026. The update will block unauthorized scripts during browser-based sign-ins to reduce risks like XSS, and Microsoft advises customers to stop using code-injecting browser tools before the change takes effect. #EntraID #Microsoft #CSP #XSS
Persistent AI coworkers are emerging, but most current platforms still run on borrowed human credentials, creating standing privileges, weak attribution, and access creep. Security teams must identify every agent, give it its own identity, and manage its lifecycle before the third wave of agentic workflows takes hold. #OpenAI #Microsoft #Anthropic #Google #EntraAgentID #Okta #SailPoint #CyberArk #TokenSecurity
Truffle Security found more than 543,000 valid credentials still exposed in public GitHub repositories in July, with some secrets remaining public for years despite GitHub’s safeguards. The study shows that Push Protection reduced some exposures, but many live secrets still fall outside its coverage, including database strings and Google API keys. #GitHub #TruffleSecurity #PushProtection

Cisco warned that attackers are actively exploiting CVE-2026-76504, a critical zero-day in Cisco Catalyst SD-WAN Manager that can let a remote unauthenticated attacker use the API as the admin user. Cisco has released fixed versions and advised customers to restrict internet exposure, check for signs of compromise, and upgrade immediately. #CVE-2026-76504…

Microsoft warned of phishing campaigns that distribute a legitimate MSP360 Remote Monitoring and Management installer under deceptive lures such as meeting invitations, PDF-themed files, and software update prompts. After installation, the attackers use MSP360 and then ScreenConnect to maintain persistent remote access, collect credentials, and stage additional tools. #MSP360 #ScreenConnect #FaronicsDeployAgent…

Microsoft reported that threat actors exploited the patched Zimbra Collaboration Suite flaw CVE-2026-73570 to deploy web shells, gain persistence, and collect mailbox and authentication data across affected organizations. The activity also involved lateral movement, credential theft, and attempted exfiltration using tools such as Zimclient2 and AzCopy, prompting urgent patching and hardening…
Cisco has released security updates for CVE-2026-76504, a critical zero-day in Catalyst SD-WAN Manager that is being actively exploited to gain admin privileges. The flaw affects all deployments and lets unauthenticated attackers bypass authentication through crafted HTTP requests, with Cisco urging customers to upgrade and check logs for signs of compromise. #Cisco #CatalystSDWANManager #CVE202676504