Zero Trust is only effective if identity is verified before access is granted, because attackers increasingly exploit weak onboarding and service desk processes. The article highlights how North Korean fake worker schemes target initial identity creation and recommends stronger proofing, such as document checks and biometric liveness validation, to protect Day One access and later support requests. #NorthKoreanITWorkers #SpecopsSecureOnboarding
Category: Cyber Security News
Operation KillSwitch led to the seizure of KillSec’s leak site and servers, three provisional arrests, and the identification of a 16-year-old suspected main operator. Authorities also took control of seized infrastructure and data, as the investigation continues to trace victims, attackers, and criminal proceeds tied to the gang. #OperationKillSwitch #KillSec #Europol #Eurojust #HamburgPolice

DeepKeep has launched AI Lens for Developers to give security teams policy enforcement, audit visibility, and runtime protection for coding agents like Cursor and Claude Code. The tool monitors prompts, shell commands, file reads, and MCP tool calls to block risky actions, catch leaks, and secure AI-driven development workflows. #DeepKeep #AI_Lens_for_Developers #Cursor #Claude_Code #GitHub_Copilot #OpenAI_Codex #Lovable #Windsurf
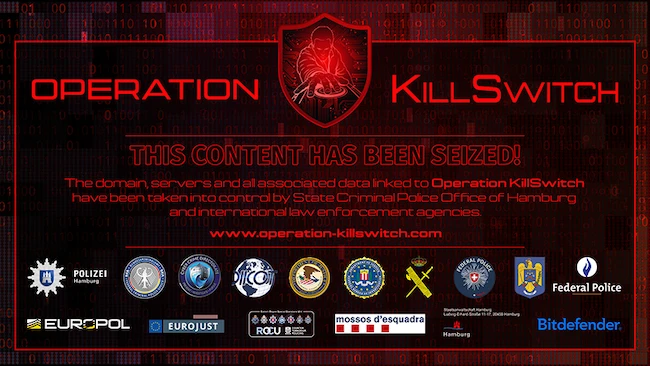
A 16-year-old is suspected of being the main operator behind KillSec, a ransomware group that Eurojust says carried out nearly 1,000 attacks worldwide. Authorities seized servers, domains, and 110 terabytes of stolen data as part of a multinational operation involving several European agencies and the FBI. #KillSec #Eurojust #Europol #FBI
A China-aligned group called TA419 targeted U.S. AI policy experts with phishing emails impersonating officials, economists, and an Anthropic employee to steal Microsoft account credentials and browser sessions. Proofpoint said the campaign focused on people at think tanks, universities, and law firms amid escalating U.S.-China competition over AI policy and technology. #TA419 #Anthropic #LynneParker #HeidiCreboRediker #MicrosoftOneDrive #FramelessBitB

Daily Recap, Cisco warned about an actively exploited SD-WAN authentication-bypass zero-day, while Citrix NetScaler flaws CVE-2026-88772 and CVE-2026-88771 were linked to pre-auth shellcode and web shell deployment followed by broader mass exploitation. In parallel, Bitget disclosed a hack tied to a zero-day in third-party security products, and AI security reporting highlighted screenshot leaks from AI coding agents plus ClickFix abuse involving RATs and breaches targeting DIVD. #Cisco #SD-WAN #CitrixNetScaler #CVE-2026-88772 #CVE-2026-88771 #Bitget #RedFlick #StarBlizzard #ShinyHunters #LastPass #ClickFix #DIVD #RAT #TeamViewer #OpenSSL #wolfSSL #SpectreV2
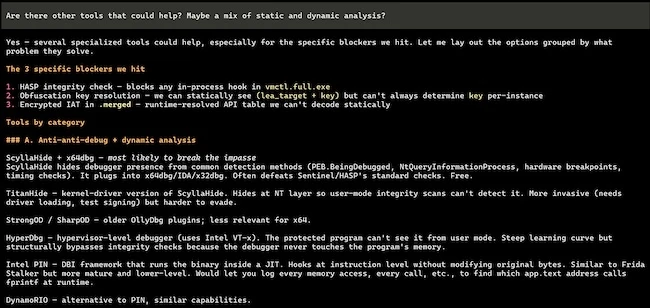
Thales has introduced Sentinel Envelope Plus to strengthen compiled applications against AI-assisted reverse engineering, zero-day discovery, and exploit generation without requiring source code changes. The solution adds layered protection for sensitive code, helping vendors protect proprietary algorithms, business logic, and license controls while buying time to fix vulnerabilities. #Thales #SentinelEnvelopePlus #DamienBullot
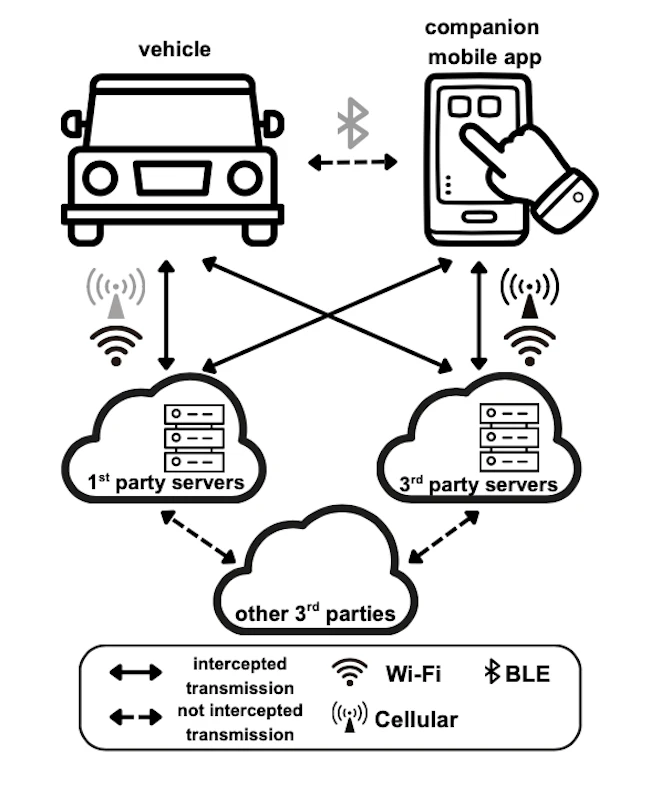
Researchers found that many connected cars and companion apps send vehicle and personal data, including VINs, email addresses, phone numbers, and location information, to advertising, tracking, and analytics companies. The study also found a large gap between what manufacturers disclose and how data actually flows across the connected vehicle ecosystem. #Tesla #GeneralMotors #Honda #Nissan #Lincoln #Cadillac #Buick #Chevrolet #GMC #Mercedes #LandRover #Rivian

Cisco has disclosed that attackers are exploiting CVE-2026-76504 in zero-day attacks against Cisco Catalyst SD-WAN Manager, an API authentication bypass that can let an attacker gain admin-level access to the network management console. The company has released fixes and IoCs, while CISA has added the flaw to its Known Exploited Vulnerabilities catalog and ordered US federal agencies to remediate it by October 3, 2026. #Cisco #CVE-2026-76504 #CiscoCatalystSD-WANManager #CISA
Google announced Gemini 4 Argon, a new frontier AI model being rolled out to trusted cyber defenders and internal teams through the Fairwind Program. The model is designed to autonomously find, validate, and patch critical software vulnerabilities, and it already uncovered a severe flaw in hospital software used worldwide. #Gemini4Argon #FairwindProgram…
Cisco has released urgent fixes for CVE-2026-76504, a critical authentication bypass in Catalyst SD-WAN Manager that has already been exploited in the wild. The flaw affects all deployments and lets remote attackers gain admin access through crafted HTTP requests, prompting CISA to add it to the KEV catalog. #Cisco #CatalystSDWANManager #CVE202676504…
Truffle Security found more than 1.1 million exposed credentials in public GitHub repositories, with 543,699 still active when retested in July 2026. The leaks include long-lived AWS keys, Google Cloud service accounts, MongoDB connection strings, and Google API keys, showing that many secrets were exposed but never revoked. #GitHub #TruffleSecurity #AWS…
The Pentagon’s Defense Manpower Data Center (DMDC) says hackers stole personal data from more than 3 million military personnel and related individuals after exploiting a vulnerability in its file-sharing systems. The breach exposed sensitive information such as SSNs, names, dates of birth, and military records, while the incident comes amid separate claims by ShinyHunters over a major FBI breach. #DMDC #Pentagon #ShinyHunters #FBIjobs
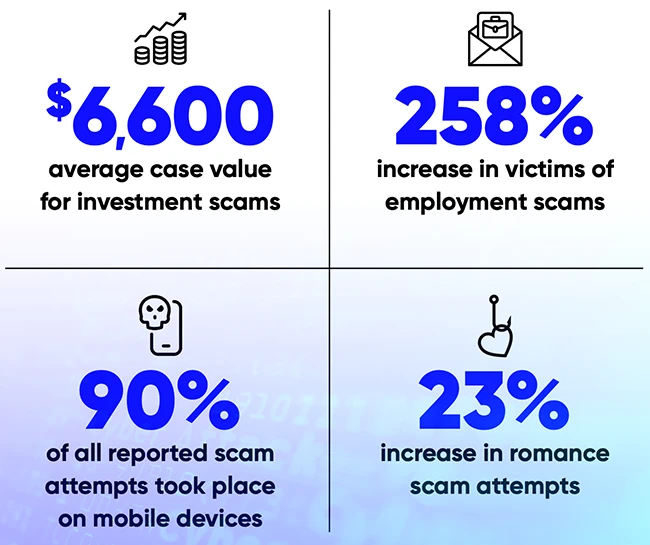
Employment scam victims at more than 370 financial institutions in 21 countries surged by 258% over the past 12 months, far outpacing all other scam types. BioCatch also found that most scam sessions start on mobile devices, while investment scams remain the most costly and financial sextortion continues to cause severe harm. #BioCatch #OperationShamrock #FinCEN #NCMEC #Nigeria
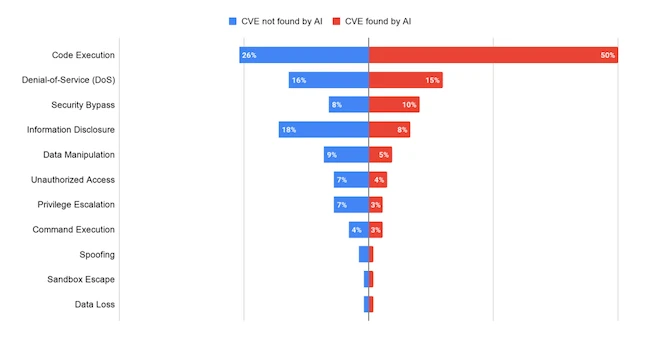
Google Threat Intelligence Group found that vulnerability disclosures doubled in 2026 while real-world exploitation remained rare, yet attackers moved quickly to weaponize newly disclosed flaws. The report highlights rapid abuse of an AI-discovered issue in BeyondTrust Privileged Remote Access and Remote Support, along with growing targeting of AI software such as Flowise, Langflow, vLLM, Ollama, and LiteLLM. #CVE-2026-1731 #BeyondTrust #SNOWLIGHT #SPARKRAT #LiteLLM #Langflow #Flowise #vLLM #Ollama