Cyberattacks on open-source software are intensifying, exposing how hard it is to secure code that underpins much of the digital world and is often maintained by small teams or volunteers. Government efforts that gained momentum after Log4j have stalled under the Trump administration, while AI-driven vulnerability discovery and mounting supply-chain compromises increase the pressure on companies and policymakers to act. #Log4j #CISA #OpenSourceSoftwareSecurityInitiative #ProjectGlasswing #cURL
Category: Cyber Security News

The U.S. Department of Justice seized a cloud computing account used by HuiOne Group subsidiaries, including HuiOne Guarantee, which helped power a massive Telegram-based criminal marketplace tied to fraud, money laundering, and scam operations. The Treasury also imposed new sanctions on Prince Group-linked individuals and entities as authorities continue targeting Southeast…

A recently patched Cisco Unified CM flaw tracked as CVE-2026-20230 is now being actively exploited, with attackers using a PoC to trigger SSRF, arbitrary file writes, and potential root privilege escalation. Cisco has not yet confirmed in-the-wild exploitation, but Defused observed attacks and SSD Secure Disclosure later published technical details and…
AI is compressing the time from vulnerability discovery to working exploit from weeks to hours, making traditional patch-and-pentest cycles too slow for today’s threat landscape. The content urges organizations to validate exposures in real time with evidence-based decisions across attack surfaces, including restricted and air-gapped assets. #CVE #Patch #Pentest #BAS…
Cisco Unified Communications Manager and Unified CM SME are being targeted in active attacks exploiting CVE-2026-20230, a high-severity SSRF flaw that can lead to file writes and root access. Defused says the current activity appears to be reconnaissance, while SSD Secure has published technical details and a proof-of-concept for the vulnerability. #CVE-2026-20230 #CiscoUnifiedCommunicationsManager #UnifiedCM #UnifiedCMSME #WebDialer

President Trump’s June 22 executive order sets firm deadlines for federal agencies to migrate high-value assets and high-impact systems to post-quantum cryptography, with key establishment due by December 31, 2030 and digital signatures by December 31, 2031. The order responds to the “harvest now, decrypt later” threat and accelerates the federal…

AIR created a fake AI agent skill called brand-landingpage and used GitHub stars, a marketplace merge, and an Instagram ad to make it look trustworthy, eventually reaching about 26,000 agents. The experiment showed that scanners from Cisco, NVIDIA, and skills.sh missed the threat because the malicious logic lived behind an external…
Anthropic’s Mythos AI model reportedly found vulnerabilities in sensitive U.S. government computer systems during a testing exercise conducted with U.S. intelligence agencies. The results have intensified debate over AI security controls and the Trump administration’s restrictions on Anthropic’s Fable 5 and Mythos 5 models. #Anthropic #Mythos #Fable5 #Mythos5 #ProjectGlasswing…

Daily Recap, LastPass confirmed its breach was tied to the Klue supply-chain compromise, while ShapedPlugin WordPress Pro plugins were backdoored in a separate supply-chain attack; London Hydro and Xsolis also disclosed large-scale data exposures. Across other headlines, the FortiBleed campaign used a custom FortiGate sniffer to steal firewall credentials, Squidbleed was shown to leak cleartext HTTP requests via Squid Proxy, and WhatsApp campaigns delivered ManageEngine RMM alongside OXLOADER and CastleStealer. #LastPass #Klue #ShapedPlugin #LondonHydro #Xsolis #FortiBleed #FortiGate #FortiGateSniffer #Russian #Squidbleed #SquidProxy #SamsungKNOX #Galaxy #WhatsApp #ManageEngineRMM #VBScript #OXLOADER #CastleStealer #JaredFromSubway #SearchYourTarget #DifyTap #Dify #AutoGenStudio #FFmpeg #PixelSmash #SAVE #postquantum #Windows1126H2 #DeepInstinct

A Russian-speaking initial access broker is behind FortiBleed, a large-scale credential-harvesting campaign that has targeted more than 430,000 FortiGate firewalls and also affected Synology NAS, Sophos firewalls, RDWeb portals, Citrix SSL-VPNs, and MS-SQL servers. The operation uses mass scanning, brute-forcing, and the FortigateSniffer tool to steal credentials and hashes, then crack…
Zafran Security found four vulnerabilities in Dify, a popular open source LLMOps platform, that could let attackers siphon data across tenants in cloud deployments. The flaws, dubbed DifyTap and tracked as CVE-2026-41947, CVE-2026-41948, CVE-2026-41949, and CVE-2026-41950, were patched in Dify version 1.14.2. #Dify #DifyTap #CVE-2026-41947 #CVE-2026-41948 #CVE-2026-41949 #CVE-2026-41950…

Dragos has launched EmberAI, an AI built specifically for OT cybersecurity that uses the company’s decade-long Intelligence Fabric to provide context-aware threat and risk insights. The platform lets analysts query in plain language while keeping humans in control, with transparent recommendations and customer data remaining inside the Dragos environment. #Dragos #EmberAI…

An Algerian man known as “SPOX” was extradited from Spain and charged in the United States for allegedly running a black-market cybercrime operation that sold phishing kits, stolen credentials, and other fraud tools through marketplaces like market0day.com and spoxy.us. Prosecutors say Abdellah Belmili helped defraud thousands of victims, created hundreds of phishing kits, and moved about $900,000 through a cryptocurrency account over three years. #SPOX #AbdellahBelmili #market0day.com #spoxy.us #JPMorganChase #BankofAmerica #PayPal #WellsFargo #CashApp #AmericanExpress #Binance
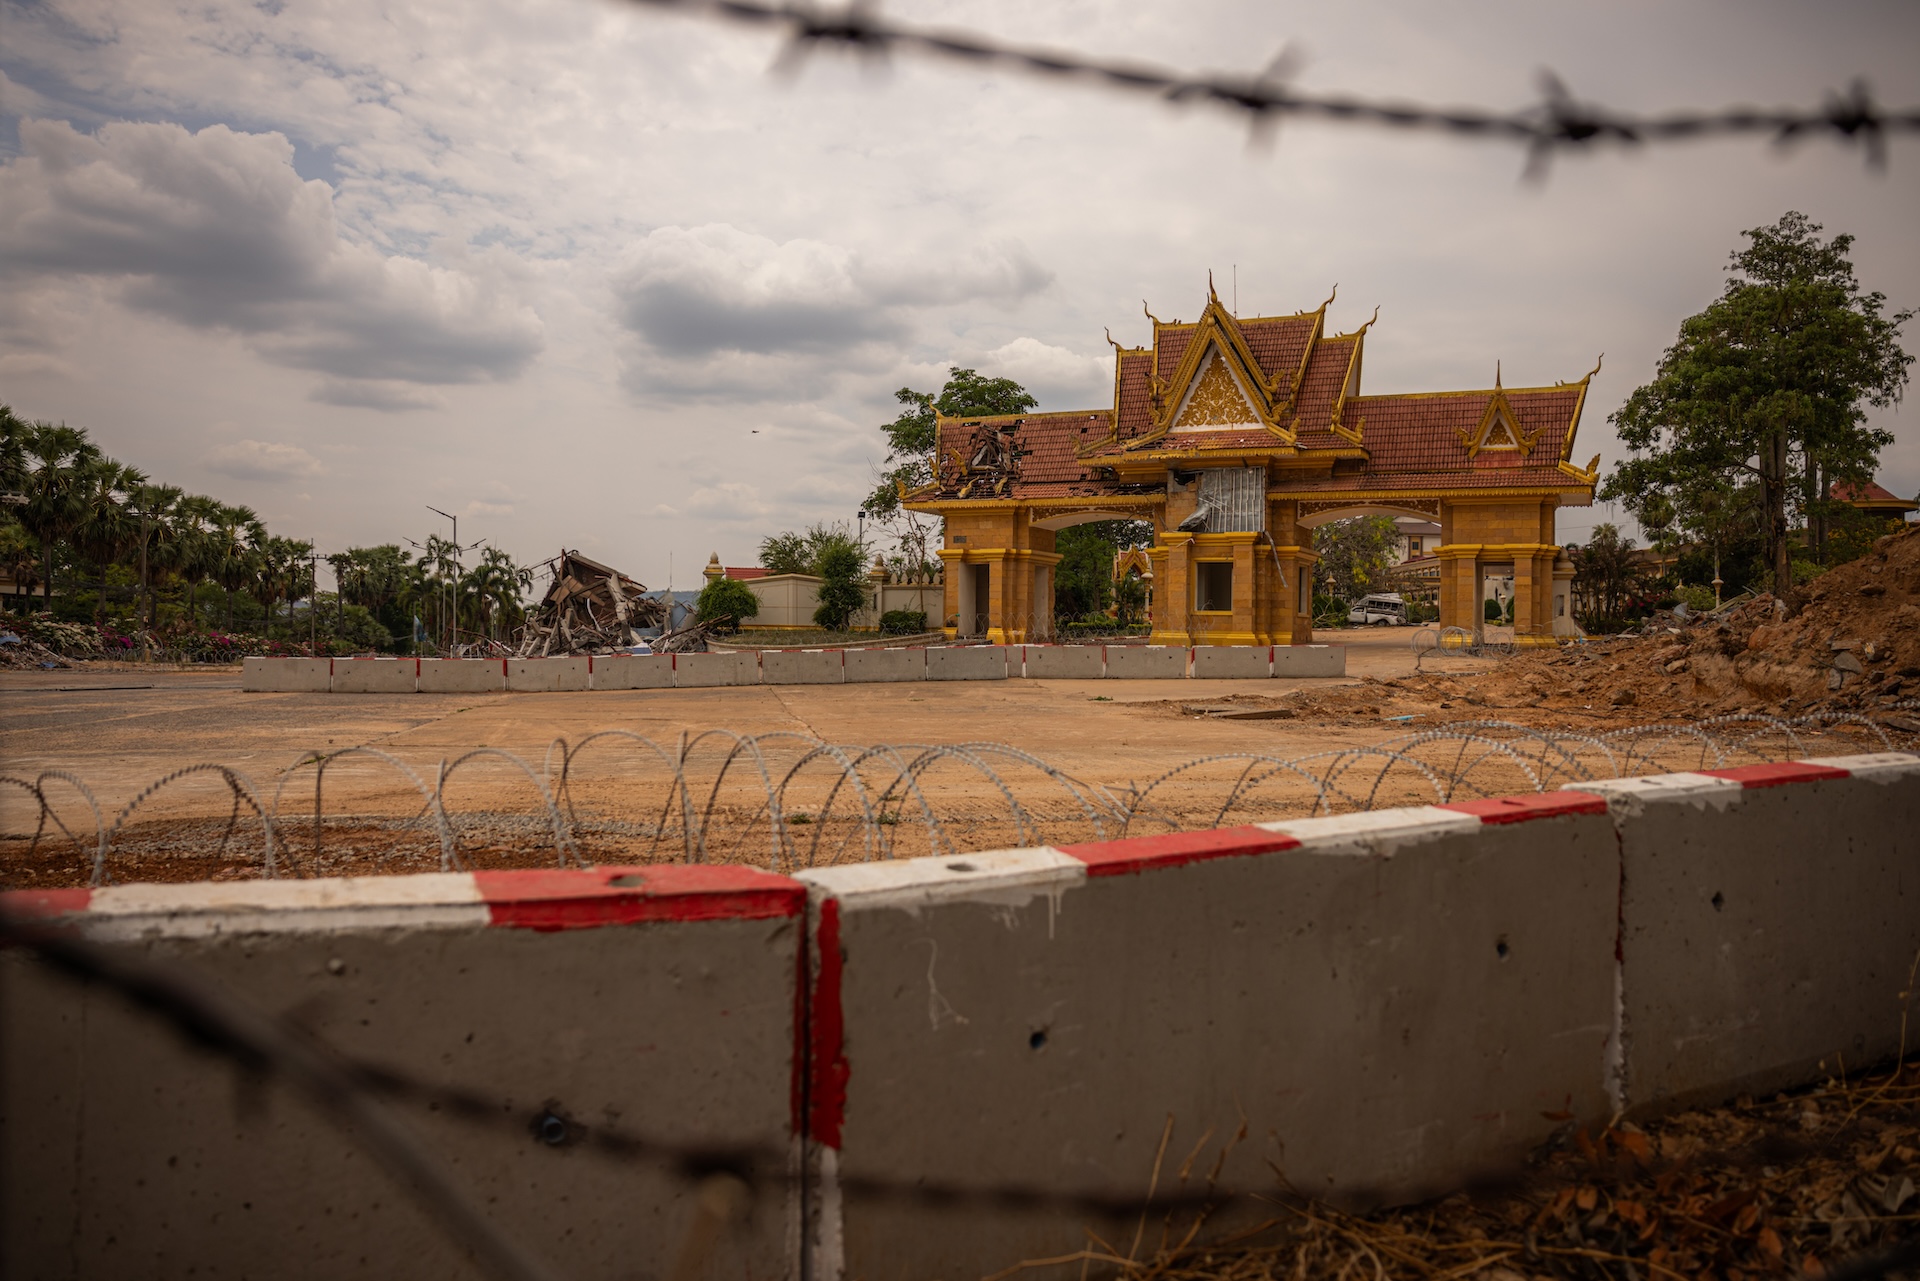
The Justice Department seized cloud infrastructure tied to Huione Group, exposing backend systems used by Huione Guarantee to help move and conceal billions in fraud proceeds. Treasury also expanded sanctions on Huione-linked firms and Prince Group affiliates as U.S. officials target a major transnational scam and laundering network. #HuioneGroup #HuioneGuarantee #HaowangGuarantee #PrinceGroup #ChenZhi
Xsolis says a targeted phishing attack exposed sensitive data belonging to nearly 1.4 million people, including names, addresses, Social Security numbers, and medical information. The company has contained the incident, notified law enforcement and affected individuals, and is offering identity monitoring through Kroll. #Xsolis #Dragonfly #Kroll