Microsoft has released KB5095093 as an optional preview cumulative update for Windows 11 24H2 and 25H2, bringing bug fixes and a new Point-in-Time restore feature. The update also rolls out improvements across Windows Update, File Explorer, Bluetooth, networking, accessibility, and other system components, while one known issue still affects launching Microsoft Office apps from some third-party applications. #KB5095093 #PointInTimeRestore #Windows11
Category: Cyber Security News
Tata Electronics confirmed a cybersecurity incident that affected parts of its IT infrastructure, but said its operations across businesses continued normally and were not impacted. The disclosure follows claims by the World Leaks group, which reportedly leaked data tied to Tata Electronics, including files related to Apple product manufacturing. #TataElectronics #WorldLeaks #Apple
Two members of Scattered Spider, Thalha Jubair and Owen Flowers, pleaded guilty to hacking Transport for London in 2024 and causing major operational disruption and financial losses. The attack exposed customer data, disrupted Oyster refund services, and led investigators to link Flowers to additional breaches at SSM Health Care Corporation and Sutter Health. #ScatteredSpider #TransportforLondon #ThalhaJubair #OwenFlowers
A new macOS ClickFix campaign uses fake CAPTCHA pages and Terminal commands to silently download and launch a malicious DMG that installs Atomic macOS Stealer (AMOS). The malware steals browser credentials, crypto wallet data, Keychain files, messaging app data, and documents, while the campaign uses servers such as svs-verificationdate[.]beer and 196.251.107[.]171. #AtomicmacOSStealer #AMOS #ClickFix #svs-verificationdate[.]beer
Abdellah Belmili, also known as Dila Belmili and Spox, was arrested in Spain and extradited to the United States for allegedly operating the Market0Day and Spoxy cybercrime marketplaces. Authorities say he helped enable phishing and bulk SMS fraud targeting major financial institutions, including JPMorgan Chase, Bank of America, American Express, and…
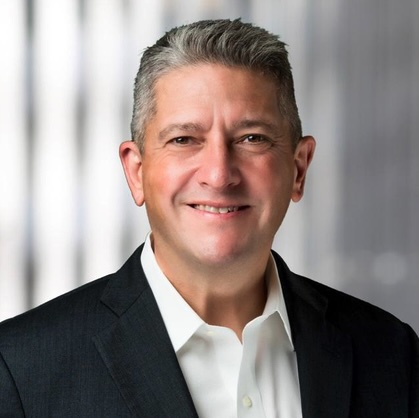
Carl Froggett serves as both CISO and CIO at Deep Instinct, a dual role he believes can work well in smaller organizations because technology strategy and security must operate in lockstep. He also warns that artificial intelligence is creating new security risks such as prompt injection, deepfakes, and AI-assisted attacks, making…
Researchers uncovered CVE-2026-20971, an eight-year-old high-severity flaw in Samsung’s KNOX kernel that affected Galaxy S9 through Galaxy S25 devices and could be exploited through the interaction between PROCA and FIVE. Samsung fixed the issue in its January 2026 update, and the research highlights how a local vulnerability in a mobile security…
Organizations continue to struggle with phishing, business email compromise, and account takeover attacks because security teams are overwhelmed by alerts and manual investigation work. A July 8, 2026 BleepingComputer webinar with Abnormal AI and Novant Health will show how behavioral AI can automate detection, investigation, and remediation to reduce alert fatigue and speed response. #BleepingComputer #AbnormalAI #NovantHealth #BEC #ATO #phishing
LastPass disclosed that hackers accessed customer data in its Salesforce environment after stealing OAuth tokens in a Klue supply chain attack. The company said its products and vaults were not affected, but exposed details could be used in phishing and social engineering campaigns, and the attack has been linked to the Icarus extortion group. #LastPass #Klue #Icarus #Salesforce #Gong
AI has collapsed the disclosure-to-exploit window from months to hours, making traditional vulnerability management and patch-first approaches too slow to keep up. The article argues for TTP-chain validation and control-aware testing to determine what is actually exploitable in an environment, with Picus Security positioning this as a better way to prove risk than live exploitation alone. #PicusSecurity #CVE-2025-29824 #OpenBSD #Storm2460 #RansomEXX #Anthropic #Mythos
Cybercriminals built a global reputation network using GitHub, SourceForge, YouTube, VirusTotal, and fake news sites to promote a Rust-based clipboard hijacker that steals cryptocurrency on Windows and macOS. Check Point says the campaign uses coordinated trust manipulation to lure crypto owners and traders into downloading fake tools that hide the malware and hijack wallet addresses from clipboards. #CheckPoint #GitHub #SourceForge #VirusTotal #YouTube
SOCRadar uncovered the broader FortiBleed campaign, in which attackers use the FortigateSniffer tool to turn compromised FortiGate firewalls into passive credential stealers across dozens of protocols. The operation has stolen more than 110 million credentials, hit organizations in nearly 200 countries, and is likely run by Russian-speaking threat actors motivated by financial gain. #FortiBleed #FortiGate #FortigateSniffer #SOCRadar #CISA #Fortinet

London Hydro is investigating a data breach that may have exposed customer personal and account information, including names, addresses, email addresses, phone numbers, and billing details. The company says no financial or other sensitive data appears to have been compromised, and it has warned customers to watch for phishing attempts and…
SOCRadar says the FortiBleed campaign is a multi-vendor credential-harvesting operation run by a likely Russian-speaking initial access broker that has targeted more than 430,000 FortiGate firewalls and compromised over 110 million credentials. The attackers use tools like FortigateSniffer, Masscan, and Shodan to sniff authentication traffic, crack stolen data, and sell access,…
OpenAI has expanded its Daybreak cybersecurity initiative with new tools, partnerships, and the updated Codex Security plugin to help defenders move faster from vulnerability discovery to remediation. It also launched GPT-5.5-Cyber and the Patch the Planet program to support open source maintainers, while extending the Daybreak Cyber Partner Program for security…