Service desk social engineering is a highly effective attack path because it exploits human trust to reset credentials, bypass MFA, and gain legitimate access to corporate systems. Recent incidents involving Scattered Spider, Silent Ransom Group, Marks & Spencer, Co-op, Harrods, and Carnival Corporation show how attackers impersonate employees or IT support to move quickly from help desk access to data theft or ransomware. #ScatteredSpider #SilentRansomGroup #MarksandSpencer #Coop #Harrods #CarnivalCorporation
Category: Cyber Security News
A malicious Microsoft Edge extension called Edgecution was used in a ransomware-related attack to escape the browser sandbox and deploy a Python-based backdoor. The campaign relied on fake Microsoft support pages, Chrome Native Messaging, and a disguised Edge Monitoring Agent to run commands and maintain persistence. #Edgecution #PayoutsKings #MicrosoftEdge #MicrosoftTeams #OutlookUpdatesManagementConsole
Mandiant revealed that CVE-2026-20245 in Cisco Catalyst SD-WAN was used in zero-day attacks to escalate privileges and create a rogue root account named “troot” on targeted devices. The intrusion involved unauthorized SD-WAN peering, stolen or bypassed access, malicious CSV uploads, and extensive cleanup to hide evidence of compromise. #Cisco #CatalystSDWAN #Mandiant #CVE202620245 #troot

A coordinated international law enforcement operation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behind credential theft, fraud, and ransomware attacks. The takedown recovered millions of stolen credentials, restricted over $47 million in criminal crypto assets, and shut down…

CISA warned that CVE-2025-67038 in Lantronix EDS5000 Series devices is being actively exploited, and FCEB agencies must apply the fix by June 26, 2026. The advisory also highlighted active exploitation of UniFi OS flaws chained as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910, which can lead to root-level code execution and broader network compromise….
AI agents can be manipulated by malicious content hidden in webpages, files, emails, and tools, causing them to trust false instructions, poison memory, or take unintended actions. Google DeepMind and security researchers describe six trap categories and emphasize that strong source verification, restricted permissions, and human approval are essential to keep…
Microsoft, Europol, and international partners disrupted infrastructure used by the Amadey, StealC, and SocGholish (FakeUpdates) malware operations under Operation Endgame. The action took down hundreds of servers and domains, seized stolen credentials and crypto-linked assets, and targeted the tools cybercriminals use to gain access and deploy ransomware. #Amadey #StealC #SocGholish #FakeUpdates #Microsoft #Europol #OperationEndgame
CISA is warning that hackers are actively exploiting critical flaws in Ubiquiti UniFi OS and Lantronix EDS5000 serial-to-ethernet servers, prompting urgent patching under BOD 26-04. The issues include remote code execution, access control bypass, and path traversal bugs that can lead to full system compromise and sensitive data exposure. #Ubiquiti #UniFiOS #Lantronix #EDS5000 #CVE-2026-34908 #CVE-2026-34909 #CVE-2026-34910 #CVE-2025-67038
Traditional SBOM, VEX, and CVSS-based triage is failing to provide enough context for modern AI and software supply chain risks, especially when vulnerabilities can have very different real-world consequences. Devashri Datta proposes SRIL and AIVEX to add safety-aware, machine-readable context so organizations can prioritize remediation based on actual operational impact. #CycloneDX…
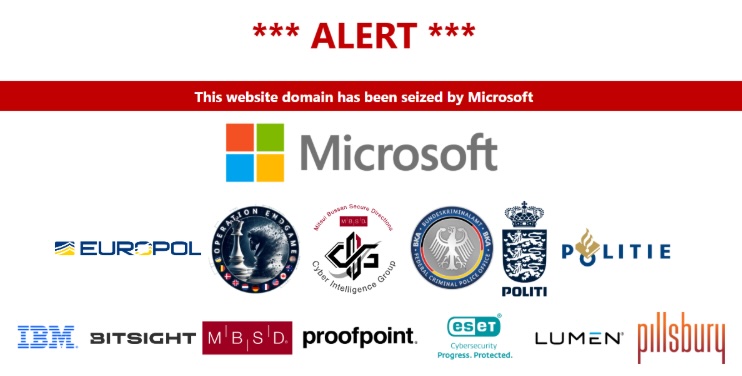
Microsoft, law enforcement, and cybersecurity partners dismantled infrastructure used by Amadey and StealC in a major Operation Endgame action. The takedown disrupted the “cybercrime assembly line,” seized millions of stolen credentials, and exposed a StealC control-panel flaw that was used in the operation. #Amadey #StealC #OperationEndgame #Europol #Microsoft…
Microsoft and law enforcement coordinated a court-authorized takedown that targeted Amadey and StealC at the same time, disrupting the shared infrastructure used by both criminal tools. The operation hit more than 200 command-and-control servers and aimed to make it harder for threat actors to rebuild and scale their attacks. #Amadey #StealC #Microsoft #Europol #RICO
Mistic is a stealthy new backdoor used in financially motivated attacks against organizations in insurance, education, IT, and professional services, with evidence linking it to the KongTuke/Woodgnat initial access broker. Symantec and Zscaler say the malware supports persistent access, in-memory execution, and expanded capabilities through Beacon Object Files, and it has been delivered through multi-stage infection chains including Microsoft Teams social engineering and ClickFix. #Mistic #KongTuke #Woodgnat #ModeloRAT #MTLBackdoor #ClickFix
Agentic AI in security can only make sound decisions when it has accurate, current, and relevant context about assets, controls, exposures, and business impact. Without that context, autonomous actions in SOC workflows can quickly become confident but wrong, which is why many experts argue human oversight is still necessary. #NagomiSecurity #Lanxit…
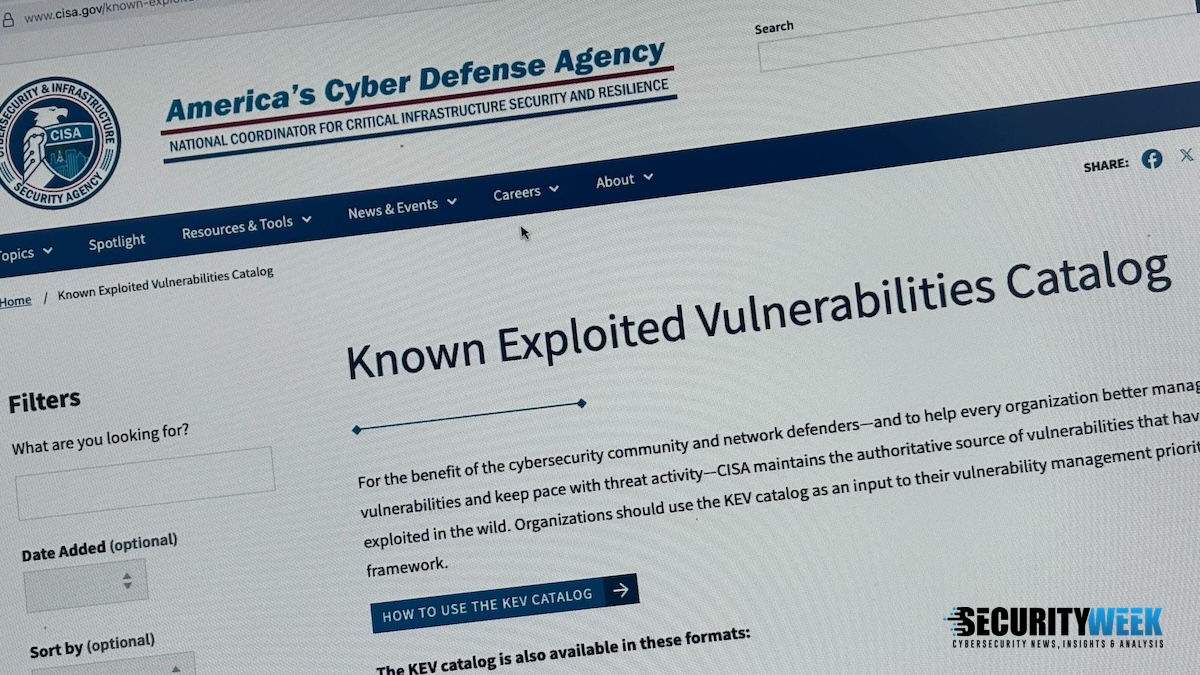
Threat actors are actively exploiting three critical Ubiquiti UniFi OS vulnerabilities, prompting CISA to add CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to its Known Exploited Vulnerabilities catalog. BishopFox confirmed the flaws can be chained to bypass authentication and achieve command injection, potentially enabling rogue admin creation and lateral movement in enterprise networks. #Ubiquiti…
A third suspect tied to the 2022 credential-stuffing attack on DraftKings has been sentenced to 18 months in prison, along with restitution and forfeiture orders. The scheme used stolen credentials from other breaches to access more than 60,000 accounts, steal funds, and resell compromised access online. #DraftKings #NathanAustad #Snoopy #KamerinStokes #JosephGarrison…