
Post-quantum cryptography is now a leadership and readiness issue, with the executive order turning a long-known quantum risk into a concrete mandate for federal agencies, contractors, and critical infrastructure. Organizations must build cryptographic visibility, ownership, funding, and crypto-agility now to meet the 2030 and 2031 deadlines and reduce exposure to “Harvest Now, Decrypt Later” attacks. #PostQuantumCryptography #QuantumComputer #HarvestNowDecryptLater
Category: Cyber Security News

Microsoft shut down StegoAd, a long-running Edge Add-ons campaign that used steganography in image and font files to hide malicious code inside 119 extensions. The operation stole credentials, hijacked sessions, and drove ad fraud while showing ties to DarkSpectre, ShadyPanda, GhostPoster, and mitarchive.info. #StegoAd #DarkSpectre #ShadyPanda #GhostPoster #mitarchive.info…
OpenAI has launched a limited preview of GPT-5.6, introducing the Sol, Terra, and Luna tiers, with Sol positioned as its strongest model for cybersecurity. The rollout is restricted to trusted partners while OpenAI and the U.S. government work on a framework to address national security risks and manage dual-use concerns. #OpenAI…
The US government is offering rewards of up to $10 million for information on individuals tied to UNC5792 and UNC4221, two threat actors linked to Russian intelligence services. These groups have used phishing and account takeover tactics against government officials, military personnel, journalists, and others by abusing secure messaging apps like…

Daily Recap, AI-native security, agentic workflows, and AI-abusing malware were front and center, including Nebulock’s $25 million raise for contextual AI security, the expanding MCP spec bringing new enterprise risks, and a new macOS malware strain that plants fake errors to throw off AI analysis. Other key stories covered Robinhood speeding up access approvals, Poland’s SIM-swapping gang bust tied to millions in crypto theft, and Microsoft extending free Windows 10 ESU support to October 2027.
#Nebulock #MCP #macOS #Robinhood #Philip Martin #Uber #Akrites #Poland #SIMSwapping #Bluekit #Cellebrite #FCC #CISA #Windows10ESU #Chrome #Shop #PirloTV #TataElectronics #Snyk
KDDI Corporation disclosed a breach of one of its email systems used by five Japanese ISPs after attackers exploited a vulnerability in third-party software. The incident may have exposed email addresses and passwords for up to 14.22 million customers, prompting KDDI to notify authorities and urge password resets. #KDDI #STNet #JCOM #ChubuTelecommunications #NIFTY #BIGLOBE
Researchers at Mozilla’s 0DIN showed that a clean-looking GitHub repository can trigger an invisible attack chain when an agentic coding tool like Claude Code tries to fix a normal setup error. The method can end with an attacker-controlled shell on a developer’s device, exposing secrets, files, and persistence opportunities through indirect steps the agent never fully sees. #ClaudeCode #0DIN #GitHub #Anthropic

OpenAI has released GPT-5.6 Sol, Terra, and Luna in a limited preview for trusted partners and U.S. government-approved companies, positioning the models for defensive cybersecurity work while adding strong safeguards against misuse. The release comes alongside government oversight efforts, OpenAI’s Daybreak and Patch the Planet initiatives, and Anthropic’s limited restoration of…
Infoblox says more than 200,000 websites are using investment scam templates built with the Chinese open source framework Uni-App, with over 236,000 second-level domains tied to fake crypto exchanges, gambling impersonators, WhatsApp phishing, and pig-butchering sites. The scam ecosystem has expanded sharply since late 2024 and includes notable operations such as…
Ukraine’s SBU, working with the FBI, exposed a long-running Russian campaign that targeted messaging accounts of officials, military personnel, politicians, activists, and citizens in Ukraine, Europe, and the United States. The attackers relied on social engineering to steal credentials and personal data from accounts on platforms such as Signal, WhatsApp, and…
Russian state-backed hackers linked to Turla have spent years developing StockStay, a malware strain used to spy on Ukrainian government and military targets as well as entities in parts of Europe. Google says the malware has evolved to masquerade as legitimate software and is part of a broader effort to maintain…
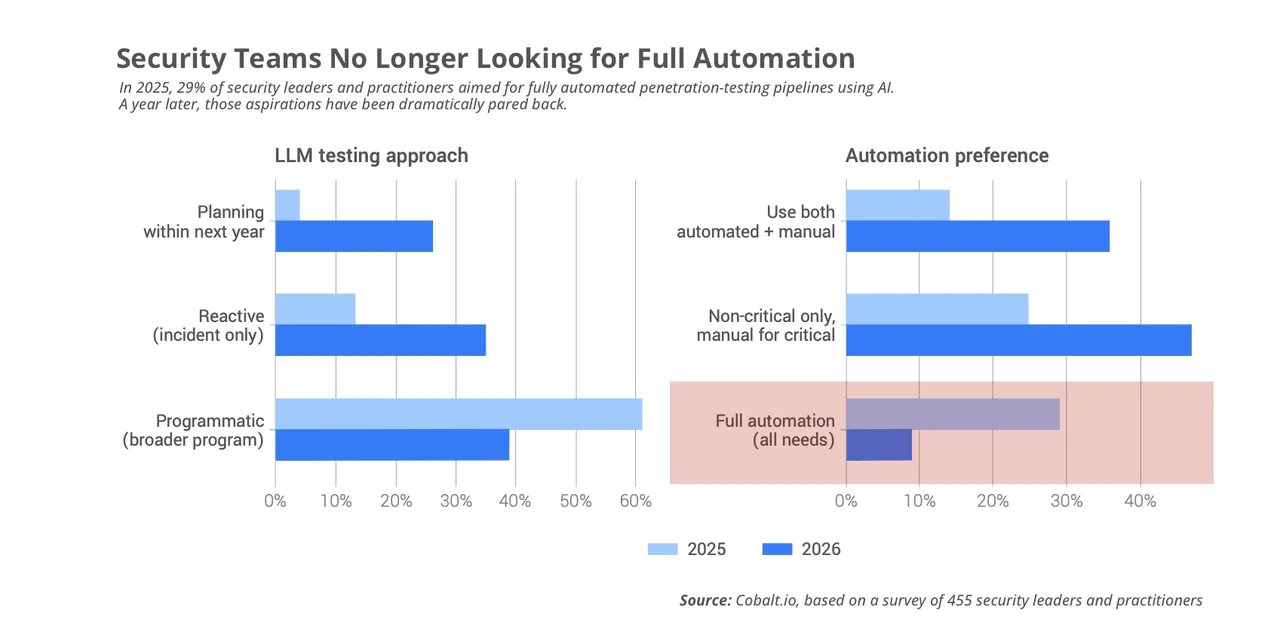
Security teams are becoming far less confident that fully autonomous AI can replace human penetration testers, as blind spots, false positives, missed critical issues, and unpredictable costs continue to undermine trust. The emerging consensus is a hybrid model where AI handles broad, repetitive work while human experts provide validation, judgment, and risk prioritization. #Cobalt #FIRST #HackerOne #BishopFox #Microsoft
Daily Recap, AI-native security, agentic workflows, and AI-abusing malware were prominent as Nebulock raised $25 million, the MCP spec expanded enterprise use while introducing new risks, and a new macOS malware strain hid fake errors to confuse AI analysis tools. Separately, Robinhood improved access-approval speed for high-velocity development while Polish authorities disrupted a SIM-swapping crypto-theft gang and attackers leveraged Bluekit, browser-in-the-middle phishing, and callback scams to target credentials. #Nebulock #MCP #macOSMalware #Robinhood #PhilipMartin #Uber #Akrites #PolandSIMSwapping #Bluekit #SIMSwapping #Cellebrite #FCC #Windows10ESU #ChromeAddOn #ShopOrderTrackingApp #PirloTV #TataElectronics #Snyk

Apple removed several major VK and Mail.ru apps from the App Store, prompting Russian officials to accuse the company of political censorship and question its trustworthiness. The apps were reportedly taken down to comply with sanctions regulations, affecting access to VKontakte, VK Music, VK Messenger, VK Video, Odnoklassniki, and Mail.ru services….

A newly observed campaign tracked as StrikeShark is delivering the previously undocumented SharkLoader malware to deploy Cobalt Strike Beacon on compromised systems. The activity targets organizations across multiple countries and uses public exploit chains, malicious droppers, and DLL side-loading to gain access and maintain control. #StrikeShark #SharkLoader #CobaltStrikeBeacon #ProxyLogon #Openfire #GeoServer…