
The FBI and CISA warn that Russian intelligence-linked operators have shifted their Signal phishing campaign to trick victims into revealing their Signal Backup Recovery Key, enabling access to backup message history and potential account takeover. The updated advisory identifies UNC5792 and UNC4221, highlights high-value targets including U.S. and international officials, and…
Category: Cyber Security News
The FBI and CISA warn that a phishing campaign tied to Russian Intelligence Services is now targeting Signal users to steal Backup Recovery Keys. If successful, the attackers can restore victims’ backups on their own devices and read historical messages, including private and group chats. #Signal #FBI #CISA #UNC5792 #UNC4221 #FSB

The ATF canceled a Penlink contract after scrutiny over its use of ad-tech geolocation data to track Americans, following revelations that the agency had already run hundreds of searches with the Webloc tool. Lawmakers and privacy advocates warned that warrantless use of ad-surveillance data raises serious legal and constitutional concerns, prompting calls for broader federal restrictions. #ATF #Penlink #Webloc #RonWyden #MichaelCloud
CISA has ordered federal agencies to patch two actively exploited critical vulnerabilities by June 28: CVE-2026-20230 in Cisco Unified Communications Manager Server and CVE-2026-12569 in PTC Windchill and FlexPLM. The first flaw is a server-side request forgery issue used to write arbitrary text files, while the second is a remote code execution bug affecting multiple PLM versions. #CVE-2026-20230 #CiscoUnifiedCommunicationsManager #CVE-2026-12569 #PTCWindchill #FlexPLM
Threat actors are abusing OpenAI’s organization invite feature by creating fake tenants that impersonate real companies and sending legitimate-looking invitations to employees. The goal appears to be luring targets into joining fraudulent ChatGPT workspaces where they may unknowingly submit sensitive company information, such as source code, documents, and strategic plans. #OpenAI #PushSecurity #AdamBateman
Polymarket says it will fully reimburse customers who lost about $3 million after a malicious script was injected into its frontend through a third-party vendor compromise. The incident was a supply-chain attack that affected a website dependency, while Polymarket’s backend systems were not breached. #Polymarket #PeckShield #Polygon #Ethereum #ParyonUSD

A Chinese-speaking APT group tracked as CL-STA-1062 has been linked to attacks on government entities and critical infrastructure in Southeast Asia using a new custom backdoor called TinyRCT. The campaign combines open-source tools with tailored malware to steal data, maintain access, and target sectors including energy and government. #CL-STA-1062 #TinyRCT #UAT-7237…
Roughly two dozen Klue customers confirmed Salesforce instances were compromised in a supply chain attack that used stolen legacy credentials and OAuth tokens to exfiltrate data. The incident has been linked to threat actor Icarus, which targeted Klue and several customers while allegedly affecting 195 Klue customers in total. #Klue #Salesforce…
Researchers at Wiz disclosed a high-severity flaw in the Amazon Q Developer extension for Visual Studio Code that could let attackers steal developers’ cloud credentials by tricking them into opening a malicious repository. AWS has patched the issue as CVE-2026-12957, along with a related symbolic link flaw CVE-2026-12958, and released fixes…
Robinhood Markets built Secure Enhanced Remote Approval (SERA) to reduce access-approval friction for developers and incident responders without sacrificing security. The platform uses passkey-based approvals from any device and cut approval time by 20%, helping the company move faster across its 24/7 engineering and incident-response workflows. #RobinhoodMarkets #SERA
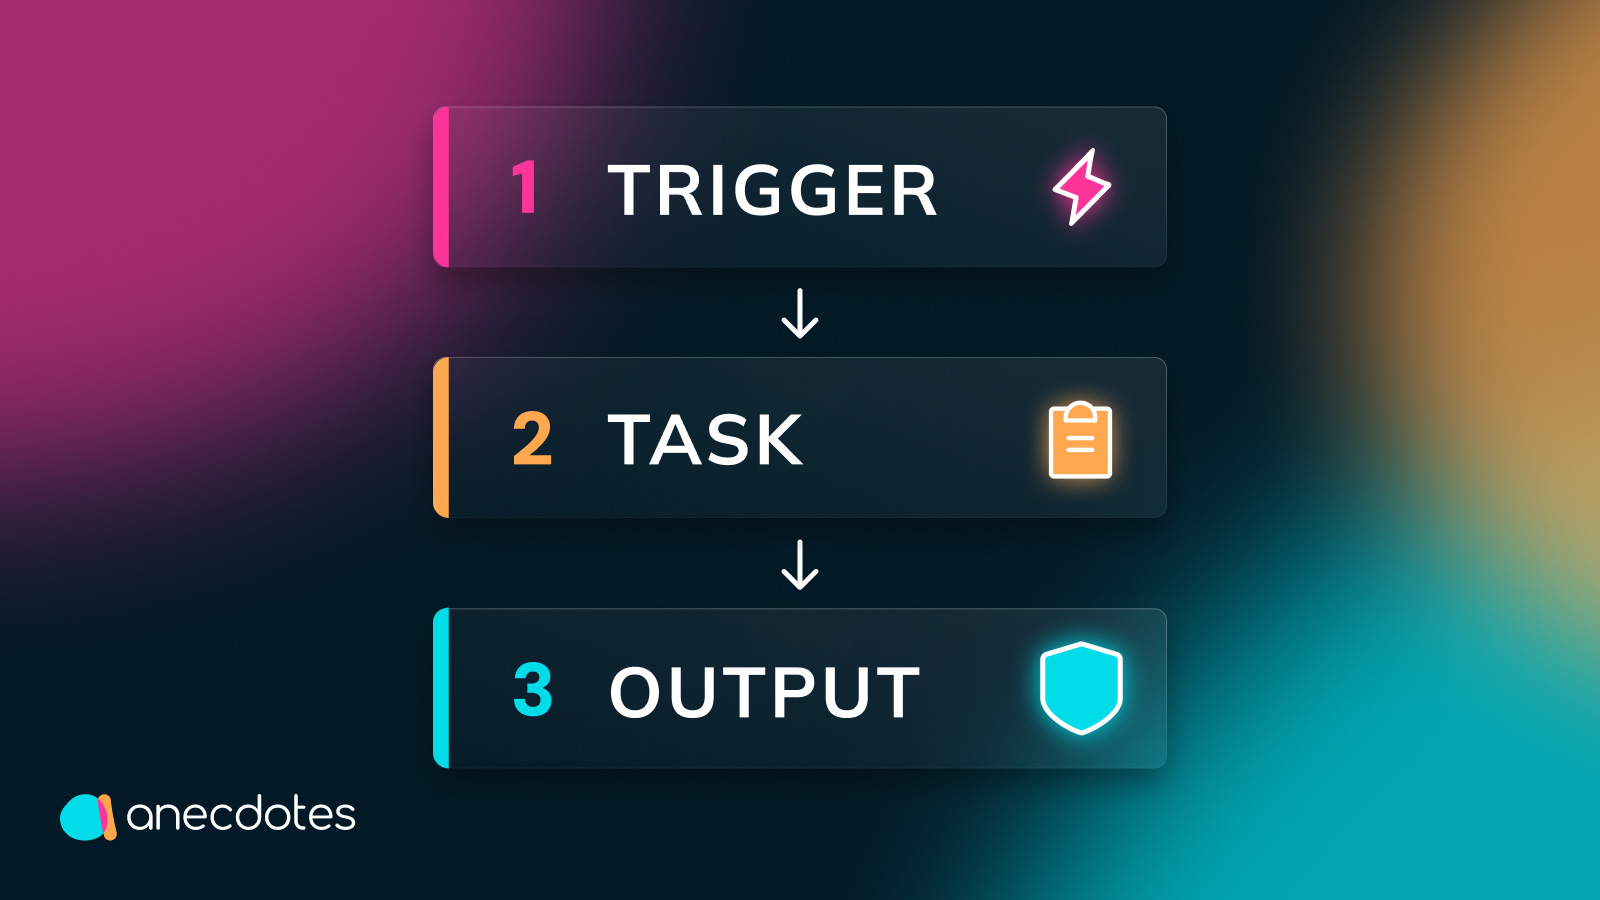
Agentic AI is changing GRC by moving it from static, periodic checks to continuous, context-aware operations that can analyze, decide, and act in sequence. The article explains how a no-code agent can monitor controls like ISO 27001:2022 A.8.5, open findings, attach evidence, and keep every action auditable while leaving final judgment with humans. #ISO27001 #A8_5 #Anecdotes #AgentStudio
The Linux Foundation has launched Akrites, a shared Security Incident Response Team to coordinate the discovery, patching, and public disclosure of open source software vulnerabilities. Backed by major companies including Anthropic, AWS, Google, Microsoft, and GitHub, the initiative aims to speed fix deployment and reduce the risk of exploitation before patches…
Nebulock has raised $25 million in a Series A round led by FirstMark, bringing its total funding to more than $33 million, as it expands its AI-powered threat hunting platform. The startup will use the investment to improve cross-telemetry correlation, deepen behavioral context analytics, and grow its team across engineering and…

This week’s roundup covers a range of major cybersecurity developments, including Russian use of Cellebrite against Andrey Pivovarov, guilty pleas tied to Scattered Spider’s Transport for London breach, and a massive Tata Electronics leak affecting Apple and Tesla. It also highlights new AI-related security warnings and policy actions, alongside the emergence…
Philip Martin has joined Uber as Chief Information Security Officer after serving as Chief Security Officer at Coinbase since 2016. His background includes leadership roles at Palantir and Amazon’s A9, as well as a decade of service as a U.S. Army counterintelligence agent and Arabic linguist. #Uber #PhilipMartin #Coinbase #PalantirTechnologies #AmazonA9…