
Medtronic is notifying 3.8 million people after ShinyHunters breached its corporate IT systems in April 2026 and stole personal and medical information, including Social Security numbers and health-related details. The company says there is no evidence the data was publicly exposed and is offering affected individuals free credit monitoring, dark web…
Category: Cyber Security News
A threat actor known as JadePuffer exploited CVE-2025-3248 in Langflow to gain code execution and use an LLM to automate reconnaissance, credential theft, and persistence. The attack later pivoted to a production server, abused Nacos weaknesses, and ended with encrypted configuration data and an extortion note. #Langflow #CVE-2025-3248 #JadePuffer #Nacos #Sysdig…
Cato Networks reported two critical flaws in Cursor, tracked as CVE-2026-50548 and CVE-2026-50549, that could let attackers achieve remote code execution on the host operating system outside the IDE sandbox. The issues, dubbed DuneSlide, were patched in Cursor 3.0 after being disclosed in February. #Cursor #CatoNetworks #CVE-2026-50548 #CVE-2026-50549 #DuneSlide…
Google, the FBI, and other organizations worked together to disrupt NetNut, a large residential proxy network tied to more than 2 million infected Android devices. The operation targeted the botnet’s backend infrastructure, infected apps, and reseller ecosystem, causing major degradation to its operations. #NetNut #Popa #Badbox20 #AlarumTechnologies…
Peter Stokes, a dual US-Estonian citizen known as “Bouquet,” was extradited to the US after being accused of helping Scattered Spider carry out cyberattacks, including a May 2025 intrusion against a luxury jewelry retailer. The case is tied to a group also known as 0ktapus and UNC3944, which has allegedly hit…

Daily Recap, cybersecurity coverage highlighted rapid exploitation of widely used software flaws, including Cisco Unified CM attacks, a CitrixBleed issue exploited immediately after disclosure, a SharePoint RCE added to CISA KEV, active targeting of Oracle E-Business instances, and an unpatched Argo CD repo-server flaw that could enable takeover of Kubernetes clusters. The same roundup also covered the FortiBleed credential-theft campaign tied to INC and Lynx ransomware, ChocoPoC RAT attempts to compromise vulnerability researchers, 81 million login attempts against Microsoft 365, and ShinyHunters’ data breach impacting Medtronic customers. #UnifiedCM #CitrixBleed #SharePointRCE #CISAKEV #OracleEBS #ArgoCD #Kubernetes #FortiBleed #INC #Lynx #ChocoPoC #ChocoPoCRAT #ClickFix #Microsoft365 #ShinyHunters #Medtronic #BioShocking #Claude #Teams #Copilot #ScatteredSpider #Kubota #HSIN #DHS
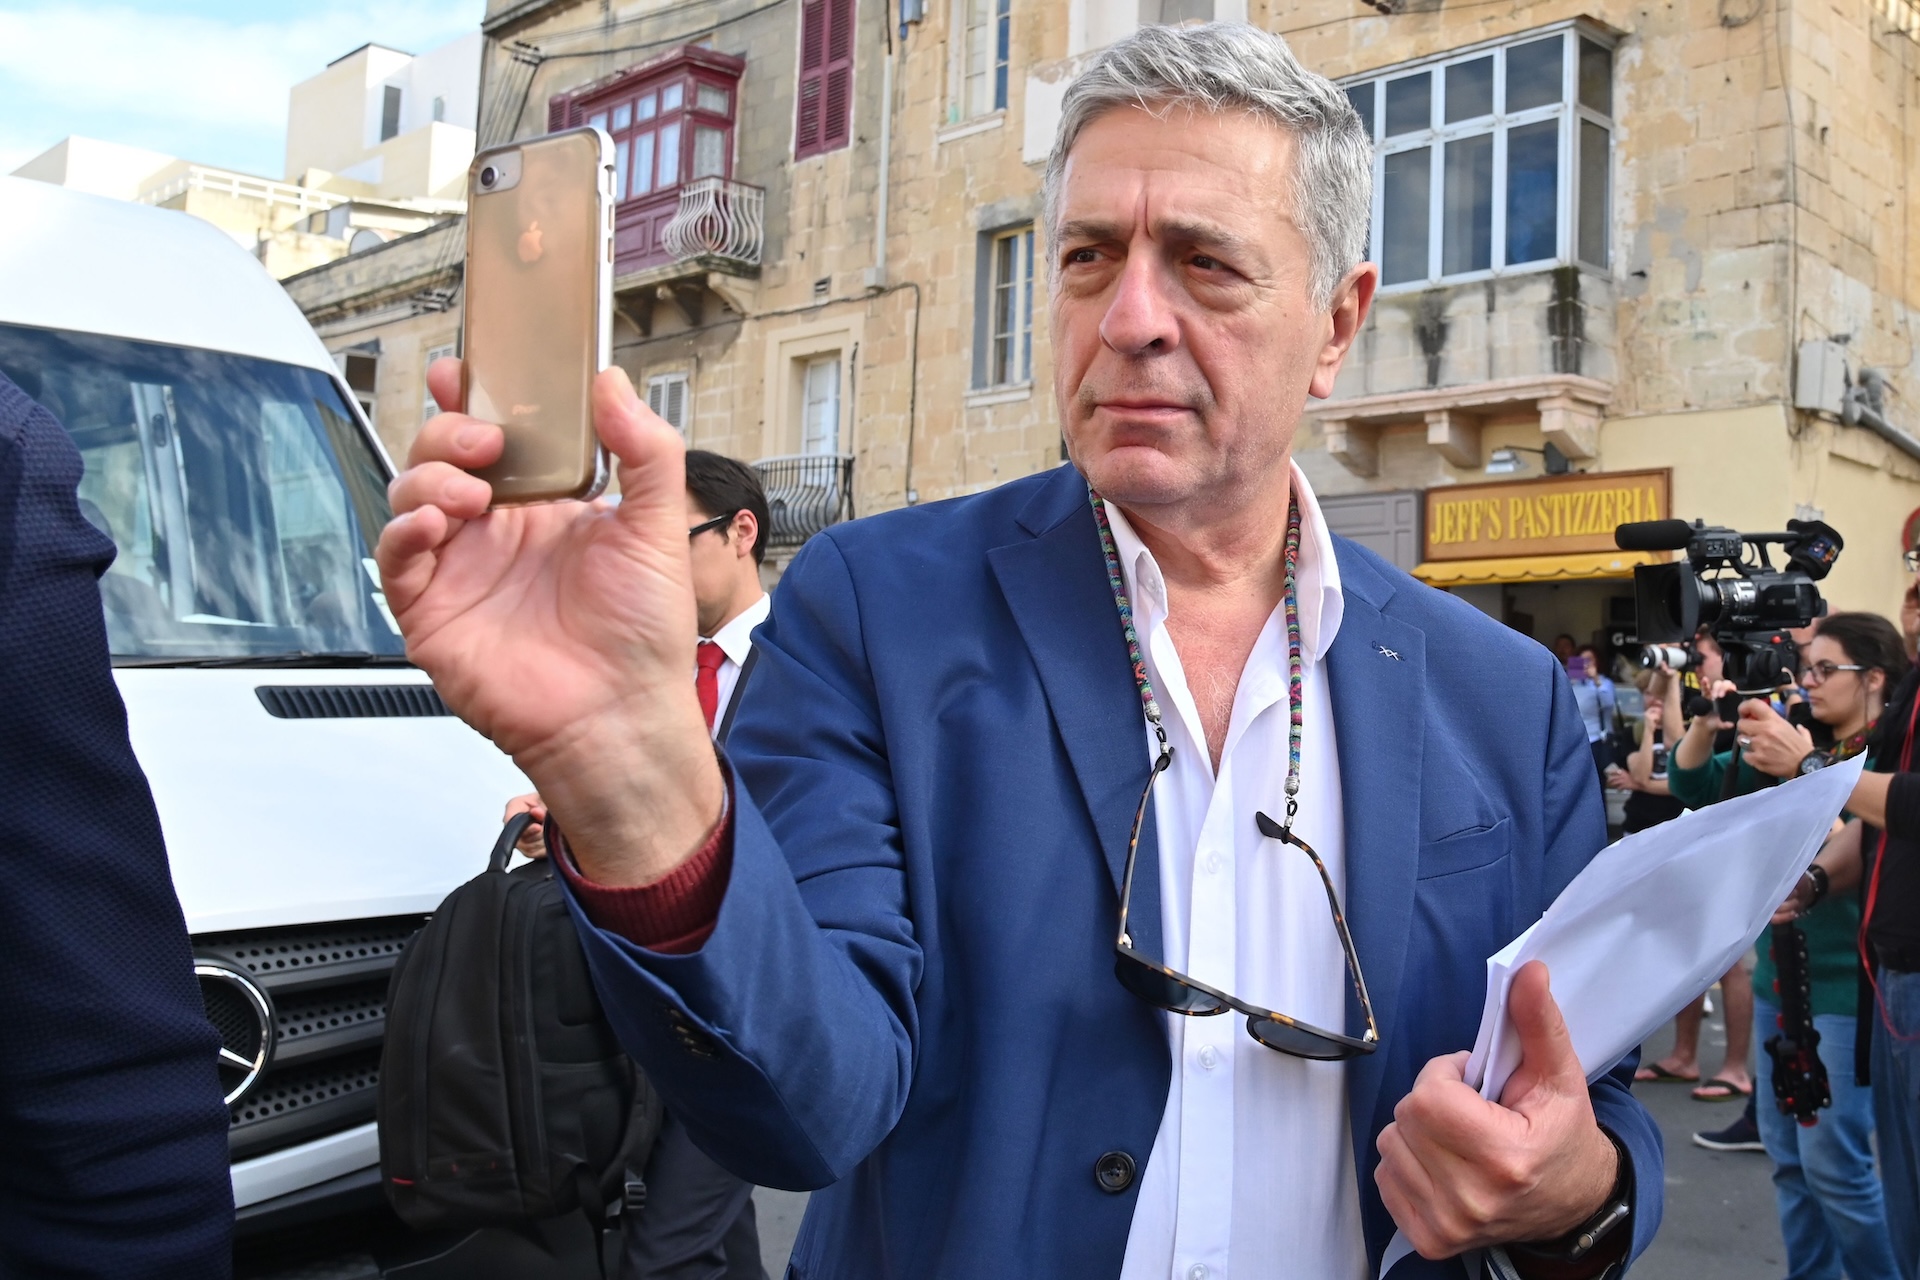
Citizen Lab found Pegasus spyware on the phone of Greek journalist and former European Parliament member Stelios Kouloglou, making him the first publicly identified PEGA Committee member to be targeted. The case underscores ongoing spyware abuse across the EU and renewed calls to implement the PEGA Committee’s recommendations and hold NSO Group accountable. #Pegasus #CitizenLab #SteliosKouloglou #NSOGroup #PEGACommittee
Microsoft fixed the GIF feature in the Windows 11 Emoji Panel by switching from Tenor to GIPHY after Tenor retired its API. The repair is available for Windows 11 24H2/25H2/26H1 through KB5095093, while Windows 11 23H2 and Windows Server 2025 still await a fix. #Microsoft #Tenor #GIPHY #Windows11 #WindowsServer2025 #KB5095093
CISA has warned that attackers are actively exploiting CVE-2026-45659, a high-severity Microsoft SharePoint remote code execution flaw that can let authenticated users run arbitrary code on unpatched servers. Microsoft has issued updates for affected SharePoint versions, while CISA has added the issue to its Known Exploited Vulnerabilities Catalog and ordered federal agencies to patch exposed systems quickly. #CVE-2026-45659 #MicrosoftSharePoint #CISA #BOD-26-04
Modern attacks like ClickFix and ConsentFix succeed by hiding malicious actions inside familiar user workflows, such as fake verification prompts or Microsoft 365 sign-in steps. ConsentFix in particular can steal OAuth session tokens through trusted delivery platforms and lead to account takeover without needing credentials or MFA bypass. #ClickFix #ConsentFix #Microsoft365 #OAuth
The Court of Justice of the European Union has rejected Google’s final appeal, keeping in place a €4.1 billion fine over Android practices that favored Google Search and Chrome. The ruling confirms that Google’s Android agreements restricted competition, while Google says the decision overlooks Android’s open and competitive ecosystem. #CJEU #Google #Android #Chrome #GoogleSearch
A Supreme Court ruling on FTC commissioner removals has put the EU-U.S. Data Privacy Framework in jeopardy because the framework depends on an independent U.S. oversight body. Max Schrems and noyb plan to challenge the deal, while the European Commission and EDPB assess the legal impact on transatlantic data transfers. #EUUSDataPrivacyFramework…

Britain’s National Cyber Action Plan has been delayed again amid political uncertainty following Keir Starmer’s resignation, even as the government says it remains committed to publishing the document. The plan is expected to center on Threat, Growth, and Resilience, while the Cyber Resilience Pledge will still launch with FTSE 350 companies…

This week’s security news highlights how attackers exploit small weaknesses in trusted systems, from phishing emails and clipboard tricks to sandbox escapes and AI prompt injection. The stories also show growing abuse of AI tools, messaging apps, browser extensions, and misconfigured services to steal data, gain access, and deliver malware. #ClaudeCowork…

Threat actors linked to the Anubis ransomware operation are exploiting CVE-2025-5777 (Citrix Bleed 2) and stolen VPN credentials to gain access, then using legitimate RMM tools and living-off-the-land tactics to move laterally, steal data, and deploy ransomware. The report also details The Gentlemen’s use of a Go backdoor and BYOVD techniques,…