Daily Recap, ransomware and extortion developments highlighted JadePuffer using an AI agent to automate attacks, alongside reports that a U.S. government entity paid $1 million to the Kairos group in a data-theft extortion case. The news also covered supply-chain and targeted intrusion campaigns, including PolinRider’s 108 malicious packages and browser extensions, North Korea–linked npm lures delivering BeaverTail, OtterCookie, and ContagiousInterview, and Pegasus spyware found on a European Parliament member’s phone.
Category: Cyber Security News

A U.S. government entity appears to have paid about $1 million to stop Kairos from leaking stolen files, based on a leaked negotiation and blockchain tracing. The case suggests Kairos may not be a traditional ransomware gang at all, but a pure data-theft extortion crew targeting sensitive county records. #Kairos #UnionCountyOhio…
Researchers say JadePuffer is the first documented ransomware operation carried out entirely by a large language model agent, which used autonomous reasoning to handle reconnaissance, credential theft, lateral movement, persistence, privilege escalation, and encryption. The attack began with CVE-2025-3248 in Langflow, later moved into Alibaba Nacos, and ended with encryption of 1,342 configuration items before the ransom note was planted. #JadePuffer #Langflow #CVE-2025-3248 #AlibabaNacos #CVE-2021-29441

North Korean threat actors tied to the Contagious Interview campaign have published 108 malicious packages and browser extensions across npm, Packagist, Go, and Google Chrome as part of the ongoing PolinRider activity. The campaign uses compromised maintainer accounts, malicious VS Code tasks, and hidden JavaScript loaders to spread BeaverTail variants and…

Daily Recap, Agentic AI was reported to drive a ransomware attack via Langflow, while Cursor AI IDE flaws could allow OS-level remote code execution affecting developers. Ransomware groups are also leveraging Citrix Bleed 2, BYOVD, and stolen supply-chain credentials, as CISA warns that a Microsoft SharePoint RCE bug is actively exploited in the wild.
#Langflow #AgenticAI #Cursor #CitrixBleed2 #BYOVD #SharePoint #RCE #Pegasus #ScatteredSpider #Medtronic #NetNut #ConsentFix #ClickFix #M365 #UKNationalCyberActionPlan
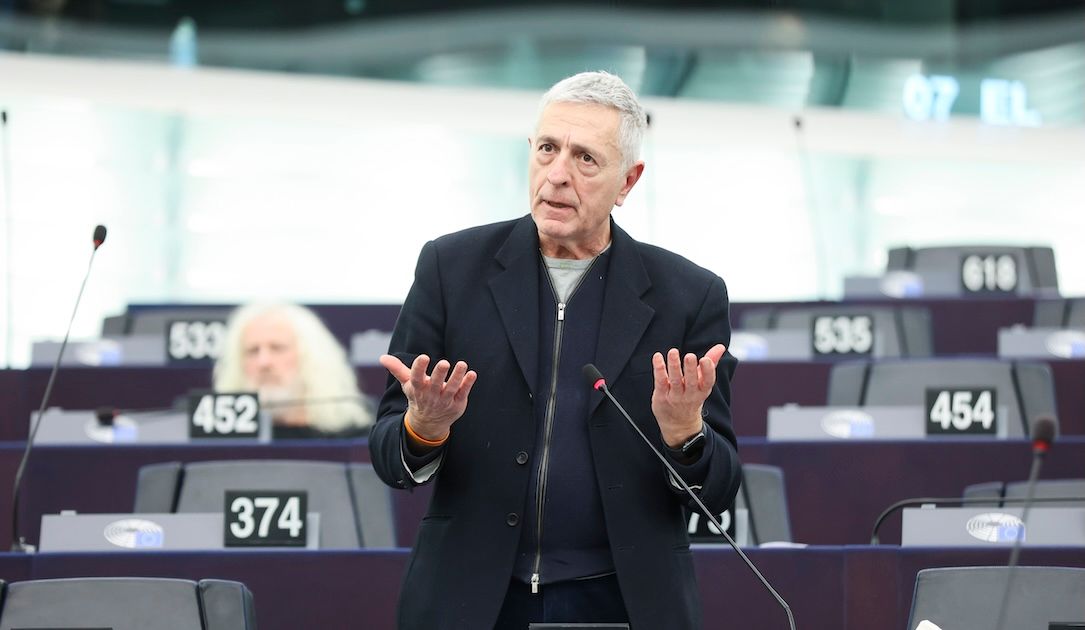
A former European Parliament member, Stelios Kouloglou, was reportedly infected multiple times with Pegasus spyware while serving on the PEGA Committee that was investigating abuse of commercial spyware in Europe. Citizen Lab linked the attacks to the same Pegasus customer behind earlier infections targeting journalists and opposition figures in Belarus and…

Researchers uncovered Avalon, a modular malware framework spread through a multi-stage phishing chain that uses stealthy delivery and extensive defense evasion to gain access, steal data, and deploy ransomware. The report also describes JADEPUFFER, an agentic ransomware attack driven by an LLM, and an AI malware that uses a Telegram bot…

Bad Epoll (CVE-2026-46242) is a Linux kernel use-after-free flaw that can let a local user gain root on affected Linux desktops, servers, and Android devices, with a fix already available. The bug is especially notable because it was found after Anthropic’s Mythos AI missed it in the same epoll code area…

runZero disclosed seven vulnerabilities in FatFs that can lead to memory corruption, device crashes, data leaks, and possible code execution on embedded systems that read FAT and exFAT media. The issues affect widely used platforms such as Espressif ESP-IDF, STM32Cube, Zephyr, MicroPython, ArduPilot, RT-Thread, Mbed, Samsung TizenRT, and SWUpdate, while proof-of-concept…
Google, the FBI, and industry partners disrupted NetNut, a massive residential proxy network that used millions of compromised Android devices, smart TVs, and streaming boxes to hide malicious traffic behind residential IP addresses. The takedown also blocked NetNut’s command-and-control infrastructure and used Google Play Protect to warn users and disable infected apps. #NetNut #Popa #Badbox2.0 #Google #FBI

Armored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns. Its toolkit includes obfuscated RATs, BusySnake Stealer, AquilaRAT, and Go2Tunnel, with attacks delivered through spear-phishing, GitHub-hosted payloads, and abused Windows shortcut chains. #ArmoredLikho #BusySnakeStealer…

North Korean-linked threat actors have been using fake Rollup polyfill npm packages to deliver layered malware that enables remote access, credential theft, and data collection from developer environments. The campaign overlaps with earlier Lazarus-linked npm activity and targets sensitive assets such as source code, cloud keys, SSH keys, browser data, and…
This week’s roundup covers major cybersecurity developments, including arrests tied to the Texas GOP cyberattack, a large KDDI data breach, poisoned tenant abuse against Push Security, and new malware and spyware activity. It also highlights Russian-linked disruption against Jaguar Land Rover, Pegasus targeting a European Parliament member, zero-day research across open…
Cisco Talos uncovered ARToken, a phishing-as-a-service platform that appears to be affiliated with EvilTokens and is built to steal Microsoft 365 tokens and maintain persistent access. The kit supports device code phishing, Primary Refresh Token abuse, and full business email compromise operations against Outlook, SharePoint, and OneDrive accounts. #ARToken #EvilTokens #Microsoft365 #PrimaryRefreshToken #CloudflareWorkers

Citizen Lab found that former MEP Stelios Kouloglou was repeatedly infected with Pegasus spyware while serving on the PEGA Committee investigating commercial surveillance abuses in the European Union. The report also links his device to broader campaigns involving Russian and Belarusian-speaking exiled journalists and activists, while separately highlighting abuse of Cellebrite…