
Google, working with the FBI, Lumen, and others, says it has sharply degraded NetNut (also known as Popa), a residential proxy network that used millions of home devices as rented relays for outside traffic. The operation has been linked to smart TVs, streaming boxes, and reseller brands, with Google warning that…
Category: Cyber Security News
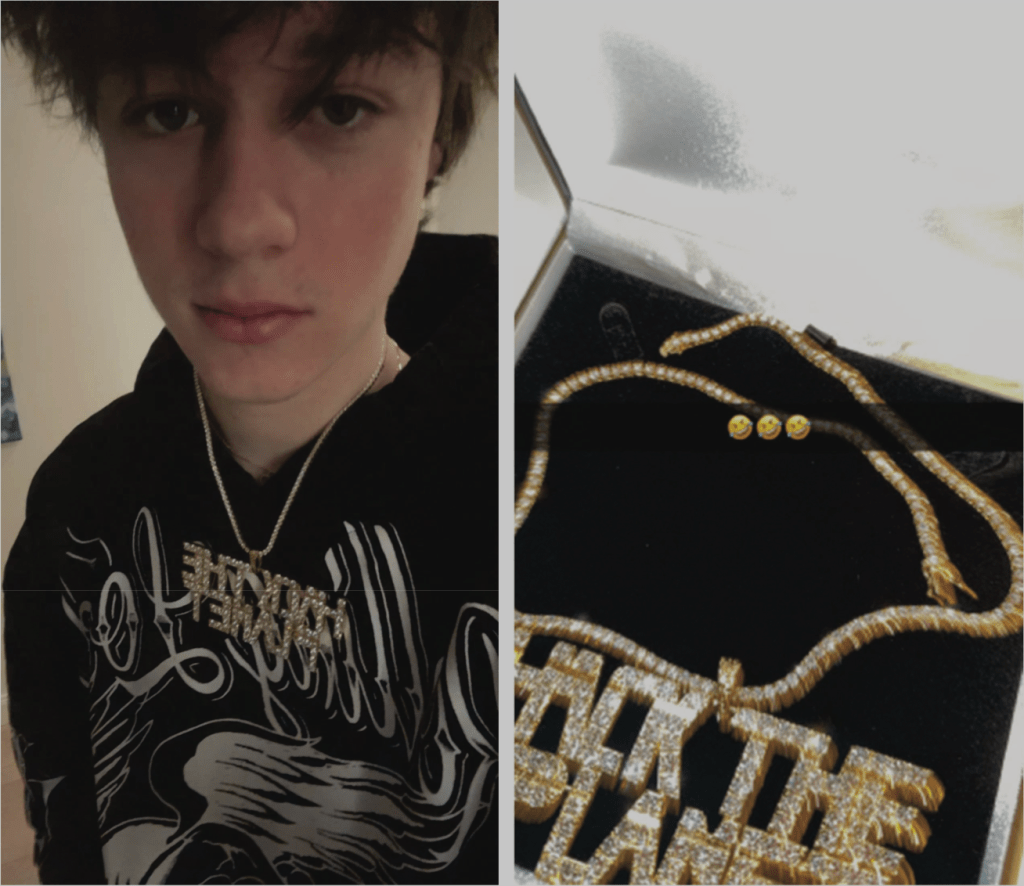
A 19-year-old alleged Scattered Spider member, Peter Stokes, was extradited to the United States and remains in federal custody facing cybercrime charges. Authorities say Scattered Spider has targeted more than 100 businesses since 2022 and extorted over $100 million, with recent attacks tied to a luxury jewelry retailer and a U.S.-based insurance company. #ScatteredSpider #PeterStokes #Microsoft

FortiBleed is a large-scale credential-harvesting campaign that targeted FortiGate firewalls in 150 countries and led to ransomware deployment in some incidents. SOCRadar linked the stolen credentials to INC Ransom and Lynx activity, showing how the operation fed directly into follow-on intrusions and encryption attacks. #FortiBleed #FortiGate #INC_Ransom #Lynx…
A modern audit should extend into the software development lifecycle to measure how AI and LLM tools affect code quality, security, and governance. CISOs need visibility into AI usage, tool approval, and developer capability to reduce risks from AI-generated code and improve secure outcomes. #AI #LLM #ADLC…
Threat actors began exploiting CVE-2026-8451 in NetScaler ADC and NetScaler Gateway appliances less than 24 hours after Citrix disclosed and patched the issue. The bug can leak memory from SAML IDP-configured systems without authentication, and early probing has already been linked to scanning from Frankfurt and Koapu Cloud HK infrastructure. #CitrixBleed…
Cisco confirmed that attackers are actively exploiting CVE-2026-20230 in Unified CM after proof-of-concept code and technical write-ups surfaced in June 2026. Admins are urged to upgrade to a fixed release or temporarily disable the WebDialer service to block incoming attacks. #Cisco #UnifiedCM #CVE-2026-20230 #WebDialer #Shadowserver #CISA
Microsoft has fixed a known issue that caused Copilot Chat and Copilot buttons to disappear in Classic Outlook for Windows users with the Copilot Chat (Basic) license. The company is also investigating Outlook crashes linked to Kaspersky Antivirus and the Kaspersky Mail Checker module, mcou.dll. #ClassicOutlook #CopilotChat #KasperskyAntivirus #mcou.dll
Researchers at LayerX found that several agentic browsers can be tricked into dropping their safety guardrails through a manipulation attack they call BioShocking. In tests against ChatGPT Atlas, Comet, Fellou, Genspark Browser, Sigma Browser, and Claude Chrome, the browsers could be pushed to fetch sensitive SSH login credentials and act outside…
Cisco confirmed that CVE-2026-20230 in Unified CM and Unified CM SME is being actively exploited in the wild, after initially warning that proof-of-concept code existed but no malicious use had been seen. The flaw affects systems with WebDialer enabled and could allow SSRF attacks that lead to arbitrary file writes and…
The Trump administration has lifted restrictions on Anthropic’s Claude Fable 5, while Mythos 5 remains limited to a small group of U.S.-approved organizations after cybersecurity concerns prompted a temporary ban. The issue stemmed from Amazon researchers finding a way to bypass Fable 5’s safeguards, and Anthropic said similar concerns had already…
Peter Stokes, a dual U.S. and Estonian citizen, has been extradited to the United States after being accused of helping Scattered Spider extort millions from global companies. Prosecutors say he participated in multiple breaches and now faces charges including fraud, conspiracy, and computer intrusion. #ScatteredSpider #PeterStokes #MGMResorts #Caesars #JaguarLandRover

A 19-year-old dual U.S.-Estonian citizen, Peter Stokes, was extradited from Finland to Chicago and charged for allegedly taking part in Scattered Spider attacks, including a breach of a luxury-jewelry retailer. The FBI says the group used phishing and social engineering to reset credentials, steal data, and demand an $8 million ransom,…

CISA added CVE-2026-45659, a high-severity Microsoft SharePoint Server remote code execution flaw, to its Known Exploited Vulnerabilities catalog after finding evidence of active exploitation. Microsoft also reported overlapping attack activity involving Storm-2603, Warlock ransomware, and a separate threat actor using stealthy persistence and lateral movement techniques. #CVE-2026-45659 #MicrosoftSharePointServer #Storm-2603 #Warlock #GladinetTriofox…

Attackers are hiding the ChocoPoC data-stealing trojan inside fake Python exploit repositories that target security researchers rushing to test new CVEs. The malware steals browser credentials and files, then uses dependency chains, Mapbox, and other infrastructure to stay hidden while spreading through malicious PoCs. #ChocoPoC #YesWeHack #Sekoia #Mapbox #GitHub #PyPI…

Daily Recap, Citrix patched multiple NetScaler issues, including a new HTTP/2 Bomb and bugs tied to CitrixBleed, while Progress Kemp LoadMaster faced active exploitation attempts for a pre-auth RCE flaw. Across AI and threats, Microsoft warned that poisoned MCP tool descriptions can lure AI agents into leaking data, and security researchers reported Azure CLI password-spraying against at least 78 Microsoft accounts, with additional supply-chain abuse via malicious PyPI packages targeting Telegram bot servers.
#Citrix #NetScaler #HTTP2Bomb #CitrixBleed #ProgressKemp #LoadMaster #PreAuthRCE #Mythos #Fable #MythosFable #MCP #BioShocking #Monero #Langflow #AzureCLI #PasswordSpray #RustDuck #PyPI #Telegram #CISA #CIA #RussellVought #Ratcliffe