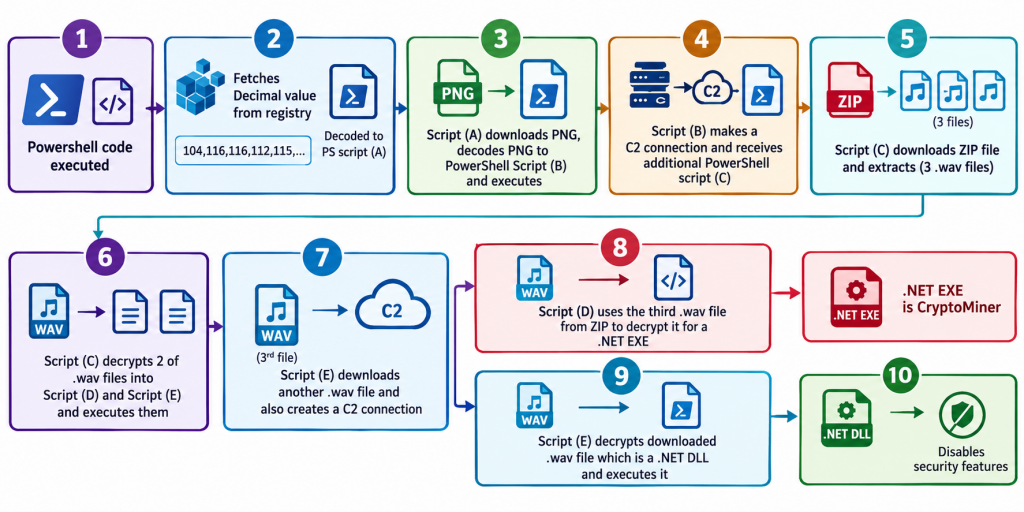
Researchers analyzed a multi-stage infection that used Registry-stored PowerShell, DNS TXT records, PNG and WAV file payload containers, and in-memory .NET loading to hide its activity. The chain ultimately deployed an XMRig-based cryptocurrency miner while maintaining a separate C2 channel and weakening Microsoft Defender and PowerShell logging controls. #XMRig #WinRing0.sys #RealtekHDAudio.wav #sslvalidcert.com #httptls.org
Keypoints
- Initial PowerShell execution was launched with execution-policy bypass and loaded payload data from a Registry value under HKLM:Softwareuf42a9660377vstdfehzr.
- The malware used DNS TXT records from sslvalidcert.com and later txtcdn.net to retrieve encoded data that led to a PNG payload container.
- A PNG image from frames-1zm.pages.dev/frames.png concealed script data in pixel channels and was reconstructed and executed in memory.
- Later stages used ZIP archives and WAV files such as Atsg.wav, Tmav.wav, and Realtek HD Audio.wav to hide additional PowerShell scripts and .NET assemblies.
- The malware established persistence through Scheduled Tasks and a WMI permanent event subscription, while disabling or weakening PowerShell and Microsoft Defender controls.
- The final payload was an XMRig-family cryptocurrency miner that used a config.txt resource, a mining pool, TLS, and a dropped WinRing0.sys driver for optimization.
- A separate C2 channel remained active independently of mining activity, allowing continued remote control and potential delivery of additional payloads.
MITRE Techniques
- [T1059.001 ] PowerShell – Used to run multi-stage scripts and execute reconstructed payloads (‘PowerShell.exe -NoProfile -executionPolicy Bypass…’; ‘the payload extracted the PowerShell code and executed it asynchronously’).
- [T1112 ] Modify Registry – Used the Registry to store and retrieve encrypted payload stages and host identifiers (‘the Registry was being used to store the next stage of the payload’; ‘stored in the Registry’).
- [T1027 ] Obfuscated Files or Information – Heavily concealed payloads with encoded data, decimal-to-ASCII conversion, nibble reconstruction, and hidden content in images/audio (‘encoded PowerShell payload’; ‘reconstructed the embedded data by combining the lower four bits’).
- [T1071.004 ] DNS – Used DNS TXT queries to retrieve data and discover C2 information (‘queries DNS TXT records’; ‘Resolve-DnsName performs the TXT record query’).
- [T1105 ] Ingress Tool Transfer – Downloaded payload containers and configuration files from remote URLs (‘downloaded a PNG image’; ‘downloaded a copy from https[:]//publicwavlib[.]pages.dev/mav.wav’).
- [T1564.001 ] Hidden Files and Directories – Created hidden Scheduled Tasks to maintain persistence (‘Hidden Scheduled Tasks were created to execute the encrypted payload’).
- [T1546.003 ] Windows Management Instrumentation Event Subscription – Set up a WMI permanent event subscription for persistence (‘a WMI permanent event subscription was configured’).
- [T1562.001 ] Disable or Modify Tools – Tampered with security and telemetry settings, including Microsoft Defender exclusions and PowerShell history removal (‘disabled or weakened selected security-related features’; ‘add broad Microsoft Defender exclusions’).
- [T1053.005 ] Scheduled Task/Job – Used Scheduled Tasks to run the payload at logon and at regular intervals (‘Hidden Scheduled Tasks were created to execute the encrypted payload at logon and at regular intervals’).
- [T1106 ] Native API – Loaded .NET assemblies directly into memory with Assembly.Load rather than writing them to disk (‘[Reflection.Assembly]::Load()’; ‘loaded it directly into the PowerShell process’).
- [T1041 ] Exfiltration Over C2 Channel – Sent host information and command results over the established C2 channel (‘transmitted “Info” and “pingo” messages’; ‘reported to the C2 server using “OK” or “ERR” responses’).
- [T1021.001 ] Remote Services: Remote Desktop Protocol – Not mentioned.
Indicators of Compromise
- [URL ] Payload, configuration, and fallback downloads – https[:]//frames-1zm[.]pages.dev/frames.png, https[:]//publicwavlib[.]pages.dev/hdaudio.wav, and 4 more URLs.
- [Domain ] DNS/C2 discovery and TXT lookups – sslvalidcert.com, httptls.org, and other domains including txtcdn.net.
- [IP Address ] C2 server endpoint – 104[.]21[.]2[.]193:8443.
- [File Names ] Hidden stages and dropped components – Realtek HD Audio.wav, mav.wav, tmav.wav, atsg.wav, and 2 more files.
- [File Hashes ] Sample hashes tied to WAV, DLL, and EXE artifacts – ED276B2312F641B00F87FA18E85C48EB, BE860A15B7E5D44B0B3D67F598238FAD, and 4 more hashes.
- [Registry Path ] Payload storage and host tracking – HKLM:Softwareuf42a9660377vstdfehzr, plus the related uf42a9660377 key.
- [Windows File/Artifact ] Driver and auxiliary component – WinRing0.sys and fp.dll.