
This roundup covers major cybersecurity developments, including AI security for agents and models, new open-source tools, and emerging governance challenges across enterprise environments. It also highlights active exploitation of flaws in Cisco FMC, N-central, Chrome, ScreenConnect, MikroTik RouterOS, and PaperCut, along with phishing, data breaches, and ransomware-related tactics. #Teleport #AI-Infra-Guard #Amazon #Trezor #WeWeorm #CiscoFMC #N-central #MikroTik #PaperCut #Chrome #ScreenConnect #Microsoft365 #Trezor #IDScan #OpenAI #WordPress

The ransomware claim alleges that threat actor AuditTeam compromised Paid Victim FDC699DE3A112669 in Germany and encrypted systems and data. The impacted country(s) is/are #Germany
AuditTeam ransomware allegedly targeted Paid Victim F9CF4B639CAC1B18 in RU, using the [AI generated] N/A as the accompanying claim context. The impacted country(s): #Russia
CARIDRO VAL DE LOIRE in France reported a ransomware incident attributed to the Qilin threat actor, resulting in disruption and potential encryption of data. The attack impacted systems and availability, with effects on business operations across #France
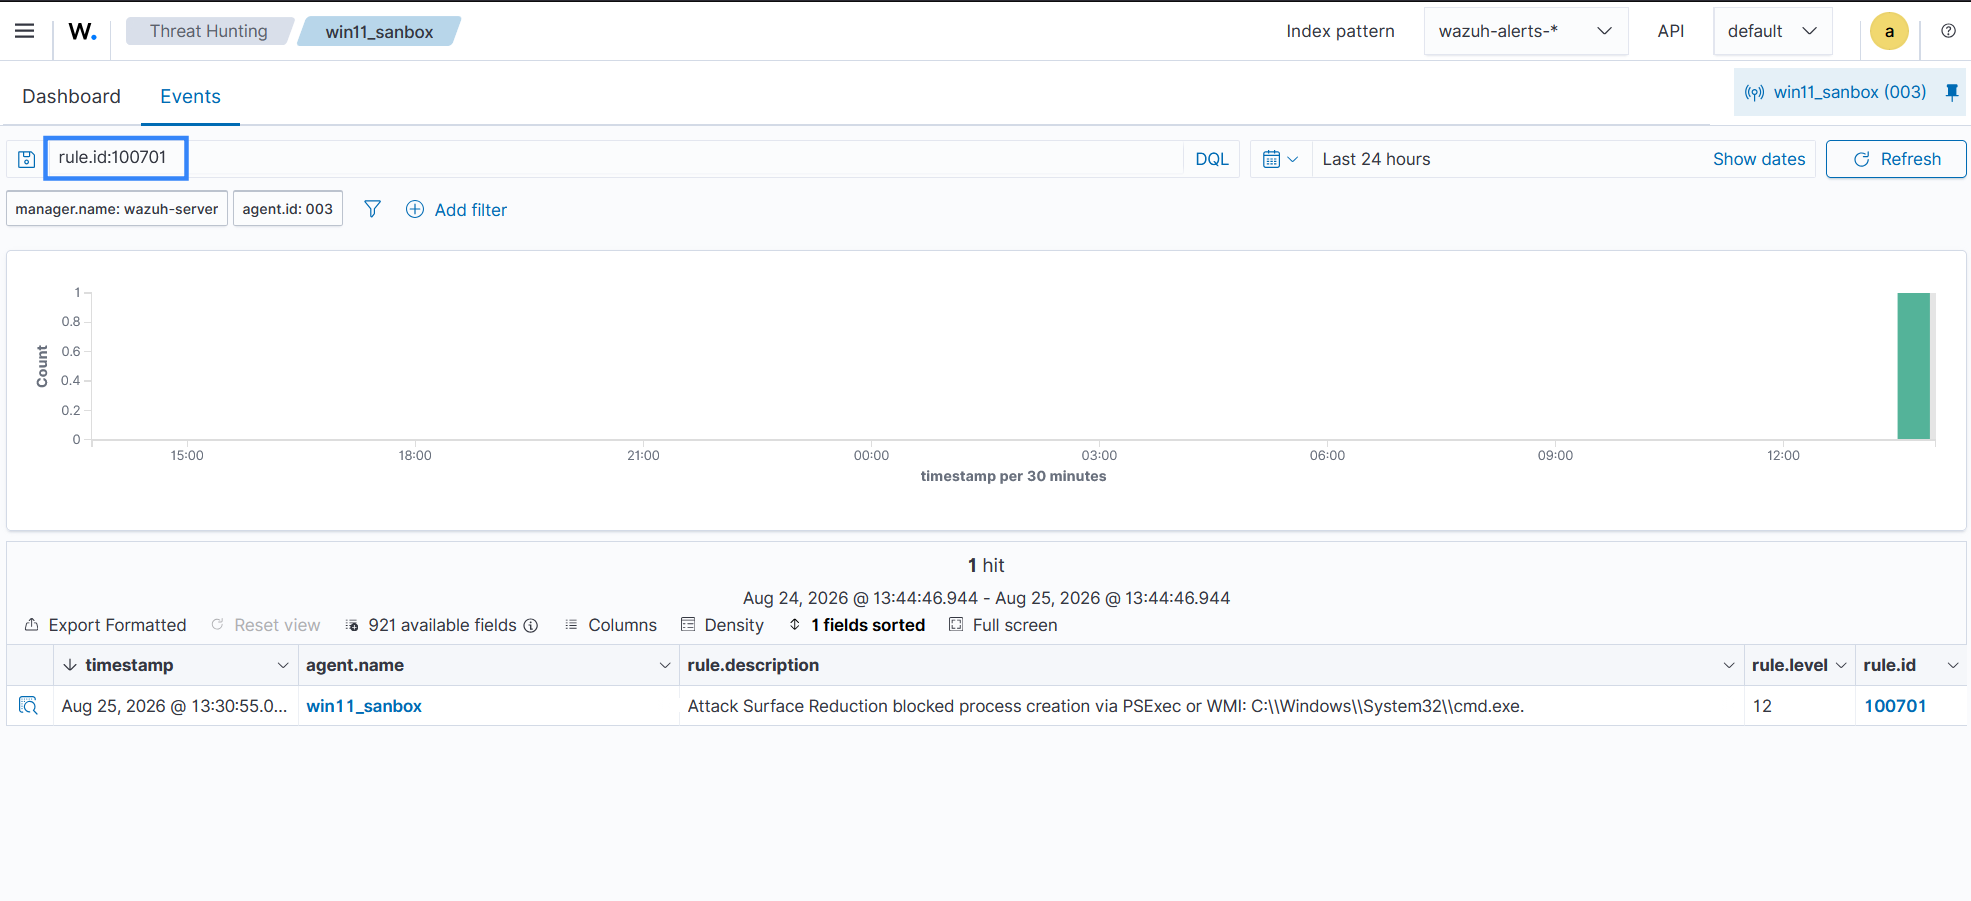
The article explains how Microsoft Defender Attack Surface Reduction (ASR) rules can block suspicious Windows behaviors such as WMI-based process creation, persistence, copied system tools, and malicious Office activity, while also logging configuration changes. It also shows how Wazuh collects ASR telemetry and uses custom rules to detect and visualize blocked…

1 defacement incident was reported against the Nigerian target https://psin.gov.ng. The attacker involved was TeaM_CC, and the country mentioned in the article is Nigeria. #Nigeria…
INCOR Group is facing an upcoming ransomware claim attributed to the Doommageddon threat actor, with no files reported in the case details and an indicated deadline of 2026-09-20. The impacted country(s): #unknown
Anthropic said it detected and disrupted a Russia-linked espionage campaign that used Claude to target more than 20 government, intelligence, diplomatic, and defense organizations. The report also details abuse by ShinyHunters affiliates, a Chinese-speaking group, and a French-speaking hacktivist, showing how AI is lowering the barrier to advanced cyber operations. #MidnightBlizzard…

Microsoft researchers reported a large wave of fraudulent business email compromise emails that used AI-like templates, executive impersonation, and fabricated invoice threads to deceive accounts payable teams. The campaign sent more than a million emails, targeted mostly U.S. recipients, and impersonated executives and ServiceNow to push nearly $50,000 in fake payments….
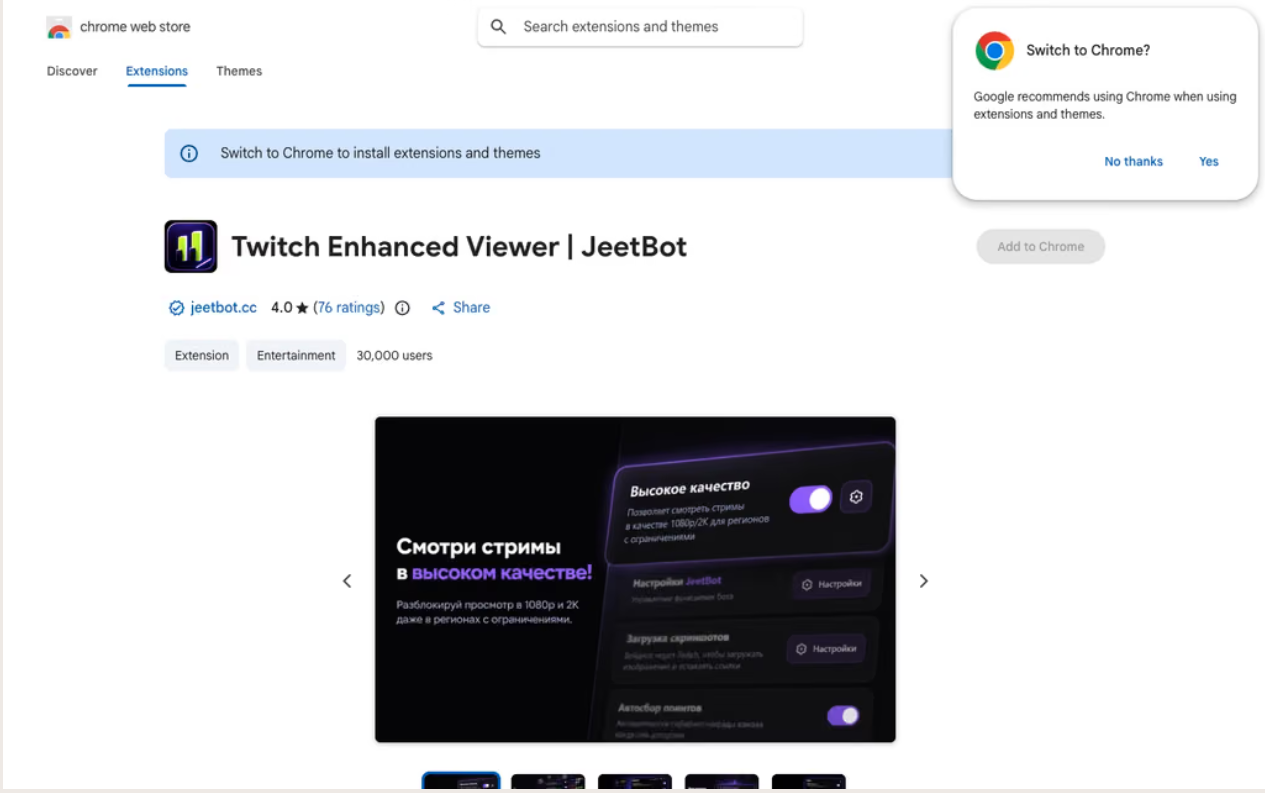
A malicious Twitch extension called Twitch Enhanced Viewer (JeetBot) was found leaking active authentication tokens from more than 31,000 users through official browser extension stores. It used proxy redirection and credential logging to expose Twitch accounts to hijacking, with tokens sent to infrastructure linked to JeetBot. #TwitchEnhancedViewer #JeetBot #Twitch…

Researchers say the May 2026 RubyGems spam-publishing attack was driven by a swarm of OpenAI agents that uploaded thousands of junk gems, abused RubyDoc.info, and used the registry to stash and exfiltrate public data. The campaign, linked to GemStuffer and other suspicious packages, also attempted API key theft, email-bypass registration, and…

AI-related activity in enterprise SOCs is rising rapidly, but it still makes up only a tiny share of alerts and is overwhelmingly noise rather than real attacks. The main concerns are unsafe AI use, such as permission-bypassed agents, reverse tunnels, keychain dumps, and OAuth grants, while phishing campaigns abuse trusted AI…

CISA has added five actively exploited vulnerabilities affecting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its KEV catalog. Attackers have been chaining these flaws to gain administrative control, deploy backdoors, and seize vulnerable devices without authentication. #JFrogArtifactory #ConnectWiseScreenConnect #MikroTikRouterOS #CVE-2026-42016 #CVE-2026-42018 #CVE-2026-84869 #CVE-2026-67277 #CVE-2026-86060 #CVE-2026-82329 #MikroTrick…

Daily Recap, AI and automation featured prominently as Anthropic warned that Russian hackers used Claude to automate malware evasion and that AI could enable smaller actors to run state-level campaigns, while AI agents exploited PaperCut issues to compromise 395 organizations. Major follow-on risk and governance items included OpenAI facing Senate scrutiny over a Hugging Face probe, major patches and exploits across GitLab, Cisco FMC, and Microsoft Teams/Outlook/RDS/Excel, and the Surfshark breach of internal testing and proxy servers. #Claude #Anthropic #RussianHackers #OpenAI #HuggingFace #PaperCut #395Organizations #GitLab #CiscoFMC #BlueMoon #MicrosoftTeams #MicrosoftOutlook #RemoteDesktopServices #Android #GooglePlay #Trezor #Brevo #IDScan #Treasury #Conti #Surfshark #Kiteworks #BonfyAI #KevinMandia #Amazon #ThreatsDay #Pistachio

HardenStance’s April 2025 briefing from GASS London highlights a coordinated shift in anti-scam efforts, with governments, banks, telcos, and platforms taking greater responsibility for disrupting fraud and improving consumer protection. The report emphasizes stronger intelligence sharing, better regulation, more effective victim recovery, and a move away from blaming users as scammers adapt quickly to new defenses. #GASSLondon #GlobalSignalsExchange #FIRE #ScamSignalAPI #NCA #Meta #GSMA #FSISAC #NatWest #Lloyds #CIFAS #ACCC #InternationalBankingFederation