Security awareness training remains widely used, but the article argues that generic, compliance-driven programs often fail to keep pace with modern social engineering and AI-enabled attacks. It concludes that training is most effective when combined with behavioral nudges, frequent refreshers, and stronger technical defenses rather than relied on as the sole…
Cisco released patches for 35 vulnerabilities across Meraki, License On-Prem, NX-OS, APIC, and Finesse, including more than a dozen critical-severity issues. The fixes address flaws ranging from memory corruption and improper access control to unauthenticated remote code execution, with Cisco saying there is no evidence of active exploitation. #Cisco #Meraki #LicenseOnPrem…
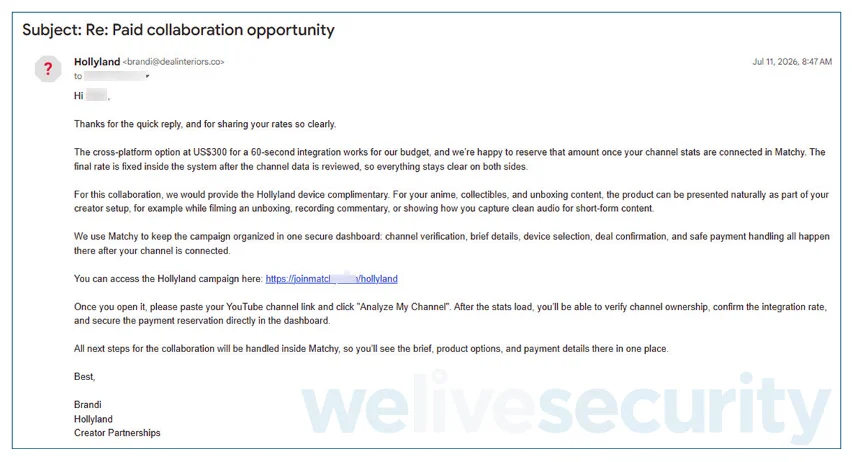
Scammers are impersonating brands like Hollyland, Nike, Spotify, and Maono to lure YouTube creators into fake sponsorship deals that end with a fraudulent Google sign-in page. Once victims enter their credentials and verification code, attackers can take over their Google services and YouTube channels, sometimes changing recovery details and backup codes to lock creators out. #Hollyland #Nike #Spotify #Maono #Google #YouTube
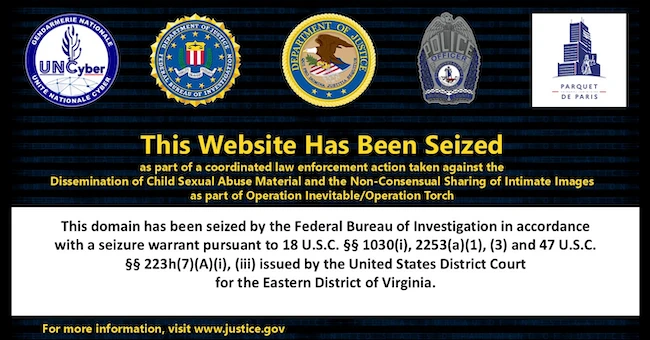
The FBI and French law enforcement seized NudeLeaksTeens, a website that sold hacked and stolen sexually explicit images and videos of young women and girls, and arrested the suspected administrator in northern France. Investigators said the platform also distributed child sexual abuse material, affected more than 17,000 victims worldwide, and stored about €700,000 in cryptocurrency. #NudeLeaksTeens #FBI #ParisProsecutorsOffice

The nightspire ransomware targeted the Asociaci,ón de Escribanos del Uruguay, a professional body supporting notaries across Uruguay with services such as guidance, representation, and professional training. The attack disrupted the organization’s operations and affected its legal services stakeholders in #Uruguay
Eclipse ransomware targeted Global AirFreight International, a Singapore-based logistics solution provider delivering air freight, ocean freight, cross-border trucking, and contract logistics services for critical shipments across multiple industries. The incident impacted operations in #Singapore
Ransomware claimed to be carried out by Eclipse targeted DIPECARR, a leading Brazil truck parts distributor founded in 1994, disrupting operations across its nationwide network. The incident impacted Brazil. #Brazil
SonicWall and Splunk released urgent security updates for multiple critical and high-severity vulnerabilities that could enable arbitrary code execution, unauthorized access, SSRF, and other attacks. SonicWall said its SMA1000 appliances are affected by a pre-authenticated SSRF flaw, while Splunk fixed serious issues across Splunk Enterprise, MCP Server, and the Add-on for…
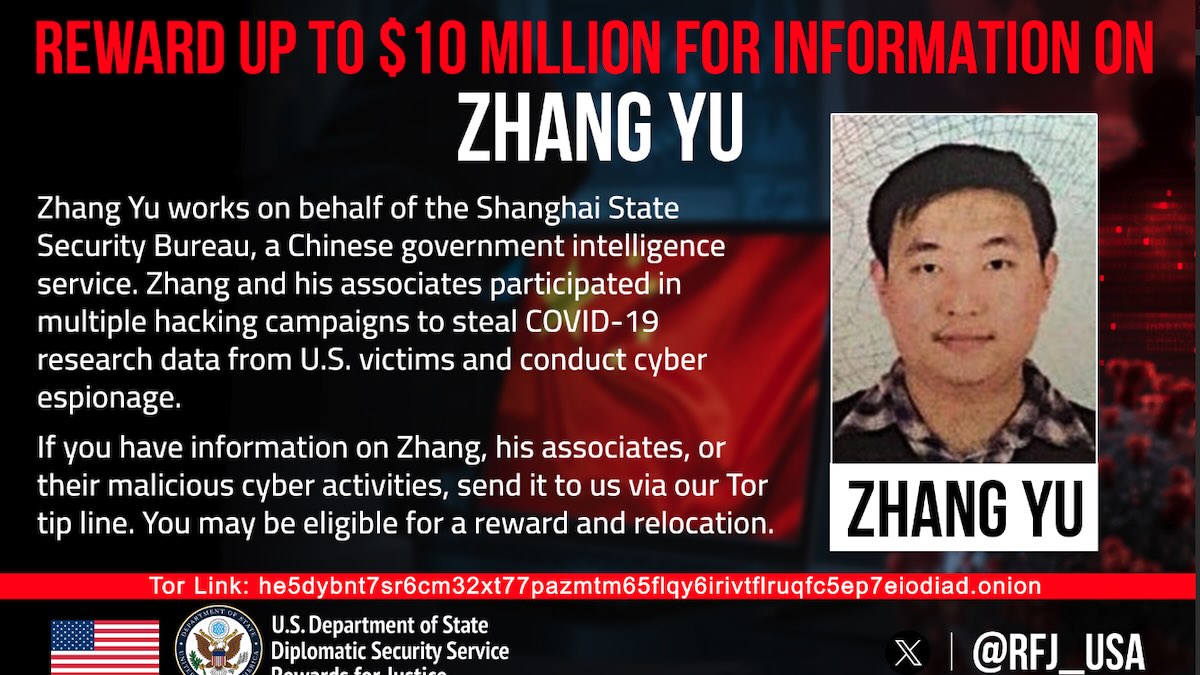
The US Department of State is offering up to $10 million for information on Zhang Yu, a Chinese national accused of helping carry out the Hafnium campaign against Microsoft Exchange servers. Zhang and Xu Zewei allegedly worked on behalf of China’s Shanghai State Security Bureau to steal sensitive information and compromise…
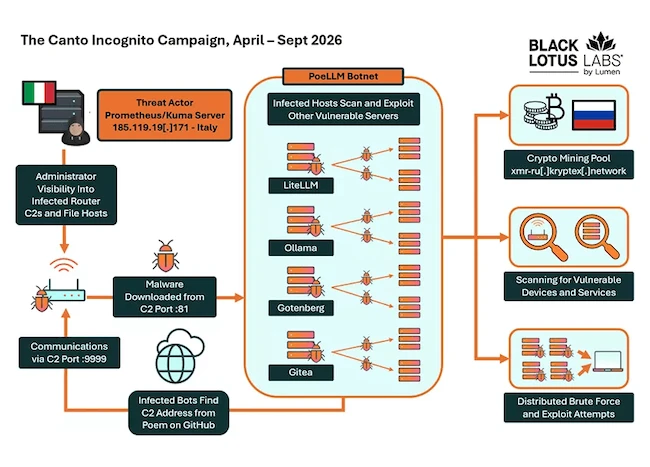
Black Lotus Labs uncovered Canto Incognito, a campaign in which the PoeLLM malware hides its C2 address in a GitHub poem and targets exposed AI services and open-source tools. The operation has compromised more than 3,400 servers, deploying miners, scanning for new victims, and potentially testing brute-force attacks. #PoeLLM #CantoIncognito #BlackLotusLabs #LiteLLM #Ollama #Gotenberg #Gitea #IvantiSentry #XMRig #Iron #Kryptex
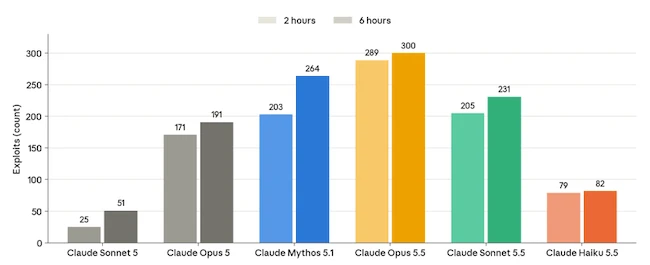
Anthropic’s Claude Haiku 5.5 delivers faster performance and stronger cybersecurity capabilities than Haiku 4.5, while still remaining below Sonnet 5.5 and Opus 5.5 in offensive skill. The model also shows improved resistance to malicious prompts, prompt injection, and harmful code-generation requests, with new pricing and platform availability across major cloud providers. #ClaudeHaiku55 #ClaudeCode #Sonnet55 #Opus55 #Anthropic #AmazonWebServices #GoogleCloud #MicrosoftAzure

Quantum computing is emerging as a serious national security threat because it could eventually break today’s widely used encryption and expose sensitive emails, financial data, government communications, and military systems. The article urges Congress and federal agencies to accelerate post-quantum cryptography efforts now, warning that adversaries may already be stealing encrypted data for later decryption. #PostQuantumCryptography #NSA #Google #CNSA20 #WhiteHouse #China
lockbit5 ransomware impacted Argentina Valores S.A. (avsa.com.ar), disrupting operations and capital markets services in Argentina. The incident affected systems used for financial processing and access, resulting in service interruption and potential data compromise #Argentina
The BYOD ransomware group threatened to compromise “Some semi-samples Of Liberty X TMO,” claiming victims were breached and implying additional activity beyond the “Trump Mobile” theme. The claim references “Amusing tweet” teasing further impact with a “Sneak peek,” and ends with the impacted country(s): #.
Morton LTC Pharmacy in the US reported that RunSomeWares ransomware disrupted its operations as part of an extortion campaign. As a family-owned Wisconsin pharmacy, Morton LTC was impacted by the attack, with consequences felt across the impacted country(s): #UnitedStates