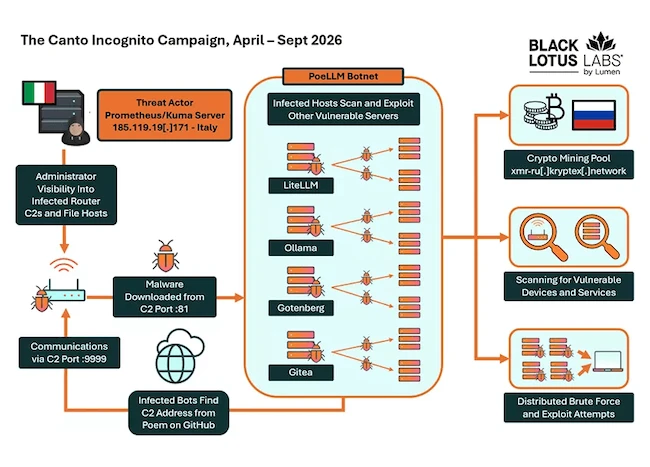
Black Lotus Labs uncovered Canto Incognito, a campaign in which the PoeLLM malware hides its C2 address in a GitHub poem and targets exposed AI services and open-source tools. The operation has compromised more than 3,400 servers, deploying miners, scanning for new victims, and potentially testing brute-force attacks. #PoeLLM #CantoIncognito #BlackLotusLabs #LiteLLM #Ollama #Gotenberg #Gitea #IvantiSentry #XMRig #Iron #Kryptex
Keypoints
- PoeLLM hides its C2 server address inside a poem on GitHub.
- The campaign has hit more than 3,400 servers since April 2026.
- Victims often run vulnerable LiteLLM, Ollama, Gotenberg, or Gitea services.
- Infected systems mine cryptocurrency using XMRig and Iron with Kryptex.
- The botnet also scans for new targets and may be testing SSH brute-force attacks.
Read More: https://www.helpnetsecurity.com/2026/10/08/poellm-malware-github-poem-ai-servers/