Cybersecurity News | Daily Recap [14 Sep 2026]

Daily Recap, Revolut disclosed a breach exposing personal and financial data, including passports, while Telus warned customers about account compromises linked to unauthorized access activity. On the defense side, CISA reported active exploitation of a max-severity GitLab flaw, researchers detailed JFrog Artifactory issues used to deploy a backdoor, and Microsoft noted September updates can break audio on some Windows PCs and cause RDS failures on Windows Server.
#Revolut #Telus #GitLab #JFrogArtifactory #CISA #BigBear2.0 #HVNC #Marimo #GRAYRABBIT #GRIMWEDGE #SUPERSTOMP #LONGTALE #SloppyRAT #ClearFake #WebDAV #Amatera #ZigCryptoStealer #NetSupportManager #Debian13.7 #Microsoft #WindowsServer #GoogleWorkspace #NSA

Read More

This report explains how illicit casino websites are used for illegal gambling, money laundering, scam gambling, and as decoys for PeckBirdy command-and-control infrastructure. It shows that China-aligned APT groups hide malware endpoints inside Chinese-language casino and adult sites, with domains like vip311[.]cc, cache-mcp[.]com, and mcp-source[.]online slipping past detection. #PeckBirdy #vip311[.]cc #cache-mcp[.]com #mcp-source[.]online

Read More
BambooToken malware controls Windows and Linux systems via MQTT

BambooToken is a previously unknown malware framework active since at least 2023 that now uses MQTT for command-and-control on Windows and Linux systems. Black Lotus Labs found it in campaigns targeting enterprise servers and infrastructure used by mobile apps, legal and financial services, with signs of possible China-aligned operations. #BambooToken #MQTT #BlackLotusLabs #TendyronOnKey #KingsoftOffice #GitLab

Read More
CenterPoint Energy confirms customer data stolen in cyberattack

CenterPoint Energy disclosed that an unauthorized third party accessed personal information tied to some customers after a threat actor claimed to have stolen and leaked 7.49 million records. The company says its electric and gas services were not affected, while it continues investigating the scope of the incident and notifying impacted parties. #CenterPointEnergy #4d722e4d656f77

Read More
Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites

A compromised Admin Menu Editor Pro website pushed malicious plugin updates to WordPress customers, creating hidden user accounts and deploying a web shell on affected sites. The incident impacted at least 230 customers across about 1,500 sites, and users of versions 2.35 and 2.36 are urged to check for signs of compromise and restore from a safe backup if possible. #AdminMenuEditorPro #JanisElsts #WordPress

Read More
 Million Sandbox Challenge Uncovers Linux Kernel Flaws

Vercel’s two-week sandbox bug-bounty challenge generated 1,285 reports, but none of the findings allowed access to customer data. The most significant issues were two Linux kernel networking flaws, and Vercel also used the event to improve its sandbox and automate triage with an agentic system. #Vercel #LinuxKernel #Firecracker #HackerOne #TrailofBits…

Read More
“We Think the Security Control Is Working” Is No Longer Good Enough

Security, risk, and control assessments are no longer enough when boards, customers, and regulators want proof that controls are working right now. The article argues for continuous control monitoring to replace point-in-time checks, using live evidence to keep pace with changing environments and reduce real risk. #NIST #CybersecurityFramework #GRC…

Read More
Anthropic Data Privacy Concerns Prompt Major Tech Restrictions

Anthropic’s AI safety report exposed that the company can access full user logs, including prompts, questions, and uploaded files, raising serious confidentiality concerns for enterprise customers. As a result, organizations such as Nvidia, Palantir, Booz Allen Hamilton, and an unnamed utility company have restricted or rejected Claude use due to Anthropic’s…

Read More
Ransom! neumerkel-gmbh.de (SEP-2026)

The City of Fort Smith, Arkansas, US, was compromised by threat actor interlock, leading to a major ransomware-related leak of 5.6 TB of confidential data, including public safety (police, fire, and 911 communications), water and sewer infrastructure, and city information systems. Exposed data included sensitive law enforcement records and PII (including over 100,000 SSNs), along with extensive datasets covering phone records and 911 calls/incidents that support critical public services. #UnitedStates

Read More
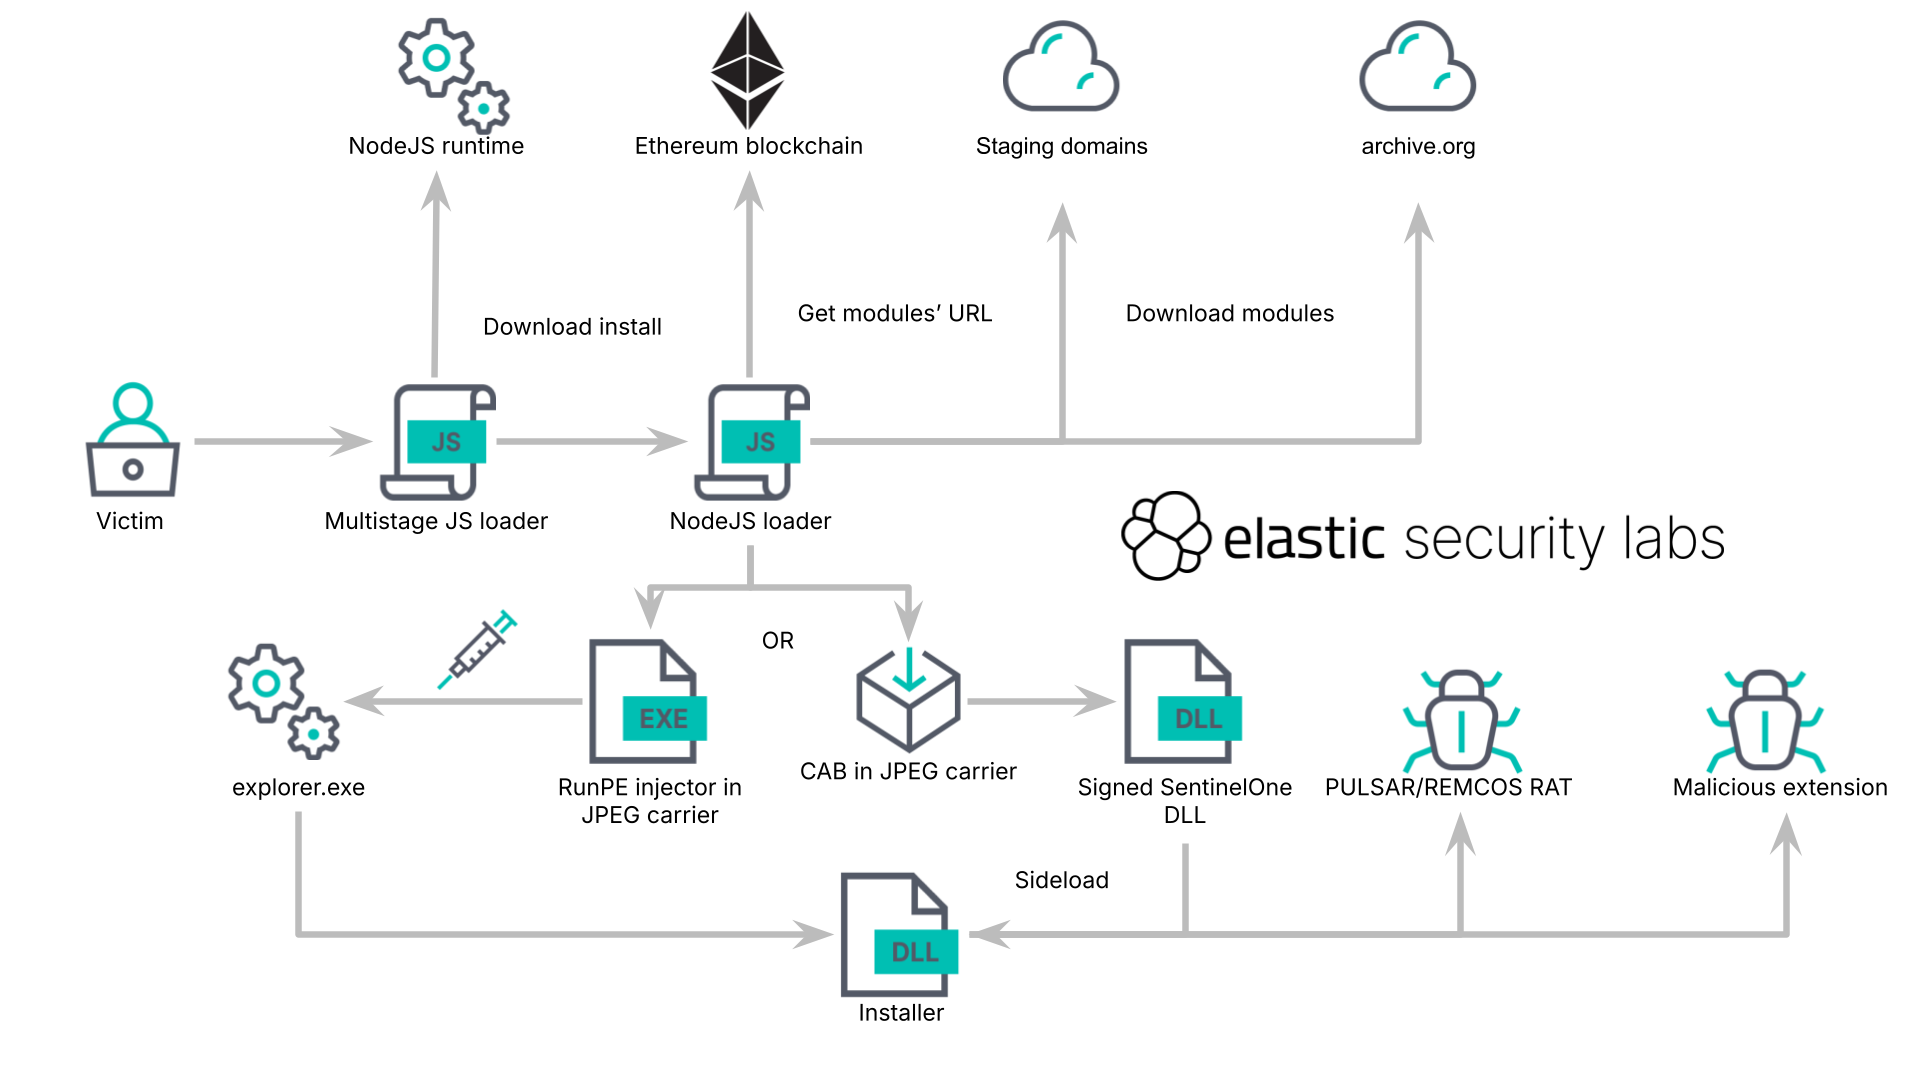
The extension you never installed: KREMLIN forges Chrome’s own integrity checks to steal banking sessions

Elastic Security Labs tracked REF9334, a Brazilian banking malware operation using the KREMLIN toolkit to deliver malicious browser extensions, credential theft, and staged loaders through JavaScript, Node.js, RunPE, and Ethereum-based infrastructure. The campaign targeted Brazilian banking users and financial institutions, and Threat Command temporarily disrupted more than 1,500 infections by registering the network canary domain used by the malware. #REF9334 #KREMLIN #ThreatCommand #Ethereum #SentinelOne

Read More