The ransomware claim targets laconcepcion.com.mx in Mexico, with the threat actor safepay asserting that the organization—one of the principal private healthcare providers in the region—serves patients from Coahuila. The impacted country(s): #Mexico

Safepay ransomware targeted triniticaring.org, a US organization jointly owned by Guardian Angels Senior Services of Elk River and Cassia, an Augustana/Elim affiliation. The incident resulted in disruption to systems and operations across the United States. #UnitedStates

CrowdStrike identified PhantomRaven, a JavaScript information stealer distributed through malicious npm packages and likely written with help from a large language model, with the operator posing as a bug bounty hunter to target organizations and potential rewards. The campaign used typosquatted packages, attacker-controlled domains, and automated exfiltration of system and CI/CD…
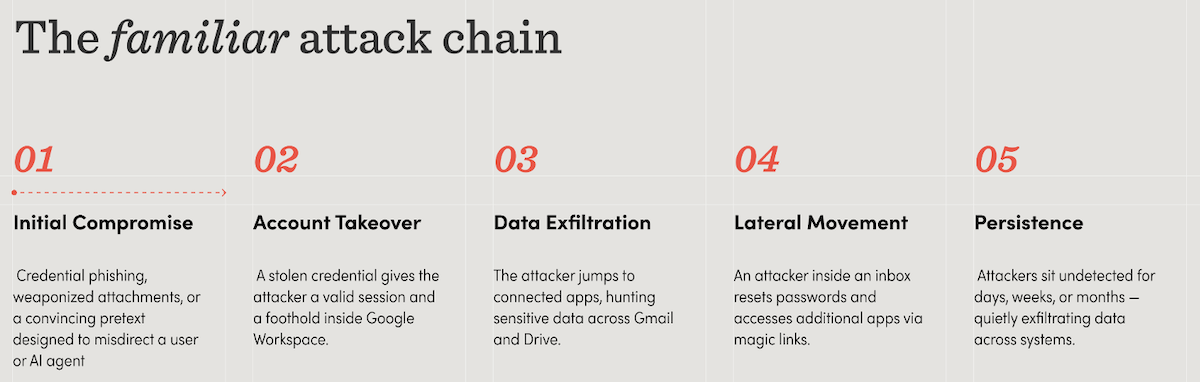
The Vercel and Composio incidents show that modern workspace attacks can start with OAuth grants instead of email, allowing access to Gmail, Drive, and broader connected systems. The article argues that AI agents using legitimate OAuth access can follow the same dangerous path, so organizations need environment-level controls across email, OAuth, and data access. #Vercel #Composio #OAuth #Gmail #Drive #GoogleWorkspace
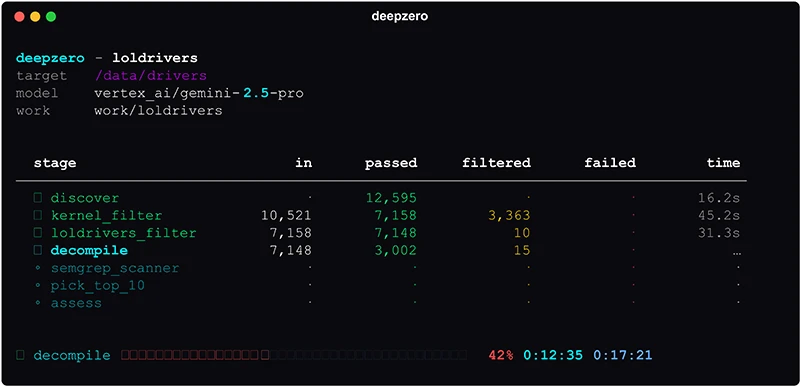
DeepZero is an open-source, Python-based engine that automates the hunt for exploitable Windows kernel drivers by parsing binaries, filtering candidates, and using a language model to assess exploitability. Its bundled pipeline focuses on BYOVD research and has already found multiple verified vulnerabilities in the Snappy Driver Installer corpus. #DeepZero #SnappyDriverInstaller #BYOVD
Gourab Basu of meshIQ explains that AI agent governance must happen inside the execution flow, because prompts alone cannot reliably control nondeterministic agent behavior. He also warns that scaling from a few agents to thousands requires framework-independent controls, auditability, and human approval for actions that affect enterprise systems. #meshIQ #GourabBasu

An actor using the name Sc0rp10nn is allegedly offering access to Hidalgo C5’s emergency dispatch system in Mexico, claiming persistent backdoor access from an earlier compromise. If true, the access could expose live incidents, caller details, and dispatch operations, while enabling false reports, patrol redirection, and assignment cancellation. #HidalgoC5 #Sc0rp10nn #Carbyne…
A forum actor calling themselves ChimeraZ claimed to have leaked 75 GB of data from Papouille France, totaling 240,177 files. The post reportedly includes email records, CRM contact data, and document metadata, but the claim remains unverified. #PapouilleFrance #ChimeraZ #BlgCloud…
A forum actor known as Venus1337 claims to be selling data from AFTT and FRBTT, including 66,852 subscriber records, 17,441 user records, and credentials for 87 club administrator accounts. The alleged breach involved a file-upload RCE, a deployed web shell, hardcoded database credentials in secret.php, and plaintext admin passwords, but the…
Ukrainian President Volodymyr Zelensky has appointed Ihor Klymenko to lead the National Cybersecurity Coordination Center, which oversees Ukraine’s government response to major cyberthreats. The move comes amid a wider reshuffle in Ukraine’s security leadership and ongoing efforts to counter Russian cyber operations and criminal networks. #VolodymyrZelensky #IhorKlymenko #NationalCybersecurityCoordinationCenter #NSDC #RussianCyberOperations…
British, American, and Dutch agencies warned that Iranian state-sponsored hackers are using CHOSEN BRICK spyware to target dissidents, activists, journalists, and others seen as threatening the regime. The malware is spread through social engineering and fake lures, then used to steal data, monitor victims, and support harassment and physical intimidation. #CHOSENBRICK…
Norwegian law enforcement is investigating whether Telenor may have aided crimes against humanity by repeatedly handing over customer traffic data to Myanmar’s military regime after the 2021 coup. The probes also examine whether Telenor violated sanctions when it sold its Myanmar subsidiary, amid claims that the company’s data and surveillance equipment…
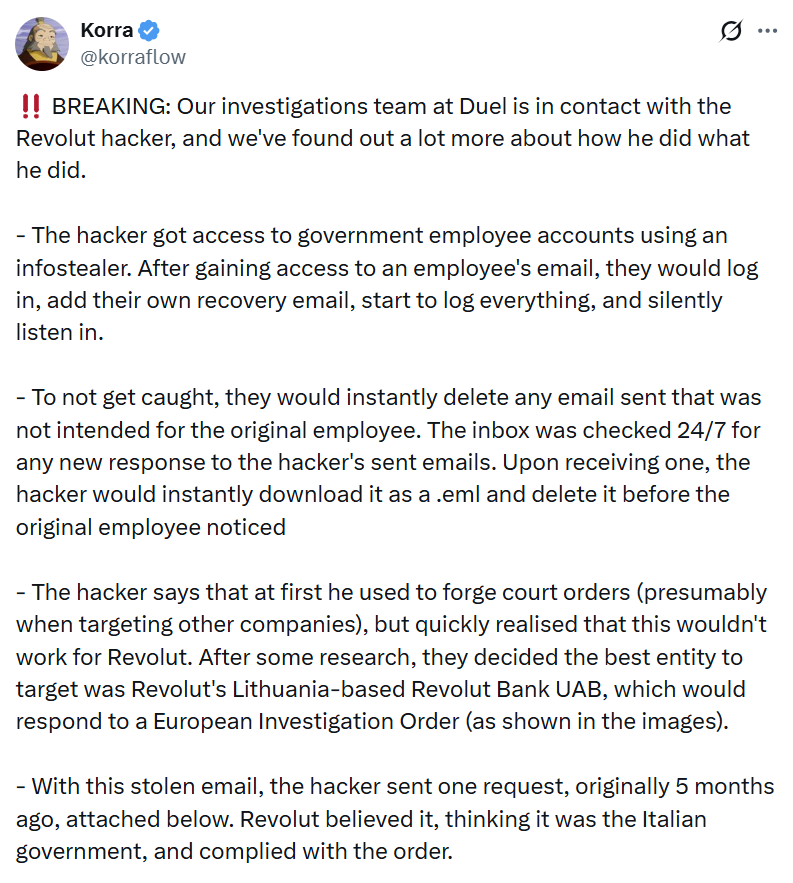
Duel’s investigations team says the hacker behind the Revolut incident used compromised Italian government email accounts, infostealer logs, and careful deletion of traces to sustain a five-month fraud campaign. Hudson Rock’s analysis suggests the attacker likely relied on pre-compromised pec.interno.it credentials rather than directly infecting the victims themselves. #Revolut #RevolutBankUAB #pecinternoit #ItalianMinistryoftheInterior #HudsonRock #Duel
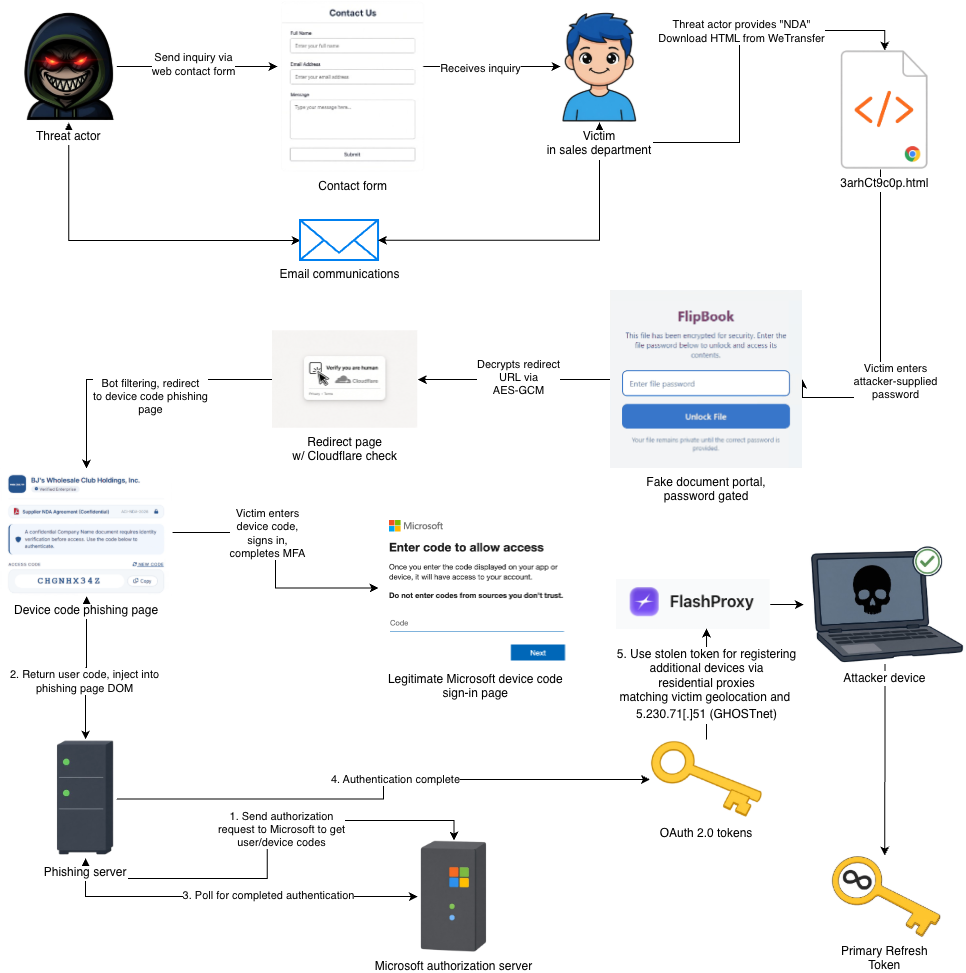
eSentire TRU uncovered GhostCode, an active device code phishing campaign delivered through web contact forms and disguised business outreach, which abused Microsoft device code authorization to steal tokens, register devices, and obtain a Primary Refresh Token in under 78 seconds. The campaign used layered HTML obfuscation, WeTransfer-hosted lures, compromised or lookalike infrastructure, residential proxy rotation, and Microsoft/Cloudflare trust signals to bypass detection and complete post-compromise access. #GhostCode #GHOSTnet #EvilTokens #Storm2372 #MicrosoftAuthBroker #CloudflareTurnstile #WeTransfer #Salesforce #BJsWholesaleClub
Owen Leigh Optometry in the United Kingdom reported a ransomware incident involving threat actor dragonforce, with the organization claiming full data loss exceeding 400 GB. “What we see is dependant upon what we are looking for and what we managed to see last time.” #UnitedKingdom