Microsoft will retire the Calendar, People, and Files Microsoft 365 companion apps on December 16, 2026, and admins are being urged to remove them from managed devices. Microsoft has already stopped installing the apps through Microsoft 365 updates and also reminded organizations to prepare for upcoming Entra ID and SMS sign-in changes. #Microsoft365 #EntraID #FIDO2
Noopur Davis built an unconventional path from software developer to Comcast’s Global CISO by embracing unexpected opportunities at Intergraph, Carnegie Mellon University, Intel, and Comcast. Her leadership style emphasizes calm decision-making, strong teamwork, empathy, and balancing security rigor with business needs. #NoopurDavis #Comcast #CarnegieMellonUniversity #Intel…
A fake LastPass Authenticator distributed through GitHub was used in a long-running impersonation campaign that spoofed at least 40 organizations and delivered the Rapuncel infostealer. The malware deploys a kernel driver to disable security tools, steal passwords and wallet data, and persist on infected systems until the driver is removed. #LastPass…
Google was fined 403 million euros by Ireland’s Data Protection Commission for unlawfully handling users’ location data under the EU’s privacy rules. The investigation found issues with Web & App Activity, Location History, and Android’s Location Accuracy feature, and three more Google privacy probes remain open. #Google #IrelandDataProtectionCommission #GDPR #LocationHistory #Android…
South Asian manufacturing is under sustained pressure from ransomware groups and nation-state actors that are exploiting IT/OT convergence, vendor access, and legacy industrial systems to disrupt operations and steal intellectual property. The assessment highlights active threats such as thegentlemen, worldleaks, dragonforce, APT41, Lazarus Group, and APT36/Transparent Tribe, with India and SAARC manufacturers urged to strengthen identity security, OT segmentation, and supply-chain defenses. #APT41 #LazarusGroup #APT36 #TransparentTribe #thegentlemen #worldleaks #dragonforce
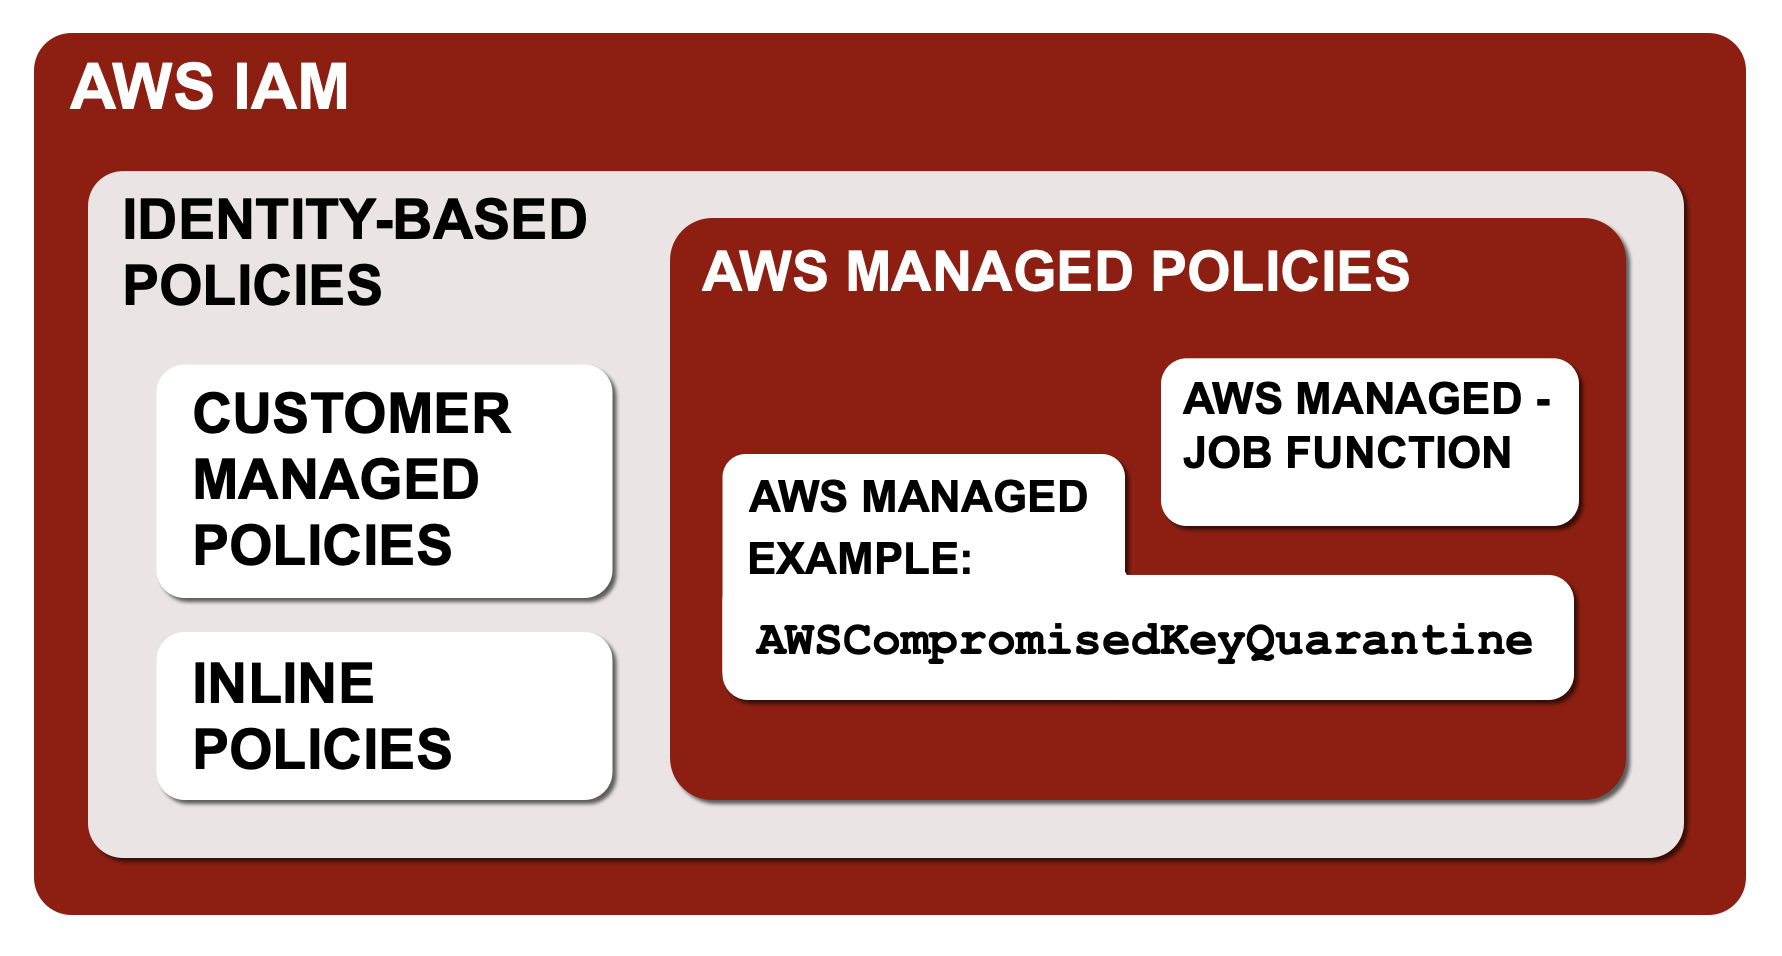
AWSCompromisedKeyQuarantine is an AWS managed policy that automatically quarantines publicly exposed IAM access keys and has evolved from v1 to v3 to deny more high-risk actions as cloud attack tactics changed. The article also explains how GitHub secret scanning, push protection, and validity checks interact with AWS to detect exposed credentials…
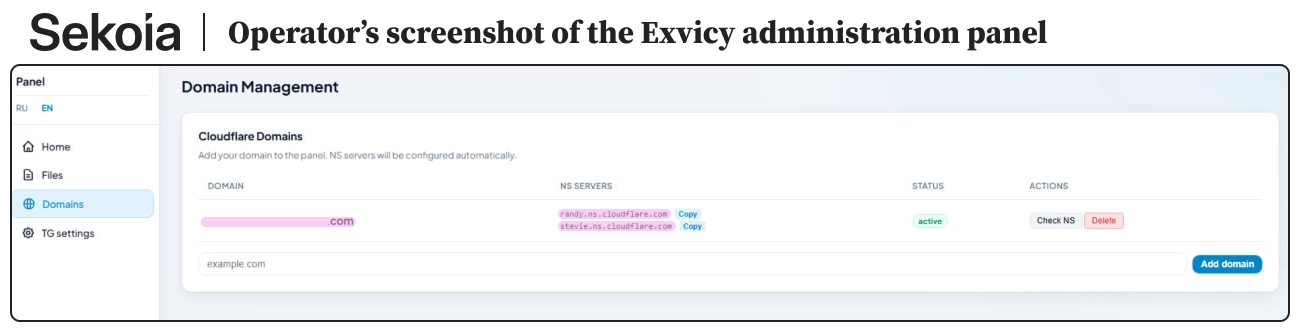
Sekoia TDR uncovered Exvicy, a ClickFix Malware-as-a-Service framework advertised on Exploit.IN by the threat actor @Exvicy and used to impersonate Cloudflare Turnstile verification pages on compromised WordPress sites. The investigation linked Exvicy to active operator infrastructure, PowerShell downloaders, and code reuse from ErrTraffic, indicating Exvicy is a copycat framework built from the same client-side codebase. #Exvicy #ErrTraffic #Exploit.IN #CloudflareTurnstile #WordPress

Fastly has introduced AI Runtime Control, AI Firewall, and expanded API Security to help organizations govern AI usage, protect AI applications, and control agent access to enterprise APIs in real time. These capabilities extend Fastly’s edge platform to secure AI workloads at scale while addressing rising AI traffic, budget pressure, and risks like prompt injection and unauthorized API use. #Fastly #AIRuntimeControl #AIFirewall #APISecurity #PromptInjection
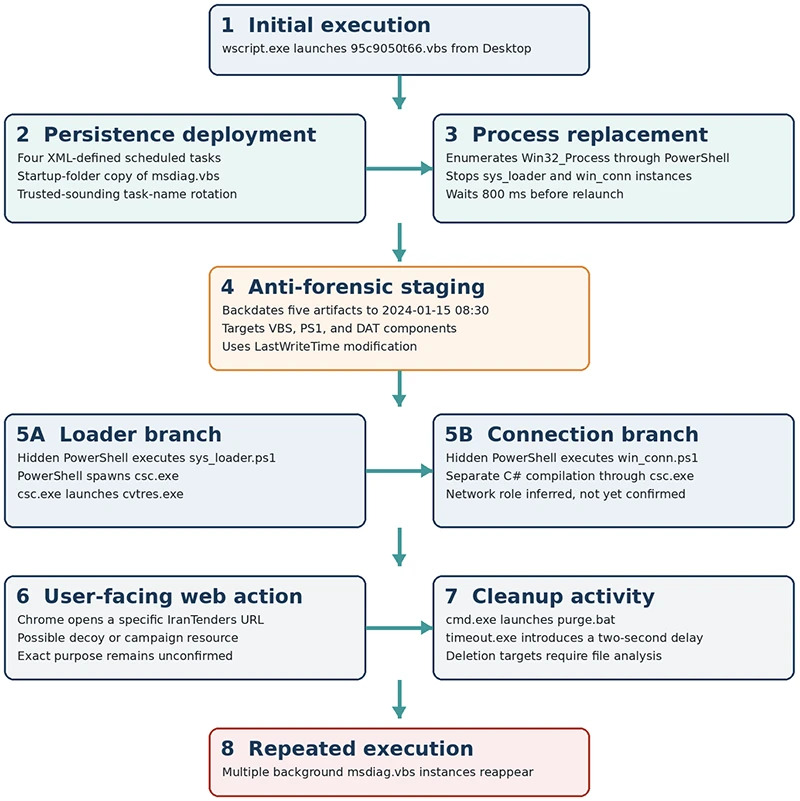
Researchers analyzed TASK#STOMP, a Windows backdoor that hunts for business documents, exfiltrates them, and persists to steal new or modified files while also collecting Wi-Fi credentials, clipboard text, screenshots, and operator commands. Securonix says the malware uses multiple footholds, likely arrives via phishing with a ZIP or ISO/IMG attachment, and shows no clear attribution to a known APT. #TASKSTOMP #Securonix #WindowsScriptHost #VBScript #PowerShell

House Democrats introduced the CISA Force Structure Assessment Act to review whether the agency still has the workforce, training, and certifications needed after about 1,000 employees departed during President Donald Trump’s second term. The bill aims to identify gaps in CISA’s ability to protect federal systems, critical infrastructure, and state and local partners amid growing risks from AI, quantum computing, and threats from Iran. #CISA #DonaldTrump #SeanCairncross #Iran

Metaencryptor ransomware targeted Bruker Corporation, a Massachusetts-based US global scientific technology company, reportedly compromising its systems used for advanced analytical instruments and services across multiple industries. The attack impacted the United States. #UnitedStates
Hudson MD Group, LLC, a U.S.-based multispecialty medical group headquartered in West Orange, New Jersey (established in 2019), reported a ransomware incident attributed to threat actor metaencryptor, impacting its network of outpatient practices and care centers across New Jersey. The group provides services including primary/internal medicine, cardiology, gastroenterology, neurology, obstetrics and gynecology, nephrology, urology, and other specialties, with an integrated practice model supporting shared administrative infrastructure. #UnitedStates
Moneymessage is alleged to have deployed ransomware against U.S. Electrical Services and Wiedenbach Brown, aiming to disrupt operations and coerce payment. The impacted country(s): #Unknown
Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after the September 2026 security updates. Affected users may see backup errors, false reconnect prompts, and Event Viewer crashes tied to FileHistory.exe and KERNELBASE.dll. #FileHistory #FileHistory.exe #KERNELBASE.dll #Windows11 #Windows10
Microsoft is urging Entra ID administrators to move users to phishing-resistant sign-in methods like passkeys before SMS first-factor sign-in is retired in February 2027. Organizations should prepare now by adopting alternatives such as QR code authentication and FIDO2 security keys, because SMS and voice will no longer be available for completing multifactor authentication and account sign-in. #Microsoft #EntraID #Passkeys #FIDO2