Microsoft-led disruption efforts have taken down the EvilTokens phishing service, which compromised more than 12,000 inboxes across over 10,000 organizations by combining account theft with AI-assisted mailbox analysis. The operation used stolen access to identify financial conversations, impersonate trusted contacts, and prepare fraud at scale, while authorities also arrested two suspects in connection with the service. #EvilTokens #Microsoft #OpenAI #Cloudflare #Coinbase #HealthISAC
WordPress released version 7.1.2 to fix CVE-2026-87902, a critical path traversal flaw in get_page_template() that could let an unauthenticated attacker load an arbitrary PHP file from outside the active theme directory. Under certain server and theme conditions, this could lead to remote code execution, so WordPress recommends updating immediately. #WordPress #CVE-2026-87902

ISO 27001 should be treated as the foundation for an evolving risk program, not the finish line or proof that controls will always keep working. As AI adoption accelerates, organizations need continuous control monitoring, clear ownership, and AI governance layered on top of established risk methods to make sound decisions at business speed. #ISO27001 #ISO42001 #NISTAIRMF #OneTrust

Daily Recap, phishing and malware activity stayed active, including EvilTokens compromising 12,000 Microsoft accounts, Contagious Interview infecting 30,000 devices and stealing $10.71M in crypto, and TASK#STOMP exfiltrating Wi‑Fi passwords, screenshots, and business files. Attackers also used fake LastPass and Google sign-in lures to deploy the Rapuncel stealer and other components, while defenders tracked newly patched and actively exploited flaws like D-Link DIR-822A (CVE-2026-86296, CVE-2026-86510) and a CISA-flagged Zyxel issue plus three Linux kernel vulnerabilities. #EvilTokens #ContagiousInterview #TASKSTOMP #Rapuncel #LastPass #DIR-822A #CVE-2026-86296 #CVE-2026-86510 #Zyxel
One defacement incident was reported, targeting antrian-adak.polkesraya.ac.id in Indonesia. The attacker involved was KatakBeracun. #Indonesia…
F5 has issued security updates for a critical zero-day in BIG-IP APM, which is being actively exploited in remote code execution attacks when specific OAuth authorization server settings are enabled. CISA has added CVE-2026-94127 to its Known Exploited Vulnerabilities Catalog and ordered federal agencies to patch the flaw promptly. #F5 #BIG-IPAPM #CVE202694127 #CISA
Karen Serobovich Vardanyan was sentenced to 24 months in prison and 3 years of supervised release for helping carry out Ryuk ransomware attacks against multiple U.S. organizations. He and his co-conspirators breached victims including a Michigan company, a Texas school, and a technology company in Oregon, generating millions in ransom payments. #KarenSerobovichVardanyan #Ryuk #WizardSpider #Michigan #Texas #Oregon
ShinyHunters claims it breached FBI systems, stole sensitive data, and defaced the FBI jobs site to prove access. The group says it used an Oracle PeopleSoft zero-day and alleges it now has data on nearly all FBI agents and applicants. #ShinyHunters #FBI #PeopleSoft #CVE-2026-35273…
F5 and CISA warned that a critical BIG-IP Access Policy Manager (APM) flaw, tracked as CVE-2026-94127, has been exploited as a zero-day to enable unauthenticated remote code execution. The vulnerability affects specific BIG-IP APM configurations, and F5 has released hotfixes while CISA added the issue to its Known Exploited Vulnerabilities list….
Arista has issued urgent fixes for CVE-2026-93952, a critical zero-day in on-premises VeloCloud Orchestrator deployments that could let remote attackers reach privileged internal functions. The flaw affects VeloCloud Orchestrator On-Prem and has been added to CISA’s Known Exploited Vulnerabilities list, with admins urged to patch and review logs immediately. #Arista #VeloCloudOrchestrator…

Seznam (seznam.cz) in the Czech Republic was impacted by the medusalocker ransomware operation, with 115 emails reportedly extracted. The attack targeted the organization’s systems and resulted in unauthorized data access. #CzechRepublic
Aokkef (aokkef.fr) in France was targeted by the medusalocker ransomware threat actor, which extracted 137 emails from the organization. The attack resulted in ransomware impact affecting the organization in France. #France
Ransomware linked to emperador reportedly compromised the MINISTÉRIO DA FAZENDA / SECRETARIA DA RECEITA FEDERAL DO BRASIL systems, exfiltrating thousands of documents containing personnel and customer data. The threat actor also accessed user data across gov.br, including passwords, impacting #Brazil.
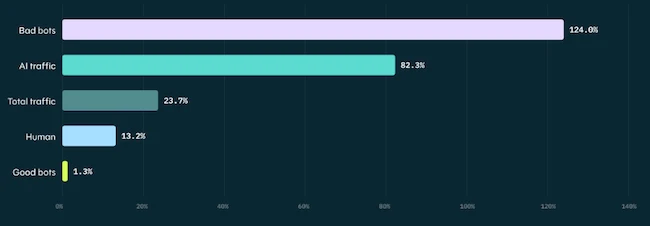
Malicious bot activity surged 124% from July 2025 to June 2026, far outpacing human traffic growth, while AI agent and LLM crawler traffic also rose sharply as attackers expanded scraping, credential stuffing, spam, and DDoS activity. DataDome’s report found that many websites still fail to detect simulated bots, and that AI assistants and malicious automation are increasingly targeting login pages, shopping carts, payment pages, and online forms. #DataDome #LLM #AIagents #CredentialStuffing #WebScraping
Scamwise from Savi is a free browser-based service that checks suspicious messages, websites, phone numbers, images, and situations for signs of fraud without requiring an account. It gives a verdict with explanations and sources, and in testing it flagged a phishing email, verified a legitimate company site, and returned an indeterminate result for a phone number. #Savi #Scamwise #CroatianGovernmentAgency #SpanishUniversity