Fresenius Medical Care reported a cybersecurity incident involving unauthorized access to a limited number of internal systems, while stating that patient care, manufacturing operations, and business continuity were not affected. The company said the incident was contained and that cybersecurity experts and law enforcement were notified on September 23, 2026. #FreseniusMedicalCare

Spirals ransomware targeted ASYAD GROUP, Oman’s global integrated logistics provider and Forbes-ranked top logistics firm in MENA. The attack disrupted the organization’s operations in #Oman
The ransomware claim targets Legis, a long-running Latin American legal and business information publisher, and alleges data access/exfiltration including SQL databases, legal documents, shareholder and ID copies, customer contract records, and detailed finance/ownership and litigation logs tied to business operations. The threat actor “rhysida” is named in connection with these alleged compromises, with impacts to Colombia, Venezuela, Argentina, Mexico, Peru, and Chile #Colombia#Venezuela#Argentina#Mexico#Peru#Chile
In Norway, settra ransomware targeted vestfrostsolutions.com, which supplies reliability and precision back bar coolers for brands including Red Bull. The attack disrupted operations for the impacted organization in #Norway
America must lead in AI while putting stronger safeguards in place to prevent powerful models from taking unintended or dangerous actions. The article argues for an AI Assurance Compact to balance AI dominance, control, and continuity across critical systems like energy, finance, and telecommunications. #Gemini #Anthropic #OpenAI #Meta #NIST

OpenAI and the Ukrainian government have partnered to give Ukraine access to AI tools and subsidized computing power through the Daybreak program to strengthen defenses for critical infrastructure. The initiative will support faster incident response, threat analysis, vulnerability validation, and other cybersecurity tasks as Ukraine continues to face persistent attacks on its power, water, and transport systems. #OpenAI #UkrainianGovernment #Daybreak #DmytroKushneruk #SamAltman #SashaBaker
Attackers are increasingly targeting infrastructure management systems, with exploited flaws in Cisco Secure Firewall Management Center, Cisco Identity Services Engine, SonicWall SMA 1000, and Check Point products enabling remote code execution and full device control. The report also highlights widespread supply-chain impact from the Linux kernel “CopyFail” flaw and firmware weaknesses affecting Cisco, AMI Aptio-based systems, and Insyde. #Cisco #SonicWall #CheckPoint #Arista #CopyFail #CyclopsBlink #Sandworm #Qilin
Honeywell’s 2026 OT Cybersecurity Benchmark Report says many industrial organizations overestimate the maturity of their OT security programs, with major gaps in asset inventory, monitoring, and SOC integration. The report also shows AI is already widely used in OT security and is expected to play a bigger role soon, even as…
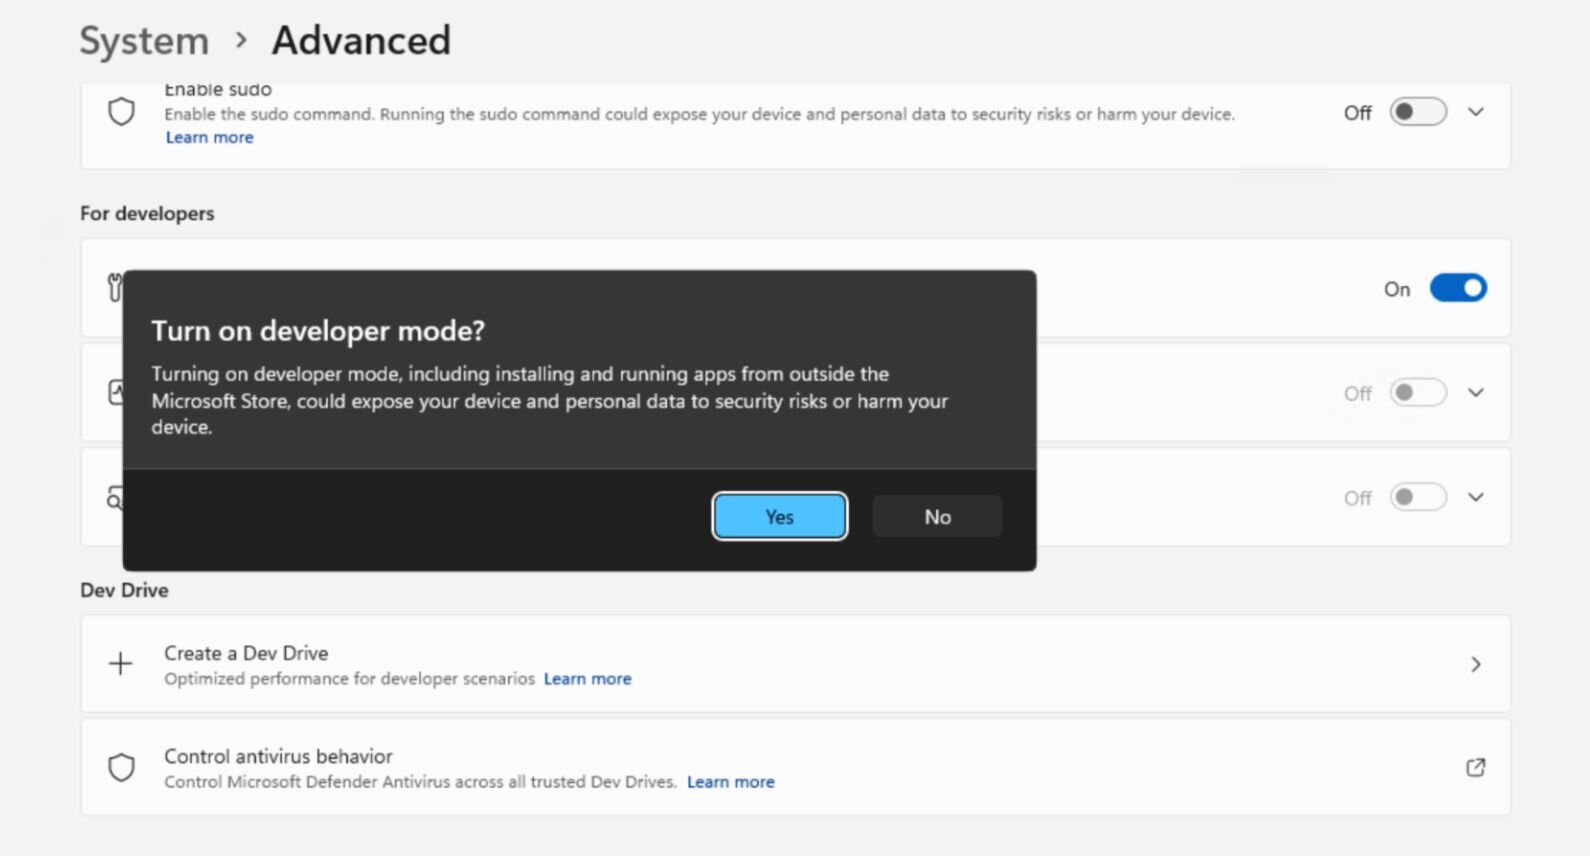
A sideloaded AppX package can abuse WWAHost.exe and WindowsRuntimeAccess=”all” to open a real Microsoft login flow, capture OAuth authorization codes, and steal access plus refresh tokens even when MFA is completed. The article also shows that the abuse is detectable with a proxy rule for MSAppHost/3.0 traffic to non-Microsoft destinations and highlights Developer Mode as the key prerequisite. #WWAHost #WebAuthenticationBroker #MSAppHost #DeveloperMode #EntraID #MicrosoftOffice

Boryeong Cord Blood Bank, South Korea’s first cord blood bank, reported a possible personal data leak after a ransomware infection affected its personal information processing system. The exposed data may include mothers’ and children’s names, ID numbers, phone numbers, and children’s birth details, while the Personal Information Protection Commission has launched an investigation. #BoryeongSaedaehyeolBank #PersonalInformationProtectionCommission
Skroutz Last Mile reported an unauthorized access incident affecting shipment-related data, including names, addresses, and phone numbers. The company said payment card details and passwords were not compromised and warned users to watch for phishing attempts. #SkroutzLastMile
CTOS Digital experienced a cybersecurity incident in which personal consumer data was accessed without authorization, and the company has since contained the affected environment. It has activated emergency response plans, engaged an independent incident response team for forensic investigation, and confirmed that its systems remain operational and the incident is limited to the specific impacted environment. #CTOSDigital
Incransom ransomware targeted Virginia A Lemon PLLC (Lemon Law) in the US, reportedly leaking 16.8 GB of data across 42K files including corporate documents, litigation materials, and client personal and financial data. The exposed information also included employee personal files and internal reporting. #UnitedStates
Varonis Threat Labs uncovered AvisLoader, a Windows loader delivered through a ClickFix lure and designed to communicate over the Tox peer-to-peer network for command-and-control. The recovered tooling included shortcut-persistence artifacts, a UAC bypass helper, and a process-hiding DLL, with exposed management features in the AvisLoader Command Center. #AvisLoader #Tox #ClickFix #UACME…
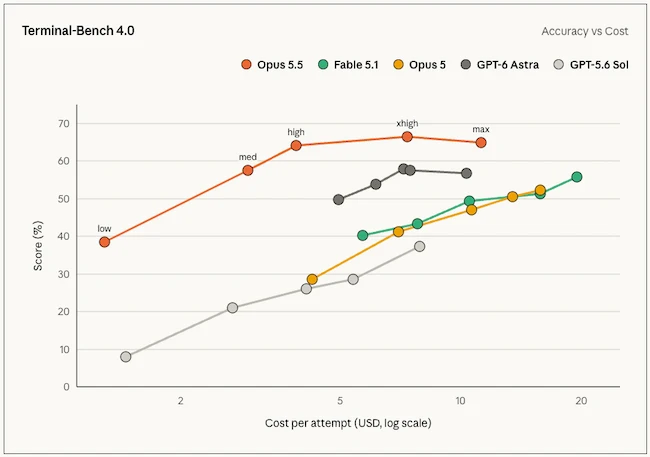
Claude Opus 5.5 is now available across Anthropic, AWS, Google Cloud, and Microsoft Azure, with watermarking and preserved-thinking safeguards designed to support EU AI Act compliance and reduce model-copying risks. The release focuses on long, complex enterprise tasks such as code migrations, audits, and analysis, while also bringing lower API prices, faster output, and stronger defenses against prompt-injection attacks. #ClaudeOpus55 #Anthropic #AWS #GoogleCloud #MicrosoftAzure #EUAIAct