IDC Frontier announced a ransomware attack targeting its IDCF Cloud service, affecting the East Japan Region 1 and impacting 495 companies and local government organizations. The company isolated the network and shut down systems to contain the incident. #IDCFrontier #IDCFCloud #EastJapanRegion1

The ransomware claim alleges that arcusmedia targeted Ladrillera Mecanizada, impacting operations at ladrillera.mx/. The affected country is: #
arcusmedia targeted mblllp (mblllp.ca) with ransomware, aiming to disrupt operations and demand action by the stated deadline. The impacted country is not provided, so #unknown.
AETHOS, a provider of comprehensive software solutions for streamlining operations, reported a ransomware claim allegedly associated with the threat actor arcusmedia. The incident is claimed to have impacted #Unknown
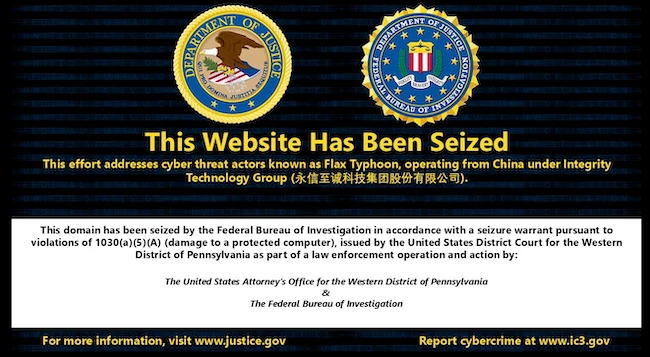
The FBI seized seven domains used by Microscan and FishHub, two hacking tools tied to Chinese state-sponsored hackers known as Flax Typhoon and linked to Integrity Technology Group. The tools were used to scan and compromise organizations worldwide, including U.S. critical infrastructure, Taiwanese universities, and airports in Japan and Poland. #FlaxTyphoon #IntegrityTechnologyGroup #Microscan #FishHub
Anthropic’s OSS Scanner is a free AI-powered service that scans open-source projects for security vulnerabilities and sends maintainers detailed reports with reproduction steps and, when possible, fixes. The service builds on Project Glasswing and aims to speed up disclosure while leaving project teams responsible for validating and prioritizing findings. #Anthropic #OSSScanner #ProjectGlasswing #Claude #OpenSSL
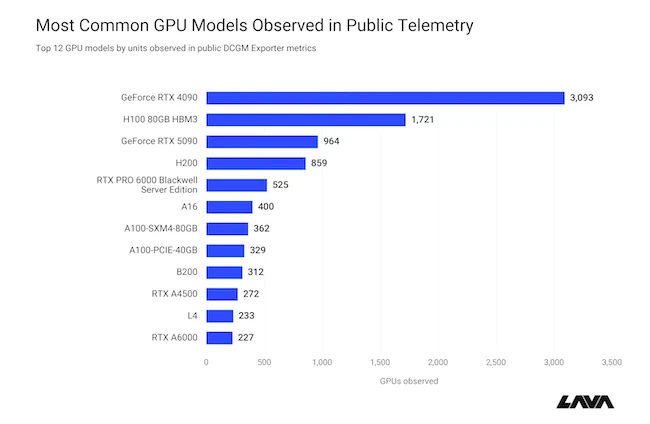
Hundreds of internet-exposed GPU servers were found running vulnerable NVIDIA DCGM Exporter instances affected by CVE-2026-47483, which can be crashed by unauthenticated attackers and may disrupt AI workloads. The exposed monitoring services also leaked detailed GPU, server, and network information across thousands of systems, with impacts seen in environments tied to NVIDIA, Voltage Park, and other providers. #NVIDIA #DCGMExporter #CVE2026-47483 #VoltagePark

Hackers are actively exploiting two unpatched AhsayCBS vulnerabilities, CVE-2026-105133 and CVE-2026-105134, to achieve unauthenticated remote code execution, deploy webshells, and gain persistence on exposed systems. Huntress says at least five organizations have been targeted, with attackers also installing XMRig miners, abusing a vulnerable driver, and disguising malicious components as Microsoft Edge….
Google said several of its domains were affected by a hijack of third-party ccTLDs, including .gh, .sl, and .as, which allowed attackers to alter DNS records and obtain unauthorized HTTPS certificates. The company blocked the certificates in Chrome, worked with CAs to revoke them, and urged domain owners to monitor Certificate…

This week’s roundup covers malware, supply chain abuse, exposed infrastructure, and high-profile criminal cases, including PoeLLM, GhostAction, and a compromised Tensorlake npm SDK. It also highlights notable developments involving CISA, Nvidia DCGM Exporter, South Korean bank attacks, and the sentencing of the Empire Market co-founder. #PoeLLM #GhostAction #Tensorlake #CISA #Nvidia #DCGMExporter…

Nissui Butsuryu, a Nissui Group subsidiary, was hit by a ransomware attack on a server in its cloud data center, causing a system outage and disrupting product inbound and outbound operations. An investigation is underway to determine whether personal data was compromised. #NissuiButsuryu #NissuiGroup
Easthampton Public Schools is dealing with a cyber incident that took its computer network offline, while students have reported limited access to the hotspots provided as a workaround. The district is working with digital forensics experts to investigate the incident and restore normal service. #EasthamptonPublicSchools #epsd.us
St-Pierre-des-Corps suffered a cyberattack on October 8, 2026, causing a complete shutdown of its telephone system and a partial disruption of its IT network. The municipality mobilized cybersecurity experts and opened a technical and administrative investigation, with the CNIL and ANSSI notified to assess any data impact. #StPierreDesCorps #CNIL #ANSSI
Medcom Tech Information (ES) reported a ransomware incident attributed to the nightspire threat actor, affecting its systems and data. The impacted country is #Spain
The ransomware claim alleges that the nightspire threat actor targeted INAPI in Algeria, causing disruption by compromising and encrypting the victim’s systems. The impacted country is #Algeria.