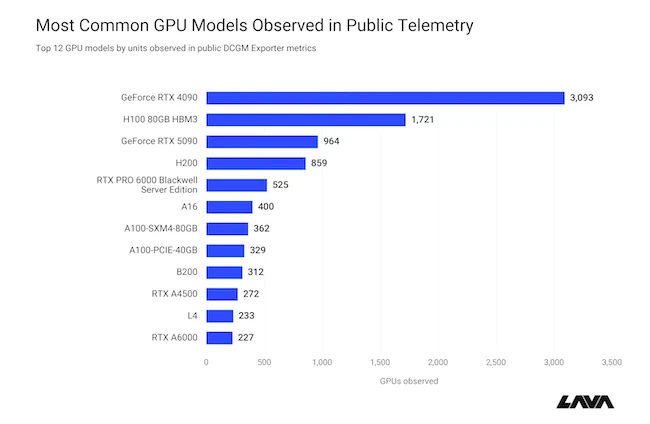
Hundreds of internet-exposed GPU servers were found running vulnerable NVIDIA DCGM Exporter instances affected by CVE-2026-47483, which can be crashed by unauthenticated attackers and may disrupt AI workloads. The exposed monitoring services also leaked detailed GPU, server, and network information across thousands of systems, with impacts seen in environments tied to NVIDIA, Voltage Park, and other providers. #NVIDIA #DCGMExporter #CVE2026-47483 #VoltagePark
Keypoints
- CVE-2026-47483 affects NVIDIA DCGM Exporter and was rated 8.2 CVSS.
- More than 2,000 internet-exposed GPU servers were found running the exporter.
- Unauthenticated requests to /debug/pprof/ can crash the monitoring service.
- Node Exporter exposed hardware, OS, and network details from thousands of hosts.
- Fixes include upgrading DCGM Exporter and keeping monitoring tools off the public internet.
Read More: https://www.helpnetsecurity.com/2026/10/09/nvidia-dcgm-exporter-vulnerability-cve-2026-47483/