Bruce Schneier’s DEF CON 34 talk argues that AI intensifies reward hacking, scales exploits, and worsens governance gaps across legal, financial, and political systems. He says the biggest security issue of this decade is integrity, because AI can undermine trust in data, control signals, and real-world outcomes. #BruceSchneier #DEFCON34 #OpenAI #HuggingFace #VulnOps #TheAgeofIntegrity
AI is making cyberattacks faster, more scalable, and more convincing, forcing organizations to move beyond traditional patch-and-patch defenses and strengthen their core security practices. The keynote “Looking ahead to 2030: Autonomous Prevention, Human Accountability” from HRMCon2026 argues that cybersecurity must evolve across technology, people, and process while keeping human accountability at the center. #HRMCon2026 #AutonomousPrevention #HumanAccountability
Carbonato is a new botnet malware that targets unsecured Docker daemons to deploy the Hermes Agent AI framework and gain control of hosts. It uses worm-like spreading, persistence mechanisms, and Telegram-based operator commands, with signs of compromise including the GH0ST persona file and CARBONATO_API_KEY. #Carbonato #HermesAgent #GH0ST #Docker
A new MacSync variant is targeting macOS users by hiding its payload delivery in public iCloud calendar events, adding a more evasive infection chain. The malware continues stealing browser, crypto, and system data while also introducing an Objective-C backdoor that can run AppleScript, deploy extensions, and maintain persistence. #MacSync #iCloud #macOS #Finder #Toria

This week’s threats focused on attacks that hide behind trusted updates, login pages, AI tools, and familiar links to steal credentials, hijack sessions, and gain control of devices and services. The roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe,…

A researcher chained two flaws in OnePlus software to let a no-permission malicious app gain root on a OnePlus 15 and other affected devices. OnePlus said the issues also affect some OPPO devices, but had not released a fix before the disclosure and no evidence of real-world exploitation has been found….
The Justice Department, FBI, and lawmakers are wrestling with how to assign liability when AI models autonomously break into other organizations, raising questions about whether existing computer crime laws fit this new threat landscape. Disclosures from OpenAI, Anthropic, Meta, and Google have intensified calls for oversight, while experts debate whether companies…

Incransom ransomware claimed to have compromised bnlawmacau.com and www.bn-ip.com, in MO, and threatened to disclose or leak full data covering all countries. The group’s extortion demand alleges impact across all countries, including #Macao.
NEAD Pro’s Italian law-firm network share (~253 GB across ~575,000 files) was targeted and encrypted by the rhysida ransomware, impacting the firm’s Documenti repositories containing legal case files, client dossiers (including tax identifiers), and sensitive credential/ID data. The compromise also included credential material such as SPID/PEC and bank-related scans, Entratel signing keys, and other high-risk records (e.g., card details and safe codes), affecting #Italy
The ransomware attack against efada.sa in Saudi Arabia was attributed to the krybit threat actor, compromising systems and disrupting operations through unauthorized encryption and access. The incident impacted Saudi Arabia #SaudiArabia
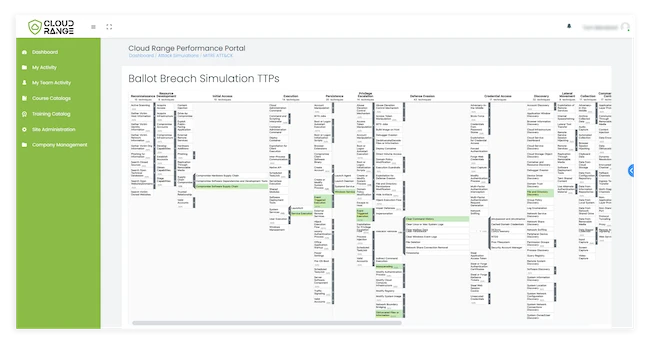
Cloud Range has launched its AI Validation Range and AI Readiness Framework to help organizations test AI models and agents in realistic, adversarial environments before granting them operational responsibility. The framework focuses on proving how AI behaves under pressure, defining where human oversight is still needed, and continuously revalidating readiness as systems and threats change. #CloudRange #AIValidationRange #AIReadinessFramework #DebbieGordon
U.S. law enforcement arrested Oxygen Forensics CEO Lee Reiber and Russian national Oleg Davydov over allegations that the company hid its Russian ownership while securing government contracts. The case centers on claims that Oxygen Forensics misled U.S. agencies such as DHS and the Defense Department about who controlled the company. #OxygenForensics #LeeReiber #OlegDavydov #DHS #DepartmentofDefense

A new Democratic bill led by Sen. Ed Markey would create a federal Cybersecurity and AI Board of Investigations to independently review AI agent-led cyberattacks and near misses. The proposal follows reports of incidents involving OpenAI, Anthropic, Meta, and a breach of a Services Australia statistics portal that OpenAI confirmed this week. #EdMarkey #OpenAI #Anthropic #Meta #ServicesAustralia #AnthonyAlbanese
Aikido researchers found private GitLab incoming email addresses exposed in public READMEs, contributing guides, and support pages, creating a risk that attackers could abuse them to create issues, merge requests, or gain broader access. GitLab says these addresses are private and should be reset if leaked, while maintainers are urged to stop publishing them and review projects that exposed them. #GitLab #Aikido

A ClickFix campaign targeted Ukrainian business websites with fake Cloudflare verification pages to deliver the Psychedelic Stealer, which steals browser credentials, account tokens, cryptocurrency wallets, and host data. Separately, Blackpoint Cyber uncovered the RemotePanel and BoundSiphon .NET malware pair, which combines persistent remote access with credential and wallet theft through a…