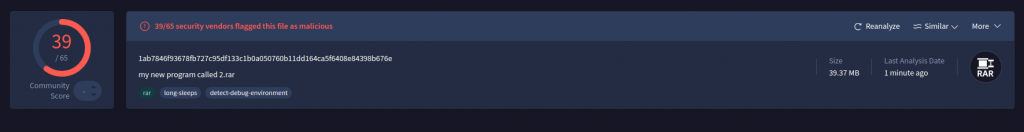
A nested archive named my new program called 2.rar ultimately revealed TokenGrabberBuilder.zip, which contained a Python-based builder and an embedded infostealer payload targeting Windows systems. The malware uses MaaS-style customization, anti-analysis checks, persistence, browser and Discord credential theft, Wi-Fi password harvesting, and webhook-based exfiltration to steal data. #TokenGrabberBuilder #stealer.py #Discord #Roblox

CISA has added two critical vulnerabilities, CVE-2026-5430 in WSO2 products and CVE-2026-71362 in Adobe Commerce and Magento, to its Known Exploited Vulnerabilities catalog after evidence of active exploitation. The flaws can enable remote code execution or unauthorized access to sensitive customer data, and FCEB agencies must patch them by September 27,…

A flaw in Cloudflare Containers allowed one customer to read leftover data from disks previously used by other customers’ containers on the same server. Cloudflare says the issue has been fixed across Containers and Sandboxes, with no evidence that anyone else used the method. #Cloudflare #CloudflareContainers #CloudflareSandboxes #OrenYomtov #Accomplish…
Threat actors are exploiting a high-severity Roundcube flaw, tracked as CVE-2026-48842, which enables unauthenticated SQL injection through the virtuser_query plugin. Successful attacks can expose messages, address books, user identities, and other sensitive database content, prompting Roundcube to release fixes in versions 1.6.16 and 1.7.1. #Roundcube #CVE-2026-48842 #virtuser_query…

The Catholic University of El Salvador (UNICAES) in El Salvador reported a ransomware incident attributed to the Wallstreet threat actor, seeking to disrupt operations through encrypted data and extortion. The attack impacted systems associated with the university’s services and availability, resulting in business interruption in #ElSalvador
Wallstreet ransomware claimed to have targeted Prater & Ridley Attorneys At Law, a Temple, Texas-based law firm established in 1993, providing family law, criminal defense, probate, and estate administration services. The impacted country is #UnitedStates.
TapClicks, a US-based marketing analytics SaaS platform, claims threat actor N0n is ransomwareing its complete platform source code, a multi-tenant production instance management system, and customer marketing datasets including client lists, user accounts with password hashes, and ad-platform connection credentials. Active with a deadline of 2026-09-28 01:59 UTC, the impact is United States #UnitedStates

A forum listing claims that the LQDFX customer dataset is being offered for sale by the actor “0x4ziz” for $800, with the price marked negotiable. If the data is genuine, exposed customer names, email addresses, amounts, and countries could enable phishing, brokerage impersonation, and social engineering. #LQDFX #0x4ziz #pouahaha…
Horizane Santé in France is reportedly targeted in a breach claim by the actor “Jaded,” with 8,864 active customer records and 12 employee records allegedly exposed. If authentic, the data could enable phishing, impersonation, and account abuse, though the available screenshot does not confirm admin access or sensitive health, payment-card, or…

This roundup highlights new cybersecurity products focused on securing AI agents, strengthening exposure management, and improving incident response across enterprise and industrial environments. Vendors including Ping Identity, Akeyless, Orchid Security, Securin, Bitsight, Cohesity, and Nozomi Networks are adding controls to help organizations understand, validate, and govern emerging AI-driven and operational risks. #PingIdentity #Akeyless #OrchidSecurity #Securin #Bitsight #Cohesity #NozomiNetworks
A VikingCloud survey of 200 security and IT leaders found that attacks at multi-location retail and franchise chains often spread beyond the initial site, and that security tools or real-time visibility did not reduce that spread. The strongest factor was governance: companies with a corporate security mandate saw less lateral movement, while many incidents still never reached executive leadership. #VikingCloud #KevinPierce #franchisees
An actor using the handle “Spaniard” is offering an alleged Pet Stop dataset with more than 1 million unique lines for $140 in XMR, with escrow required. The claim is unverified, but if real, the exposed names, email addresses, location fields, and possible passwords could enable phishing, impersonation, and account-takeover attempts….
A sales listing on ARNTREAL claims to offer a dataset tied to the French stats and rewards platform, with 101,015 users, affiliate codes, contact details, and social identifiers included. The post, attributed to “RedStone,” advertises more than 5.5 million total rows across multiple tables, but the data, source, and authenticity remain…
An actor identified as “RandomRussian” claimed to be leaking a dataset tied to Relais Colis, with volume claims ranging from 6.2 million lines to more than 12.9 million records. The unverified sample reportedly contains names, phone numbers, email addresses, and location details that could be used for spam, phishing, and impersonation….
An alleged leak tied to Kaya claims to expose 1.7 million records across 87 collections, including identity data, private messages, financial details, and account information. The report remains unverified, and the data could pose risks of impersonation, fraud, and credential exposure if authentic. #Kaya #DaOnlySpark #Freelancercom #Zarinpal…