Kiteworks warned customers to shut down its platform for a six-hour window over the weekend after receiving credible threat intelligence about a possible attempt to target some customer systems. The advisory is precautionary, with the company saying it is not aware of any compromise and noting its latest release, 9.5.1, addresses…
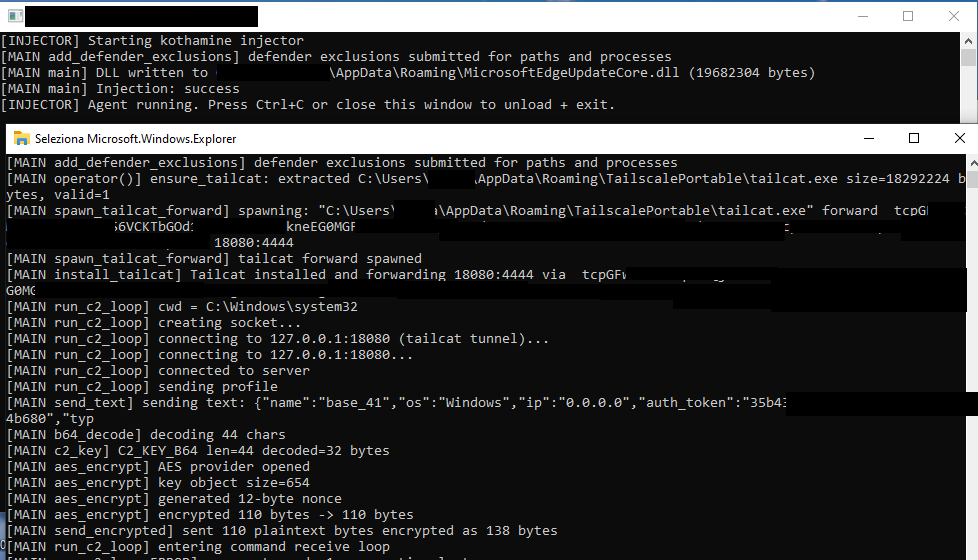
Researchers uncovered Kothamine Agent, an undocumented RAT linked to malicious npm packages that can control Windows systems, steal browser data, and capture audio/video on some builds. Recent variants use tailcat and earlier ones used Tailscale VPN, giving operators encrypted command access while avoiding a conventional C2 domain. #KothamineAgent #tailcat #Tailscale #npm…
ThreatLabz found a phishing campaign using fraudulent Google ads and fast-changing Vercel redirects to impersonate Ledger and steal users’ secret recovery phrases. The campaign sent victims through Google Cloud Storage and Google Sites, then used a fake device-verification flow to collect wallet credentials. #Ledger #GoogleAds #GoogleCloudStorage #Vercel #GoogleSites

metaencryptor ransomware activity targeted GE Vernova Inc., a global energy equipment manufacturing and services company headquartered in Cambridge, Massachusetts, disrupting operations across its Power, Wind, and Electrification segments. The claim indicates systems were compromised and data was likely impacted in the United States. #UnitedStates
S… in an unnamed country was impacted by ransomware attributed to SilentRansomGroup, with the full company name pending disclosure and active full data timer. The incident has affected #countryname
SilentRansomGroup, identified as the threat actor in the N… ransomware claim, targeted the redacted organization (full company name pending disclosure; full data timer active) with an extortion demand following unauthorized access. The incident impacted the affected entities in #countryname

Netskope Threat Labs tracked a cloud-hosted tech-support-scam kit that uses fake loading screens, browser full-screen tricks, and runtime decryption to display bogus Microsoft Defender or Apple alerts and push victims to call a scam support number. The campaign was distributed through paid Google Ads, affected at least 619 organizations, and used anti-analysis tradecraft to hide its hidden C2 and encrypted payloads. #Netskope #GoogleAds #MicrosoftDefender #Apple #ShopEase

The U.S. Supreme Court ruled that states may use the federal SAVE database to verify voter citizenship, reversing lower court decisions that questioned its accuracy and privacy implications. The decision could aid election officials, though critics say the system is outdated and could wrongly remove eligible voters from registration rolls. #SAVE #U.S.SupremeCourt #DepartmentofHomelandSecurity #LeagueofWomenVoters #ElectronicPrivacyInformationCenter
CISA says attackers are actively exploiting critical flaws in WSO2 and Adobe Commerce, along with additional issues in Microsoft SharePoint and Mikrotik RouterOS. Federal agencies must patch the critical KEV entries by September 27, while SharePoint and RouterOS fixes are due by September 28. #WSO2 #AdobeCommerce #MicrosoftSharePoint #MikrotikRouterOS #CVE-2026-5430 #CVE-2026-71362 #CVE-2026-65660 #CVE-2026-67279
A CSRF vulnerability in the Elementor WordPress plugin can let an attacker trick a logged-in administrator into creating a new attacker-controlled admin account through a crafted link. The flaw affects Elementor versions 4.3.0 and 4.3.1, and users are urged to upgrade to 4.3.2 to block the REST API bypass. #Elementor #Patchstack #WordPress

AI is making cyberattacks cheaper to retry by reducing the time, skill, and cost needed to debug failed intrusion attempts, helping attackers move faster through reconnaissance, escalation, and exploitation. The article argues that defenders need a stateful SOC that preserves identity, evidence, hypotheses, constraints, and learning across handoffs so incidents do…

PamStealer has appeared in a new macOS variant that uses a server-side decryption chain, making the payload impossible to recover statically without live C2 cooperation. The campaign lures victims through a fake Wavel cryptocurrency wallet site and ultimately steals passwords, keychain items, browser credentials, and system data from compromised Macs. #PamStealer…

Two GitHub Actions from the actions-cool project were disabled again after becoming accessible and reactivating malicious payloads tied to the May 2026 Mini Shai-Hulud campaign. The incident highlights how mutable version tags can silently reintroduce supply chain risk, and why SHA pinning is critical for protection. #actions-cool #MiniShaiHulud #GitHubActions…
Wallstreet ransomware targeted Tobin & Company, a small CPA firm in Harrison, New York, impacting its accounting, tax, auditing, and nonprofit-focused consulting services. The impacted country(s): #UnitedStates
Morula IVF (ZA) reported a ransomware incident attributed to threat actor everest, impacting its healthcare network and services. The affected operations are tied to fertility and assisted reproductive treatment activities in South Africa. #SouthAfrica