Keio Corporation confirmed a ransomware attack on its servers that disrupted some business and hospitality systems, while train operations were not affected. Tokyo Metro also disclosed a separate cyber incident that exposed 59,000 member email addresses, and it is unclear whether the two events are connected. #KeioCorporation #TokyoMetro

Coosalud.com in Colombia, operated by Coosalud EPS (Coosalud Entidad Promotora de Salud S.A.), reported a ransomware incident attributed to the ThreeAM threat actor. The attack disrupted the organization’s healthcare operations across #Colombia
MinMor Industries reported a ransomware attack by threat actor cry0, with damages indicated by “Coming soon…”. The impacted country(s): #countryname
The ransomware attack targeted M*** P**** M*** in Malaysia, attributed to the netrunner threat actor, resulting in unauthorized access and disruption. Data and system availability were affected by the netrunner ransomware campaign in Malaysia, #Malaysia

Apple has released security updates for older versions of iOS, iPadOS, and macOS to fix CVE-2026-86950, an out-of-bounds write in CoreGraphics that could enable arbitrary code execution. The company said the flaw may have been exploited in highly targeted attacks against specific individuals, and it was discovered and reported by Meta…

A post by UWAYS and the Uways Qarani group claims access to Prince Sultan Military Medical City in Riyadh and says it contains thousands of personnel records, patient files, staff lists, and military identity cards. The screenshots shown include a dashboard sample for Prince Sultan Armed Forces Hospital Madinah, but they…
A post by “Syrv4x” claims to offer a free dataset tied to Les Clés de l’Atelier, a French vocational training organization, with a hidden download revealed only after a reply. The advertised file is said to contain 10,193 lines and may include names, birth details, training records, schedules, location data, and…
A forum post by the actor Syrv4x claims to offer a free 3 MB dataset from Spareka containing 7,770 lines of appointment data. The visible sample lists customer names, phone numbers, emails, appliance and brand fields, and repair issue details, but the post does not prove the data’s authenticity or how…
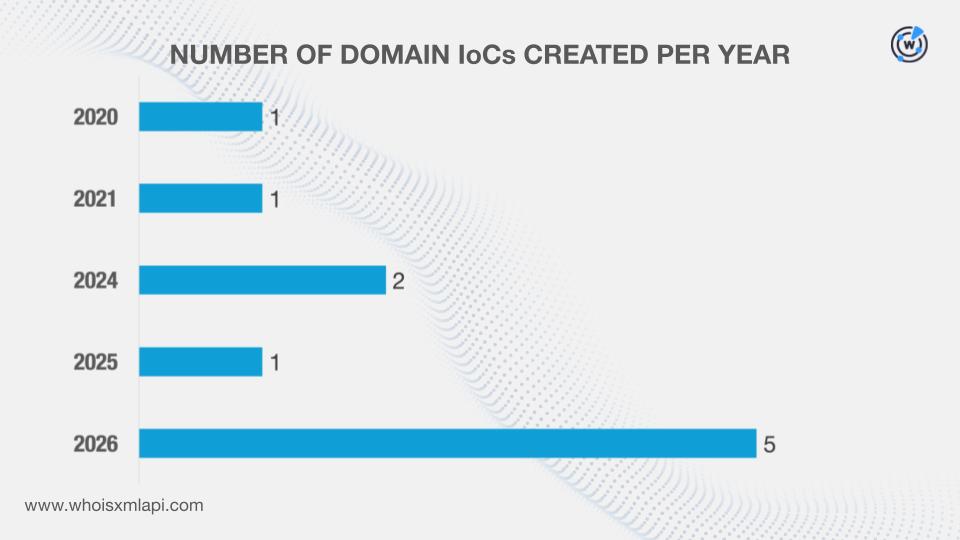
Security researchers analyzed Jewelbug, a China-based hackers-for-hire group running espionage and crypto fraud campaigns from a single control panel across the Middle East and Asia. The investigation found over 1 million implant check-ins and 580,000 stolen browser cookies in less than three months, along with numerous domains, subdomains, and IPs tied to the operation. #Jewelbug #SocGholish #Cloudflare #Azure #CloudFront

NVIDIA has launched the Open Agent Safety Platform to improve the security of AI agents through stronger sandboxes, monitoring, and hardware-backed policy enforcement. The platform has support from more than 100 organizations, including Anthropic, Microsoft, and JPMorgan Chase, as the industry pushes to make agentic AI safer in real-world environments. #NVIDIA #OpenAgentSafetyPlatform #Anthropic #Microsoft #JPMorganChase #Bluefield4 #OpenShell
Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with sensitive data such as PII, passwords, authentication tokens, and in some cases credit card information. UpGuard linked the exposure to weak configuration practices in AI-assisted app development and advised users to review Supabase security controls to reduce risk. #Supabase #UpGuard #AIcodingagents
Dutch police confirmed the arrest of a 24-year-old Amsterdam man in an investigation tied to the ShinyHunters hacking group, with authorities expected to provide more details at his court appearance in Rotterdam. The suspect, identified by reporters as Pepijn van der Stap, has previously been convicted of hacking and blackmail, while ShinyHunters denied any connection to him. #ShinyHunters #PepijnvanderStap #PolitieLandelijkeOpsporingenInterventies
Times Car has confirmed that a cyberattack exposed data belonging to about 6.6 million current and former members, including personal, driver’s license, and account information. The company says credit card data was not affected, no stolen data has been found online, and it is warning customers to watch for suspicious messages and fraud attempts. #TimesCar #Park24 #TimesMobility
Threat actor threeam claimed ransomware against safescaffolding.net, a GB-based commercial and residential construction scaffolding contractor providing scaffolding infrastructure, materials, and equipment setup for building and renovation projects. The impacted country is: #UnitedKingdom
Bakemyday.se, a Swedish (SE) business, reportedly became a ransomware victim of the incransom threat actor, threatening access to its systems and data. The attack targeted the company providing handcrafted, fresh bakery experiences with 10 employees and an estimated $5M revenue, resulting in disruption in Sweden #Sweden