Storm ransomware reportedly targeted West County Health Centers, a US healthcare provider serving western Sonoma County from its headquarters in Guerneville, California. The incident impacted the organization’s operations in the United States. #UnitedStates

Threat actor ULose is accused of deploying ransomware against www.newyjh.com in Korea (KR), resulting in system disruption and encrypted files for the victim. The threat appears to be in a “Sale” status, with the impacted country(s) being #Korea.
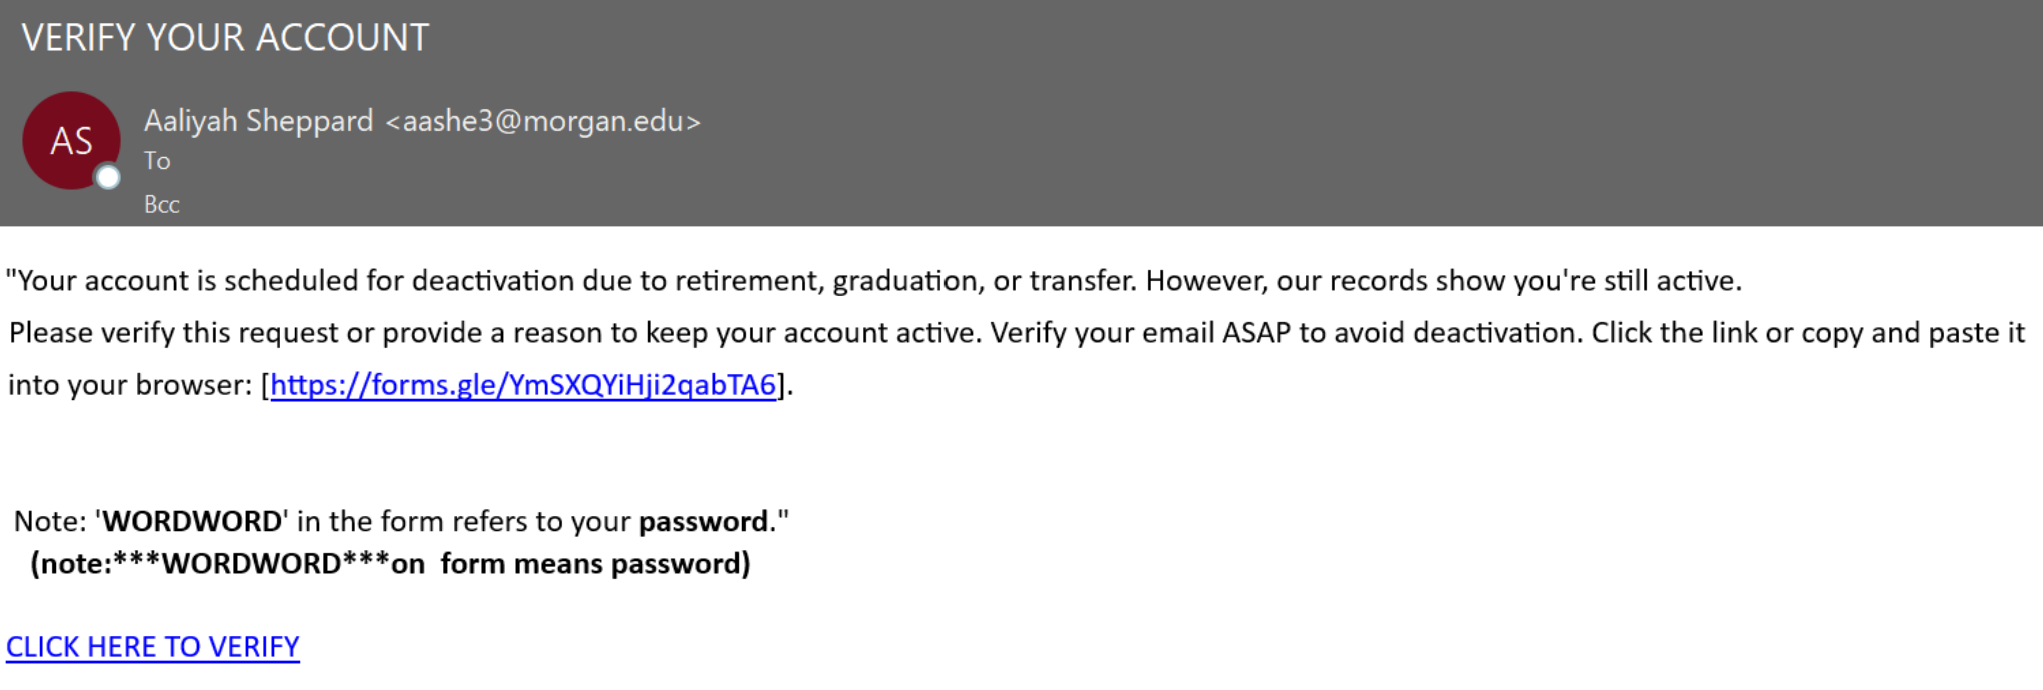
Proofpoint tracked a campaign targeting U.S. universities where attackers used compromised .edu accounts and fake password-verification forms to harvest credentials and PII. The same access was then used to push job-scam advance fee fraud involving fake checks, gift cards, and payment requests, with activity linked to Nigeria and tracking via Grabify….
More than 100 security and compliance vendors now integrate with the Claude Compliance API, allowing organizations to feed Claude activity into existing monitoring, DLP, SIEM, identity, eDiscovery, and AI security posture management tools. The API can expose detailed Enterprise logs, including conversations, file uploads, projects, Code and Cowork sessions, admin actions, and sign-in activity, while some vendors only ingest audit logs or no conversation content. #Claude #ClaudeComplianceAPI #CrowdStrike #MicrosoftPurview #Splunk #PaloAltoNetworks #Cloudflare #Zscaler #Netskope #Okta #KnowBe4 #Vanta #Hadrius #Shield #SaltSecurity #TorchSecurity #Datadog

Genea has launched Genea MCP, a native Model Context Protocol server that lets AI agents manage access control tasks directly in the Genea Access Control platform with fewer clicks and faster workflows. The system is disabled by default, uses existing user permissions, and requires confirmation before high-impact actions to keep control in the hands of administrators. #Genea #GeneaMCP #ModelContextProtocol
Two men, Chijioke Timothy Odimegwu and Harafat Mogaji, were sentenced to a combined 189 months in federal prison for running BEC and phishing campaigns against US businesses while serving in the Air Force. Their scheme stole credentials and financial data, diverted large wire transfers, and involved victims in Iowa, Ohio, and a nonprofit in Pella, Iowa. #ChijiokeTimothyOdimegwu #HarafatMogaji #FBI #IowaCity #Pella #ATandT #Snowflake

Cybersecurity researchers disclosed technical details of CVE-2026-88772, a critical Citrix NetScaler ADC and Gateway flaw that is being actively exploited in the wild. The bug is a DTLS-related memory overflow in the NetScaler Packet Processing Engine and can lead to remote code execution or denial-of-service. #CVE-2026-88772 #CitrixNetScaler #NetScalerADC #NetScalerGateway #NSPPE…
President Donald Trump and leaders from major AI companies signed a voluntary accord at the White House that calls for internal controls, external audits, and board-level oversight of AI systems. The agreement comes as the administration promotes AI growth through new tools like America.gov, while critics warn that self-policing may not…
OpenSSL and WolfSSL have released patches for a combined 25 vulnerabilities, including multiple high-severity flaws that could enable memory disclosure, denial of service, and authentication bypass. The most serious issues affect DTLS, TLS, and certificate validation paths, putting VPNs, VoIP, IoT products, and software using Nginx, HAProxy, Stunnel, and Apache httpd…
Malicious custom ChatGPT variants promoted in sponsored Google results are luring users to fake backup sites that trigger ClickFix attacks and install malware through PowerShell commands. Huntress says the campaign used OpenAI-hosted GPTs like “Plus 5.6” and delivered a RAT with persistence via Windows Run keys and scheduled tasks. #OpenAI #ChatGPT #Plus5.6 #Huntress
Edcon (South Africa) was hit by ransomware claimed by thegentlemen, impacting edcon.co.za, the Johannesburg-based retailer with major regional brands. The situation disrupted a business already under restructuring, leaving creditors dealing with ongoing proceedings in South Africa. #SouthAfrica
Samwumed, based in South Africa (KR), was targeted by thegentlemen with a ransomware claim against its operations tied to samwumed.org and zoominfo.com/c/samwumed/346685548. #SouthAfrica
LegalWise (legalwise.co.za) in South Africa, covered by the threat actor thegentlemen, reported a ransomware claim associated with its legal-expenses insurance services for members across multiple provinces and neighboring countries. #SouthAfrica

Mandiant and GTIG identified active exploitation of CVE-2026-88772 against Citrix NetScaler ADC and NetScaler Gateway, with intrusions using custom tooling to gain root access, persist, and move into internal networks. The campaign deployed WHIPSHOT and SLAPSHOT to hide C2 in HTTP headers, proxy traffic for reconnaissance and credential theft, and abuse modified web server settings, while Citrix also warned that CVE-2026-88771 is being actively exploited. #CVE-2026-88772 #CVE-2026-88771 #CitrixNetScaler #WHIPSHOT #SLAPSHOT
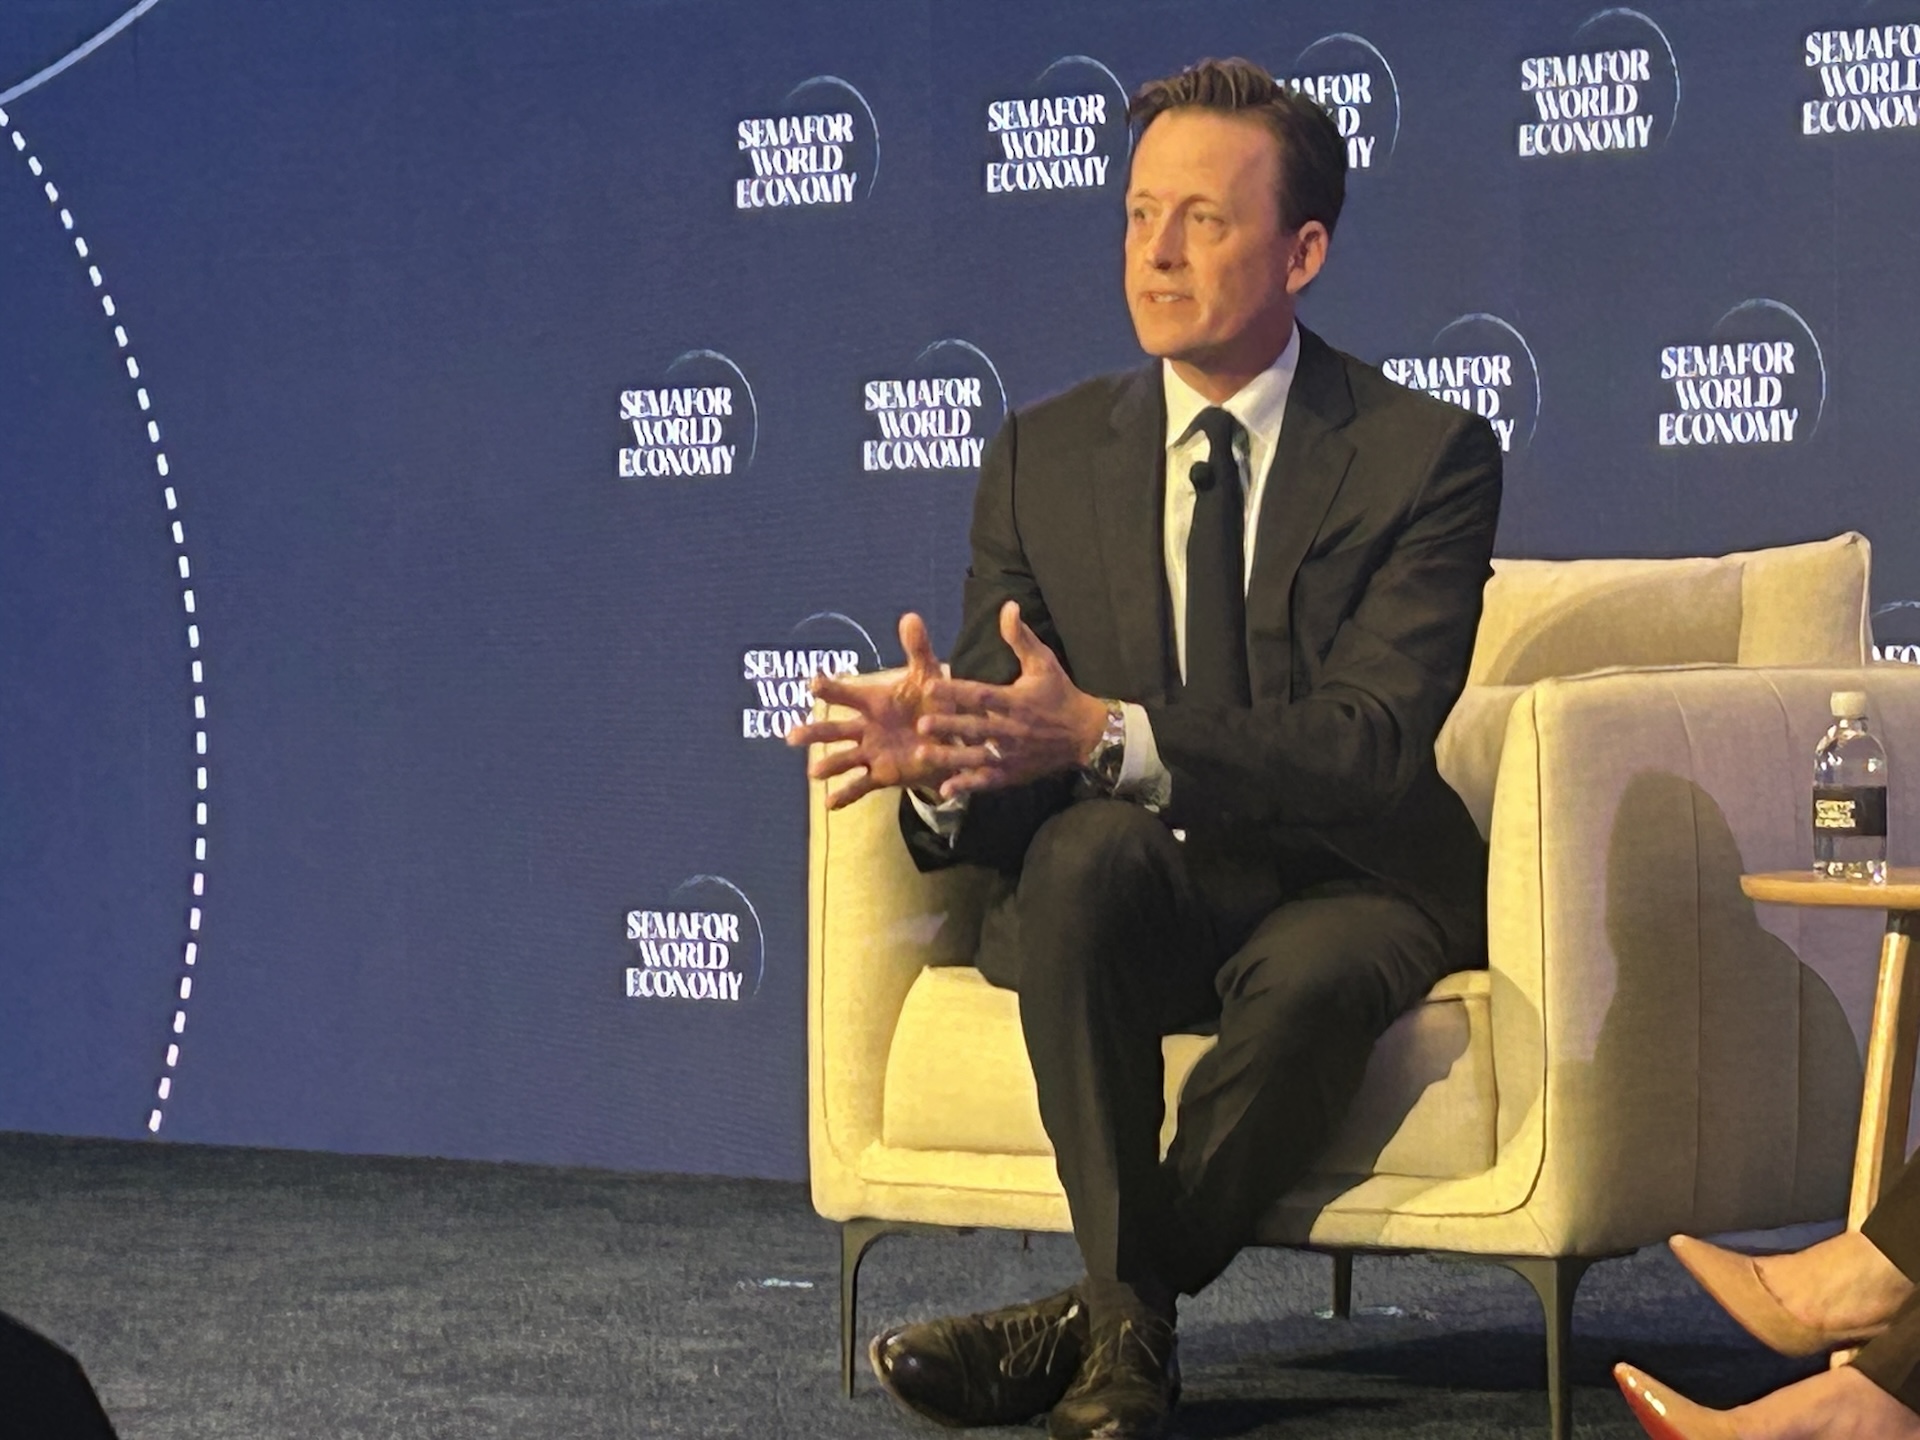
The U.S. government is partnering with critical infrastructure operators to deploy AI across essential systems and improve cyber defenses, according to National Cyber Director Sean Cairncross. He also stressed the need for visibility into AI agents and supply chain access, while noting ongoing debates over regulation, innovation, and replacing outdated systems. #SeanCairncross #USTelecom #Mythos #WhiteHouse #DonaldTrump #JDVance #MikeJohnson