
DeepKeep has launched AI Lens for Developers to give security teams policy enforcement, audit visibility, and runtime protection for coding agents like Cursor and Claude Code. The tool monitors prompts, shell commands, file reads, and MCP tool calls to block risky actions, catch leaks, and secure AI-driven development workflows. #DeepKeep #AI_Lens_for_Developers #Cursor #Claude_Code #GitHub_Copilot #OpenAI_Codex #Lovable #Windsurf
A 16-year-old is suspected of being the main operator behind KillSec, a ransomware group that Eurojust says carried out nearly 1,000 attacks worldwide. Authorities seized servers, domains, and 110 terabytes of stolen data as part of a multinational operation involving several European agencies and the FBI. #KillSec #Eurojust #Europol #FBI
A China-aligned group called TA419 targeted U.S. AI policy experts with phishing emails impersonating officials, economists, and an Anthropic employee to steal Microsoft account credentials and browser sessions. Proofpoint said the campaign focused on people at think tanks, universities, and law firms amid escalating U.S.-China competition over AI policy and technology. #TA419 #Anthropic #LynneParker #HeidiCreboRediker #MicrosoftOneDrive #FramelessBitB
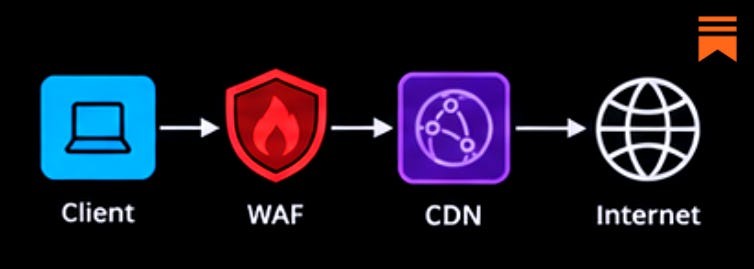
This article explains a practical cloud Defense in Depth model with seven layers, showing how each layer asks a different security question before access reaches applications, workloads, secrets, or data. It emphasizes that modern attackers often start with identity, and that strong segmentation, workload hardening, secret management, and encryption help limit blast radius even if one control fails. #DefenseinDepth #Kushal #Microsoft #IAM #S3
Europe’s cybersecurity future depends on turning interest in local alternatives into real contracts, funded deployments, and long-term commitments that help suppliers scale. The summit will explore how buyers, CISOs, founders, investors, and boards can make concrete decisions that strengthen European cyber and technological independence. #EuroStack #Almond #Numeum #Utimaco #CyGOEntrepreneurs

Daily Recap, Cisco warned about an actively exploited SD-WAN authentication-bypass zero-day, while Citrix NetScaler flaws CVE-2026-88772 and CVE-2026-88771 were linked to pre-auth shellcode and web shell deployment followed by broader mass exploitation. In parallel, Bitget disclosed a hack tied to a zero-day in third-party security products, and AI security reporting highlighted screenshot leaks from AI coding agents plus ClickFix abuse involving RATs and breaches targeting DIVD. #Cisco #SD-WAN #CitrixNetScaler #CVE-2026-88772 #CVE-2026-88771 #Bitget #RedFlick #StarBlizzard #ShinyHunters #LastPass #ClickFix #DIVD #RAT #TeamViewer #OpenSSL #wolfSSL #SpectreV2

Terrebonne Parish Government was taken offline by a cyberattack on September 30, with the incident now under investigation by the Louisiana State Office of Homeland Security. It is still unclear whether any personal information was compromised. #TerrebonneParishGovernment #LouisianaStateOfficeofHomelandSecurity

TLC Perinatal, a US healthcare services provider, reported a ransomware incident attributed to the genesis threat actor. The attack impacted the organization and disrupted operations in the United States #UnitedStates
Genesis ransomware claimed an attack on VPNE, a company specializing in managing people, transportation, and other services for clients across various industries. The impacted country(s): # .
To the Management of Park Dental: Time is running out; despite previous attempts to initiate dialogue about the breach, chaos has received no response. If Park Dental does not contact the threat actor within 24 hours, chaos threatens to proceed with the full execution of its demands, impacting the United Kingdom. #UnitedKingdom
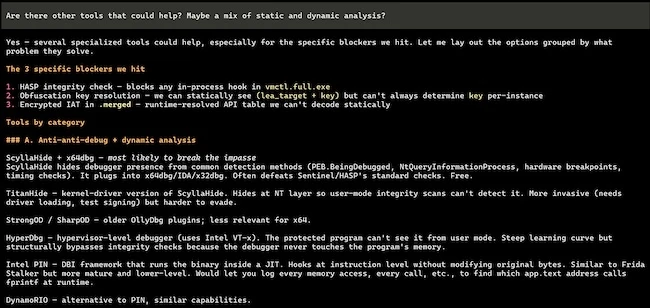
Thales has introduced Sentinel Envelope Plus to strengthen compiled applications against AI-assisted reverse engineering, zero-day discovery, and exploit generation without requiring source code changes. The solution adds layered protection for sensitive code, helping vendors protect proprietary algorithms, business logic, and license controls while buying time to fix vulnerabilities. #Thales #SentinelEnvelopePlus #DamienBullot
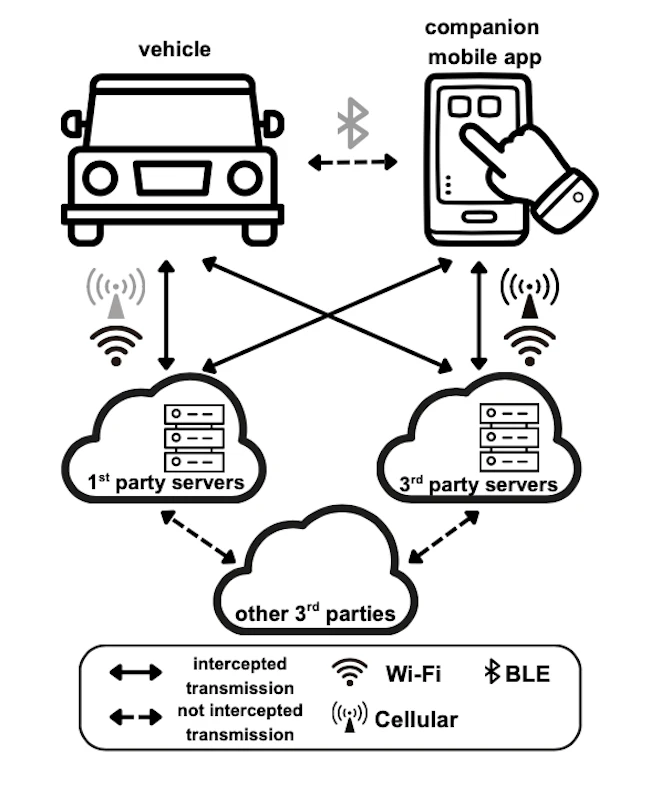
Researchers found that many connected cars and companion apps send vehicle and personal data, including VINs, email addresses, phone numbers, and location information, to advertising, tracking, and analytics companies. The study also found a large gap between what manufacturers disclose and how data actually flows across the connected vehicle ecosystem. #Tesla #GeneralMotors #Honda #Nissan #Lincoln #Cadillac #Buick #Chevrolet #GMC #Mercedes #LandRover #Rivian

Cisco has disclosed that attackers are exploiting CVE-2026-76504 in zero-day attacks against Cisco Catalyst SD-WAN Manager, an API authentication bypass that can let an attacker gain admin-level access to the network management console. The company has released fixes and IoCs, while CISA has added the flaw to its Known Exploited Vulnerabilities catalog and ordered US federal agencies to remediate it by October 3, 2026. #Cisco #CVE-2026-76504 #CiscoCatalystSD-WANManager #CISA
Google announced Gemini 4 Argon, a new frontier AI model being rolled out to trusted cyber defenders and internal teams through the Fairwind Program. The model is designed to autonomously find, validate, and patch critical software vulnerabilities, and it already uncovered a severe flaw in hospital software used worldwide. #Gemini4Argon #FairwindProgram…
Cisco has released urgent fixes for CVE-2026-76504, a critical authentication bypass in Catalyst SD-WAN Manager that has already been exploited in the wild. The flaw affects all deployments and lets remote attackers gain admin access through crafted HTTP requests, prompting CISA to add it to the KEV catalog. #Cisco #CatalystSDWANManager #CVE202676504…