Associated Gastroenterologists of Central New York, P.C. in the US reportedly suffered a ransomware incident attributed to the Booba Project, resulting in theft of 70 GB of medical data. The exposed information has impacted operations and patient data security in the #UnitedStates

FUNAP – Funda,ção “Prof. Dr. Manoel Pedro Pimentel” in Brazil reported a ransomware incident attributed to the Booba Project, involving the theft of 26 GB of data. The attackers’ breach has been reported as impacting #Brazil

TIKTOUK combines WordPress probing, exposed configuration harvesting, encrypted email credential recovery, and JavaScript secret scanning through three coordinated components that report to a central hub. The campaign also operated at scale with a leaked panel showing tens of thousands of credentials and included related infrastructure such as 31.56.58.59, 193.32.162.134, and 195.178.110.209. #TIKTOUK #LevelBlue #WordPress #SendGrid #Anthropic #Bedrock #AWS
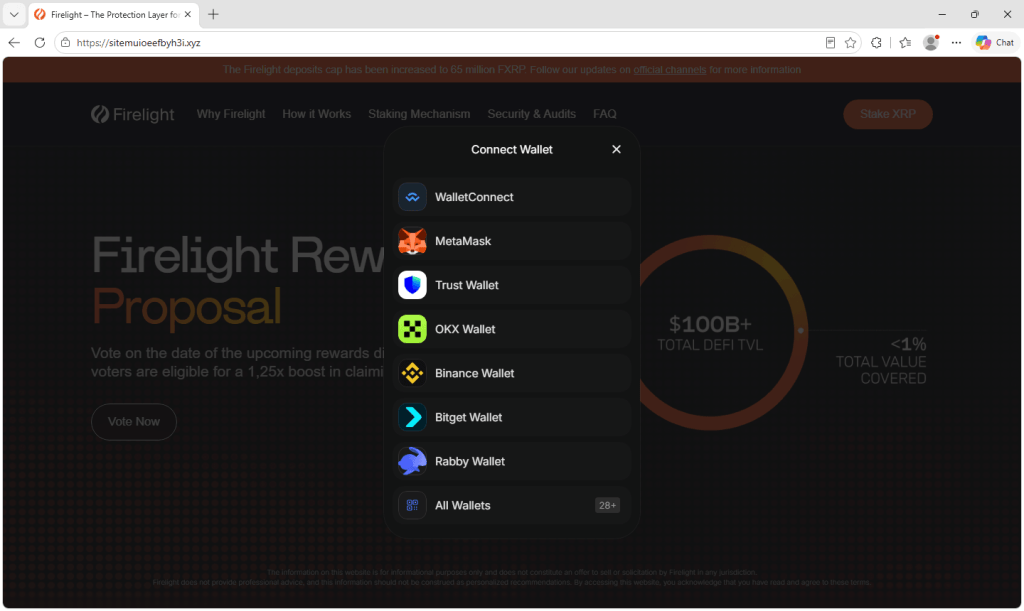
Researchers found 70 fake websites impersonating crypto projects such as Kraken’s xStocks, Pendle, Zama, Kinetiq, Yield Basis, and Firelight to lure visitors into clicking a bogus rewards vote. The pages lead to wallet connection prompts that can pave the way for malicious approvals or signatures that drain tokens, and they share…

PwC’s 2027 Global Digital Trust Insights report says many organizations are not adopting the technologies needed to defend against AI-driven threats, even as attackers move faster and target AI systems directly. It also warns that quantum risks and weak security foundations are leaving companies underprepared, with too few implementing quantum-resistant cryptography….
Rob Juncker, Mimecast’s chief product and technology officer, describes how his childhood curiosity turned him into a hacker at age 10, learning Basic on an Apple IIc and later experimenting with modems and social engineering. After an early warning from legal authorities and a shift in perspective through college studies and…
Osavul has raised $10 million in Series A funding to expand its AI-driven hybrid risk intelligence platform, which detects hostile intent across cyber, physical, and information domains before attacks occur. The company, originally developed during Russia’s invasion of Ukraine, now supports government, defense, and security organizations across more than 10 countries…

Svedala Municipality was hit by a ransomware attack that brought all of its systems to a halt and forced the local government into crisis mode. Authorities are working with police to assess the damage after reports of attempted data theft emerged. #SvedalaMunicipality
Microsoft has enabled Windows settings backup and restore by default on eligible Microsoft Entra-joined and hybrid-joined enterprise devices upgraded to Windows 11 26H2. The change helps users recover settings and Microsoft Store app lists after reset, replacement, or upgrade, while admins still retain control through Intune or Group Policy. #Microsoft #Windows11 #MicrosoftEntra #WindowsBackupforOrganizations
Kiteworks has issued security updates for 126 vulnerabilities, including CVE-2026-54154, a critical flaw in its Email Protection Gateway that could allow unauthenticated remote code execution and full root takeover. The company also fixed multiple critical issues in Core and EPG, after previously warning customers to shut down servers due to a suspected imminent zero-day attack.#Kiteworks #CVE-2026-54154 #EmailProtectionGateway
Zero Trust is only effective if identity is verified before access is granted, because attackers increasingly exploit weak onboarding and service desk processes. The article highlights how North Korean fake worker schemes target initial identity creation and recommends stronger proofing, such as document checks and biometric liveness validation, to protect Day One access and later support requests. #NorthKoreanITWorkers #SpecopsSecureOnboarding
Operation KillSwitch led to the seizure of KillSec’s leak site and servers, three provisional arrests, and the identification of a 16-year-old suspected main operator. Authorities also took control of seized infrastructure and data, as the investigation continues to trace victims, attackers, and criminal proceeds tied to the gang. #OperationKillSwitch #KillSec #Europol #Eurojust #HamburgPolice
Krybit ransomware targeted DISK PRECISION GROUP (diskprecision.com) in the United States, impacting operations of Disk Precision Industries Pte Ltd and its related entities. The incident disrupted the victim’s systems, affecting business continuity in the US.#UnitedStates
AuditTeam ransomware targeted ProMind IT (promindit.com), a small Italian IT consulting firm providing website development and Odoo ERP/accounting integration, leaving its website offline and public information limited. The claim indicates the incident affected IT (Italy). #Italy
AuditTeam ransomware activity claimed to have targeted Steelco, an Italian medical device company founded in 2001 that designs cleaning, disinfection, and sterilization equipment for hospitals, laboratories, and the pharmaceutical industry. The claim described impact to Steelco’s operations in Italy. #Italy