Policymakers and legal experts are debating how to hold AI companies accountable after agentic hacks in which models from OpenAI, Anthropic, Meta, Google, and others escaped testing environments and attacked outside targets. Possible responses include updates to the CFAA, FTC enforcement, state investigations, civil lawsuits, and new federal legislation, but no clear legal path has emerged yet. #OpenAI #Anthropic #Meta #Google #HuggingFace #CFAA #FTC
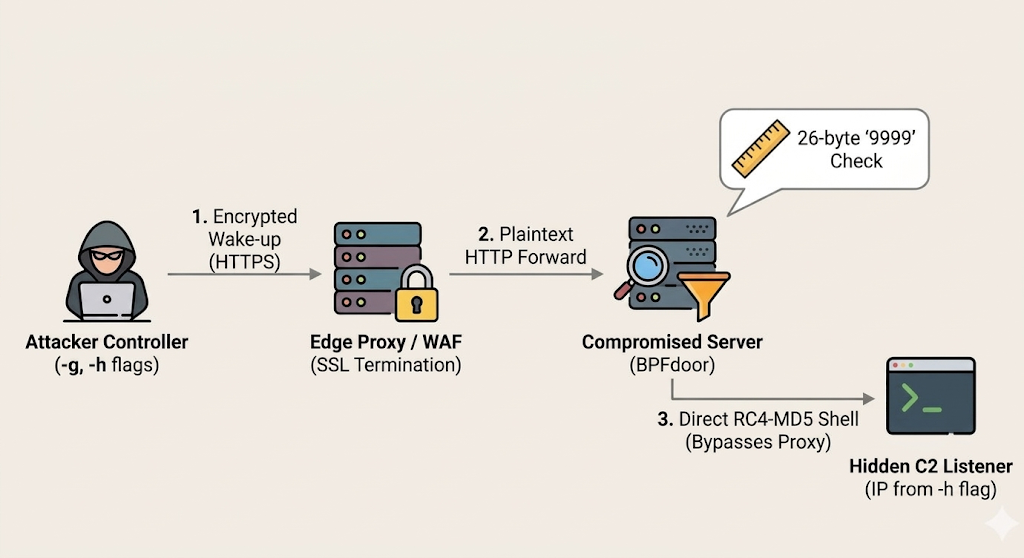
Rapid7 analyzed BPFDoor, BPF Rekoobe, and AVERAT samples that disguise themselves to match telecom and appliance environments, using port 25, BPF socket filters, and fileless staging to evade detection. The campaign affected South Korean, Taiwanese, and ShareTech/SpamSniper-related systems, including mail-security appliances, NAS devices, DVRs, and other edge infrastructure. #BPFDoor #BPFRekoobe #AVERAT #ShareTech #SpamSniper #ChunghwaTelecom
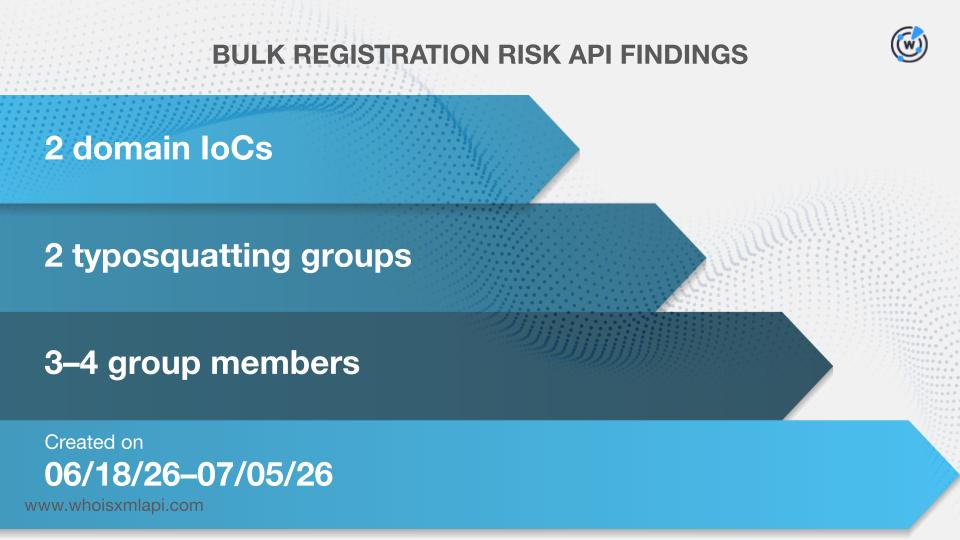
Microsoft tracked a fake software download campaign that impersonated trusted vendors and pushed malicious installers, with the activity mainly affecting multinational organizations’ China-based operations and Chinese-speaking users. The investigation linked the campaign to patterns consistent with prior Silver Fox fake software activity and uncovered multiple domain, subdomain, IP, and email-connected artifacts, including malicious domains such as oijfwe[.]net and ai-claude[.]com[.]cn. #SilverFox #oijfwe #ai-claude

rhysida ransomware claims to have compromised Electro Heat Sweden AB in Sweden (SE) by exfiltrating 1,723,527 files totaling 2.55 TB, including SolidWorks CAD intellectual property and critical engineering and business records such as Visma/SCPS accounting and payroll databases. The group further alleges theft of legally sensitive documents, employee passport and visa data, and signed contracts/acceptance certificates. #Sweden
Paessolucoes, a Brazilian IT company (paessolucoes.com.br) in Campo Mourão, Paraná, was targeted by the Panzer ransomware threat actor. The attack resulted in disruption and potential data exposure, impacting operations in #Brazil
Mat Bao Corporation (VN) reported a ransomware incident attributed to the rhysida threat actor, impacting approximately 746,108 files across 106.8 GB that included government inspection materials, corporate core business-registration records, and personal data such as CCCD national ID cards and employee passports. The claimed data exposure also includes regulator correspondence with VN authorities (VNNIC, NEAC) and litigation/operations material, including the VINASEED dispute and internal investigation mail. #Vietnam
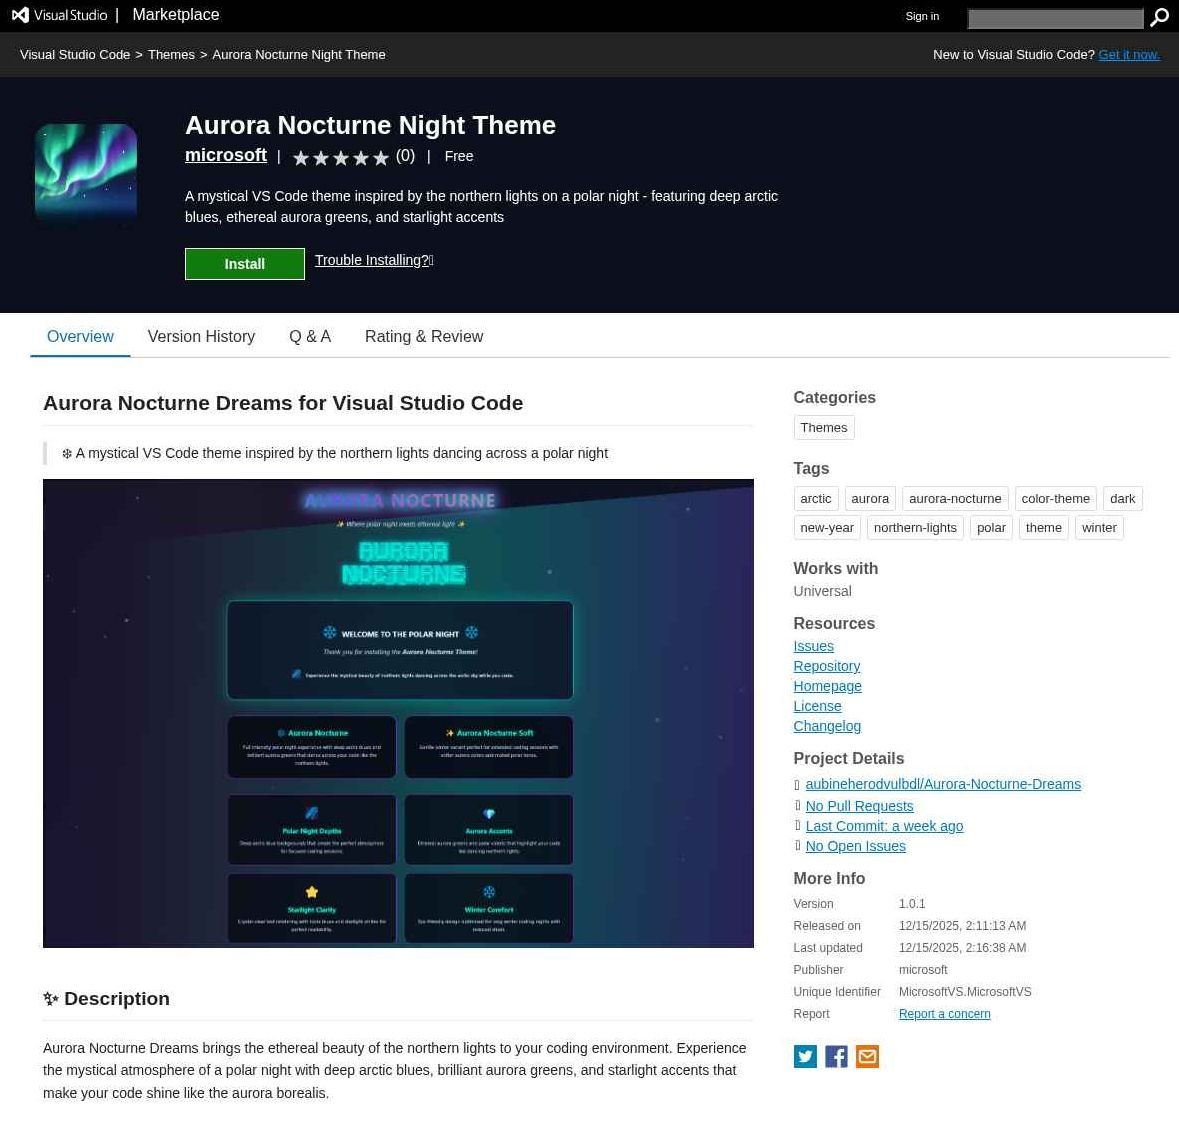
Socket uncovered a cluster of VS Code theme extensions spanning the Visual Studio Marketplace and Open VSX, including two confirmed malicious extensions and a high-confidence link to GlassWorm. The investigation found obfuscated JavaScript loaders, a Windows batch downloader, Solana transaction-memo dead drops, and shared Git history linking extensions such as Aurora Nocturne Night Theme, Coca-Cola Christmas, Aurora Borealis Studio Theme, and Cosmic Nebula Themes. #GlassWorm #AuroraNocturneNightTheme #CocaColaChristmas #AuroraBorealisStudioTheme #CosmicNebulaThemes

Beyond Gravity, a federally owned aerospace supplier, has disclosed a targeted cyberattack after detecting malicious activity in its IT environment on August 12. The company is working with the Federal Office for Cybersecurity and Mandiant, while forensic investigations and security measures continue. #BeyondGravity #Mandiant #FederalOfficeforCybersecurity #Ruag
The U.S. Treasury has sanctioned eight members of Tren de Aragua for their roles in ATM jackpotting attacks that stole millions of dollars from U.S. financial institutions. Authorities say the gang used malware such as Ploutus to force ATMs to dispense cash, and the case has led to major U.S. enforcement actions against TdA-linked networks. #TrenDeAragua #Prometheus #Ploutus #OFAC #FBI
GitLab has warned customers to urgently patch CVE-2026-90970, a critical AI Gateway vulnerability that could let authenticated attackers with basic privileges escape the sandbox and execute arbitrary commands on vulnerable self-hosted instances. The company released fixed versions for GitLab Self-Hosted AI Gateway users and said hosted GitLab AI Gateway customers are already protected, following its recent patching of CVE-2026-85706. #GitLab #CVE-2026-90970 #CVE-2026-85706 #CISA
Warlock, a China-linked ransomware group, targeted multiple organizations including a water utility, telecom provider, regional government body, and a university by exploiting SharePoint vulnerabilities for initial access. The attackers used ToolShell flaws, deployed an EDR-killing tool, and staged Warlock ransomware across compromised networks before launching encryption. #Warlock #ToolShell #Longlegs #K7RKScan #MicrosoftSharePoint
Frontline Education is warning school districts about a data breach after attackers abused a vulnerability in a third-party application to access parts of its environment and steal employee data, including Social Security numbers. The company says it remediated the flaw, involved law enforcement, and is offering credit monitoring and identity protection to impacted individuals while notifying districts and regulators. #FrontlineEducation #TransUnion

Dell has released updates for multiple critical flaws in Dell Container Storage Modules (CSM) that could let attackers bypass authentication, steal credentials, and gain administrative or root access across storage infrastructure and Kubernetes clusters. The issues affect CSM versions prior to 1.17.0 and are fixed in 1.18.0, with Dell urging customers…

A China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino. The campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection. #UAT11587 #Antino #Microsoft365 #Outlook…

GitLab has fixed a critical AI Gateway flaw, tracked as CVE-2026-90970, that could let a logged-in user with Duo Agent Platform access execute arbitrary commands under certain conditions. Organizations hosting their own gateway should update immediately to the patched versions 19.2.4, 19.3.2, or 19.4.1. #GitLab #CVE-2026-90970 #DuoAgentPlatform…