
Public exploit details published on July 27 describe CVE-2026-61511, an unauthenticated remote code execution flaw in vBulletin’s template engine that can reach PHP’s eval() and execute commands on unpatched forum servers. Although vBulletin had already patched affected self-hosted branches and released vBulletin 6.2.2 weeks earlier, defenders are still urged to monitor…
A Cl0p ransomware affiliate is exploiting CVE-2026-12569, a critical RCE flaw in PTC Windchill and FlexPLM, using chained vulnerabilities to gain access and deploy JSP webshells. The campaign targets aerospace, automotive, manufacturing, and retail/apparel organizations for data theft and extortion. #Cl0p #PTC #Windchill #FlexPLM #CVE-2026-12569…
GitHub and PyPI have rolled out new measures to reduce supply chain attacks by slowing the spread of poisoned package releases and blocking tampering with older stable versions. GitHub’s Dependabot now waits three days before opening pull requests for new non-security releases, while PyPI restricts new file uploads to releases older…

BH Security, LLC (brinkshome.com) in the US was targeted by shinyhunters, with over 4.9 million Salesforce records containing some PII compromised. This is a final warning that the threat actor may leak the data unless BH Security contacts them by 30 July 2026, with the threat escalating as of 27 July 2026. #UnitedStates
Shadow AI agents are being created across tools like Salesforce Agentforce, Microsoft Copilot Studio, Cursor, Zapier, and Retool without IT or security visibility. Nudge Security helps discover these agents, assess their risks, and govern them without slowing down employees. #SalesforceAgentforce #MicrosoftCopilotStudio #Cursor #Zapier #Retool #NudgeSecurity
Coca-Cola confirmed that the ransomware attack on its Fairlife subsidiary led to a data breach after the Anubis group claimed to have stolen 1 TB of data and encrypted systems. The company says most production has resumed at its U.S. Fairlife facilities, with retail availability and product safety largely unaffected. #CocaCola…
Nvidia and a broad coalition of companies launched the Open Secure AI Alliance to build and share open source tools, models, and techniques for securing AI systems and agents. The alliance highlights projects such as NOOA, SPIFFE/SPIRE, Lightwell, MDASH, and Grok Build, while urging policymakers to avoid restricting open frontier AI…
MedusaHVNC is a malware-as-a-service RAT that uses a hidden Windows desktop to run a browser and interact with the system without the user seeing it. BlackFog found that it relies on a multi-stage infection chain, encrypted payloads, persistence in the Startup folder, and a hardcoded C2 address to stay stealthy and…

This article explains that Claude is not a single security surface but six distinct ones, including Enterprise access, Projects, MCP servers, Claude Code, Managed Agents, and the Platform Console. It argues that real risk comes from toxic combinations of identity, permissions, and stale access across those surfaces, and that Reco’s discovery and posture tools provide the visibility needed to govern them. #Claude #Anthropic #Reco
AnMed’s hospital system is dealing with a cybersecurity disruption that has caused its phones and internet to go down. State and federal authorities, along with third-party cybersecurity specialists, are assisting as AnMed works to restore services and keep urgent care and lab operations open. #AnMed
CRPxO ransomware targeted the IPTV Platform in the technology/video streaming sector and exfiltrated 3.2 GB of data. The incident impacted United States #UnitedStates
Katathani Phuket Beach Resort in Thailand (TH) reported a ransomware incident attributed to threat actor dragonforce, impacting operations at the luxury beachfront resort on Kata Noi Beach. The attack disrupted services supporting guest experiences and resort amenities, including lodging and on-site facilities, in Thailand. #Thailand
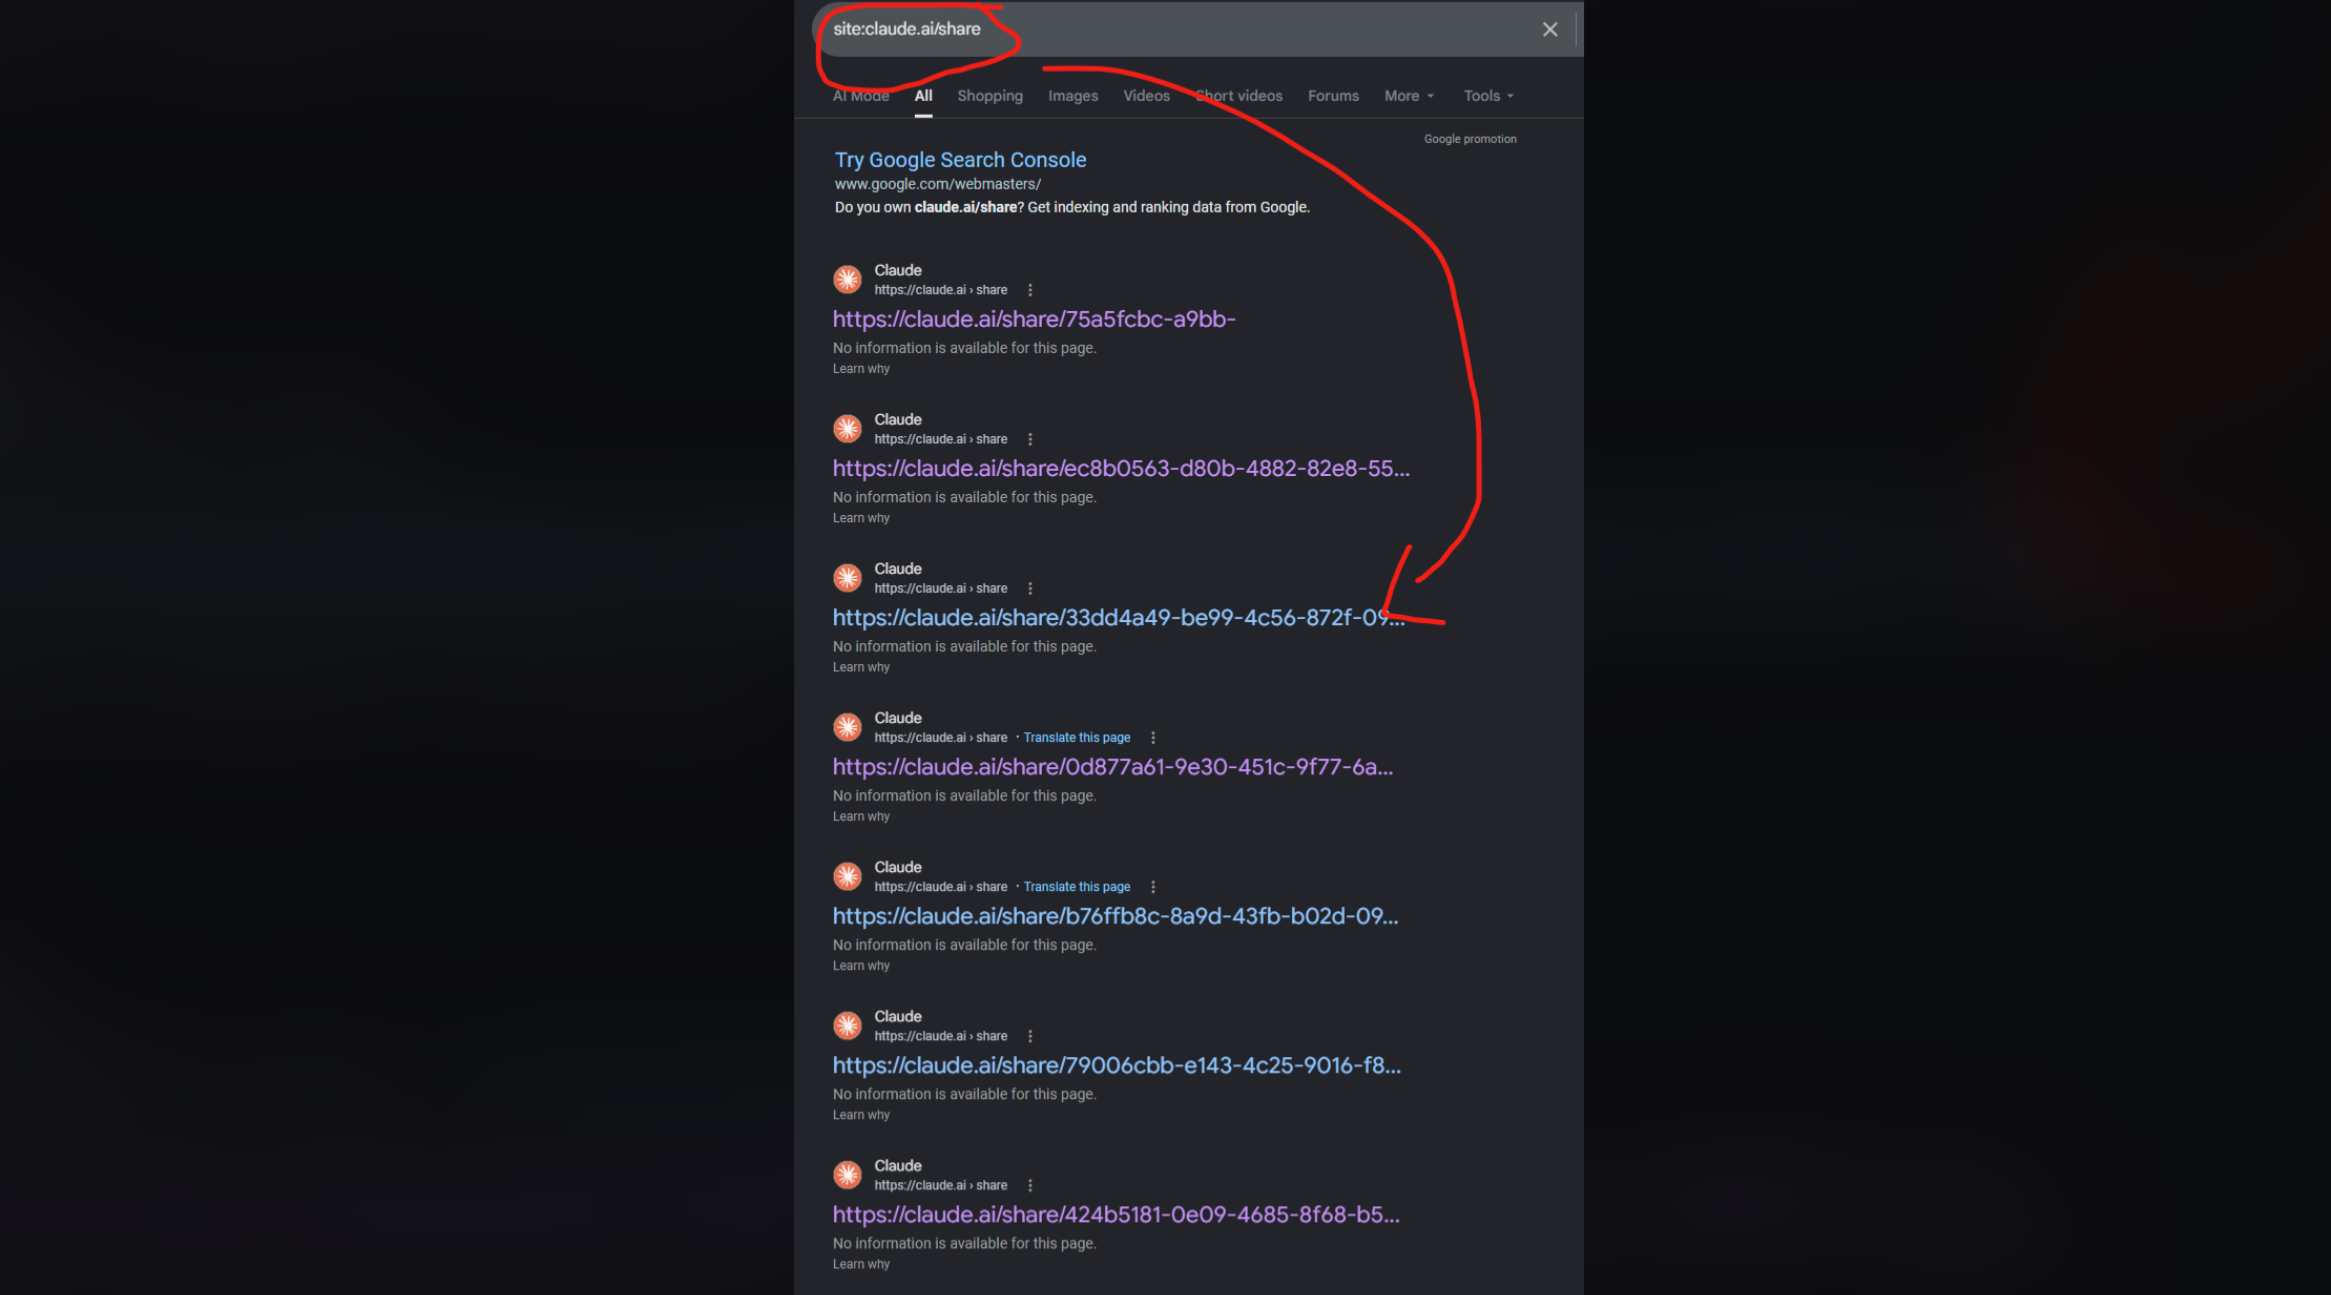
Claude AI conversation share links were indexed by Google and other search engines, exposing some user-shared chats that contained sensitive information such as wallet private keys and personal data. The issue stemmed from a crawler-indexing misconfiguration, and Anthropic has since requested removal of the exposed links. #ClaudeAI #Anthropic #Google #Bing #Yandex…
MCBS, an Atlanta-based medical business management company, disclosed a breach that affects more than 1.2 million people after hackers accessed its systems in September 2025 and may have stolen sensitive personal and medical data. The PEAR ransomware group claimed responsibility, saying it exfiltrated over 3 TB of files and also boasted…
ExfilSquad ransomware allegedly targeted Wesco International in the US, exfiltrating 2.6M~ records containing customer and employee PII, account and contact data, CRM user profiles, credit and business identifiers, authentication metadata, and access information. The threatened actor’s claim impacts #UnitedStates