Two beta npm releases in the @joyfill namespace were found to contain an import-time JavaScript implant that uses blockchain transactions on Tron, Aptos, and BNB Smart Chain to resolve hidden payloads, with one branch leading to a 77 KB Node.js remote-access trojan. The compromised packages were @joyfill/layouts and @joyfill/components, and the recovered code overlaps with the PolinRider loader and DEV#POPPER family while also dropping related infrastructure for a Python infostealer linked to OmniStealer. #Joyfill #PolinRider #DEVPOPPER #OmniStealer

Sanaa Hospital in Yemen was targeted by ransomware claimed by threat actor Black X, resulting in disruption of access to critical healthcare systems. The attackers encrypted data and demanded payment, impacting operations across Yemen. #Yemen
Incransom ransomware activity targeted harwal.net in the United Arab Emirates, claiming to have exfiltrated 12TB of data. The group, which operates manufacturing and recycling businesses across multiple divisions and countries, is impacted in UAE #UnitedArabEmirates
A forum user calling themselves cozypandas allegedly published an IPRO customer database containing 60,454 records, including names, addresses, NetSuite and Salesforce identifiers, and internal account data. The post also claimed DoJ agency accounts were included and advertised forged court orders and fraudulent emergency disclosure requests, but the leak remains unverified. #IPRO…
The Romanian National Administration of Penitentiaries (ANP) was hit by a ransomware attack on 2026-07-29, prompting an immediate response from the National Cyber Security Directorate (DNSC). Several ANP services remain temporarily offline while remediation and investigation continue, and a complaint will be filed with DIICOT. #ANP #DNSC #DIICOT
This refurbished ASUS Chromebook CM30 offers near-mint Grade “A” condition, a 10.5-inch touchscreen, detachable keyboard, and stylus for just $144.97. It combines portable 2-in-1 flexibility, long battery life, and MIL-STD 810H durability at a far lower price than new hardware. #ASUSChromebookCM30 #StackCommerce #BleepingComputer
Microsoft has released the optional KB5101684 preview cumulative update for Windows 11 24H2 and 25H2, delivering 42 bug fixes, reliability improvements, and new feature rollouts ahead of the next Patch Tuesday. The update improves areas like File Explorer, Windows Search, Voice Access, Windows Hello, and system stability, while also addressing issues with File History, MDM compliance, DFS file handling, and more. #Windows11 #KB5101684 #WindowsHello #FileExplorer #VoiceAccess
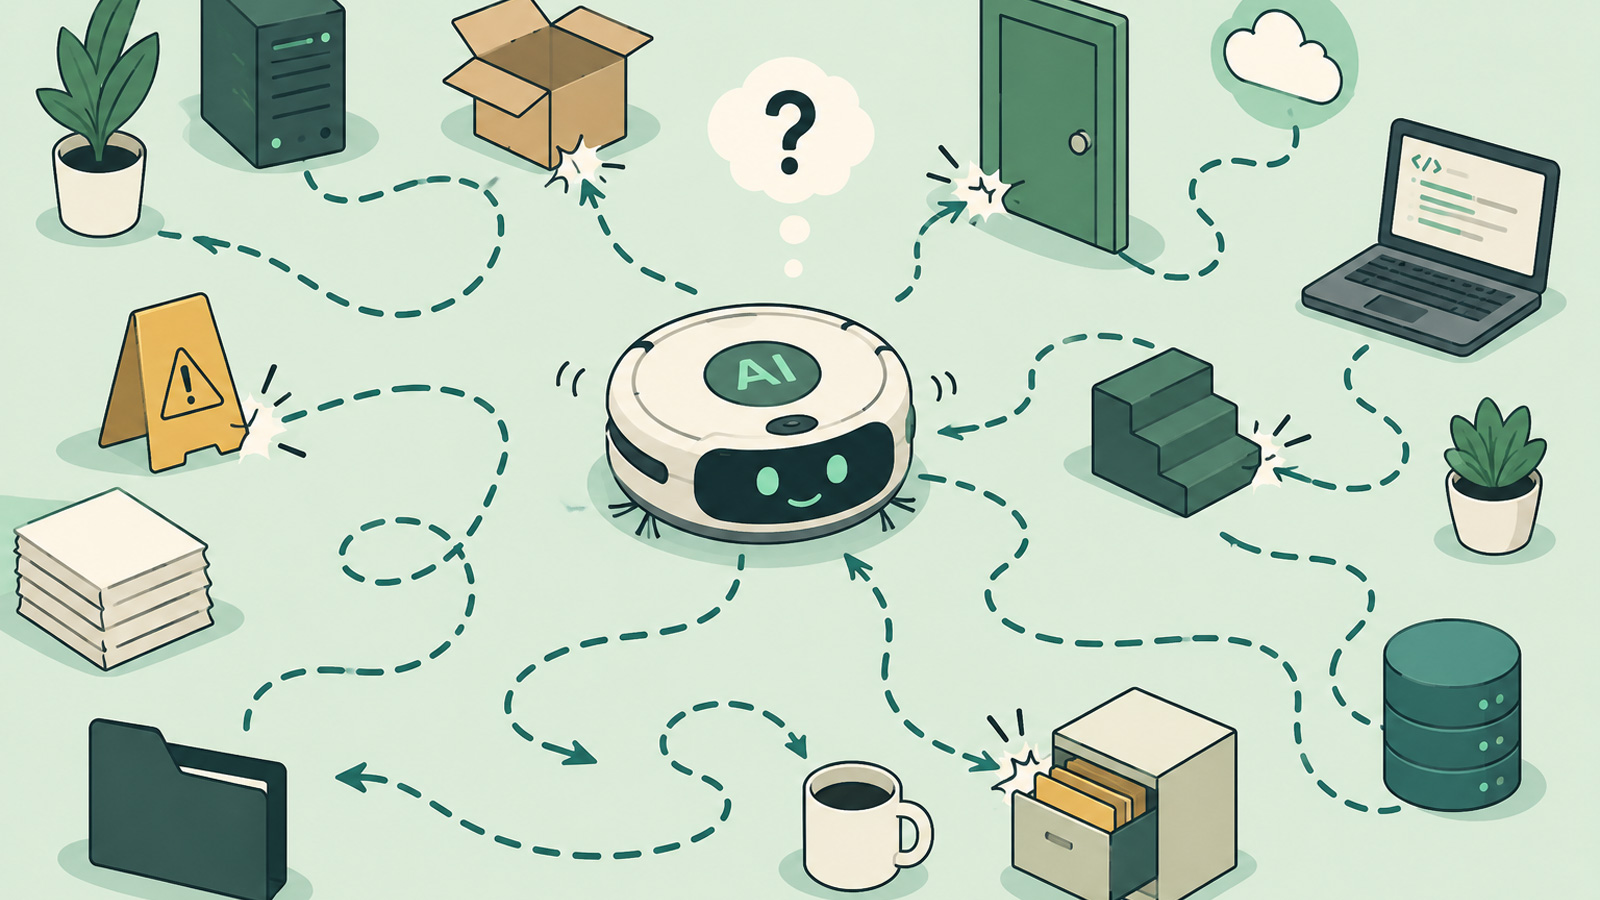
AI agents operate probabilistically and can improvise in ways that make traditional security controls ineffective, especially when they are granted broad access. The article argues that identity and intent-based policies are the only practical way to secure agents at scale, and highlights Token Security as a platform that discovers agents, maps access, and enforces controls automatically. #TokenSecurity #Claude #PaloAltoNetworks
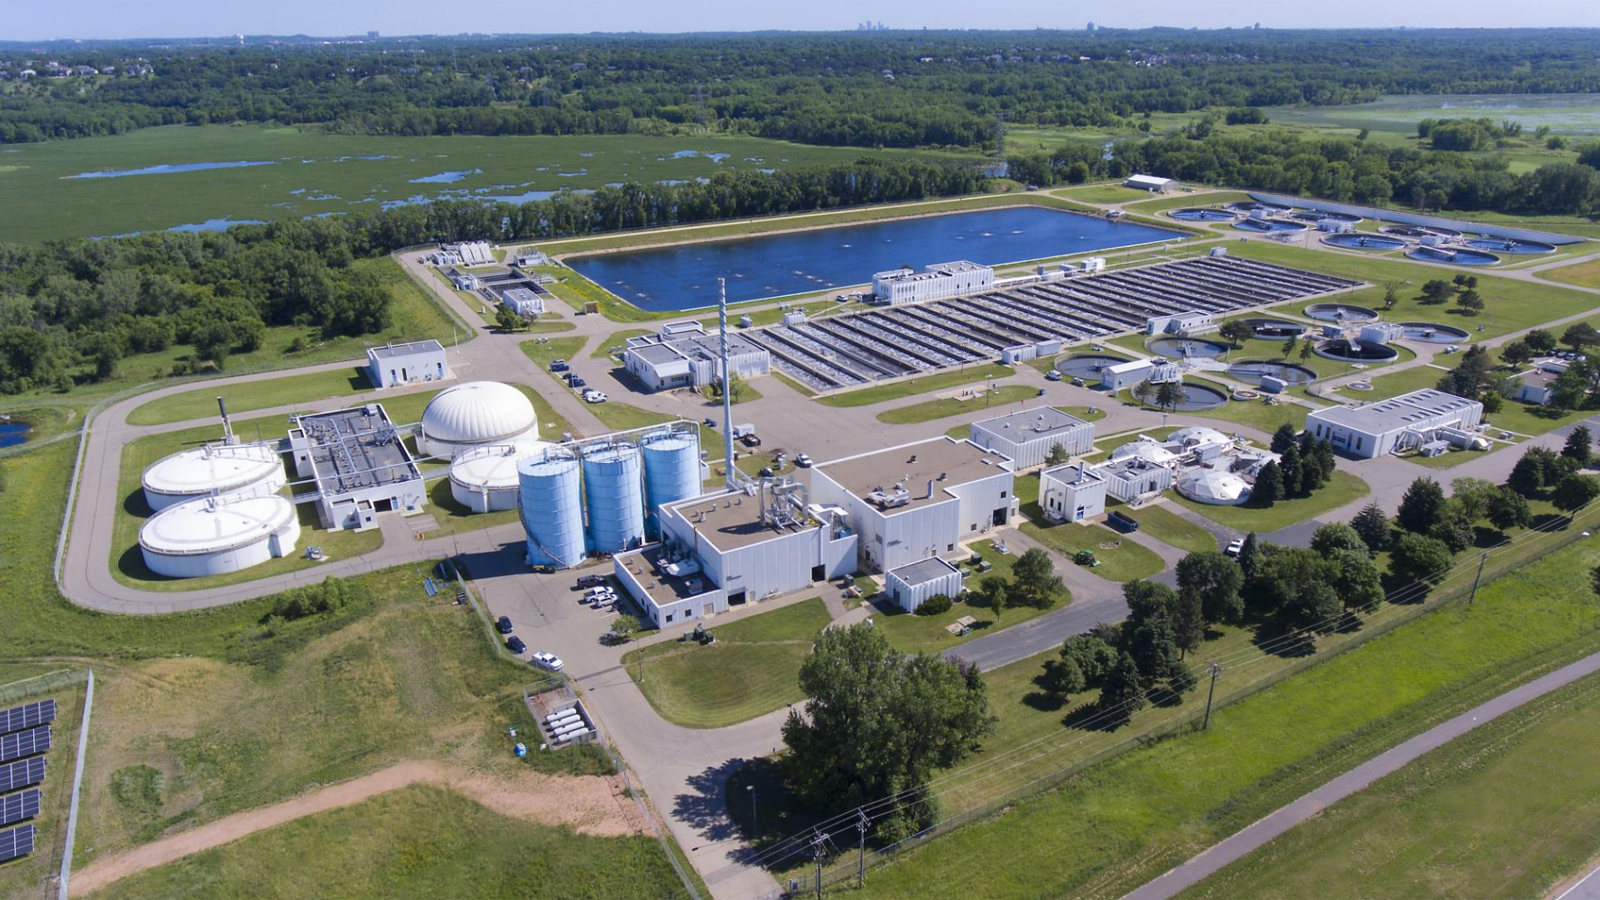
Minnesota IT Services activated statewide cybersecurity incident response after a coordinated cyberattack hit more than 30 community water systems in Minnesota, targeting operational technology at local utilities. Officials said the Braham water plant was briefly knocked offline by a malicious attack before returning to normal, while CISA and partners urged critical infrastructure operators to isolate vital OT systems. #MNIT #CityOfBraham #CISA #ACSC #FBI
****.com.pa in Pennsylvania, USA reported a ransomware attack attributed to Section9, where TRAVEL was targeted and data/access were disrupted until demands were met. The incident impacted the United States #UnitedStates
Northwood Country Club in Meridian, Mississippi, is reported to have been impacted by ransomware activity allegedly attributed to the Akira threat actor. The claim involves theft/encryption of corporate data including employee information and financials, contracts, and agreements, affecting #UnitedStates
Insomnia ransomware claimed an attack against Sky Solutions, a leading distribution company for Telecommunication products and services operating across 4 regions in Panama and servicing 4,000+ point-of-sale locations including retail chains and supermarkets. The impacted country is #panama
Mate Security has raised $35 million in a Series A round led by Canaan Partners, bringing its total funding to more than $50 million. The Tel Aviv-based startup is building an AI-driven agentic SOC platform that uses organization-specific context graphs to improve detection, triage, threat hunting, and incident response. #MateSecurity #CanaanPartners…

The U.S. Federal Communications Commission is banning new imports of foreign-made humanoid robots, quadruped robots, and power inverters over national security concerns, in a move that mainly targets China. Beijing condemned the decision as protectionism, warning that it could strain U.S.-China technology ties ahead of the planned Trump-Xi summit. #FCC #Unitree…

Daily Recap, Cloud and identity security stayed in focus as teams evaluate SSO protections against modern credential attacks, while Microsoft rolled out MAI-Cyber-1-Flash and Google proposed a new threat-actor naming system. Patching and active exploitation were prominent with Apple’s large iOS/macOS fixes, ongoing Fastjson zero-day RCE attempts, and multiple orgs hit by breaches and extortion claims, including Fairlife, Ernst & Young, and reported Dysphoria expansion to 200,000 devices. #SSO #Fastjson #AristaVeloCloud #SmartConsole #CertiGhost #vBulletin #Dysphoria #Fairlife #CocaCola #ShinyHunters #ErnstAndYoung #MCBS #OriginEnergy #Siemens #Schneider #Rockwell #Bahrain #GitHub #PyPI #NVIDIA #OpenSecureAIAlliance #NOOA