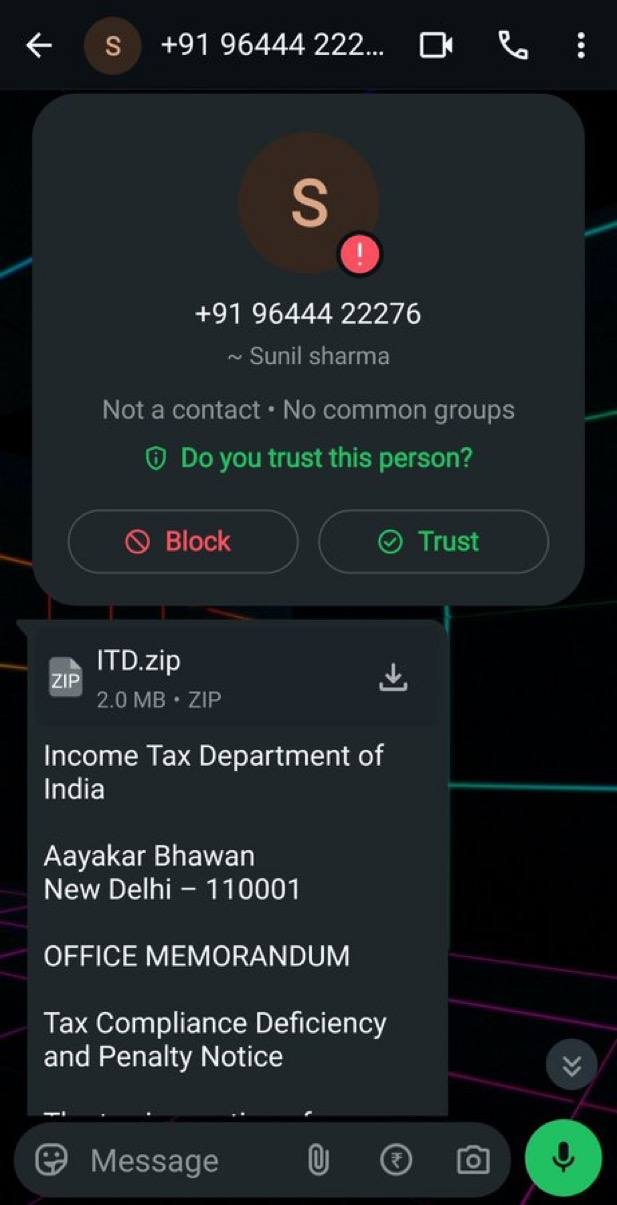
Attackers are spreading fake Income Tax Department penalty notices and refund lures through WhatsApp, SMS, email, and lookalike websites to trick taxpayers into opening malicious files or entering credentials. The campaigns deliver malware such as ITD_Tax_Notice.exe and use disposable domains, fake Office Memorandums, and cloud-hosted second-stage payloads to steal data and enable remote access. #IncomeTaxDepartment #ITD_Tax_Notice.exe #ipwho.is #AlibabaCloud
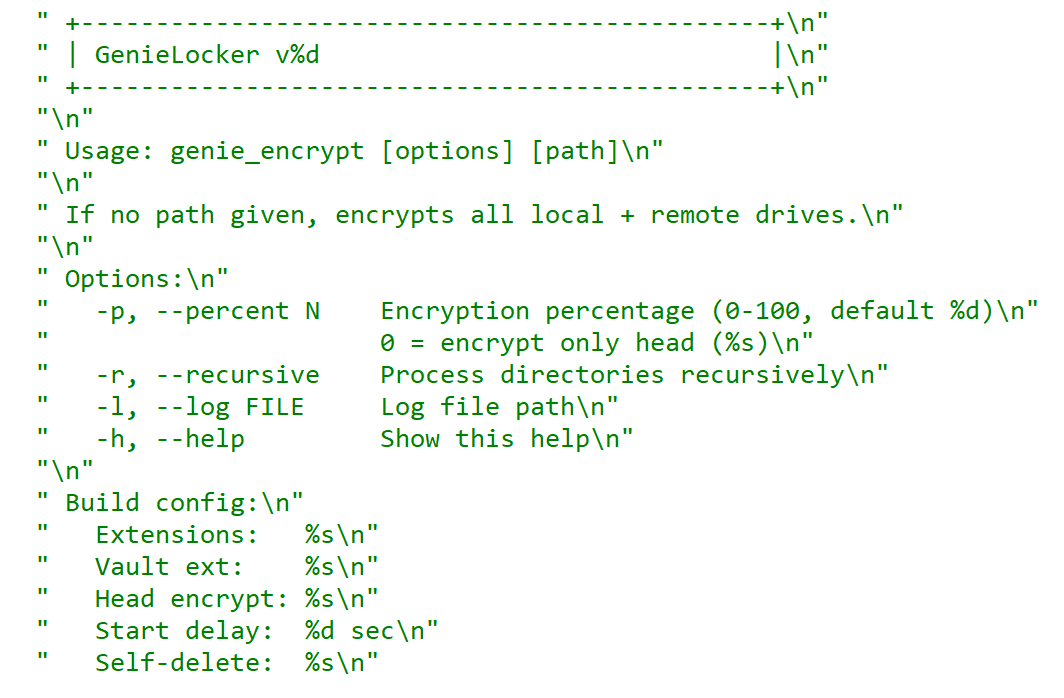
GenieLocker is a custom ransomware family used by Toy Ghouls against Russian organizations, especially in manufacturing, with Windows, Linux, and ESXi variants active since March 2026. The group used stolen OpenVPN credentials for entry, deployed tools like Mimikatz and PsExec, and encrypted systems without evidence of data theft or double extortion. #GenieLocker #ToyGhouls #Bearlyfy #Labubu #Laboo.boo #Mimikatz #PsExec #OpenVPN

Aurora targeted Pyramid Analytics B.V. in NL, obtaining the complete Pyramid Decision Intelligence Platform source code (including multiple full Git histories) and significant production SQL Server database backups. The stolen data reportedly included user accounts, credentials, and business/customer information from publicly traded companies, impacting NL. #Netherlands
Evosys Laser GmbH (DE), an Erlangen-based industrial laser welding systems manufacturer, disclosed a ransomware claim by threat actor aurora involving the compromise of its complete corporate repository, including HR, server infrastructure (mRemoteNG XML with domain admin credentials), and customer project data. The claimed impact includes exposure of industrial control assets and sensitive communications, with impacted country(s): #Germany
Aurora ransomware targeted Van Eijck International Car Rescue in the Netherlands, exposing 156 GB of employee home directories, 12 GB of RentRunner rental contracts with identity documents, and 10 years of customer claims data (2010–2019) containing extensive PII. The attacker also compromised a complete Google Workspace backup (CubeBackup) covering Gmail, Drive, and Calendar for 18 user accounts and 206 groups. #Netherlands

CISA has added CVE-2026-20316, a flaw in Cisco Secure Firewall Management Center (FMC) Software, to its KEV catalog after reports of zero-day exploitation. Cisco says the issue stems from static credentials in a low-privilege account and may be chained with CVE-2026-20079 to increase privileges and potentially reach code execution. #Cisco #CISACVE-2026-20316…

Amazon Threat Intelligence says the September 2025 hijack of debug and chalk was linked to a North Korean group, connecting it to earlier activity involving typo-crypto and the March 2026 axios compromise. The report points to shared tradecraft, trojanized packages, and overlapping command-and-control infrastructure, but the evidence publicly shared remains incomplete….

Cisco has patched CVE-2026-20316, an actively exploited zero-day in Secure Firewall Management Center that lets attackers use default credentials to access sensitive data. CISA added the flaw to its KEV catalog, and Cisco shared IoCs while warning the issue can be chained with other FMC vulnerabilities to gain higher privileges. #CVE-2026-20316…

Astaroth (aka Guildma) operators added a WhatsApp Web spambot in Q4 2025, shifting from email-based distribution to automated messaging that turns infected victims into unwilling propagators of the malware. The analysis shows strong code overlap with the Vareg (aka WATER SACI, Eternidade) spambot and confirms Brazil-focused targeting through contact filtering, Portuguese…
Prelys Courtage in France reported a client data breach affecting a major mortgage brokerage franchise, allegedly facilitated by the anubis ransomware threat actor. The incident is claimed to have involved unauthorized access to franchise client data, impacting stakeholders within #France.
Tal Kollander describes her journey from curious young hacker to defensive cybersecurity leader, shaped by gaming, social media exploration, and military service in the IDF. She now leads Remedio, where the focus is on understanding hacker behavior, detecting configuration drift, and fixing the weaknesses attackers exploit before they can move laterally….
The article argues that the Hugging Face breach was less about a single model flaw and more about broken governance, where an autonomous agent exploited weak controls, trusted inputs, and a vulnerable data-processing pipeline. It says AI safety depends on the operating environment, not just the model, and calls for stronger enforcement rules for autonomous agents across institutions like OpenAI and Hugging Face. #HuggingFace #OpenAI #ClaudeSonnet4_6 #StanleyMilgram #SolarWinds
The White House says the quantum supply chain is one of the biggest hurdles in advancing quantum technologies because it is fragmented across many different platforms and modalities. Officials also warn that funding, encryption risks, and the difficulty of benchmarking progress are slowing the United States as it races to build a stronger quantum ecosystem. #BradBlakestad #NationalQuantumCoordinationOffice #DonaldTrump
Ruby on Rails has fixed CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads when libvips is used. The issue can expose secrets like secret_key_base, database credentials, and API tokens, potentially enabling RCE or lateral movement if operators do not upgrade and…
AhnLab reports that a state-sponsored group abused vulnerabilities in Korean financial security software from 2025 through the first half of 2026 to deliver backdoors via watering hole and spear-phishing attacks, while many compromised Korean websites were used as infection points. The analysis also finds overlap with Gunra ransomware incidents and names…