Genesis ransomware by the threat actor genesis impacted C.A. Walker Construction, a construction management company in the US, by encrypting or compromising their systems. The incident affected organizations in #UnitedStates

Boyum IT Solutions (HOT!) in Denmark, an IT services provider, was targeted by the genesis ransomware threat actor, compromising business systems and data. The incident impacted Denmark #Denmark
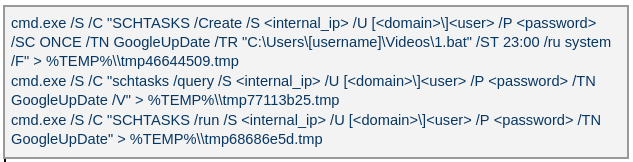
The article describes OctLurk, SilkLurk, and LurkProxy, three closely related implants used since January 2025 against government and other organizations across Central Asia and the Syrian Arab Republic, with victim-specific loaders and heavy obfuscation. The same campaign also included credential theft, keylogging, browser password theft, network scanning, remote access, and the later deployment of PlugX, while infrastructure overlap and shared artifacts suggest a Chinese-speaking threat actor. #OctLurk #SilkLurk #LurkProxy #PlugX

North Korea-linked threat actors launched a macOS malvertising campaign that uses a fake full-screen update page and ClickFix-style clipboard abuse to trick victims into running malicious Terminal commands. The campaign, tied to Contagious Interview and EtherHiding, delivers a Node.js backdoor, an info stealer, and a malicious Chrome extension targeting cryptocurrency wallets…
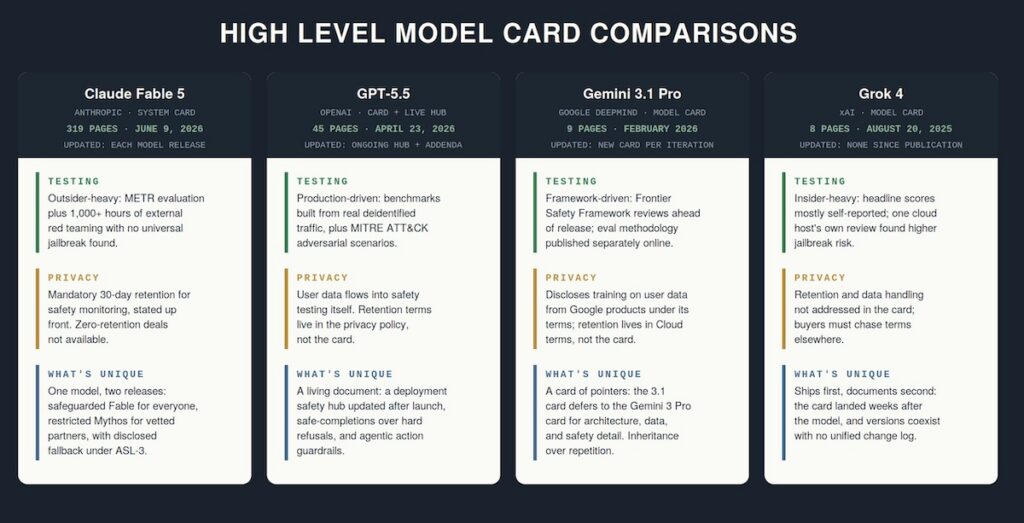
AI compliance should move away from bloated questionnaires and toward concise, evidence-based checklists that can be answered with logs, configs, eval reports, and other artifacts. The article argues that standardized model cards, risk-tiered assessments, and reusable controls can help organizations satisfy the EU AI Act, ISO/IEC 42001, and NIST AI RMF…
Okta has signed a definitive agreement to acquire Permiso Security, a cloud-native identity security platform focused on detecting threats across human, non-human, and agentic identities in multi-cloud environments. The acquisition will expand Okta’s identity security capabilities into ITDR and SOC operations, while integrating Permiso’s P0 Labs and threat research into Okta’s…

Brinks Home disclosed that attackers breached some of its systems and are threatening to leak stolen data, though its alarm monitoring and system functionality were not affected. ShinyHunters claimed responsibility for the intrusion and said it used a Microsoft Entra vishing attack to steal Salesforce and customer support data, while Brinks Home continues to investigate. #BrinksHome #ShinyHunters #MicrosoftEntra #Salesforce #Cresta
Broadcom has issued emergency patches for five VMware vulnerabilities affecting vCenter, ESX, Workstation, and Fusion, including three critical flaws that could let attackers bypass authentication, execute code, or escape a virtual machine to the host. Administrators of VMware Cloud Foundation, VMware vSphere Foundation, and VMware Telco Cloud products should update immediately, as Broadcom says there are no workarounds and no evidence of active exploitation yet. #Broadcom #VMware #vCenter #ESX #VMXNET3 #VMwareCloudFoundation #VMwarevSphereFoundation #VMwareTelcoCloudPlatform #VMwareTelcoCloudInfrastructure
Amazon linked a series of npm supply-chain compromises involving typo-crypto, debug, chalk, and axios to the North Korean Sapphire Sleet threat actor, also known as BlueNoroff and Stardust Chollima. The campaign used social engineering, malicious package updates, and evolving stealth techniques, while Amazon also backed community defenses and the Akrites initiative. #SapphireSleet #BlueNoroff #StardustChollima #npm #axios #debug #chalk #typo-crypto #OpenSSF #Akrites
cmdorganization ransomware actors claimed their intrusion impacted Contact Group, a proudly Tasmanian Australian building services and multi-technology solutions provider serving commercial, government, healthcare, and education clients across electrical and communications, HVAC-R, infrastructure, fire, technology, security, plumbing, and facilities maintenance. With over 35 years of experience, Contact Group’s operations were targeted in #Australia.
In June 2026, incransom compromised Australia-based Partnered Health Group, exfiltrating 3.2 TB of data—including 27 years of patient records, payroll/HR files, and multiple SQL and Best Practice database backups—from 21 servers across 21 clinics. The stolen dataset also includes Bupa corporate billing and program information, placing patients and staff in Australia at risk of further exposure. #Australia
Section9 ransomware claim targeted “And where does the newborn go from here? The net is vast and infinite.” with threats to compromise or disrupt systems. The impacted country(s): #

Operation Cronos exposed that LockBit did not reliably delete stolen data after ransom payment, undermining the assumption that victims could buy data safety. The piece also shows how volatile outcomes, especially from groups like Icarus, Silent Ransom, and Dharma, are reshaping ransomware payments, tactics, and trust in extortion negotiations. #LockBit #OperationCronos #Icarus #SilentRansom #LunaMoth #Klue #Dharma

A 41-year-old Ghanaian national, Derrick Van Yeboah, was sentenced to 85 months in prison for helping steal more than $10 million from vulnerable victims through romance scams. He was a high-ranking member of a Ghana-based criminal organization linked to over $100 million in losses and was extradited to the United States after his arrest in Ghana. #DerrickVanYeboah #JusticeDepartment #SouthernDistrictofNewYork
The article warns that U.S. troops remain exposed to telecom-based attacks because commercial cellular networks are still vulnerable to signaling abuse that can expose locations, intercept communications, and disrupt service. It calls on carriers, Congress, regulators, and the Pentagon to tighten oversight, improve defenses, and provide more secure mobile service for servicemembers. #Iran #Russia #China #SaltTyphoon #Spiral4