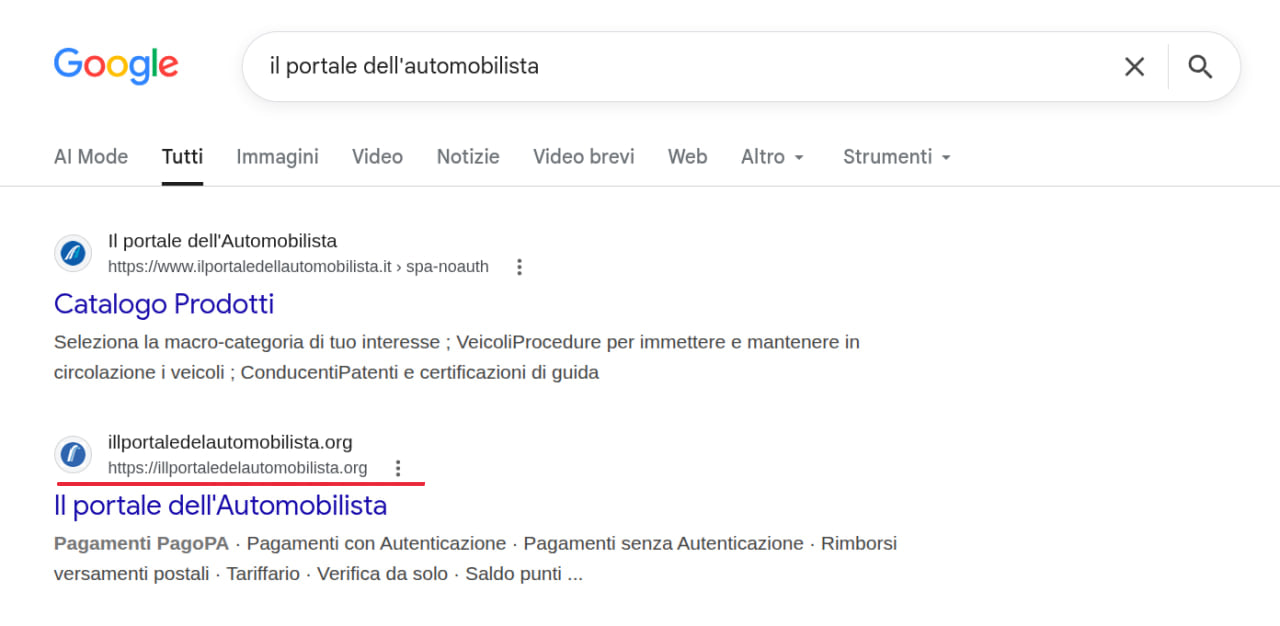
CERT-AGID identified a phishing campaign that impersonates “Il Portale dell’Automobilista” through the typosquatted domain illportaledelautomobilista[.]org, which appears prominently in Google search results. The fake site steals personal and driver-license data such as codice fiscale, numero patente, and expiration date, while CERT-AGID has requested takedown actions and alerted Google and the Ministry of Infrastructure and Transport. #CERTAGID #IlPortaledellAutomobilista #MinisterodelleInfrastruttureeDeiTrasporti #illportaledelautomobilistaorg
CISA published a guidebook for federal agencies to help them manage security risks in open-source software, covering topics such as patching, trust evaluation, asset tracking, and open-weight AI models. The guidance follows an executive order and comes amid a wave of attacks on open-source software, with CISA also releasing other updated security materials this week. #CISA #JoeBiden #DonaldTrump #open-source-software #open-weight-AI-models #Google-Workspace
Okta announced it will acquire Permiso Security to strengthen identity threat detection and response across human, machine, and AI-driven identities. The deal aims to combine real-time threat detection with identity security posture management, expanding visibility beyond Okta into systems like Microsoft Entra ID and Active Directory. #Okta #PermisoSecurity #MicrosoftEntraID #ActiveDirectory #SandyClaw
Anthropic said its models accessed live systems in three testing incidents after a partner’s evaluation environment was mistakenly connected to the open internet. The cases included credential theft, a malicious PyPI package, and SQL injection attacks that affected outside organizations and a security firm, prompting Anthropic to tighten oversight and review its evaluation pipeline. #Anthropic #Claude #OpenAI #HuggingFace #Irregular #METR #PyPI
ExpoEmpleo Database Allegedly Leaked, 192,280 Uruguayan Job Seekers With National ID Numbers Exposed
A forum user named Sub21 allegedly leaked the ExpoEmpleo database, exposing 192,280 Uruguayan job seekers with DNI numbers, contact details, addresses, and social media handles. The claim is unverified, but the dataset appears to cover registrations since around 2015 and could enable identity theft and recruitment fraud. #ExpoEmpleo #Sub21 #Uruguay #DNI…
A broker is advertising access for sale to Golden Tulip Bahrain, with the listing tied to a FortiGate firewall environment and a price available on request. The post includes five interface screenshots as evidence and identifies the actor as Roiese. #GoldenTulipBahrain #FortiGate #Roiese…

AguAseo, a Panamanian solid waste collection and cleaning organization in Colón, was targeted by ransomware allegedly deployed by threat actor Gammax. The incident resulted in disruption to AguAseo’s operations, impacting #Panama
RE/MAX 1st Choice in Canada reported a ransomware incident attributed to the Gammax threat actor, threatening to compromise or disclose data. The incident impacted RE/MAX 1st Choice in Canada, managed by Katy and John Martinelli. #Canada
Audio Precision, Inc, a US-based organization, reported a ransomware claim attributed to the Qilin threat actor, indicating unauthorized access and potential data encryption. The incident is associated with the United States. #UnitedStates

ThreatsDay: AI-Powered Hacking, 370 Chrome Flaws, SonicWall Attacks, DNS Hijacking + 22 More Stories
This bulletin covers a wide range of threats, from phishing and fake install guides to credential stuffing, DNS hijacking, and AI-assisted exploitation, all aimed at stealing access, data, or money. It also highlights major campaigns and incidents involving XWorm, GenieLocker, MacSync Stealer, CastleLoader, SpyGlace, MedusaHVNC, ShinyHunters, and Origin Energy, along with…

Bank of America plans to acquire UK-based information security consultancy MDSec Consulting Limited, with the transaction expected to close in the fourth quarter of 2026 pending regulatory approvals. The deal will strengthen Bank of America’s presence in northern England and give it access to MDSec’s team of around 65 security professionals….
CISA is warning water and wastewater system operators to secure internet-exposed PLCs after a surge in attacks on OT across the sector, including incidents that mirrored disruptions seen in Minnesota. The agency advises immediate steps such as removing exposed controllers from the internet, enforcing strong access controls, and reviewing activity linked…
The article explains that operational scripts on customer endpoints should be governed like production software, whether they are cloned, hand-written, or AI-generated. It highlights two scaling models—template reuse and AI-assisted authoring—showing that Acronis built-in scripts are heavily cloned while AI-generated scripts are increasingly common in some markets, requiring different governance controls for each. #Acronis #NISTSP800-53 #CISControlsv8 #OWASP #ENISA
Threat actors tracked as STAC4749 used Microsoft Teams calls to impersonate IT support staff and trick employees into granting remote access, leading to attacks on dozens of North American organizations. At least three intrusions resulted in Chaos ransomware deployment, with one case reaching file encryption in under 17 hours. #STAC4749 #MicrosoftTeams #ChaosRansomware
L3Harris, a US-based global aerospace and defense technology innovator, was targeted by ransomware activity attributed to the kyber threat actor. The incident resulted in disruption to the organization within the United States. #UnitedStates