
SecurityWeek’s weekly roundup covers major cybersecurity developments, including the OnTrac breach, Adobe vulnerability patches, SonicWall credential stuffing, and a North Korea-linked supply-chain campaign against popular NPM packages. It also highlights data exposure at the UK Department for Education, flaws in VE Commercial Vehicles’ My Eicher platform, and AI-assisted cryptanalysis research from…
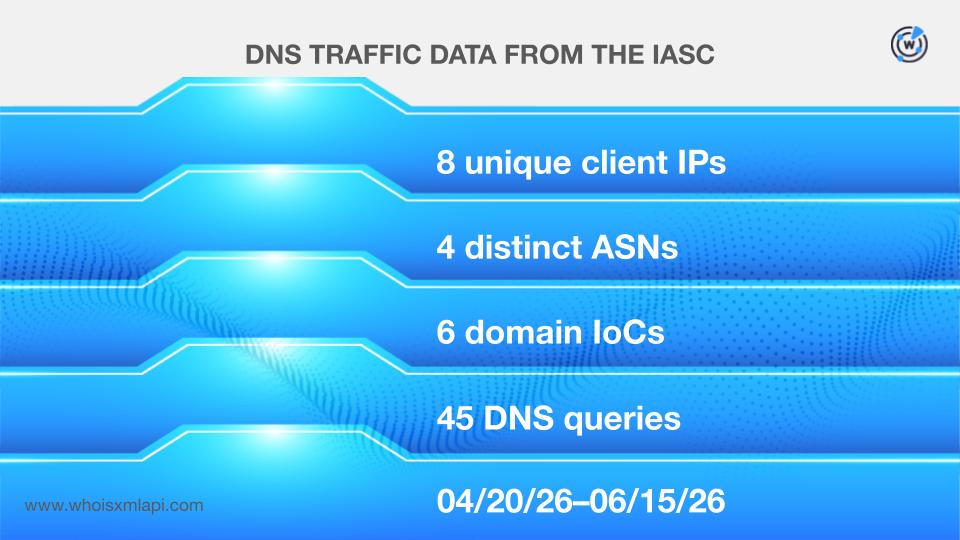
Sekoia researchers analyzed a new ErrTraffic ClickFix campaign that targeted WordPress servers, used fake AI tool lures, and hid C&C infrastructure in blockchain-based networks. Their DNS and WHOIS investigation uncovered 71 domains, multiple malicious IPs, typosquatting clusters, and possible links to the LenAI MaaS operator and the Aeternum botnet. #ErrTraffic #ClickFix #LenAI #Aeternum
Rapid City, South Dakota, reported a cyber intrusion attempt targeting a wastewater lift station, but its water and wastewater systems remained safe. The incident comes amid a national warning about attacks on internet-connected industrial controllers used by water utilities, while the city works with federal agencies. #RapidCity #PenningtonCounty
Attackers in H1 2026 are scaling their operations by adapting familiar techniques to new platforms, with AI increasingly used in both attack infrastructure and malware. ESET reported nearly 900,000 AI skills analyzed, the emergence of PromptSpy as the first known Android malware to use generative AI, and continued growth in ClickFix, quishing, and EDR killer use. #PromptSpy #Gemini #ClickFix #quishing #EDRkillers #ESET
CISA is warning that internet-exposed PLCs in water and wastewater systems are being increasingly targeted, with recent attacks disrupting more than 30 Minnesota community water systems. The agency says attackers have changed passwords, altered IP settings, and exploited exposed OT assets, while advising organizations to remove direct internet exposure and secure access through VPNs or gateways. #CISA #Minnesota #RockwellAutomation #AllenBradley #Siemens #SchneiderElectric #MicroLogix1400

A Chinese-speaking threat actor used DeepSeek and the open-source Hermes Agent to run autonomous attacks against exposed servers with minimal human involvement. Unit 42 found the campaign showed a functional end-to-end AI offensive workflow, even though the observed exploit attempts failed to compromise the targets. #DeepSeek #HermesAgent #Unit42 #FOFA #Langflow #n8n #CVE-2026-33017 #CVE-2026-21858 #CVE-2025-68613 #CitrixNetScaler #ApacheTomcat #MarimoNotebook #WindowsIKEVPN

The ransomware claim targets Betz Industries in the US, with the Booba Project threat actor allegedly stealing 7 GB of data. The impacted country(s) are: #UnitedStates
Interlock ransomware has claimed responsibility in the US, stating that Gardiner Family Chiropractic’s patient data, client records, medical histories, and internal financial information were compromised and are being exposed. #UnitedStates
The ransomware claim alleges that dragonforce targeted Lamont Pridmore, an independent chartered accountancy practice in the UK (GB) based in Carlisle, Cumbria and Lancashire, stealing or encrypting confidential internal and client financial documentation. The released archive, which expands to about 250 GB after unpacking, is said to include sensitive client data across the firm’s services, including accountancy, tax, and business advisory, resulting in exposure of confidential information in #UnitedKingdom

Researchers from Nanyang Technological University uncovered a widespread class of implicit trust errors in 4G and 5G core networks that can lead to denial-of-service and session hijacking attacks. Their study found 84 previously unknown vulnerabilities across open-source and commercial LTE/5G core implementations, including issues in Open5GS, free5GC, OpenAirInterface, SD-Core, eUPF, and…

Google fixed 1,072 Chrome security bugs in versions 149 and 150, while Chrome 151 addressed another 370 flaws, including seven critical issues. The company is accelerating Chrome security with faster release cadences, dynamic patching, and memory-safe development to reduce exposure to rapidly discovered vulnerabilities. #Chrome #Chrome151 #CVE-2026-3545 #Gemini…

Daily Recap, funding accelerated across security and data platforms, with DataBahn raising $40M, Cantina emerging from stealth with $8M, Discern Security securing $13M, and ThreatLocker landing a $190M Series F to expand its security platform. Major risk headlines included actively exploited Cisco Secure FMC zero-days tied to static credentials, critical Rails and VMware flaws spanning file read, auth bypass, code execution, and VM escape, plus threat activity such as Huntress targeting 30 SonicWall customers and Russian hackers abusing Microsoft Exchange OWA for long-term mailbox access. #CiscoSecureFMC #StaticCredentials #Rails #VMware #Ruflo #MCP #MicrosoftExchangeOWA #RussianHackers #SapphireSleet #OpenAI #Huntress #SonicWall #ShinyHunters #HealthISAC #MinnesotaWaterUtilities #AnalogDevices #KB5101684
BLUEVISTALLC.COM in the United States reported a ransomware incident in which the threat actor clop encrypted or threatened to expose data unless ransom demands were met. The impacted country(s) is: #UnitedStates
US-based law firm MBM Law (Moore Bradley Myers), www.mbmlawsc.com, was targeted in a ransomware claim attributed to the threat actor dragonforce. The attack affected the firm in the United States. #UnitedStates
Ransomware claimed by dragonforce targeted RUS Industrial, a US heavy industrial construction services provider serving chemical refineries, petrochemical plants, oil and gas facilities, and mission-critical data centers. The incident disrupted operations and services, impacting operations in the United States. #UnitedStates