Ransomware activity attributed to the safepay threat actor targeted pradotuylaw.com, a US-based law firm handling matters such as personal injury, wrongful death, workplace harassment, business litigation, civil settlements, and environmental litigation. The impacted country(s): #UnitedStates

Universitatea De Vest Vasile Goldi Din Arad in Romania reported a ransomware attack attributed to the qilin threat actor, though specific details were not provided. The incident impacted #Romania

Zscaler details BINDCLOAK, a new 64-bit modular Windows backdoor that appears to be a variant of OctLurk and was delivered through MIXEDKEY in a multi-stage attack against government entities in the Middle East. The report also links the campaign to shared C2 infrastructure, reflective DLL loading, token abuse, and encrypted TLS-over-TCP communications used by the same threat actor behind OctLurk. #BINDCLOAK #OctLurk #MIXEDKEY #TELESHIM #cert.hypersnet.com #about.blsouqs.com #ftabnews.com

Unit 42 described three Windows post-compromise attack paths, Pass-ta-key, Silver Pass-ta-key, and Golden Pass-ta-key, that let malware abuse Chrome’s Google Password Manager to log into passkey-protected accounts without a visible user prompt. The report says the techniques target Chrome’s device keys, re-enrollment flow, and Security Domain Secret handling on TPM-equipped systems,…

Researchers found malicious npm packages that impersonate Alibaba private packages and deliver a cross-platform RAT against Chinese-speaking developers in a targeted supply chain campaign. The attack uses layered dependencies, Alibaba-themed infrastructure, and OS-specific payloads to enable persistence, espionage, and lateral movement. #lib-mtop #aone-kit #aone-kit-cli #aone-sandbox #local-config-parser #smart-config-manager #Alibaba…

A cyberattack accessed Liechtenstein’s register of economic beneficiaries, exposing data tied to about 31,000 people behind companies, foundations, and trusteeships. The government took the system offline, set up a crisis unit, and said there were no signs the data was altered or deleted. #Liechtenstein #registerofeconomicbeneficiaries…
PIONEER COLDSTORE & CLADDING PVT. LTD. (PCC) at pcclimitedindia.com in India reported a LockBit5 ransomware attack, with the threat actor demanding a ransom after encrypting or disrupting data systems. The incident affected operations in #India
Belasco Electric, a trusted electrical service provider in Muskegon, Michigan serving residential and commercial clients, reported a ransomware claim by the akira threat actor. The attackers stated they will exfiltrate 16GB of corporate data soon, potentially including employee PII (such as SSNs and passport/driver’s license details), financials, contracts, and NDAs, impacting the United States #UnitedStates
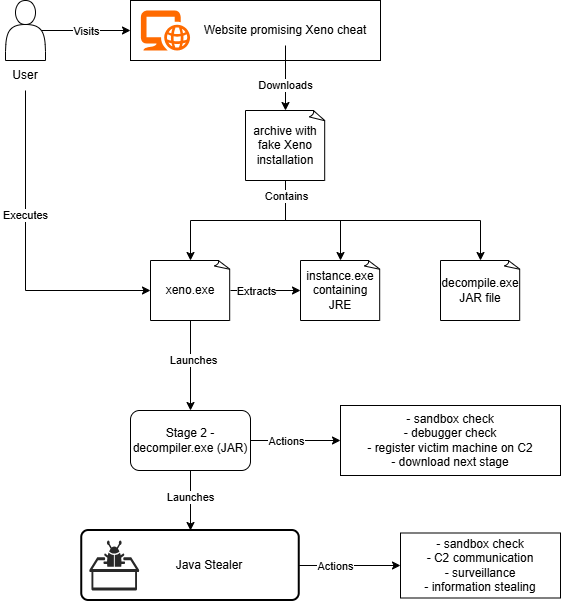
Bitdefender researchers uncovered a Java-based malware campaign that impersonates an “undetected” Xeno Roblox script executor and spreads through gaming forums and Discord communities. The payload steals browser cookies, Discord, Roblox and Minecraft accounts, crypto-wallet and payment data, while also enabling keylogging, webcam access, desktop streaming, file manipulation, PowerShell execution, and remote…
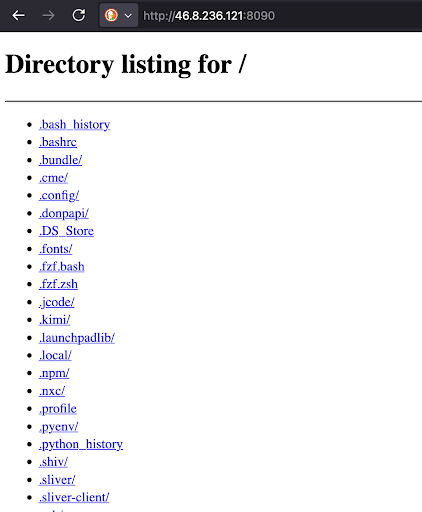
An exposed server tied to a Russia-nexus operator exposed months of activity showing high-volume initial access brokerage, broad exploitation of appliances, credential theft, and full Active Directory compromise across many sectors worldwide. The same operator later used Sliver C2 for targeted collection against Ukrainian defence and aerospace organisations, including theft from Git repositories and imagery from thousands of exposed IP cameras, with the activity aligning to AIVD/MIVD warnings about Russian camera surveillance. #Sliver #AIVD #MIVD #Fortinet #F5 #Citrix #SonicWall #SAP #HikVision #Neo-reGeorg
BTMOB started as a centrally run Android RAT malware-as-a-service operation, but it has since splintered into a fragmented underground market of resellers, source-code vendors, independent server operators, and impersonators. Flare researchers found that the official channel kept releasing new versions and infrastructure offers while cheaper and sometimes unverified BTMOB listings spread across Telegram and other platforms. #BTMOB #Flare #Telegram
A cyberattack on the U.K.’s Police National Legal Database (PNLD) exposed contact details belonging to more than 100,000 police officers and other criminal justice professionals. The ExfilSquad group claimed responsibility, alleging it stole 135,000 records and threatened to leak the data unless a ransom was paid. #PNLD #ExfilSquad
River Financial Corporation, the bank holding company behind River Bank & Trust, says it received confirmation that data stolen in a ransomware attack was deleted. The company is still investigating the incident, including whether any personal information was accessed or exfiltrated, after hackers compromised portions of its network and prompted multiple…
Visa has agreed to acquire BioCatch for $2.4 billion in cash to strengthen its fraud prevention, cyber risk, and financial crime detection capabilities. BioCatch’s behavioral biometrics and AI-driven technology help identify account takeovers, scams, money mule activity, and other fraud before payments are completed. #Visa #BioCatch #Permira…
Security vendors at Black Hat USA 2026 in Las Vegas unveiled a wide range of new products and updates, with many focused on protecting AI agents, improving detection, and automating remediation. The roundup highlights announcements from Acalvio, Cyera, SentinelOne, Varonis, XM Cyber, and others, alongside research showing that identity and privilege…