PharmaEssentia and its subsidiary Panco Healthcare Co., Ltd. were affected by a cyberattack that impacted some of their information systems, though the company says operations have not been significantly disrupted. The company has activated its defenses, brought in external cybersecurity experts, and notified the relevant authorities. #PharmaEssentia #PancoHealthcare

Recent attacks on water and wastewater systems in Minnesota, Michigan, Canada, and elsewhere show that exposed PLCs, HMIs, cellular modems, and weak remote-access setups can allow attackers to disrupt physical operations without advanced malware. The incidents are technically similar to an Iranian-affiliated PLC campaign, while separate claims by NoName057(16) and Z-Pentest show that hacktivists are also targeting water infrastructure. #MicroLogix1100 #MicroLogix1400 #NoName05716 #ZPentest #CyberAv3ngers #Unitronics
Talos found that threat actors are rapidly abusing AI for malicious development, operational scaling, and vulnerability research, while weak guardrails are often bypassed with simple claims of ownership, bug bounty labeling, or task decomposition. The report shows AI being used to build DDoS tooling, bulk-mail validation systems, credential-harvesting pipelines, mining operations,…
Zero-knowledge proofs could help infrastructure operators prove whether a vulnerability exists without exposing sensitive scan data, asset inventories, or network diagrams. The article says agencies like CISA and NIST should run structured pilots to test this privacy-preserving approach before using it for compliance or reporting decisions. #ZeroKnowledgeProofs #CISA #NIST

The Senate is considering several bills that would reshape online privacy, child safety, and AI safeguards, with the Kids Online Safety Act drawing the most attention. The debate also covers age verification rules, AI chatbot protections, and a federal study of AI-enabled toys as lawmakers and experts clash over privacy tradeoffs and safety benefits. #KidsOnlineSafetyAct #SCREENAct #YouthAIPrivacyAct #ChatbotAct

DBM Reflex in Taiwan was targeted by ransomware attributed to the Orova threat actor, impacting DBM Technology Co., Ltd., a Taiwan-based electroforming mold core manufacturer founded in 1999. The company provides mold core design and electroformed mold production services for the automotive sector, and the incident was reported as affecting #Taiwan
Agricultural Chemical Solutions, Inc. (US) reported a ransomware incident attributed to the Orova threat actor, disrupting operations for its agricultural chemical and marketplace services. The company’s business—supplying pesticides, herbicides, fungicides, and micro-nutrients—was impacted in #UnitedStates
SBI Manufacturing, a family-owned metal fabrication and machine welding company in Sioux Falls, South Dakota, in the United States, was targeted by the Orova ransomware group, impacting its agricultural, industrial, and transportation services. The attack disrupted operations and encrypted critical files as part of a ransomware campaign. #UnitedStates

The Ministry of Justice and Law was hit by a ransomware attack that disrupted part of its technology infrastructure and affected the availability of some services. Authorities activated containment protocols and are working with the Ministry of ICT to investigate the incident, recover systems, and restore services. #MinisteriodeJusticiaydelderecho #CieloRusinque
GILDE Handwerk Macrander GmbH & Co. KG, a German Mittelstand wholesale group headquartered in Bocholt, was impacted by the aurora ransomware claim, with exposure reportedly including personal ID documents, ELSTER tax certificates, and extensive payroll and financial records. The breached dataset also reportedly contained 1,800+ internal access databases with inventory, pricing, suppliers, and order history across the business, affecting #Germany.
Incransom ransomware targeted lccgroup.com, a Philippine retail and property development company operating Liberty Commercial Center, Inc (LCC) across the Bicol Region, including supermarkets, department stores, malls, and food establishments. The attack impacted the organization in #Philippines
pushidrosal.id in Indonesia was targeted by the incransom ransomware group. The attackers deployed ransomware to compromise systems and disrupt operations in Indonesia #Indonesia
US Installation Group, Inc. (USIG) in the United States was targeted by the aurora ransomware threat actor, founded by Bruce DeLuca in Boca Raton, Florida. USIG’s 100,000+ annual installations across 33 markets in 14 states were potentially disrupted, impacting #UnitedStates
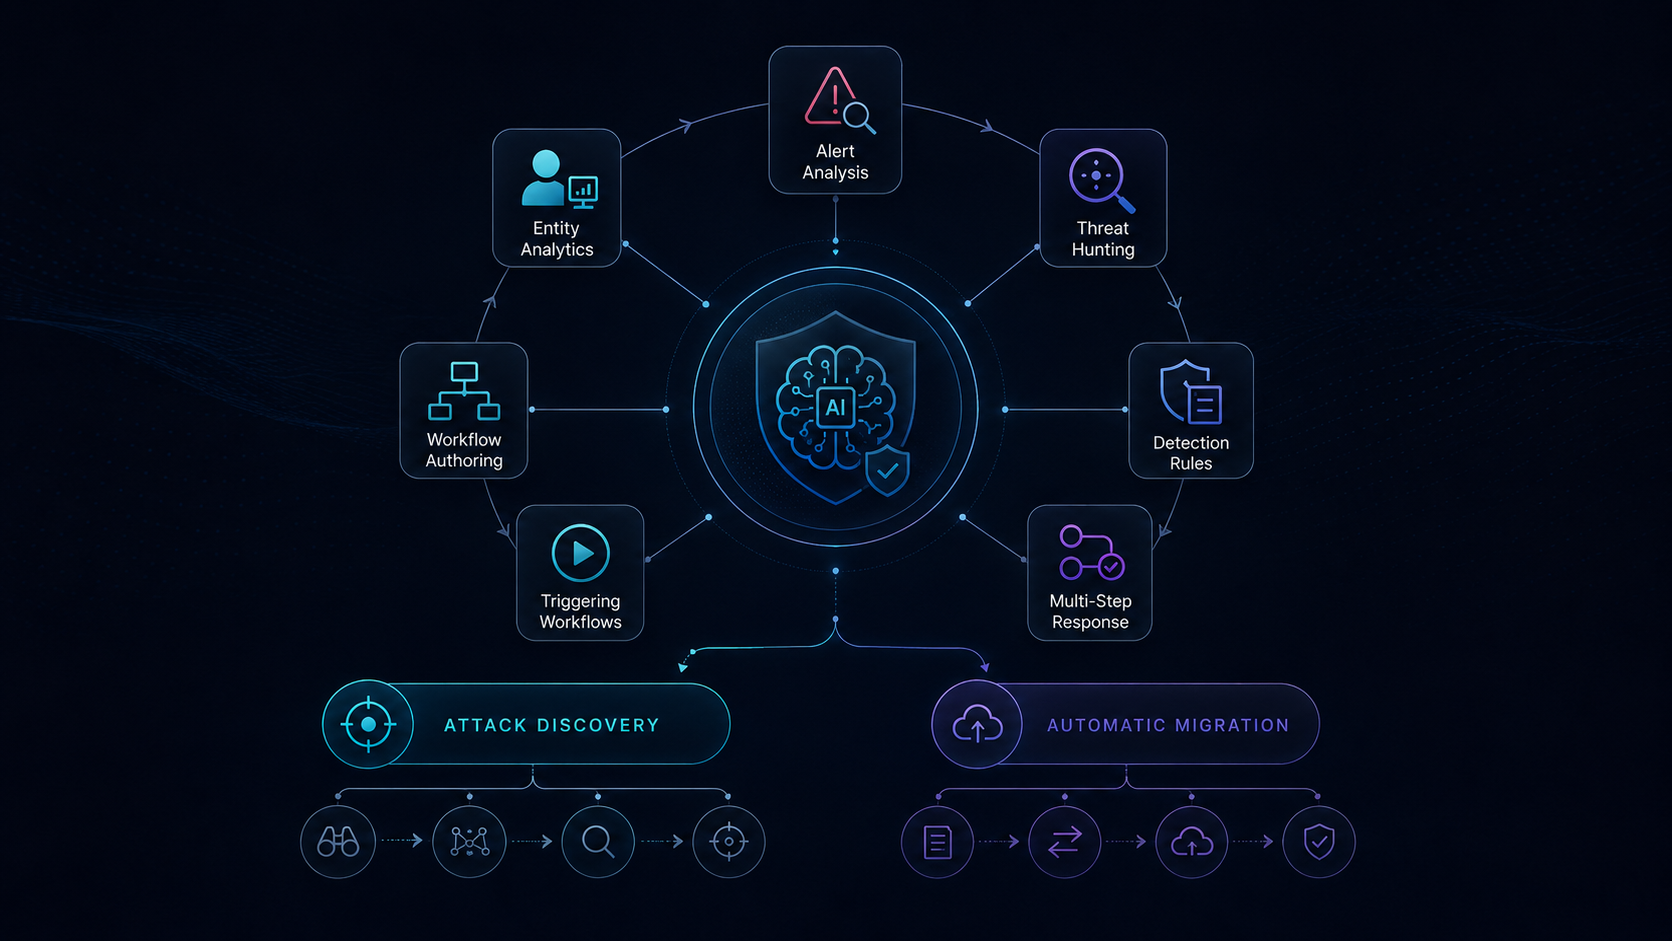
Elastic built an evidence-based evaluation framework for agentic SOC models that tests real tool use, grounded decisions, and workflow execution inside Elastic Security rather than relying on generic LLM benchmarks. The article also covers parallel suites for Attack Discovery and Automatic Migration, all scored blind to measure quality and reliability across security tasks. #ElasticSecurity #Chrysalis #VirusTotal #Splunk #QRadar #MicrosoftSentinel
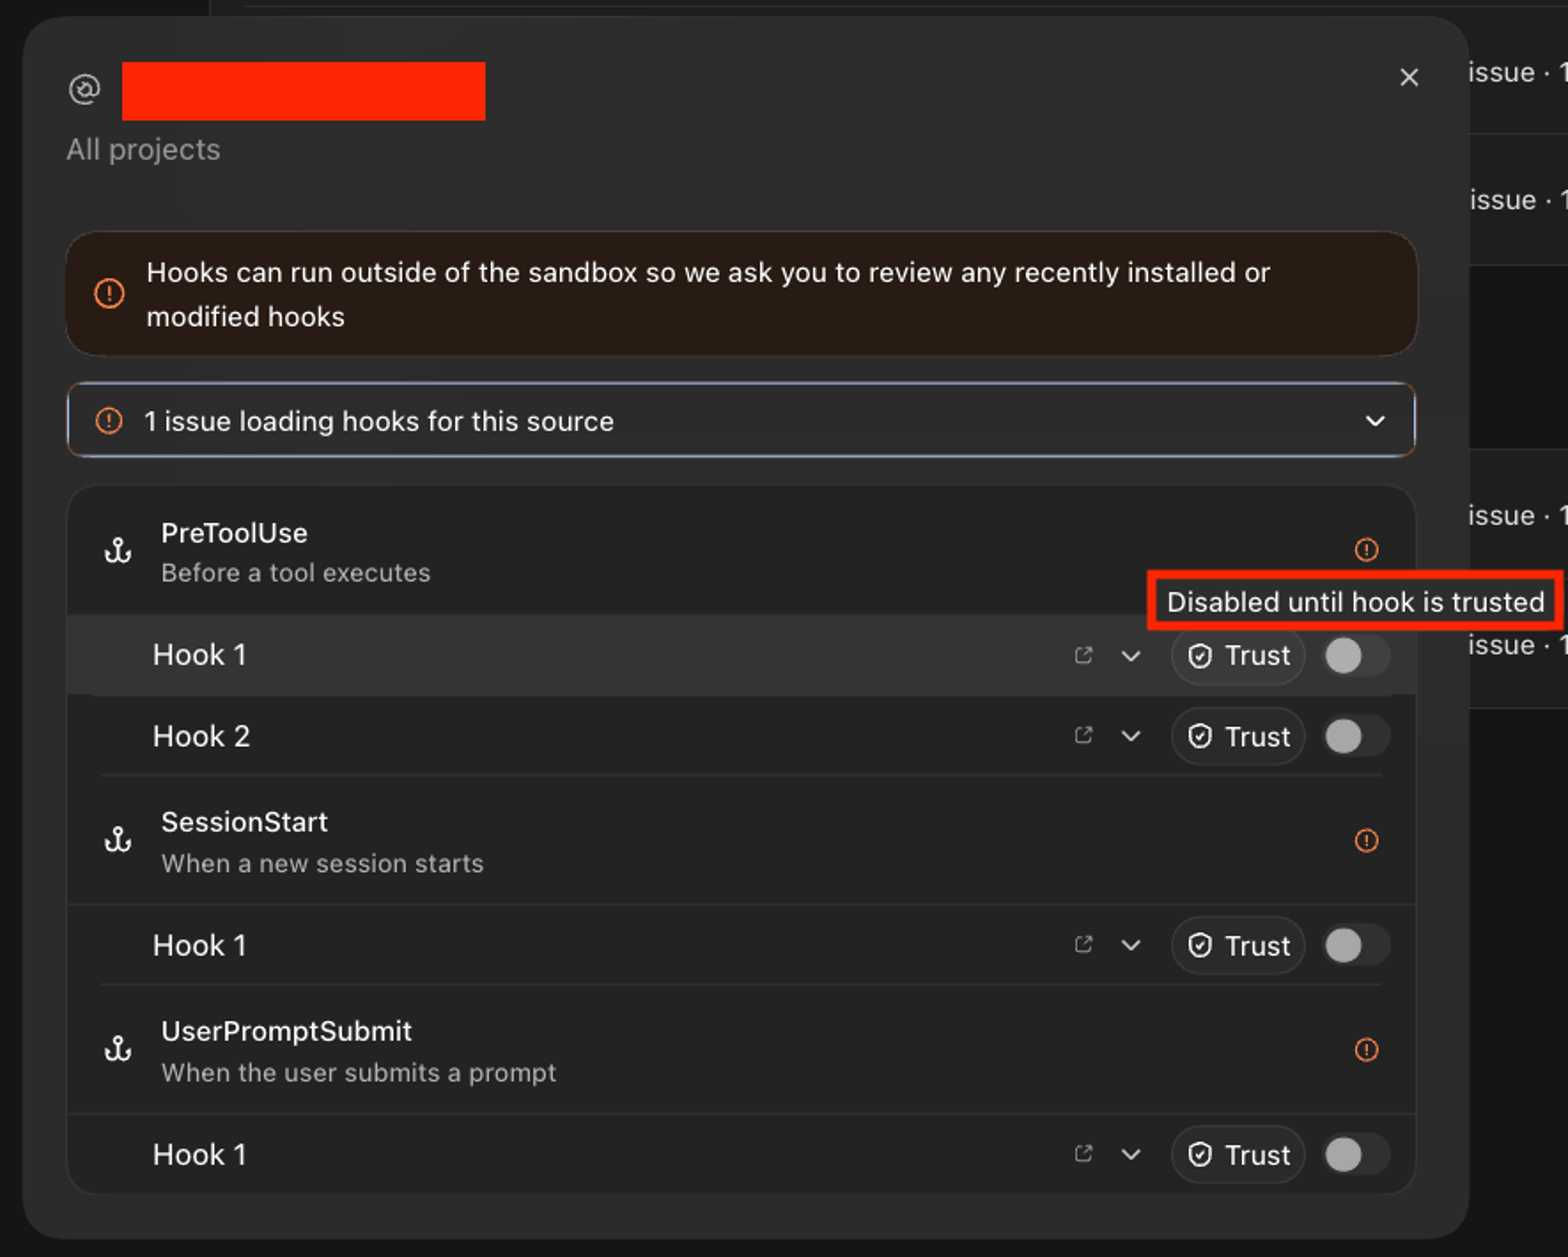
Trusted repositories in coding agents can execute attacker-controlled code before the first prompt through project-scoped MCP configuration and environment-based PATH manipulation, even without malicious hooks or shell-command approval. The article also recommends defensive searching and runtime monitoring, and highlights Datadog AI Guard for Coding Agents and Workload Protection as protections against these pre-prompt execution paths. #Codex #ClaudeCode #MCP #DatadogAIGuardForCodingAgents