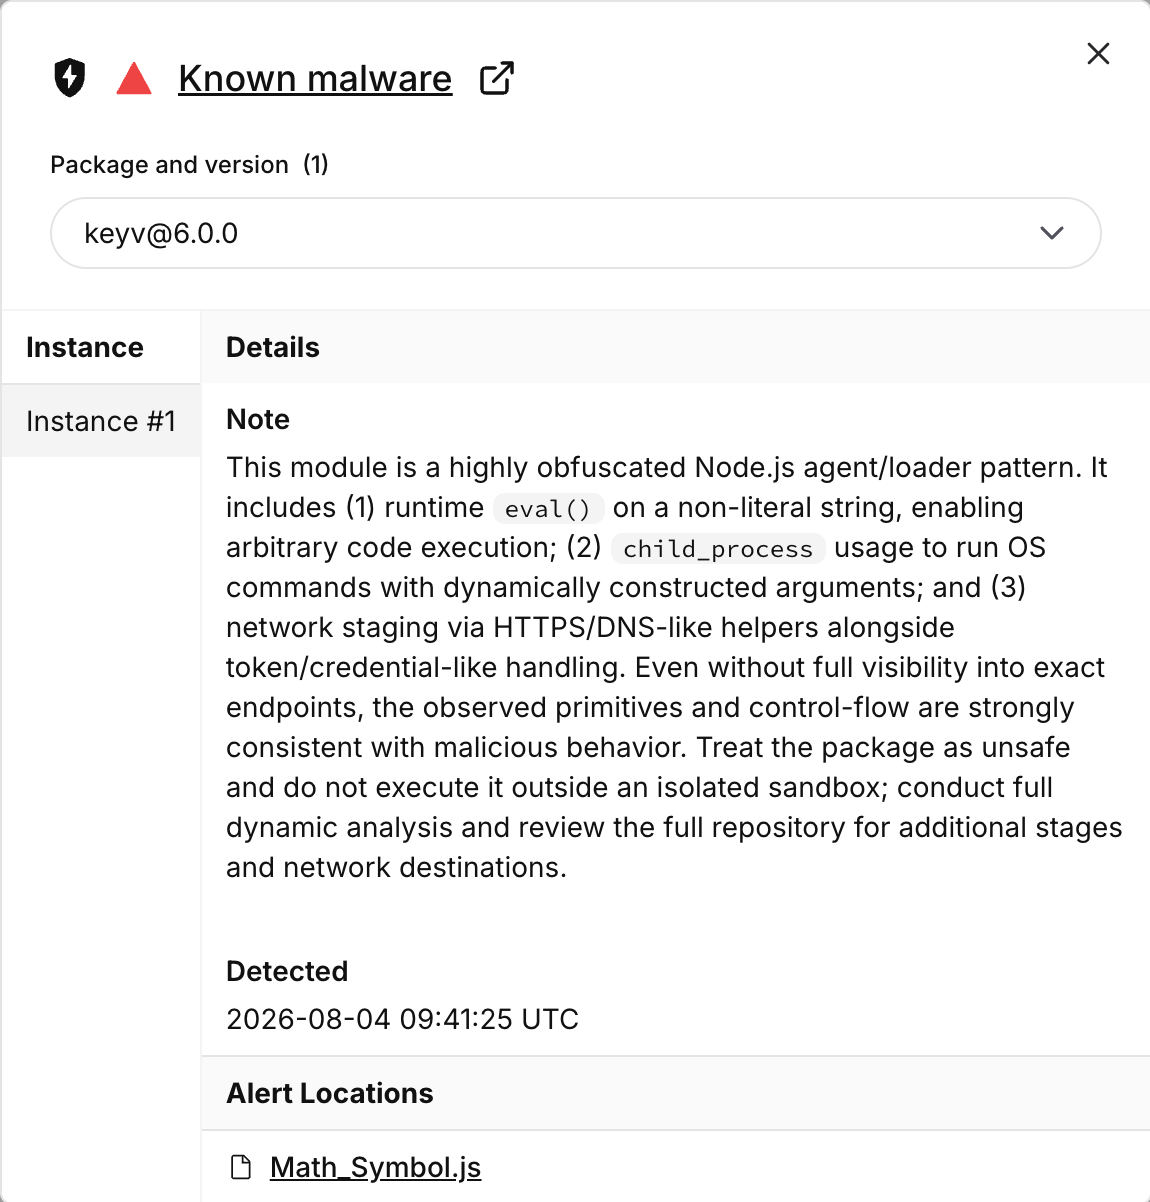
Socket is tracking an active supply chain compromise in the keyv and cacheable npm ecosystems, where trojanized packages used a malicious preinstall hook to download Bun, steal cloud and CI credentials, and republish infected packages through stolen npm tokens. The campaign affected tens of millions of weekly downloads and also planted persistence in developer and AI coding environments via .claude and .vscode hooks. #keyv #cacheable #Jaredwray #Bun #npm #GitHubActions #HashiCorpVault
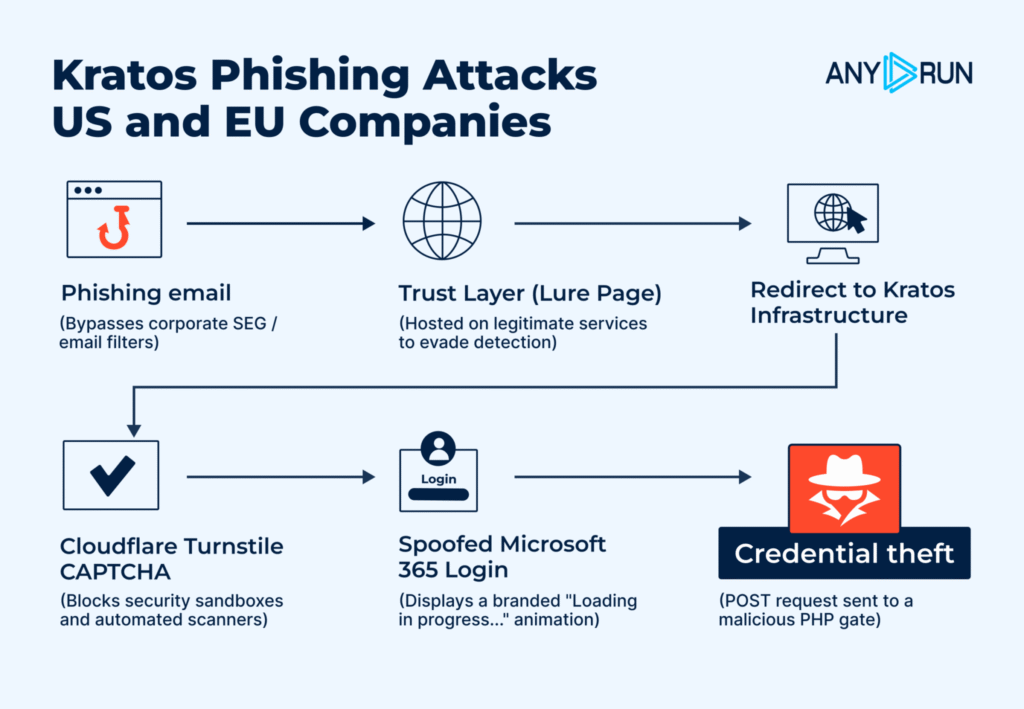
July 2026 attacks showed how trusted business workflows, legitimate platforms, and built-in tools were abused to drive account takeover, data theft, fraud, and persistent access across the US, Europe, and Brazil. ANY.RUN highlighted campaigns involving Kratos, PhantomEnigma, Kali365, Banana RAT, DARTHVADER Stealer, OVERLORD RAT, DestinyStealer, and fake Zoom event lures that…
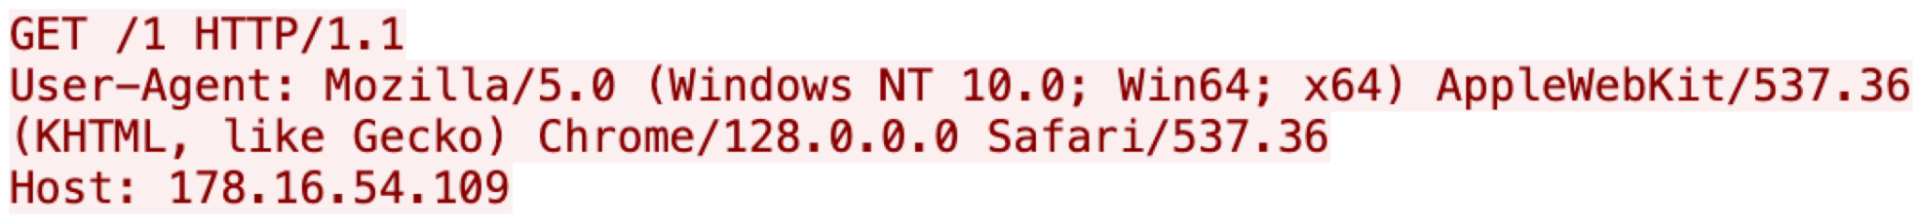
Unit 42 found that nearly half of malware samples with command-and-control activity make direct-to-IP connections, bypassing DNS and exposing a major visibility gap in traditional defenses. The report highlights ZT-IP detections for Phorpiex, SectopRAT, Mozi, and Boatnet activity, plus an obfuscated GET exfiltration campaign and hard-coded IP-based infrastructure. #Phorpiex #SectopRAT #Mozi…
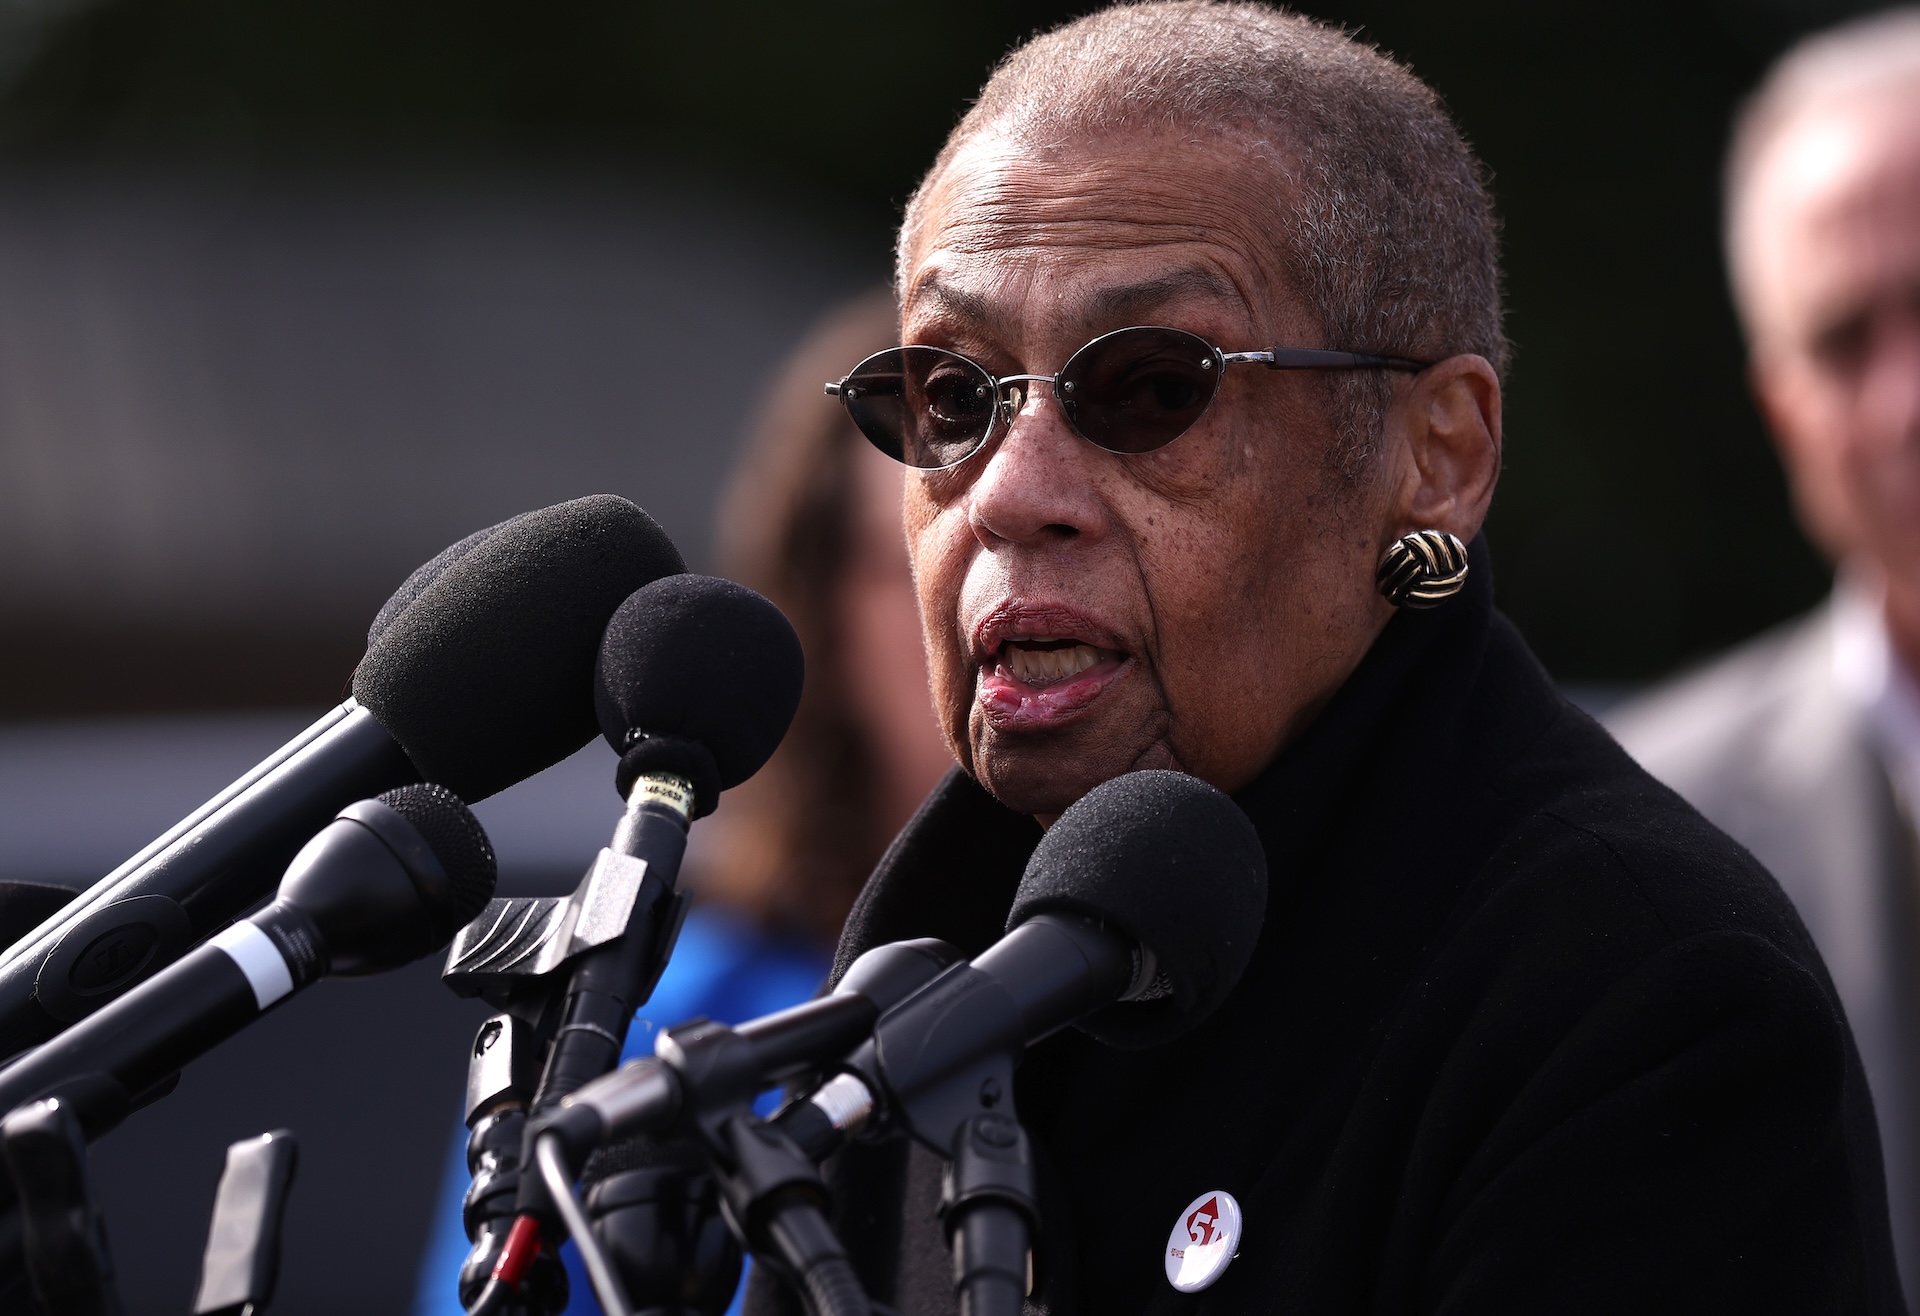
Lawmakers are pushing to make identity protection for millions of victims of the 2015 Office of Personnel Management breach permanent before the current authorization expires in September. The RECOVER PII Act would extend lifetime coverage and reimbursements for affected federal employees and contractors after data stolen by alleged Chinese hackers exposed sensitive personal information. #OfficeofPersonnelManagement #RECOVERPIIAct #MarkWarner #EleanorHolmesNorton #ChineseHackers

Researchers said INC ransomware has become the most active threat actor exploiting two recently disclosed SonicWall zero-days, chaining the flaws for full access soon after public disclosure. The attacks have affected multiple organizations, with evidence of attempted extortion and new alleged victims appearing on INC’s leak site. #INC #SonicWall #CVE-2026-15409 #CVE-2026-15410
Democratic senators warned that the Trump administration’s inconsistent AI security actions could push companies and governments toward Chinese open-weight models, creating new national security and supply-chain risks. They cited the Hugging Face breach and the Anthropic Fable 5 and Mythos 5 access suspensions as examples of opaque decisions that may undermine U.S. competitiveness and confidence in American AI systems. #OpenAI #HuggingFace #Anthropic #Fable5 #Mythos5

There were 4 defacement incidents targeting sites in the United Kingdom, India, and Brazil. The attackers involved were maw3six, Captain Zerox Uchiha, and baskov. #UnitedKingdom #India #Brazil…

Daily Recap, Cyber threat research points to a rise in open-source and developer-supply-chain compromises across PyPI, npm, Docker, and GitHub Actions, while AI is being both leveraged by attackers and targeted in ongoing operations. Reports also flag active exploitation of SonicWall vulnerabilities in ransomware activity, N-able N-central server takeovers after an incomplete fix, and new backdoor tooling including AtlasRAT, OctLurk, SilkLurk, and GoGRPC in phishing and helpdesk-vishing campaigns. #PyPI #npm #Docker #GitHubActions #SonicWall #N-able #N-central #AtlasRAT #OctLurk #SilkLurk #GoGRPC #BTMOB #BrinksHome #WiFi #COLDCARD #Bitcoin
Russ Kirby’s career path shows how passion, discipline, and a willingness to take opportunities helped him grow from technology roles into senior CISO positions at Creditsafe, ForgeRock, and Ping Identity. He says cybersecurity suits his personality, values leadership and enthusiasm, and sees AI as the latest major challenge that defenders must…
Oligo Security has raised $60 million in a new funding round, bringing its total funding to $140 million, as it expands its runtime security platform for application code, cloud workloads, and AI systems. The company says its technology helps block exploit attempts, prevent supply chain attacks, and provide zero-day response and…

University SprinklerSystems, Canada’s largest irrigation company, reported a ransomware incident in which the akira threat actor accessed and exfiltrated employee data (DLs and other files), client information, and other internal files. The attacker enabled password-free archive downloads as part of the incident, impacting #Canada
WD Masonry & Concrete in the US was targeted by the qilin ransomware group, resulting in file encryption and disruption of operations. The impacted country(s): #UnitedStates
Worldtube, a manufacturer of new automotive parts in South Korea, reported a ransomware incident attributed to threat actor gunra, resulting in disruption and potential loss of access to operational systems and data. The impact on their business was significant given their estimated US$ 20,000,000 revenue, affecting operations and recovery efforts across #SouthKorea
Aqua detected a multistage fileless XMRig cryptojacking campaign targeting containerized Node.js applications built with Next.js, exposing malicious activity across in-memory execution, container drift, persistence, and outbound mining communication. The campaign used tactics like memfd-based loading, cron and rc.d persistence, SSH key backdoors, and anti-removal defenses, while Aqua runtime enforcement could block the attack before unauthorized code ran or mining traffic left the workload. #XMRig #Nextjs #Aqua #memfd #Nodejs
Varonis announced Agent Intent-Based Access Control (IBAC) in Varonis Atlas, a new control for keeping AI agents aligned with their intended tasks while stopping dangerous or unauthorized behavior in real time. It evaluates agent intent, runtime actions, and full-session activity to block, alert, log, or quarantine when agents drift from policy. #Varonis #VaronisAtlas #AgentIBAC