
Security vendors at Black Hat USA 2026 announced new products, research, and services spanning AI security, endpoint protection, privileged access, and attack detection. Notable findings include 1Password’s research showing many AI-generated patches fail to fix vulnerabilities, while Zenity exposed a malicious skills campaign affecting AI agent ecosystems. #1Password #OffBy1Labs #Zenity #Vercel…

L Group ransomware operators targeted uva.edu.br in Brazil, compromising systems of Universidade Veiga de Almeida (UVA), a private higher education institution in Rio de Janeiro. The attack affected the education services used by students and staff in Brazil. #Brazil
ChainDrop is a self-propagating npm worm that infected hundreds of packages, stole developer and cloud credentials, and republished itself through compromised npm tokens while also targeting GitHub Actions and AI coding tool environments. Its operators used Ethereum-based C2 resolution and could silently rotate infrastructure without updating the malware, with evidence linking…

There were 9 defacement incidents reported, targeting websites in Brazil, Burkina Faso, India, Madagascar, Sri Lanka, Costa Rica, Serbia, and Kyrgyzstan. The attackers involved were Trenggalek Cyber Army, CoupDeGrace, Antonkill, and Team_CC. #Brazil #BurkinaFaso #India #Madagascar #SriLanka #CostaRica #Serbia #Kyrgyzstan…
The ransomware incident impacted www.ernat-bureau-etudes.fr in France, attributed to the krybit threat actor. ERNAT (Etudes R,éalisations Négoce Assistance Technique) SARL SCOP, a French worker cooperative (SCOP — Société C….), experienced disruption from the attack. #France
In France, www.actini.com reported a ransomware incident attributed to the threat actor krybit. The attacker’s compromise impacted the victim company, Actini Group (ACTINI SAS), with the affected country ending in #France
Krybit ransomware targeted reflet2000.fr, a French building cleaning services company founded in 1984. The incident impacted France #France

Google Threat Intelligence Group tracks UNC6671 as an active extortion operation that uses vishing, AiTM credential theft, and SaaS exfiltration while operating across multiple brands including BlackFile, Redact, Pink, Helix, and Falcon. The report also details shared infrastructure, shifting targeting toward financial and legal sectors, and a Bitcoin-based ransom operation that continued even after the alleged BlackFile shutdown. #UNC6671 #BlackFile #Redact #Pink #Helix #Falcon
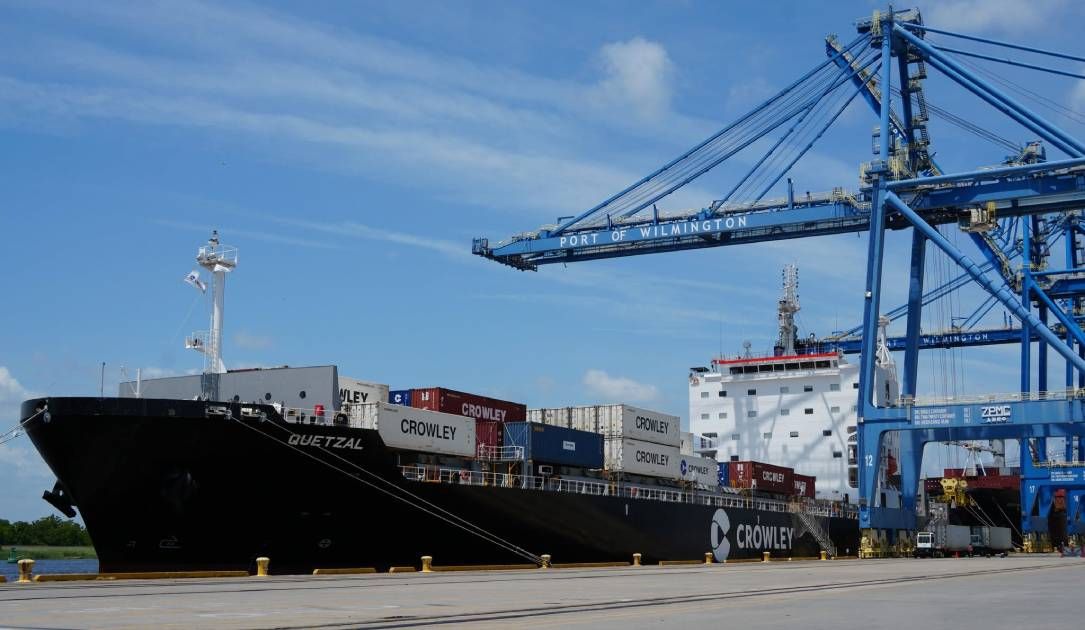
North Carolina Ports is recovering after a cyberattack forced Wilmington, Morehead City, and Charlotte to shift to manual operations while outside forensics teams work to restore affected systems. Officials said the breach has been contained, delays are expected, and no threat actor has claimed responsibility. #NorthCarolinaPorts #Wilmington #MoreheadCity #Charlotte…
SilentRansomGroup ransomware activity targeted Mayer Brown, a distinctly global law firm uniquely positioned to advise leading companies worldwide, disrupting operations across its services. The impacted country(s) are: #UnitedStates
krybit ransomware targeted HYMIASA (www.hymiasa.com), a leading Mexican company specializing in fluid systems, disrupting its operations in Peru. The intrusion resulted in ransomware encryption and data compromise affecting the victim in #Peru
The ransomware claim targets www.serengetiestates.co.za in South Africa (ZA) by threat actor krybit, aiming to compromise data associated with Serengeti Golf and Wildlife Estate. The impact is described for the victim in #SouthAfrica
Researchers discovered a way to bypass recent Spectre v2 mitigations on Intel and AMD processors by exploiting a Time-of-Neutralization to Time-of-Use window. Their attack can leak sensitive Linux kernel data, including hashed passwords from /etc/shadow, and was presented at Black Hat USA by MIT CSAIL researchers Daniël Trujillo and Mengjia Yan. #SpectreV2 #BranchTargetInjection #Linux #Intel #AMD #MITCSAIL #BlackHatUSA
A Go-based malware delivered through ClickFix attacks is targeting macOS users to steal cryptocurrency assets, browser-stored passwords, Apple Keychain data, and cached credentials. It can also intercept and redirect crypto transactions, while Huntress traced the operation to infrastructure linked with Aeza Group in AS 210644. #ClickFix #macOS #Huntress #AezaGroup #AppleKeychain #Bitcoin #Litecoin #Dogecoin #Monero #Ethereum #XRP
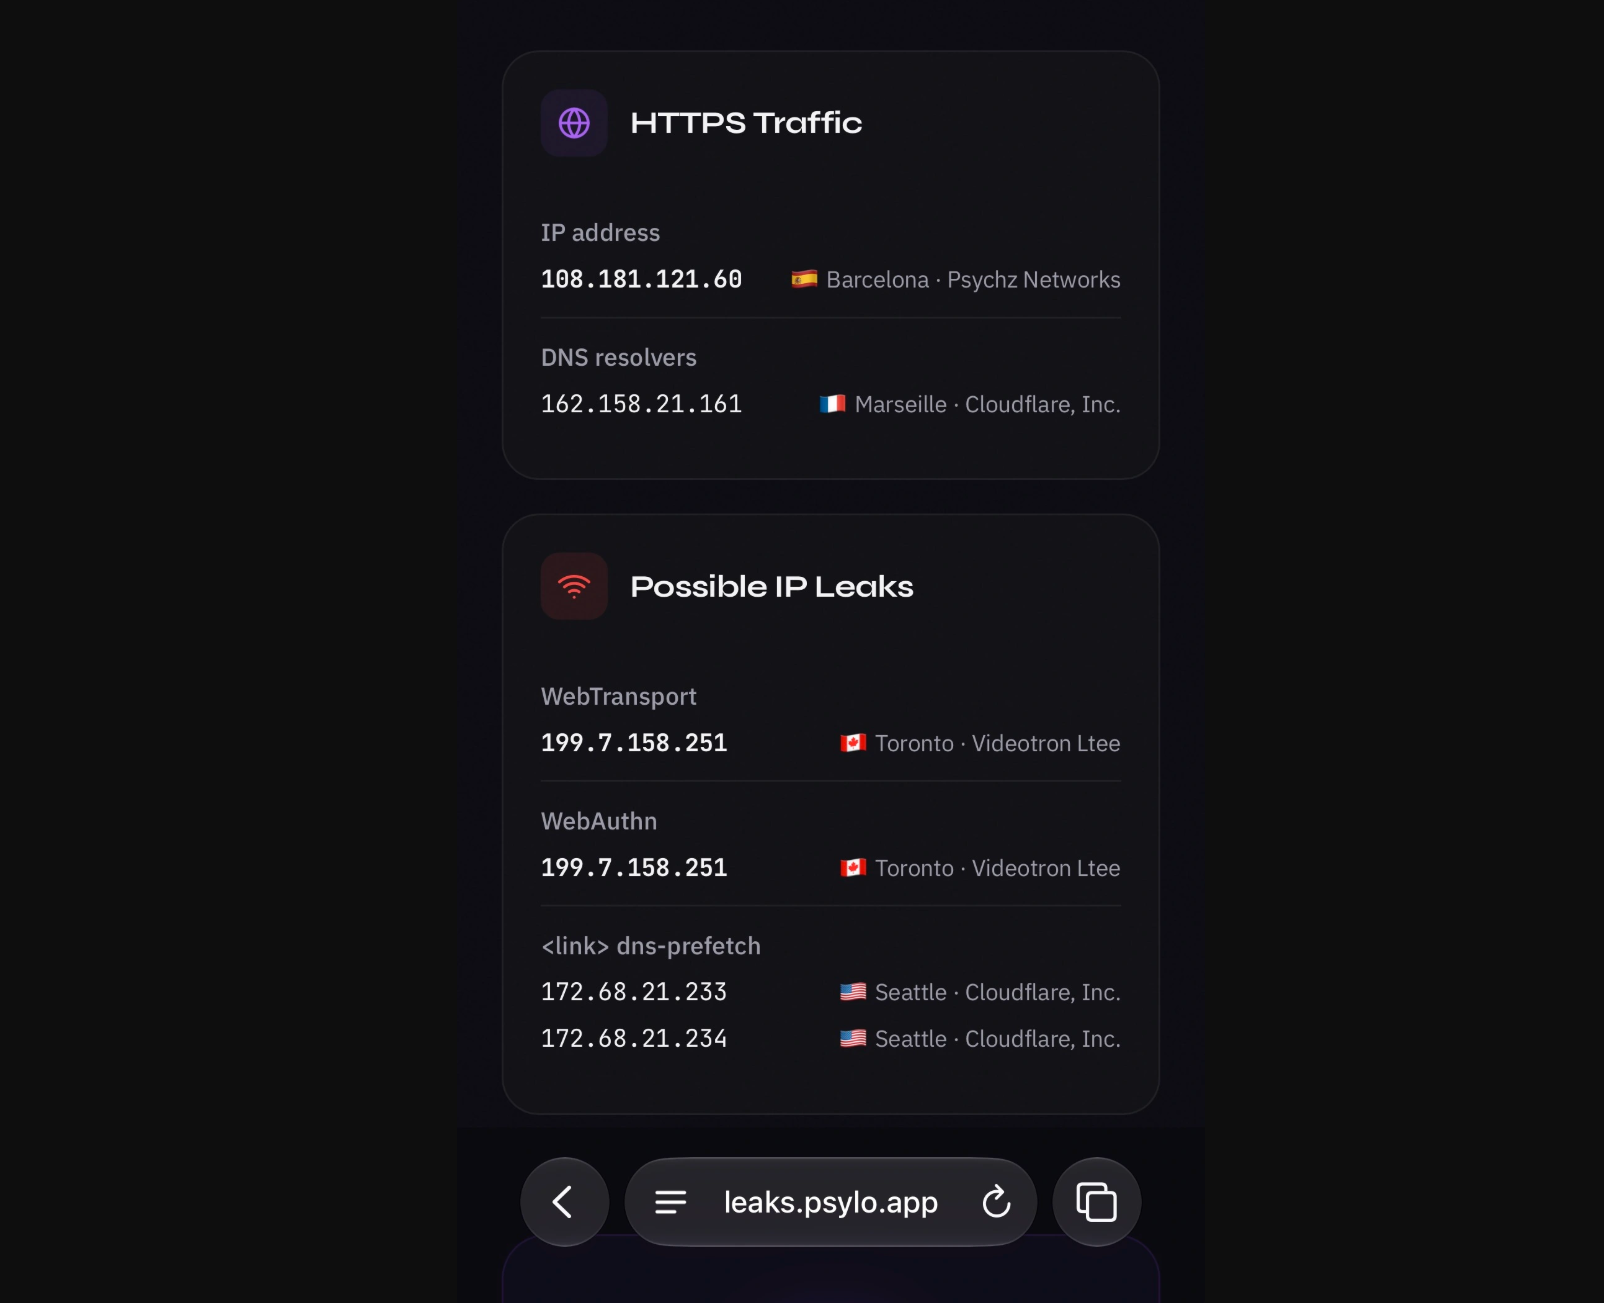
Apple’s iCloud Private Relay protects Safari traffic, but it is not a full device-wide VPN and can fail to hide real IP and DNS data during passkey authentication and other WebKit-related network actions. Security researchers found that WebAuthn, DNS prefetching, and WebTransport can expose user network identifiers, affecting both Safari and…