John C Saunders, CPA, in the US, was targeted by the Qilin ransomware threat actor, resulting in encryption of files and disruption of business operations. The impacted country is the United States. #UnitedStates

EISNER ZT GMBH in Austria was targeted by the qilin ransomware group, resulting in disruption of operations and the encryption of files. The incident highlights the threat posed by the actors behind the attack and its impact on the affected organization in the region #Austria
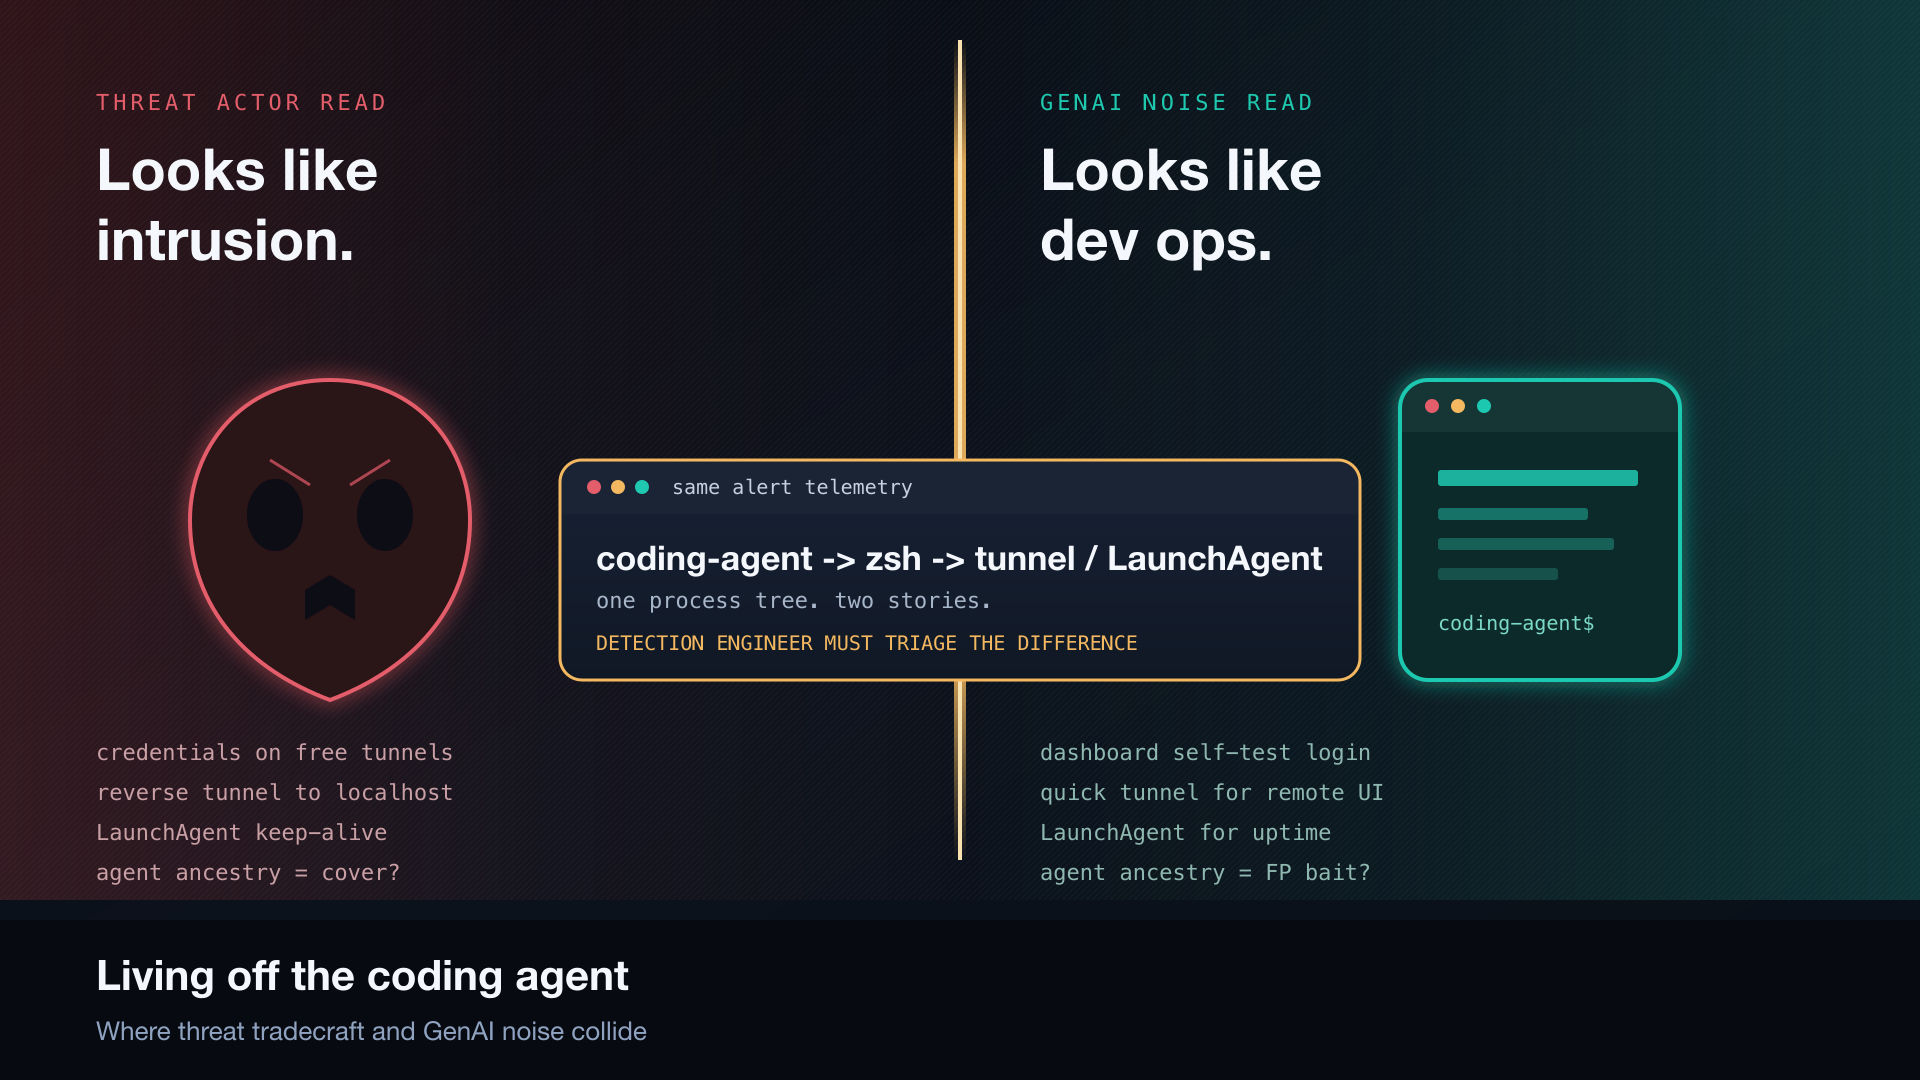
Elastic Security analyzed a macOS developer endpoint where Claude Code and related coding-agent activity parented credentialed HTTP requests, reverse tunnels, and LaunchAgent persistence across free tunnel services like localhost[.]run, Cloudflare Quick Tunnels, and ngrok. The article highlights how these dual-use behaviors can resemble legitimate local admin access while still producing high-severity outcomes that are difficult to triage. #ClaudeCode #Cursor #CloudflareQuickTunnels #ngrok #localhostrun
In the GB-based ransomware claim against Filtronic, the threat actor qilin is alleged to have deployed ransomware to compromise systems and extort the victim. The impacted country is #UnitedKingdom
Astro Electroplating, in the US, was targeted by the qilin ransomware group, resulting in disruptive encryption and operational impact. The affected systems disrupted business operations in #UnitedStates
The ransomware claim targets MEDICOS, a European manufacturer of packaging for beauty and food based in France, with expertise in plastic injection molding and drawn glass production, attributed to the bravox threat actor. #France
The Senate confirmed Adam Cassady as the next U.S. ambassador for cyber and digital policy in a 51-47 vote, making him only the second person to hold the post. His role will be shaped by a State Department reorganization that split the Bureau of Cyberspace and Digital Policy and raised questions…
The National Rural Water Association and DEF CON Franklin have launched the Water Watch Center to bring threat intelligence and cybersecurity support to underfunded U.S. water and wastewater systems. The program targets smaller utilities and comes amid a growing wave of attacks linked to Iranian hackers, with partner firms including Rapid7,…
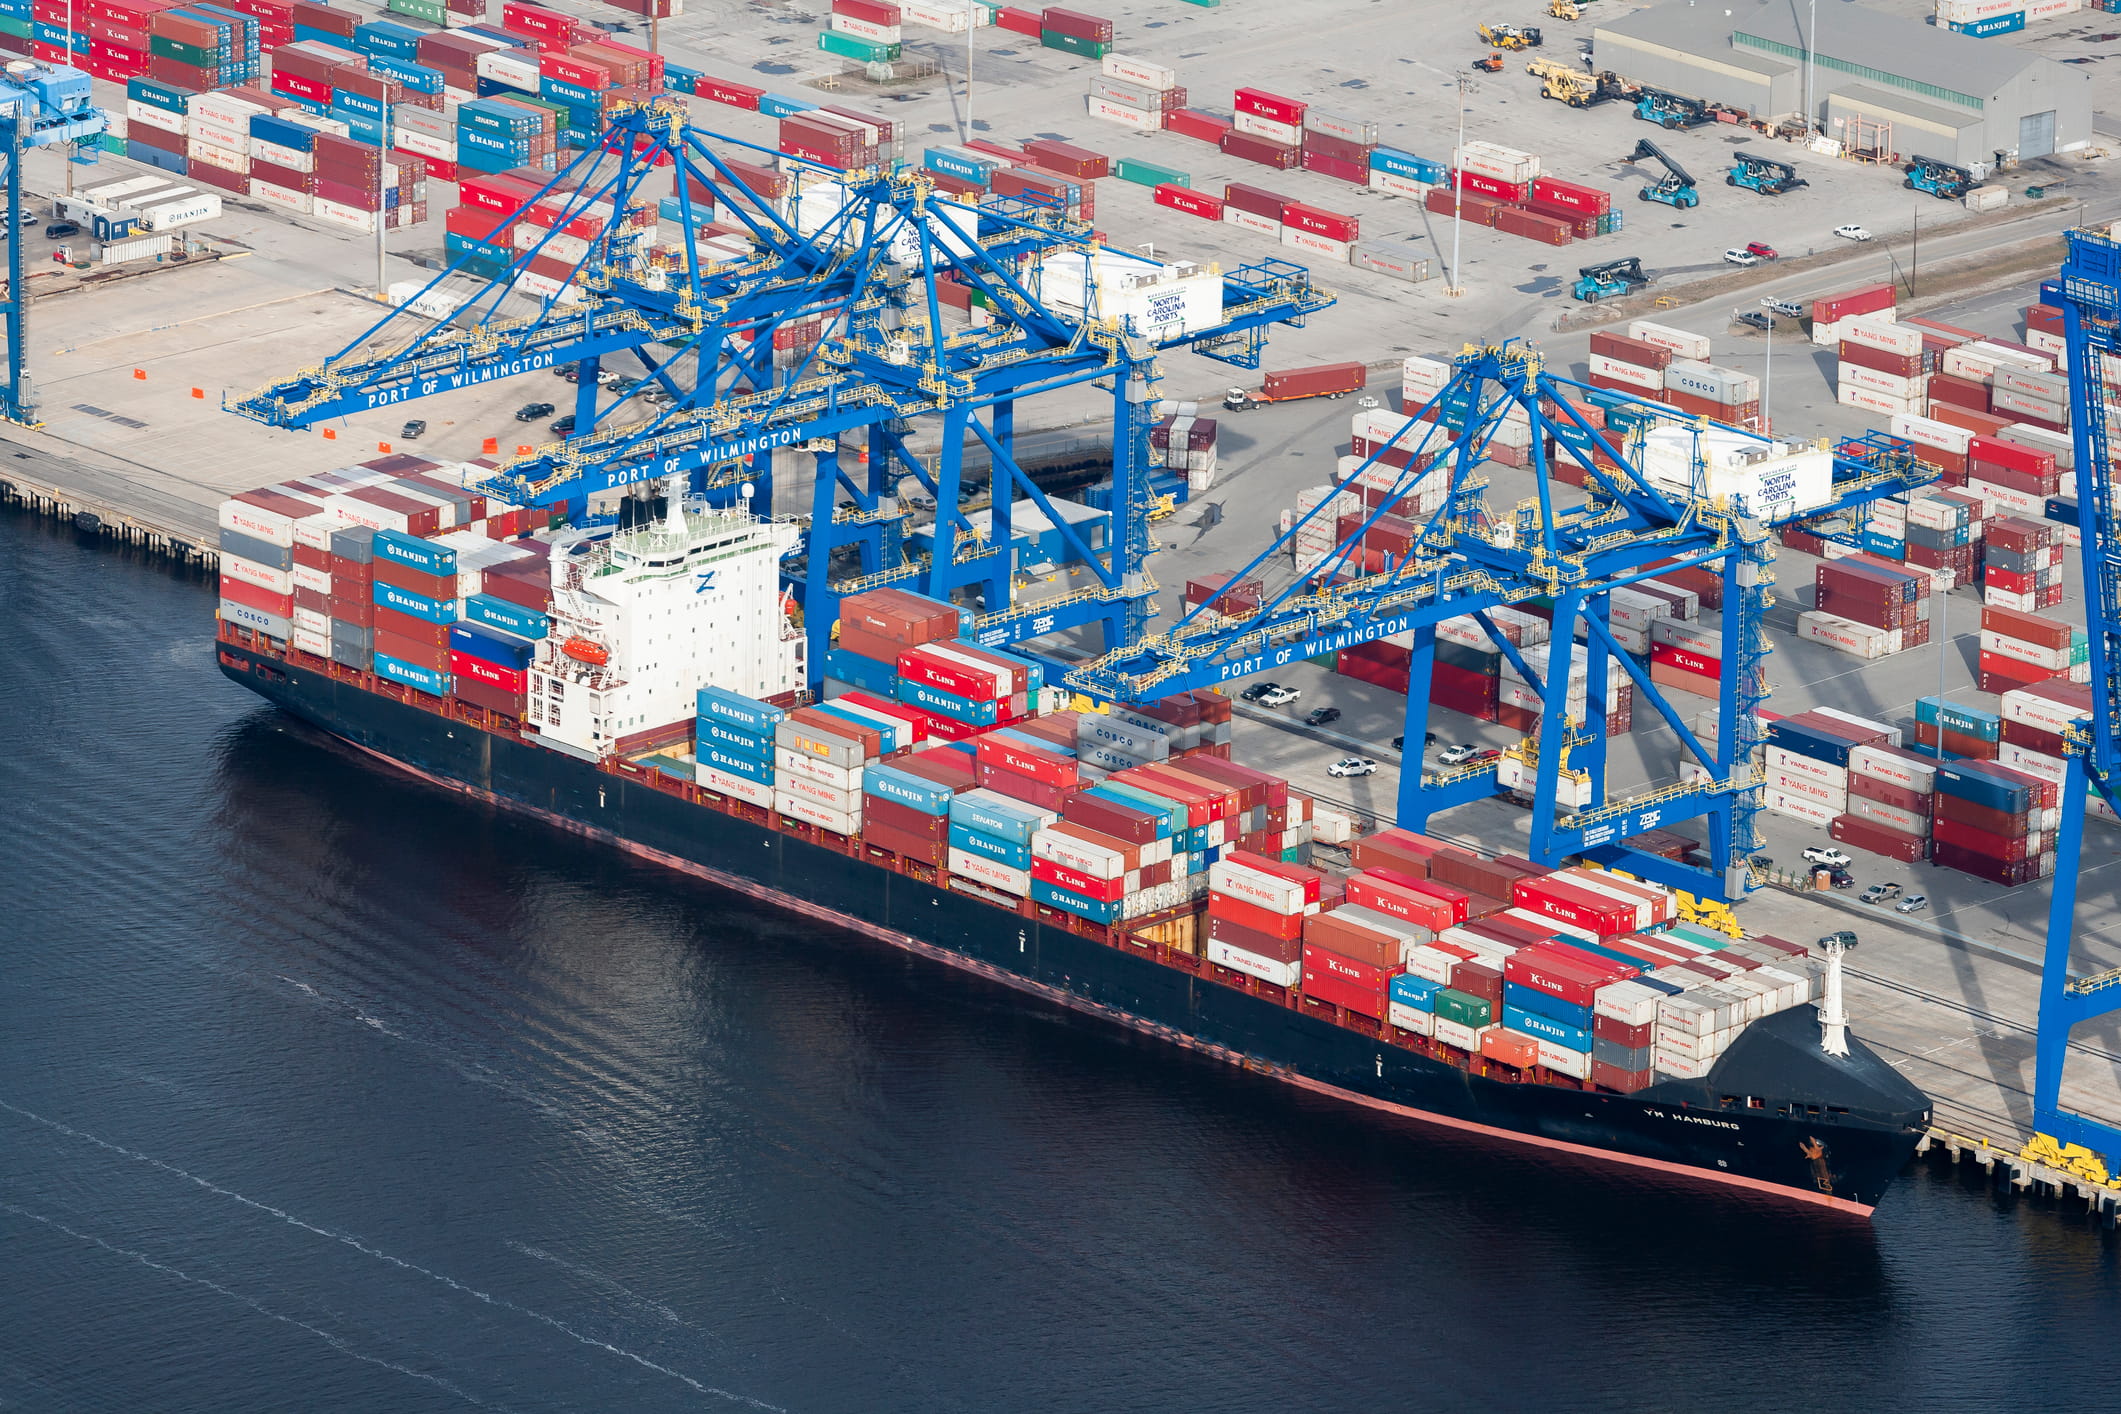
The U.S. Coast Guard is monitoring the fallout from a cyberattack that disrupted gate operations at North Carolina’s Port of Wilmington, Port of Morehead City, and Charlotte Inland Port. The North Carolina State Ports Authority activated its cybersecurity contingency plan, shifted to manual processing, and continues investigating the incident with state and federal partners. #USCoastGuard #NorthCarolinaStatePortsAuthority #PortofWilmington #PortofMoreheadCity #CharlotteInlandPort

A forum user named 888 allegedly posted a breach of ACRE Africa that claims exposure of 14,300 farmer records along with source code, configuration files, access tokens, private keys, and hardcoded credentials. The report is unverified, but the leaked data could enable convincing fraud against smallholder farmers and pose ongoing access…
Cybernox allegedly leaked the Bloctel Do-Not-Call Register, publishing free mirrored copies that claim to contain 3 million French phone numbers and registration identifiers. If true, the leak would invert a consumer-protection system into a target list for callers and fraudsters, especially affecting older consumers in France. #Bloctel #Cybernox #France…
An actor using the name citizengod allegedly posted data tied to the Schools Division of Iloilo, including staff, student, and family records, along with source code and server details. The claimed leak also includes fingerprint templates, identity numbers, attendance records, and weak password hashes, but the report says the breach is…
Alya Construtora (BR) was targeted in a ransomware incident attributed to the ransomhouse threat actor, claiming disruption to the company’s operations. The affected entity was located in Brazil. #Brazil
The ransomware group thegentlemen reportedly targeted Hartfiel Automation, an industrial automation provider, impacting operations in Germany. #Germany
Storm ransomware activity targeted Pioneer Bank, a leading financial institution in New York’s Capital Region headquartered at 652 Albany Shaker Road, Albany, NY 12211, with 201–500 employees. The claim indicates disruption to the bank’s operations in the United States. #UnitedStates