AKIRA ransomware actors claimed to have exfiltrated 170GB of corporate data from ALCAST, a leading aluminum casting company specializing in precision, sand, and die casting, including employee personal files and sensitive business information such as projects, customer data, and contracts. The victim was impacted in #countryname

Presentations.AI (US) reported that unsafe ransomware actors encrypted and demanded payment, affecting company operations and access to critical data. The incident reportedly impacted operations with an estimated $5 million in claimed revenue loss, and the impacted country was the United States #UnitedStates
LexisNexis took its Diligence, Metabase API, and Newsdesk services offline after detecting unusual activity on servers hosted by a third-party vendor. The company is investigating with a cybersecurity forensic firm and rebuilding affected systems in a new environment before restoring service. #LexisNexis #NexisDiligence #NexisMetabaseAPI #NexisNewsdesk
Justin Swaddle, a member of The Com, was sentenced to two years in prison for blackmail and sextortion targeting nearly 120 victims worldwide, including 117 girls aged 13 to 17. The case exposed links to The Com’s broader network of abuse, coercion, and child exploitation across platforms such as Snapchat, Telegram, and Discord. #TheCom #JustinSwaddle #WestYorkshirePolice #NationalCrimeAgency
AI is accelerating account takeover by making phishing, credential theft, MFA abuse, and session hijacking faster and more personalized, while stolen credentials and proxy-based logins are harder to detect. Device trust and Zero Trust controls are needed to ensure valid credentials alone are not enough without the right approved device context. #Specops #ActiveDirectory #Restreamio #IGN #Verizon

Digitide Solutions announced a cybersecurity incident in one of its subsidiaries, confirming unauthorized access to data. The company said there is no major operational or financial loss reported at this time, and an internal investigation is underway. #DigitideSolutions
Foresee immediately activated its information security defenses and engaged external cybersecurity experts to contain the breach, assess its scope, and strengthen its network infrastructure. The company’s preliminary internal evaluation indicates that the attack has not had a significant impact on its normal business operations. #Foresee #ForeseePharma
Germany’s BSI released updated CRA compliance guidance and SBOM specifications, while Czech and Hungarian authorities delivered notable GDPR decisions on pseudonymized data and privacy notices. The article also covers NAI’s AI-in-advertising governance guidance, a UN scientific warning that AI governance is lagging behind agentic systems, and Stanford HAI’s call for new rules for world models and spatial intelligence. #BSI #TR03183 #SBOM #CzechSupremeAdministrativeCourt #NAIH #IndependentInternationalScientificPanelonArtificialIntelligence #StanfordHAI

At-Bay’s 2025 InsurSec Report shows that cyber claims rose sharply in 2024, driven by more ransomware, growing third-party losses, and persistent financial fraud. The report highlights major incidents such as the CDK Global outage, the expansion of ransomware groups, and the growing impact of email-based deception. #AtBay #CDKGlobal #MOVEit #LockBit #BlackBasta #BlackSuit
TRP International in the U.S. was targeted in a ransomware claim attributed to the Storm threat actor, disrupting the company’s distribution and operations. TRP International, LLC distributes high-quality components from strategically located centers across North America, and the incident impacted operations in the United States #UnitedStates
Storm ransomware actors claimed to have targeted Southern Metals Company, a US-based (Charlotte, NC) recycler of ferrous and non-ferrous metals, with a history dating back to 1938. The victim’s operations were allegedly impacted, with the incident affecting #UnitedStates
Global Secret Group ransomware targeted Cook Remodeling, a construction management firm operating cookremodeling.com, encrypting 23.2 GB across 47,193 files and 8,323 folders. The incident affected Arizona, United States. #ArizonaUnitedStates
CISA warned that attackers are actively exploiting CVE-2026-8037, a critical command injection flaw in Progress Kemp LoadMaster that can let unauthenticated threat actors run arbitrary commands on exposed appliances. Progress has already released patches, and CISA is urging all defenders to prioritize remediation, especially for the widely deployed LoadMaster and MOVEit WAF products. #CVE-2026-8037 #ProgressKempLoadMaster #ProgressSoftware #CISA #MOVEitWAF
Baicizhan (CN), a language learning platform specializing in English instruction, reportedly became a target of the dragonforce ransomware threat actor. The attack impacted systems supporting its English learning tools and resources, resulting in service disruption in #China
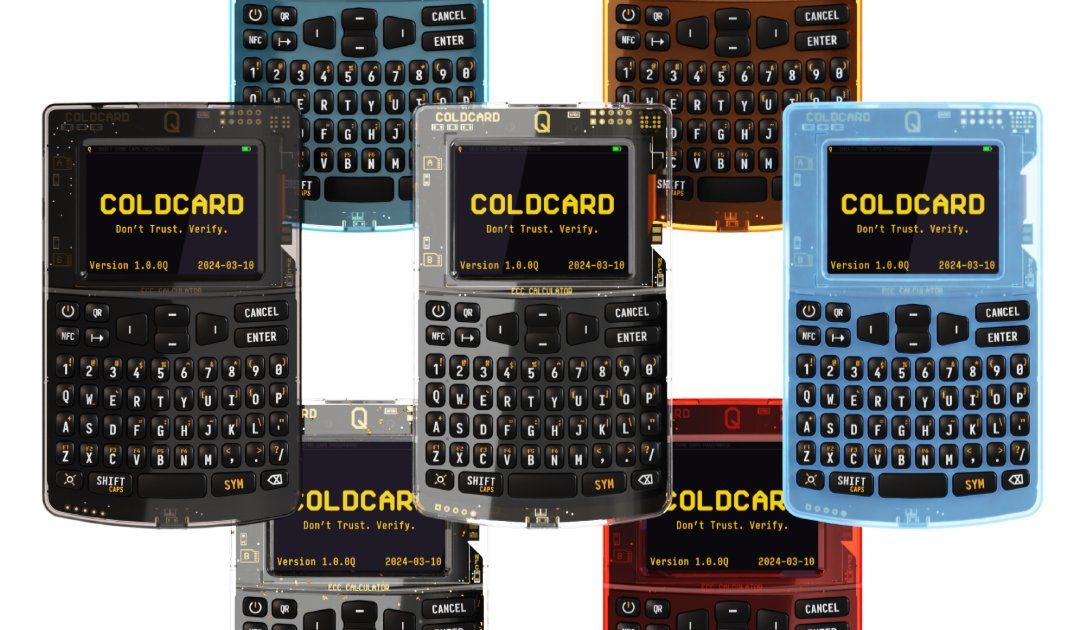
Coinkite destroyed its remaining Coldcard inventory after a firmware vulnerability was exploited to steal at least 1,367.05 BTC, worth about $88.6 million, from thousands of bitcoin wallets. The company released a patched firmware version and is working with affected customers and law enforcement to help recover funds and identify those responsible….