The U.S. Department of Justice announced the arrest of Anibal Alexander Canelon Aguirre, the alleged developer of Ploutus malware used in ATM jackpotting attacks that stole millions from U.S. banks and credit unions. The case ties the scheme to Tren de Aragua and highlights a broader investigation that has led to dozens of charges and sanctions across multiple countries. #Ploutus #AnibalAlexanderCanelonAguirre #TrenDeAragua #FBI #OFAC
tenfold’s Community Edition now gives organizations with under 150 users full access to its IGA platform, including new free capabilities for shared content governance and event auditing. These updates help small teams control Microsoft 365 sharing, review access regularly, and spot suspicious identity activity in real time. #tenfold #Microsoft365 #Teams #OneDrive #SharePoint #EntraID #ActiveDirectory
South Korea’s Financial Services Commission held an emergency meeting after cyber incidents hit major banks, confirming a data breach at Shinhan Bank and impacts to Kookmin Bank and Hana Bank. Authorities ordered financial firms to inspect exposed IT systems and tighten controls while investigators examine whether AI-powered attack automation tools may have been involved. #ShinhanBank #KBKookminBank #HanaBank #FSC #KISA #ARTEXAI
Dell warned customers to urgently patch a critical flaw in the System Update (DSU) CLI tool that could let an unauthenticated remote attacker execute code with root privileges through a path traversal weakness. The company also fixed several other high-severity DSU and Container Storage Modules issues, while CISA ordered federal agencies to patch vulnerable Dell systems quickly. #CVE-2026-86360 #CVE-2026-63697 #CVE-2026-71168 #CVE-2026-86361 #CVE-2026-86362 #CVE-2026-63688 #CVE-2026-63692 #Dell #DSU #CISA
Denmark’s Central Population Register (CPR) says a breach exposed personal data for about 8.8 million registered individuals, including names, addresses, and CPR numbers. The incident involved brute-forcing valid CPR numbers through a private Danish company’s legitimate access, and authorities have blocked the access and launched an investigation. #CentralPopulationRegister #CPR #ChristinaEgelund
Clover Health Investments and AngMar Management Services have both disclosed data breaches that together affected more than 250,000 people. The stolen information includes sensitive PII and PHI, and AngMar was later named by the Interlock ransomware group. #CloverHealthInvestments #AngMarManagementServices #Interlock…
FortiGuard Labs uncovered ClingSTUN, a Linux backdoor that turns infected devices into STUN-based proxies and includes exploits for self-propagation across many vulnerable products. It also uses persistence, architecture-specific payloads, and remote command capabilities while abusing legitimate public STUN servers for NAT connectivity. #ClingSTUN #FortiGuardLabs #STUN #Avtech #EnGenius #DLink #Ivanti #TPLink…
Google has temporarily paused product vulnerability submissions to its Open Source Software Vulnerability Reward Program after a surge in automated reports, most of which were invalid. The pause does not affect supply chain reports or pending submissions, and Google plans to provide an update in Q1 2027. #Google #OSSVRP #CloudVRP #PatchRewardsProgram…
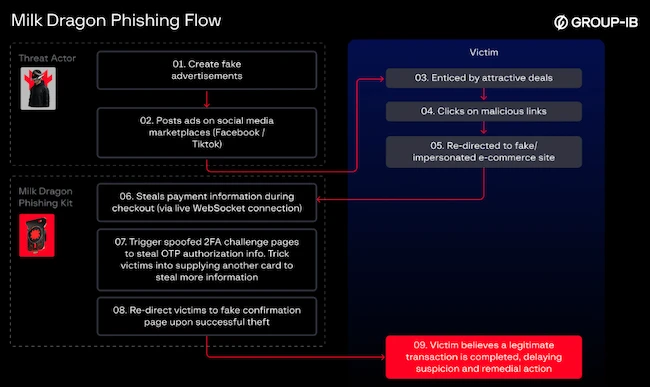
Group-IB has warned that cybercriminals are using fake discount ads on Facebook and TikTok to drive shoppers to phishing sites that steal payment card details and one-time passwords. The Milk Dragon phishing kit, also known as NaiLong, has linked thousands of fake shopping pages across 66 countries by impersonating brands such as LEGO, Calvin Klein, and Aeon Malaysia. #GroupIB #MilkDragon #NaiLong #Facebook #TikTok #LEGO #CalvinKlein #AeonMalaysia

CISA has added CVE-2026-88779, a Citrix NetScaler memory overflow flaw, to its Known Exploited Vulnerabilities catalog after reports of targeted attacks causing denial of service and repeated crashes on vulnerable appliances. Citrix says the issue affects service availability on on-prem deployments using SAML with Gateway or AAA functionality, while advisories urge upgrades, IOC checks, and use of Global Deny List signatures. #CVE-2026-88779 #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772 #watchTowr #BishopFox #Geico

Iranian hackers’ attacks on water systems in 12 U.S. states exposed serious weaknesses in America’s critical water infrastructure and showed how a broader campaign could trigger a nationwide public health crisis. The article argues that the U.S. must urgently strengthen defenses with zero-trust architecture, formal methods, and AI-enabled cybersecurity support for utilities of all sizes. #IranianHackers #WaterSystems #ZeroTrustArchitecture #VoltTyphoon #ClaudeMythos

O2 Dental Group in the US suffered a ransomware incident attributed to the interlock threat actor, impacting patient data and business records. The attack led to compromised PHI, billing and insurance documents, and consent and authorization forms, affecting the healthcare environment in #UnitedStates
The ransomware attack involving the threat actor “qilin” targeted Asia Era One in Malaysia, with malicious encryption activities disrupting affected systems. The claim indicates compromise of organizational data and operational services, impacting Malaysia #malaysia
Eclipse ransomware reportedly targeted part02.simplexengg.in in India, encrypting files and disrupting normal operations. The incident impacted India #India
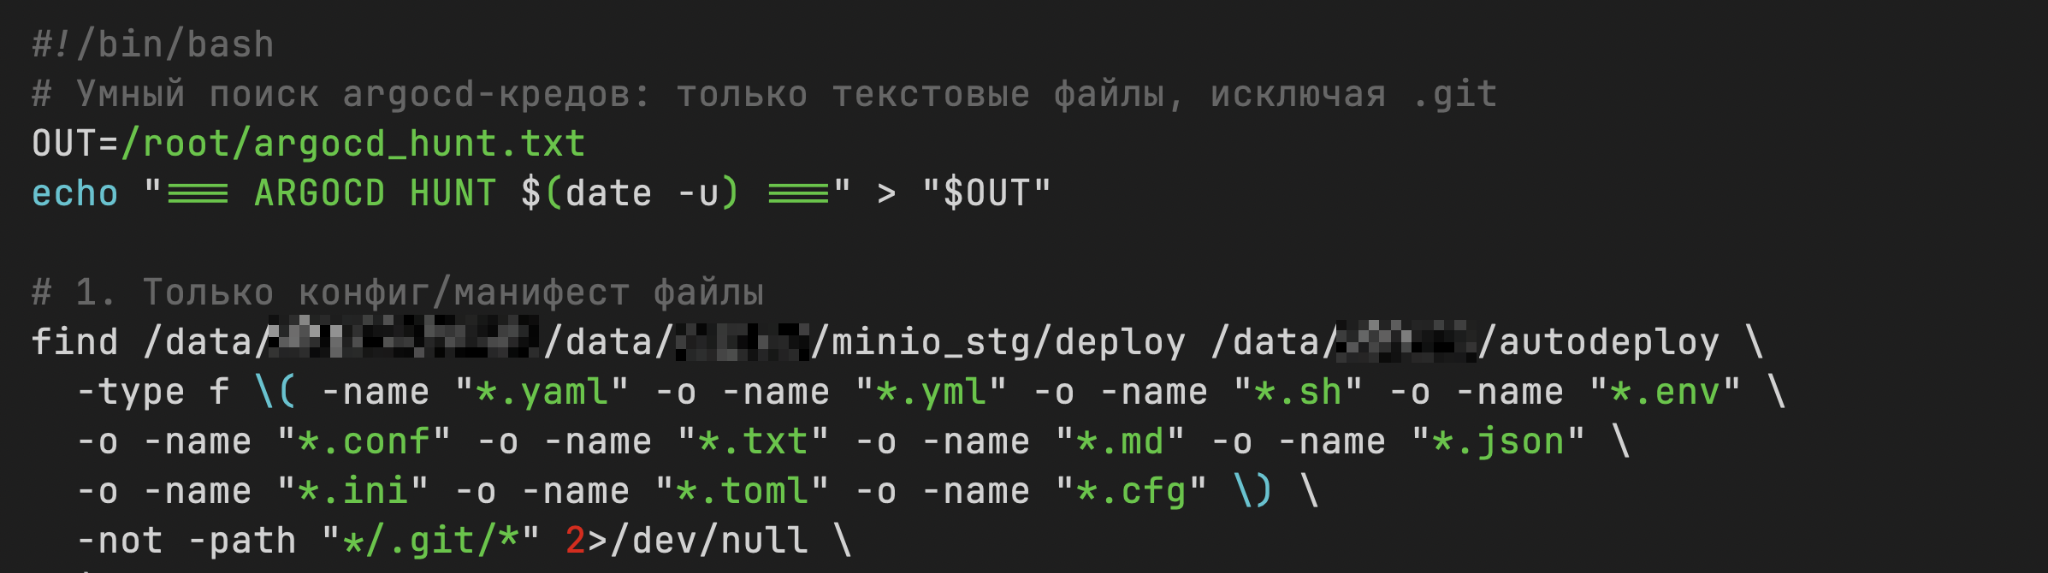
CloudSEK uncovered Azazel, a Russian-speaking affiliate of the Gentlemen ransomware group, who used stolen CI/CD secrets and a separate AI-platform intrusion to compromise more than two dozen organizations and exfiltrate over 6TB of data. He also ran his own independent leak site, LEAKNED, bypassed the RaaS operator’s revenue stream, and used MCP-based tooling and internet-wide scanning to support the operation. #Gentlemen #LEAKNED #Azazel #MCP #GitLab