Google says Chrome’s anti-abuse systems cut unwanted Android notifications by more than 7 billion per day in Q1 2026. The company is using layered defenses, automatic permission revocations, and network-wide analysis to stop deceptive notification abuse tied to scams, phishing, malware, and fraudulent payment requests. #Chrome #Google #Android

Ransomware attributed to the qilin threat actor compromised Crown Group in Pakistan, encrypting data and disrupting operations while demanding ransom for decryption. The incident impacted Pakistan #Pakistan
G.M.A. GRANDI MARCHE AUTOMOBILI – S.R.L in Italy reported a ransomware incident attributed to the Qilin threat actor. The attack resulted in unauthorized encryption and disruption of operations in the impacted environment. #Italy
Genesis ransomware, attributed to the threat actor genesis, reportedly targeted the US healthcare organization **E***, encrypting critical files and disrupting operations. The incident’s impacts are reported in the United States#UnitedStates

The Chrome extension “AI Sidebar with DeepSeek AI” was relisted after being removed for stealing AI conversation content, and its latest build now performs affiliate referral fraud through silent tab opens on update and uninstall. Netskope found the malicious version 1.7.3.0 being delivered to enterprise endpoints via Google’s CRX distribution, with the extension ID inhcgfpbfdjbjogdfjbclgolkmhnooop and prior exfiltration domains deepaichats[.]com and chatsaigpt[.]com. #AISidebarwithDeepSeekAI #inhcgfpbfdjbjogdfjbclgolkmhnooop #deepaichats #chatsaigpt

AnMed is still dealing with widespread disruption two weeks after a cyberattack, while its Facebook page briefly displayed ransom demands linked to the The Gentlemen ransomware group before being removed. The group claimed to have stolen 6 terabytes of sensitive health data, but AnMed has not verified those claims and says…
The National Security Agency has appointed Kerianne Tobitsch as its new general counsel, filling a role that had been vacant for about a year after a series of high-level departures. Her appointment comes as the agency prepares for key legal and policy battles, including the renewal of Section 702 of FISA….

A set of Zoom annotation-tool flaws could let a meeting participant take over other attendees’ computers, with no click or visible prompt required. Zoom had already shipped fixes in June and July, and the issues are tracked as CVE-2026-53413, CVE-2026-53414, and CVE-2026-53415. #Zoom #CVE-2026-53413 #CVE-2026-53414 #CVE-2026-53415 #A_Security…
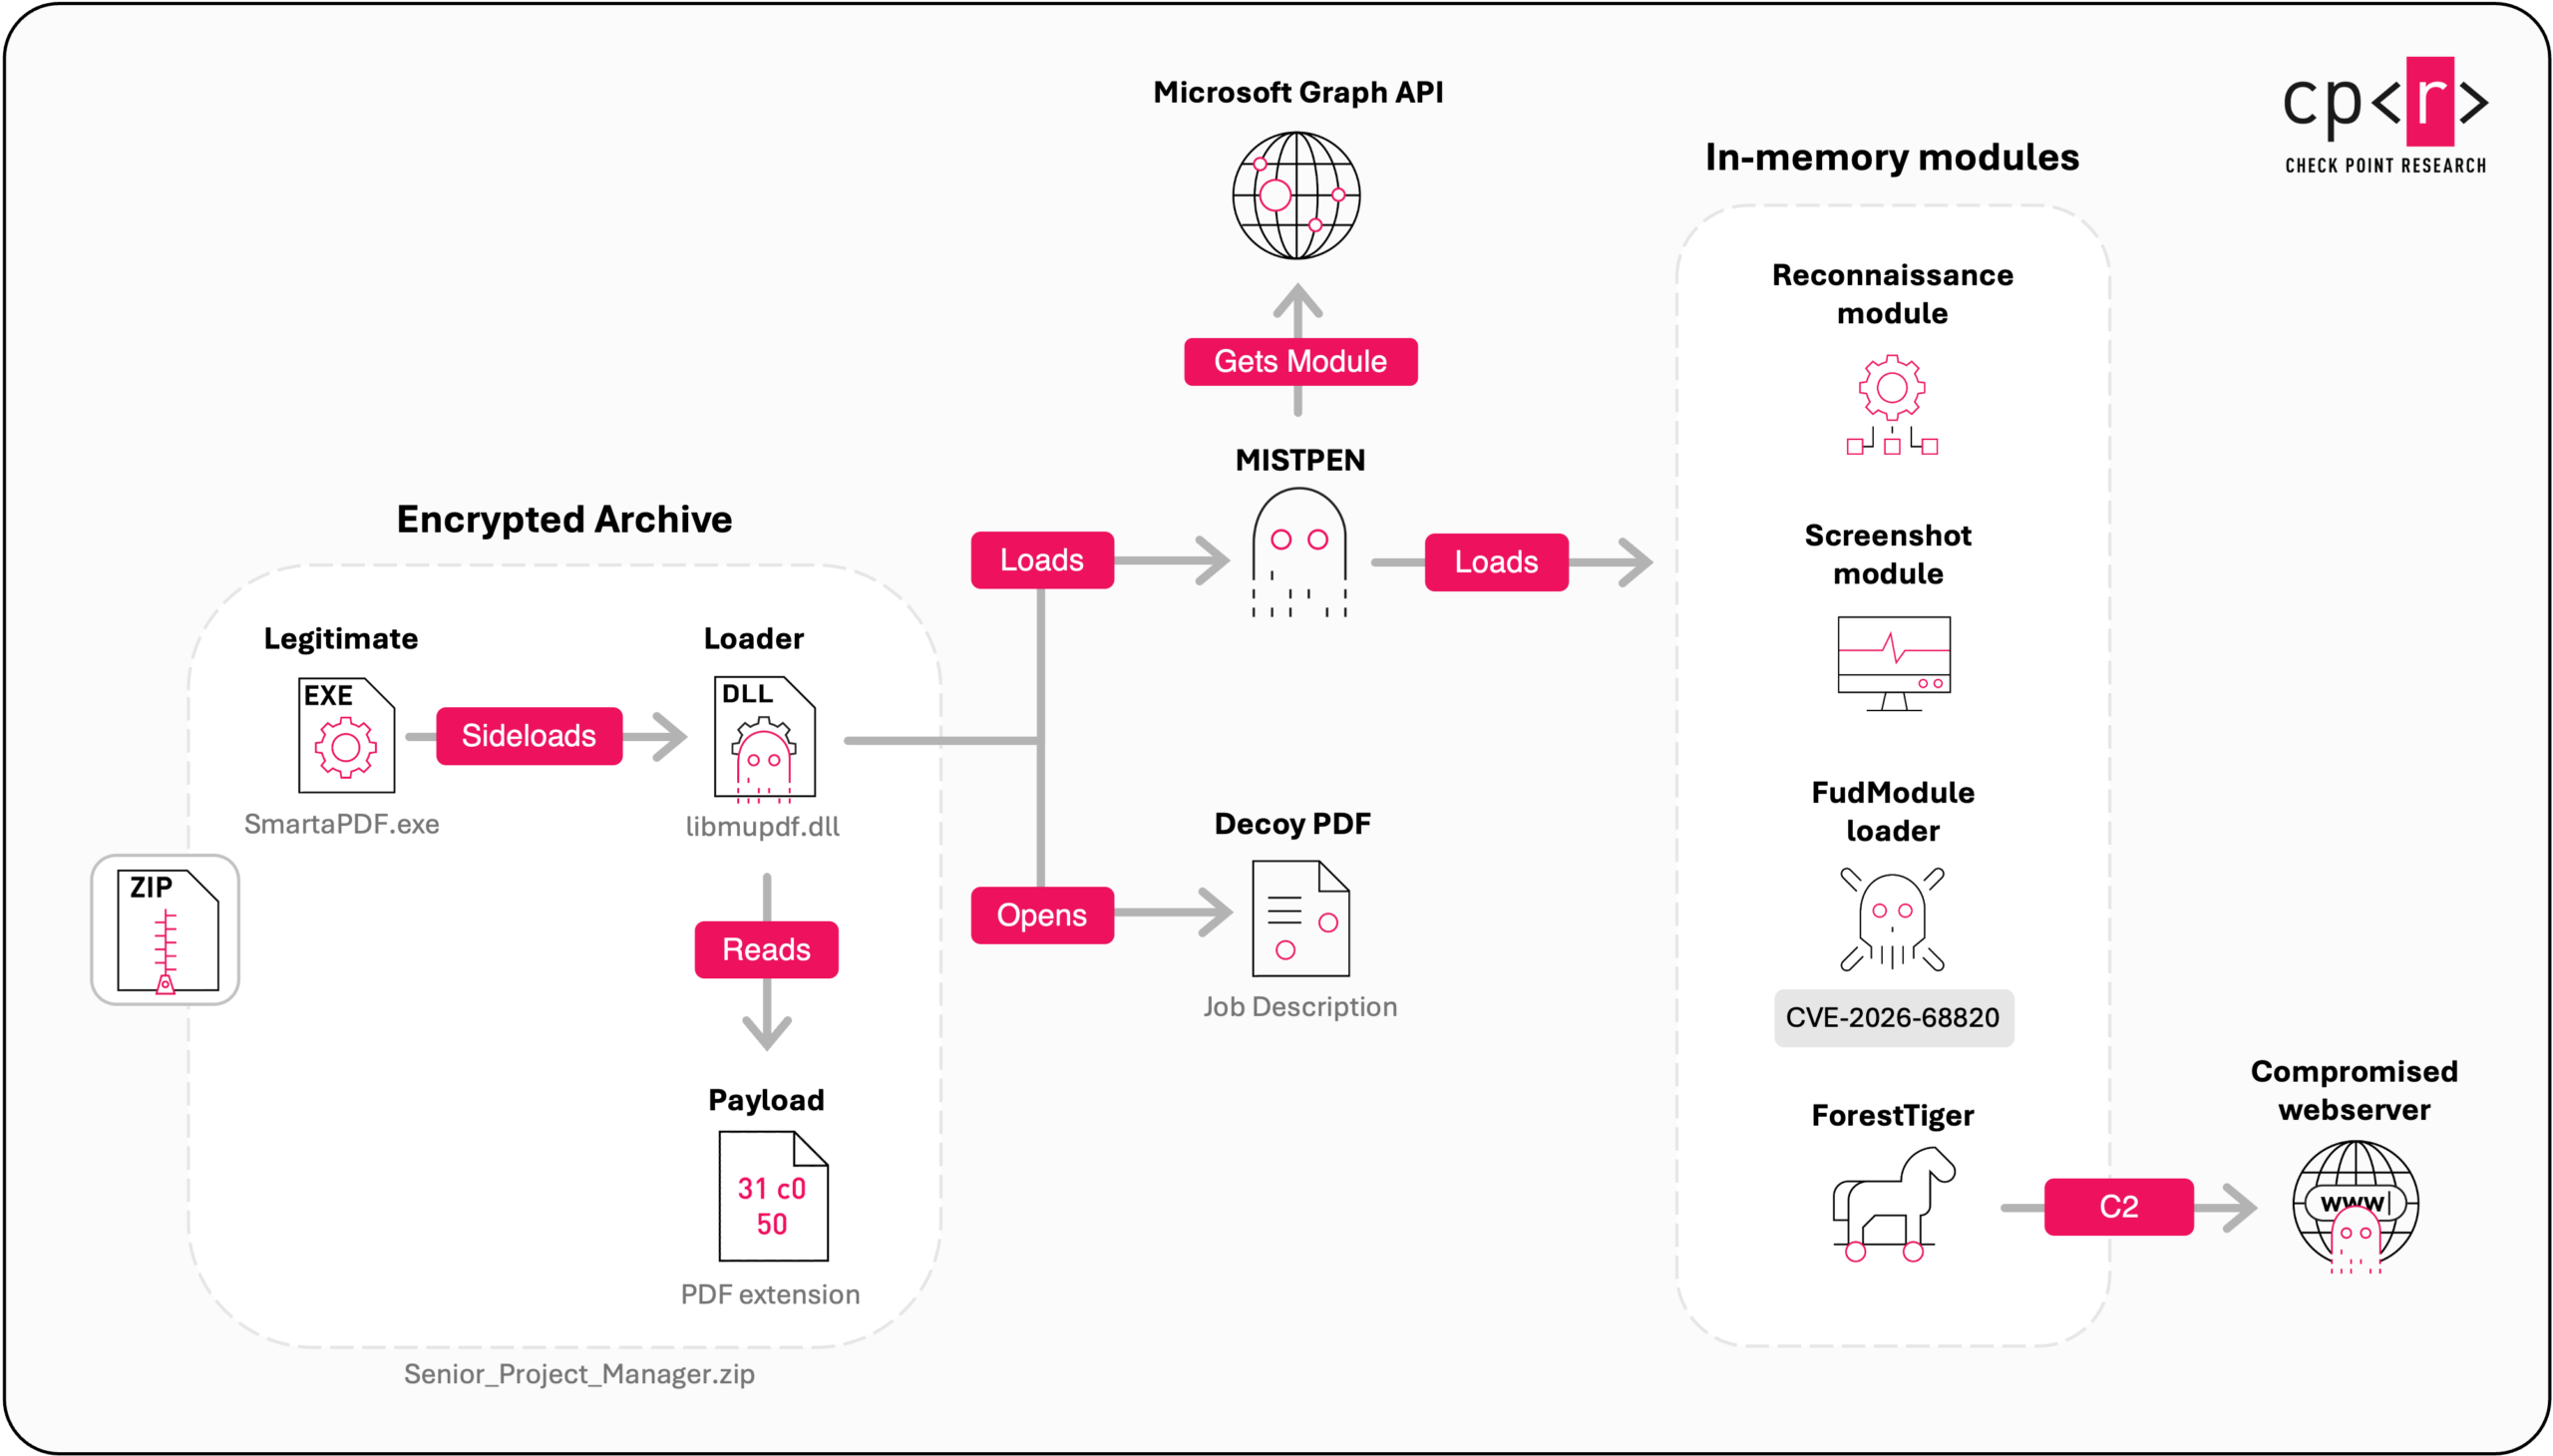
Check Point Research tracked a long-running Operation Dream Job campaign linked to Lazarus, with a latest wave targeting defense organizations in Europe and India using trojanized PDF viewers, spear-phishing, and compromised web infrastructure. The campaign deployed SecurityPDF, Troy, MISTPEN, RelayShell, and a new FudModule variant exploiting CVE-2026-68820 while also abusing Roundcube servers via CVE-2025-49113. #OperationDreamJob #Lazarus #SecurityPDF #Troy #MISTPEN #RelayShell #FudModule #CVE-2026-68820 #CVE-2025-49113

A forum user named slvsh3r allegedly leaked the database and full source code of HeyPulse, a French B2B marketing platform used by local businesses. The exposed data may include client account details and sensitive code components such as authentication, payment, email, and database layers, though the claim remains unverified. #HeyPulse #slvsh3r…
A post by DarkMafiaX allegedly leaked the HerbaSis database, exposing Brazilian customers’ medical conditions, CPF national ID numbers, and other sensitive personal details. The claim is unverified, but the sample data suggests a serious privacy exposure affecting a third-party wellness platform used by nutrition consultants. #HerbaSis #DarkMafiaX #CPF…
An actor using the name exfilar is claiming to sell a 110GB dump from Gran Caribe Hotel Group that allegedly includes 26,094 guest passport records, employee files, and full corporate systems. The unverified listing says the data spans eight Cuban properties and is being offered for $10,000, with potentially severe identity…
The ransomware claim alleges that the threat actor settra compromised oligo.de, a German-based entity connected to businesses supplying luminaires for prominent landmarks including Deutsche Bank, Burj Dubai, and Scout Motors’ assembly operations. The impacted country is #Germany
The ransomware claim targets flowco-inc.com in the United States, attributed to the settra threat actor, and DEEP WELL indicates stolen data including Flowco Production Solutions documents such as payroll records with employee names and po…. The impacted country(s): #UnitedStates
FirstDigital.com (US) was targeted by the ransomware threat actor settra, allegedly involving The Digital Cartel: How a Telecom Empire Robs Its Own Customers and Employees. The incident impacted #UnitedStates